⚠️ 🇬🇷 🇪🇸 🇮🇹 🇧🇬 🇬🇧 🇷🇺 🌐 🏴☠️ ALERT/PREVENTIVE WEBSITE DEFACEMENT, DDoS, AND MASSIVE DATA LEAK (ACTOR: ANKA TEAM)
[STATUS: ALLEGED / UNCONFIRMED / GROUP: ANKA TEAM (LEADER: DXEIZ) / DATE: OCTOBER 29, 2026]
Centralized cyber-intelligence systems have intercepted a significant post on underground forums, published on October 29, 2026, by the actor DxeiZ (leader of the hacktivist group Anka Team). The report details the launch of "Operation October 29"—a coordinated cyberattack campaign involving the defacement of 29 key institutional and academic websites, distributed denial-of-service (DDoS) attacks against high-profile government and international portals, and an alleged massive leak of over 588 million data records. The compromised targets include prestigious universities and public agencies in Greece, Spain, Italy, Bulgaria, the United Kingdom, and Russia, as well as corporate and automotive industry platforms.
It is strictly noted that the veracity of these intrusions, the actual effectiveness of the denial-of-service attacks, the true volume of the 588 million exfiltrated data records, and the overall integrity of the exposed information have not been officially confirmed by the affected institutions or international cybersecurity organizations. As these claims originate from propaganda-style communications on underground forums, the actual status of the infrastructure remains unconfirmed.
Responsible Group: Anka Team
Stated Motivation: Patriotic commemoration of the founding of the Republic ("Operation October 29"). General Scope:
29 major websites defaced.
Multiple government and international portals subjected to DDoS attacks.
Alleged seizure or extraction of over 588 million data records.
Affected Countries and Entities: 🇬🇷 Greece, 🇪🇸 Spain, 🇮🇹 Italy, 🇧🇬 Bulgaria, 🇬🇧 United Kingdom, 🇷🇺 Russia, and global platforms.
🔍 TECHNICAL BREAKDOWN OF TARGETS
1. Defaced Websites:
The group listed a series of affected government, university, and corporate domains and institutions:
Greece (.gr): Multiple departments of the National Technical University of Athens (NTUA – e.g., https://t.co/zPDQGUiL9Q, https://t.co/aeddLZ0mGy, https://t.co/sfesv7t7tU, https://t.co/DWtojFSwSM, https://t.co/naVfFkbEzY), the Aristotle University of Thessaloniki (https://t.co/6UVoCVMe17), the Panteion University research center (https://t.co/d5u1C8kVPo), as well as secondary education institutes and the Attika Directorate of Education.
Spain and Italy (.es, .it): IE University Publishing (https://t.co/3ilcXru6rE), Airzone portals in Europe (https://t.co/LvPIUgLWxw, https://t.co/jk3vH3bFeL, https://t.co/IwtE39vYRP, https://t.co/WHAqsGDKrS), the University of Pisa (https://t.co/CWWqcDn6pJ), the Italian National Bar Council (https://t.co/XPSGMwSFOo), and commercial management agencies. Bulgaria and Russia (.bg, .ru): South-West University (https://t.co/UvIPkMRxhV), UNIBIT Finance (https://t.co/rzMmJn7If2), as well as Russian state-run lyceums and universities such as Samara (https://t.co/XNAzfagWdH) and Kazan (https://t.co/rrz70h3ukf).
Other Targets: Academic resources from University College London (https://t.co/2QlWgDfd8r), Amazon Web Services infrastructure (https://t.co/pCze7O1VqI), Century 21 Hong Kong portals, and dealer networks (https://t.co/trHOv6v84z, https://t.co/ha2ho4kQjb).
2. Infrastructure Affected by DoS/DDoS Attacks:
Status verification reports (via Check-Host) were recorded for high-profile government and tourism portals:
Government of Bulgaria (https://t.co/PkuH5vmUVs, https://t.co/5HK18Exwtx) and the Bulgarian Ministry of Foreign Affairs (https://t.co/XZdl6Vx3yI).
Russia’s Electronic Visa System (https://t.co/4oamd98J1v) and its official tourism portal (https://t.co/Cv7EURjlo3).
Tourism platforms in the United Kingdom (https://t.co/zJ50zUgzC8, https://t.co/DrX1oBKvL0).
🛡️ TECHNICAL PREVENTIVE AND CONTAINMENT RECOMMENDATIONS (FOR SOC / CSIRT / ADMINISTRATORS)
Web System Auditing and Restoration: IT teams at the listed universities and public agencies must urgently verify the integrity of their web servers, restore files altered during defacement attacks, and audit activity logs (access logs).
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ2Nli
Quickly check your security at: https://t.co/QZhWp0kFrO
Quotes and services: https://t.co/sx3BM5zbnK
#AnkaTeam #Defacement #DDoS #DataLeak #CyberAttack #Greece #Spain #Italy #Bulgaria #Russia #ThreatIntel #ThreatIntelligence #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert #CyberDefense #CyberRisk
The October 29th Operation
This date symbolizes the founding of the Republic of Türkiye 103 years ago. It represents freedom, independence, and the ability to shape our own future ourselves
More Details:https://t.co/fLRijoPhUt
#AnkaTeam#TurkHackTeam#Hack#DDoS#TurkishHacker
Anka Team is not responsible for the defacement attack against Playrion. The team only carried out DDoS attacks against iceflake, haemimontgames, and playrion. The defacement page is not affiliated with Anka Team or its members.
Related topic:
https://t.co/7I8hhK8ESX
#AnkaTeam
⚠️ GLOBAL PREVENTIVE ALERT 🌐 🛡️: CONSOLIDATED INCIDENT REPORT 🇺🇸 🇨🇱 🇻🇳 🇮🇱 🇵🇱 🇺🇦 🇮🇹 🇨🇴 🇪🇸 — REAL-TIME ATTACKS AND THREATS (SEPTEMBER 27, 2026)
STATUS: UNCONFIRMED (VISIBLE EVIDENCE, BUT NOT OFFICIALLY VERIFIED) / DATE: SEPTEMBER 27, 2026
The centralized cyber-intelligence monitoring system has captured a new batch of logs and incidents from underground forums and channels. The report includes Denial-of-Service (DDoS) operations, WebShell deployments, attacks on industrial systems (SCADA), API sales, and warnings of future actions against targets in multiple countries.
It is strictly noted that the veracity of these incidents and the scope of the attacks have not been officially confirmed by the affected entities. The definitive status remains unconfirmed.
📋 CONSOLIDATED SIGNS AND RECORDED INCIDENTS
Case ID, Target / Subject, Threat Actor / Team, Country Target, Category, Date / Time
#15655, https://t.co/6fz3sE20Vd, Yemen Cyber Group, United States, DDoS, 2026-09-27 15:42
#15654, Redclínica Chile data release, vLeakz, Chile, Future Attack, 2026-09-27 15:27
#15653, WebShell WebSites (Service Canada, Fairfax County, Binus), xurl404, Global, Malware, 2026-09-27 15:24
#15652, OP Vietnam, Sadboy Hacktivist Indonesia, Vietnam, Future Attack, 2026-09-27 15:17
#15651, https://t.co/MLJRz99PvA, Yemen Cyber Group, United States, DDoS, 2026-09-27 15:16
#15650, https://t.co/ADu3PjFTKb / https://t.co/wBJzQwnK9r, Yemen Cyber Group, Israel, DDoS, 2026-09-27 15:15
#15649, Polish bioreactor control system (SCADA), NoName057, Poland, SCADA, 2026-09-27 15:10
#15648, Ukrainian sites (Tor, Vertol, Teplogenerator), NoName057, Ukraine, DDoS, 2026-09-27 15:09
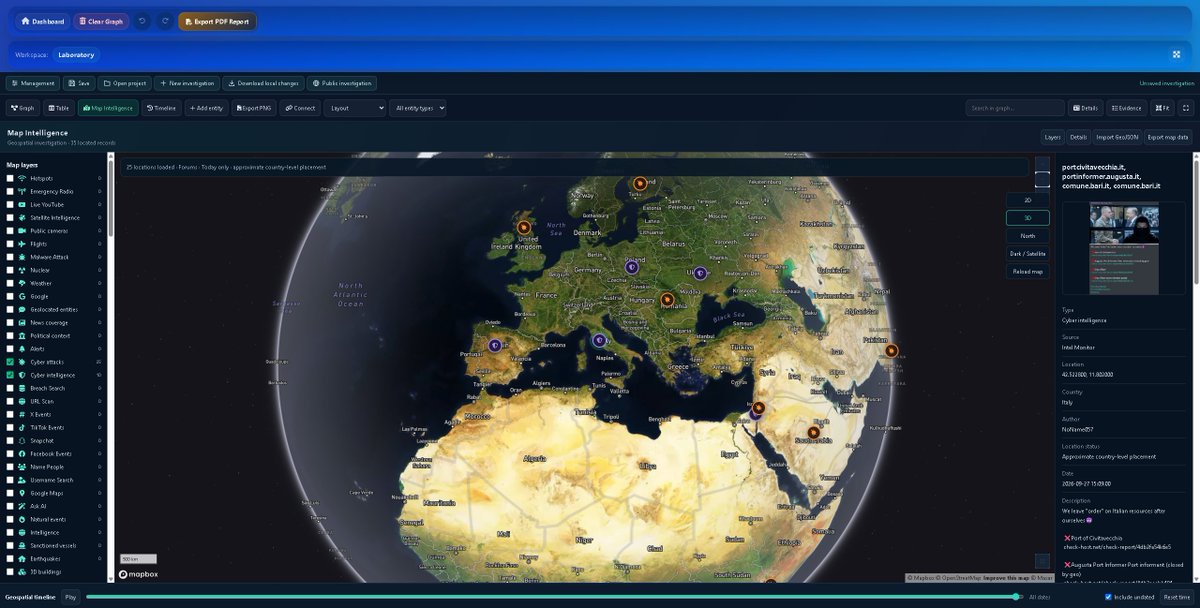
#15647, Italian ports and municipal sites (Civitavecchia, Augusta, Bari), NoName057, Italy, DDoS, 2026-09-27 15:09
#15646, Colombia API sale, vLeakz, Colombia, Analytical Study, 2026-09-27 01:23[cite: 16]
#15645, https://t.co/OUjOvAm8ak, vLeakz, Spain, Future Attack, 2026-09-27 01:22[cite: 16]
#15644, https://t.co/JCUWtyoOp4, 0x1A7, Unknown, DDoS, 2026-09-27 00:41[cite: 16]
#15643, CESCTM Vulnerability, zfo, Global, Exploit, 2026-09-27 00:28[cite: 16]
🔍 CRITICAL SIGNAL SUMMARY AND ANALYSIS
Massive DDoS Attacks and Critical Infrastructure:
Yemen Cyber Group: Reported Denial-of-Service (DDoS) actions against portals in the United States (idrtech. us, highspeedrural. us) and Israel (carsforum .co.il).
NoName057: Continues campaigns against European targets, notably claiming access to industrial control systems (HMI/SCADA for a bioreactor in Poland) and causing outages for portals in Ukraine and Italy (ports of Civitavecchia and Augusta).
Leaks and Threats Against Health and Government Entities:
Chile and Spain (#15654, #15645): The actor vLeakz is preparing the alleged release of data from the Redclínica institution in Chile and has issued direct threats against the official website of the Spanish National Police (policia. es).
Colombia (#15646): The sale of a comprehensive Colombian database API has been announced.
WebShell Deployment and Exploitation (#15653, #15643):
The actor xurl404 reports the presence of WebShells on global government and educational portals (including Canadian services and educational institutions). Meanwhile, the actor zfo has exposed a critical vulnerability in the CESCTM system.
🛡️ TECHNICAL PREVENTIVE AND CONTAINMENT RECOMMENDATIONS (SOC / CSIRT)
Active DDoS Mitigation: Organizations in the affected sectors (government, healthcare, and critical infrastructure) must keep protection services against volumetric and application-layer attacks (Cloudflare/WAF) active.
Perimeter and Web Server Audit: Review activity logs for unauthorized files (WebShells) and apply security patches for potential access control vulnerabilities.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ2Nli
Quickly check your security at: https://t.co/QZhWp0kFrO
Quotes and services: https://t.co/sx3BM5zbnK
#Cybersecurity #ThreatIntel #DDoS #SCADA #WebShell #DataLeak #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert
⚒️ 0xSQL v1.1 | SQL Scanner
This is a tool developed by the Anka Team that automatically discovers SQL vulnerabilities and tests them by sending payloads.
For details and to download: https://t.co/7X2r3GzyFK
#AnkaTeam#TurkHackTeam#Hack#TurkishHacker#0xsql#tool#sqlinject
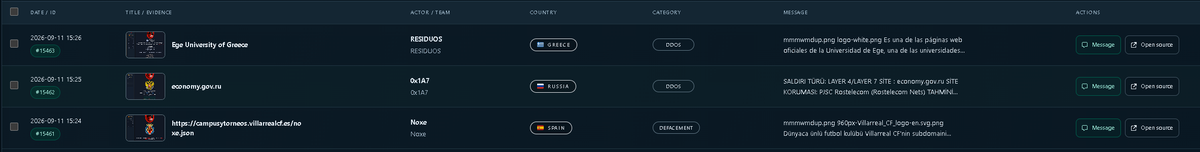
🚨 CTI ALERT 🇬🇷🇷🇺🇪🇸 | NEW HACKTIVIST ACTIVITY — RESIDUOS, 0x1A7, AND Noxe CLAIM RESPONSIBILITY FOR DDoS AND DEFACEMENT ATTACKS AGAINST A UNIVERSITY, THE RUSSIAN GOVERNMENT, AND VILLARREAL CF
[STATUS: UNCONFIRMED / TYPE: HACKTIVIST ACTIVITY · DDoS · DEFACEMENT · GOVERNMENT / EDUCATION / SPORTS TARGETING / COUNTRIES: 🇬🇷 GREECE · 🇷🇺 RUSSIA · 🇪🇸 SPAIN / DATE OBSERVED: 11-SEP-2026]
Cyber-intelligence monitoring has identified three new claims of responsibility published within a span of just minutes, targeting university, government, and sports infrastructure.
The observed incidents involve:
🇬🇷 Ege University (Greece) – Actor: RESIDUOS – Category: DDoS
🇷🇺 https://t.co/MMqCLHdNdy – Actor: 0x1A7 – Category: DDoS
🇪🇸 Villarreal CF / https://t.co/vL87VhyJBz – Actor: Noxe – Category: Defacement
⚠️ All three activities remain WITHOUT INDEPENDENT CONFIRMATION. Evidence shows the actors' posts and categorizations but does not, in itself, demonstrate sustained impact, prolonged disruption, or full compromise of the organizations.
🖥️ Centralized Threat Monitoring System:
https://t.co/wk9bZJ2Nli
Monitoring Console:
https://t.co/5LuqwzYuS6
#Greece #Russia #Spain #DDoS #Defacement #Hacktivism #VillarrealCF #GovernmentSecurity #EducationSecurity #CyberSecurity #ThreatIntel #CyberIntelligence #SOC #CSIRT #IncidentResponse #ThreatMonitoring #VECERT
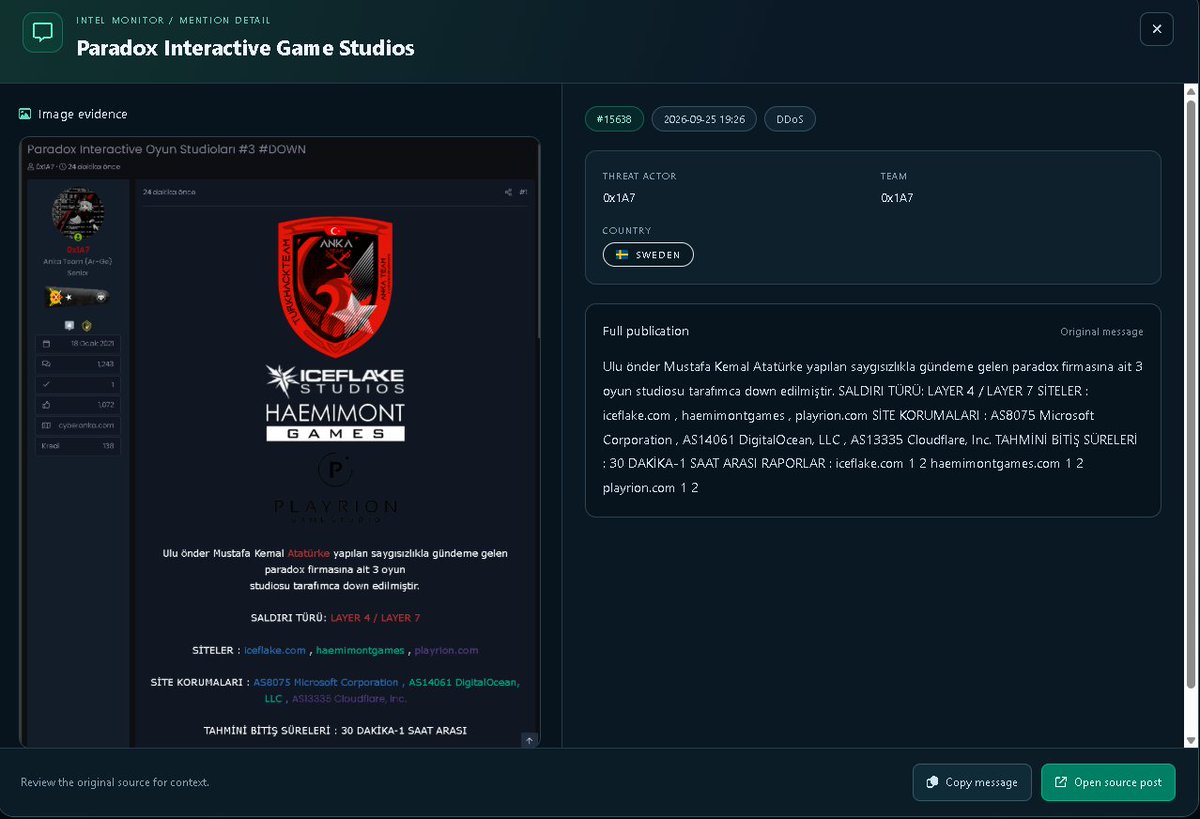
⚠️ CRITICAL PREVENTIVE ALERT 🇸🇪 🎮: ALLEGED DENIAL-OF-SERVICE (DDoS) ATTACK AGAINST PARADOX INTERACTIVE STUDIOS (ACTOR: 0X1A7 / ANKA TEAM)
[STATUS: UNCONFIRMED; EVIDENCE VISIBLE BUT NOT VERIFIED / THREAT ACTOR: 0X1A7 (ANKA TEAM) / DATE: SEPTEMBER 25, 2026]
Centralized cyber-intelligence monitoring has detected a post on underground forums, made on September 25, 2026, by user 0x1A7 (of the Anka Team group). The post announces that three video game development studios owned by Paradox Interactive have been taken offline via Denial-of-Service (DDoS) attacks.
It is strictly noted that the veracity of this compromise and the reported unavailability have not been officially confirmed by the affected company. The definitive scope remains unconfirmed.
🔍 TECHNICAL INFRASTRUCTURE BREAKDOWN
According to the information published by the actor, the targeted entities and their respective perimeter protections are as follows:
Iceflake Studios:
Domain: iceflake. com
Infrastructure Protection: AS8075 Microsoft Corporation.
Haemimont Games:
Domain: haemimontgames .com
Infrastructure Protection: AS14061 DigitalOcean, LLC. Playrion Game Studio:
Domain: playrion .com
Infrastructure Protection: AS13335 Cloudflare, Inc.
🛡️ PREVENTIVE TECHNICAL CONTAINMENT RECOMMENDATIONS (SOC / CSIRT / WEB INFRASTRUCTURE)
Volumetric and Application-Layer Traffic Mitigation: Infrastructure teams and DDoS mitigation providers (Cloudflare, Microsoft, DigitalOcean) must implement strict rate-limiting rules and JavaScript challenge validation to filter out malicious traffic targeting the affected domains.
Availability (Uptime) Monitoring: Continuously monitor server connectivity logs to ensure rapid service recovery in the event of traffic fluctuations.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ3laQ
Quotes and Services: https://t.co/sx3BM5zJdi
#Cybersecurity #ThreatIntel #DDoS #ParadoxInteractive #AnkaTeam #GamingSecurity #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert