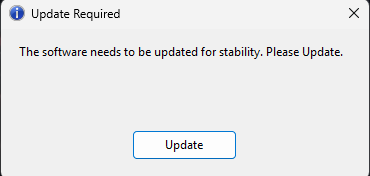
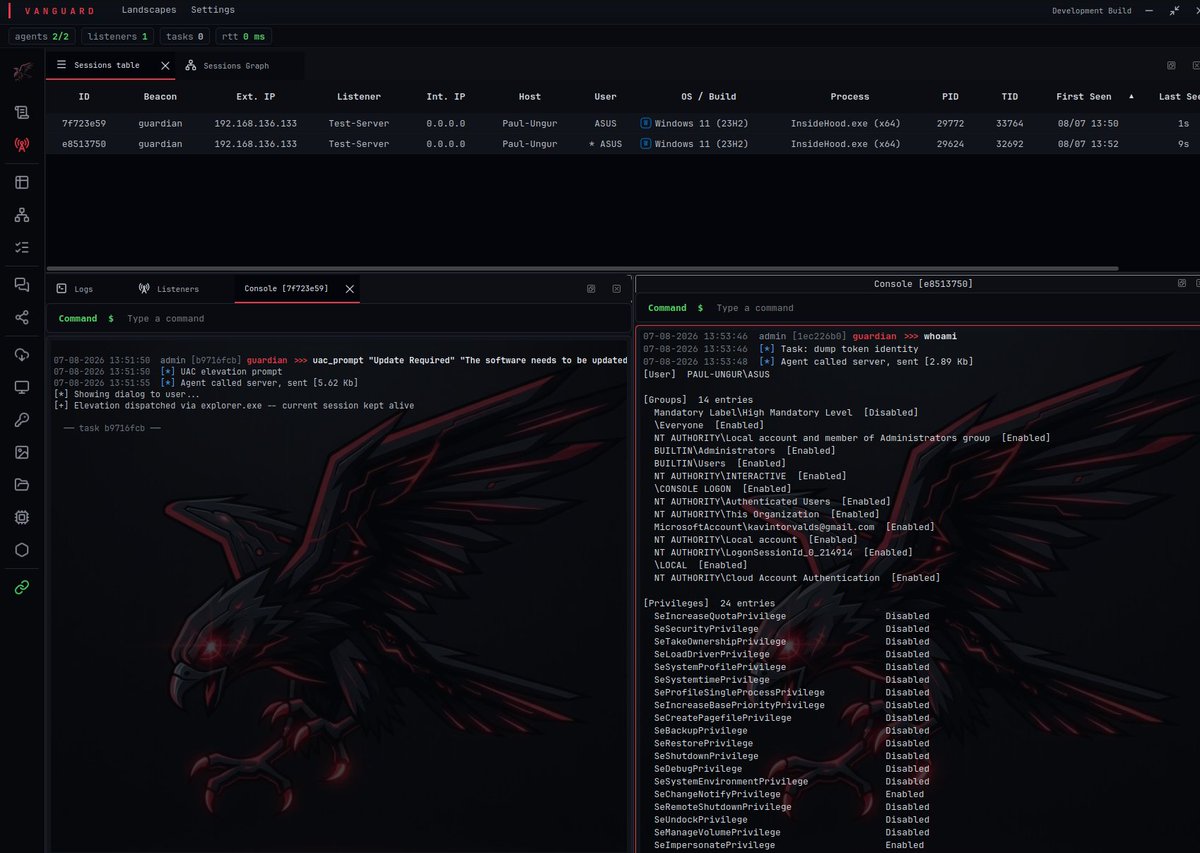
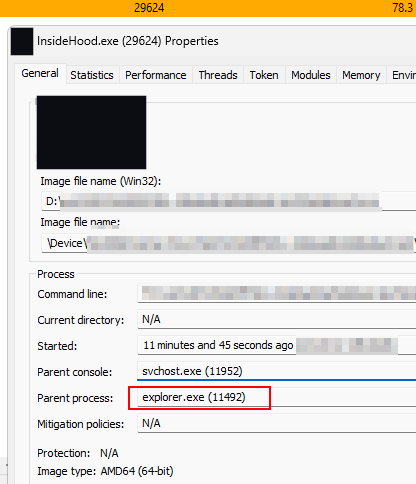
I wrote a BOF for social engineering UAC elevation. It pops a fake update dialog, and when the user clicks the button, the real UAC consent prompt appears. This works especially well in EDR environments. The same technique can also be used for credential related scenarios.
It walks IShellWindows to obtain explorer.exe's IShellDispatch2 via COM marshaling, then calls ShellExecute runas cross process. The actual elevation call stack lives entirely inside explorer.exe. The callbacks will be module backed code instead of unbacked stack. The parent PID will be explorer.exe. This is a known documented technique, but I have never seen anyone implement a BOF works within a memory since that is a lot of pain debugging stuffs, so I decided to try it.
The dialog box can be improved significantly since this is just a PoC =)
> I think Next development should be GetAsyncKeyState, LDAP Query BoF, a default plugin for file operations like cp, rm, mv, rename etc !!
> EkkoFrozenTwin inspred by Ekko = )
Just documenting my journey and sharing stuffs =)
An anonymous GitHub account is mass-dropping exploit PoCs framed as undisclosed 0-days, with a note telling readers to report them and "take credit for the CVE" themselves.
Coordinated disclosure, minus the coordination.
Une vulnérabilité de sévérité CVSS 7.3 a été corrigée sur l’outil de collecte DFIR-ORC développé par l’ANSSI. Elle permet à un attaquant d'obtenir une élévation locale de privilège. Le bulletin de sécurité et les versions correctives sont ici : https://t.co/rp7i4VKvo0
We are investigating unauthorized access to GitHub’s internal repositories. While we currently have no evidence of impact to customer information stored outside of GitHub’s internal repositories (such as our customers’ enterprises, organizations, and repositories), we are closely monitoring our infrastructure for follow-on activity.
💥 Introducing "Dirty Frag"
A universal Linux LPE chaining two vulns in xfrm-ESP and RxRPC. A successor class to Dirty Pipe & Copy Fail.
No race, no panic on failure, fully deterministic. ~9 years latent.
Ubuntu / RHEL / Fedora / openSUSE / CentOS / AlmaLinux, and more.
Even if you've applied the "Copy Fail" mitigation, your Linux is still vulnerable to "Dirty Frag". Apply the Dirty Frag mitigation.
Details:
https://t.co/9nqku4svkY
GitHub - samftggr/VEN0m-Ransomware: Demonstrate how a signed driver can bypass defenses to deploy ransomware on Windows 11 with advanced AV and UAC evasion techniques. · GitHub https://t.co/bMPcb44YVI
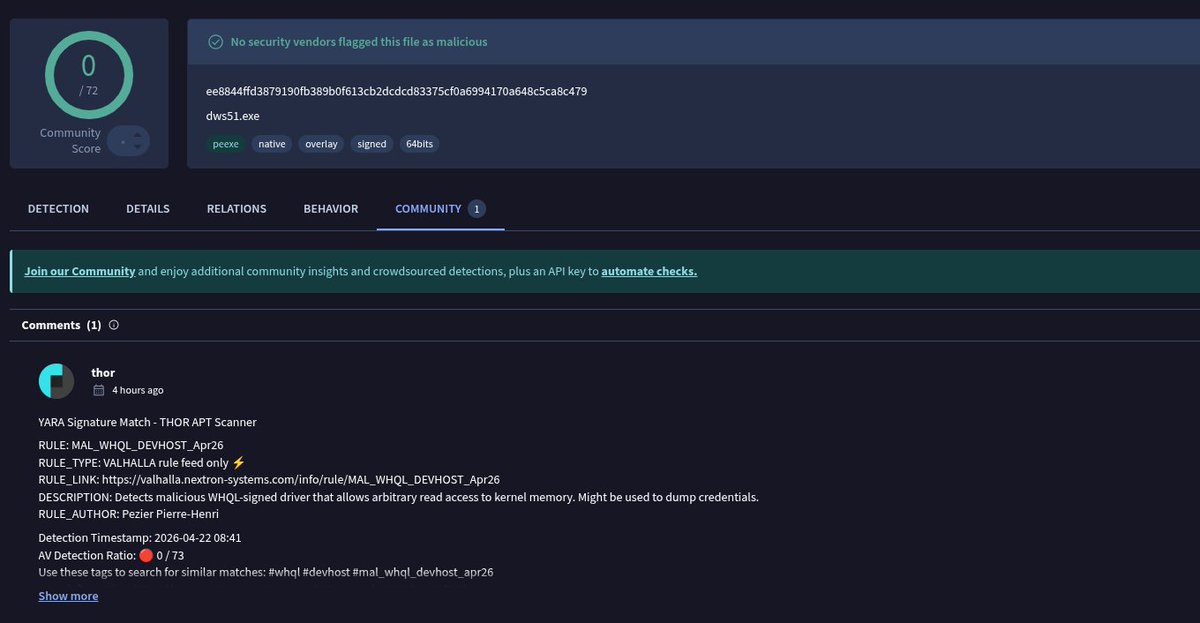
WHQL-signed Windows kernel driver that hands any user-mode caller an arbitrary memory read primitive
This primitive is basically tailor-made for credential stealers i.e. LSASS dump
- Opens as \.\devhost - no ACL beyond a device handle
- Exposes the kernel page-table root at load - user-mode can walk page tables itself
- Arbitrary physical memory read (MmMapIoSpace)
- Arbitrary kernel virtual memory read (MmCopyMemory, SEH-safe)
SpcSpOpusInfo = 深圳市奥联信息安全技术有限公司, submitted from china 📷 ee8844ffd3879190fb389b0f613cb2dcdcd83375cf0a6994170a648c5ca8c479 - devhost.sys
Just pushed a minor update to #mimikatz 2 🥝(no - it's *NOT* the version 3) to support specific GMSA DPAPI passwords in LSA secrets to be able to to decrypt Masterkeys
> https://t.co/UNUIxSOhtS
Only for @topotam77 convenience ;)
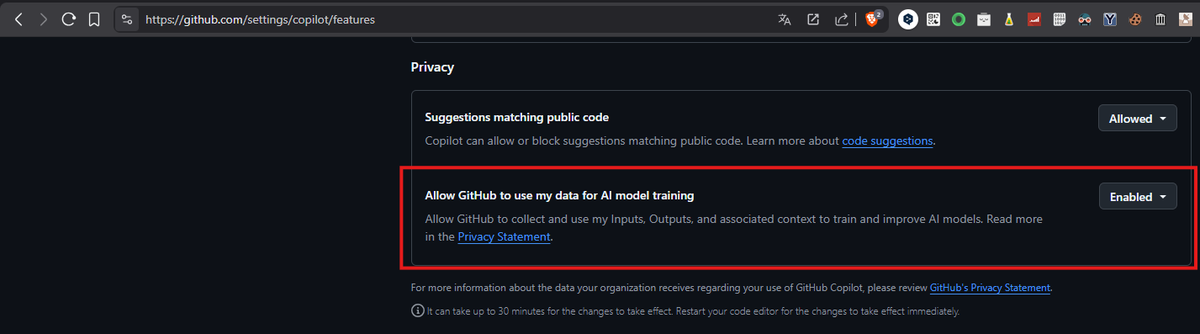
Si vous avez du code non libre hébergé sur #Github et que vous ne souhaitez pas qu'il serve à entrainer l'IA #Copilot il va falloir faire un opt out ! On peut imager que tout ce qui est déjà en #CC0 ou #WTFPL est déjà utilisé et de toutes façons ... c'est du code publique. Concernant la license #GPL c'est autre chose, c'est en cours de jugement apparemment, mais préparez vous au futur changement des CGU imposant l'entrainement de Copilot en hébergeant une instance #Gitlab ou en contactant :
.@bearstech qui savent très bien faire ça ! :)
The Mimikatz Missing Manual
TLDR; The project is the culmination of years of technical research and specialized training material originally developed for private classes at security conferences. This information was only shared behind closed doors.
https://t.co/sv94J8vD88
Recipe for deobfuscating second-stage of new #ClickFix that uses nslookup via CyberChef:
Regular_expression('User defined','@\\((.*?)\\)',true,true,false,false,false,false,'List capture groups')
From_Decimal('Comma',false)
A couple weeks ago, @fabian_bader and I launched an unofficial PowerShell module for Defender XDR
With this module, you can perform tasks and access data that are not possible via official APIs 🔥
Check out the video below, we're just getting started
Welcome to XDRInternals :)
🏭 Chaque installation #industrielle présente des particularités et des risques propres qu’il convient d’analyser pour déployer des mesures de sécurisation adaptées.
📚 Pour aider à leur mise en œuvre, l'ANSSI publie un nouveau guide :
https://t.co/hqkEGxDSBm
📚 Les guides de l’ANSSI sont sur #MesServicesCyber !
🖥️ Alors que le site de l’ANSSI évolue, MesServicesCyber se transforme pour vous simplifier l’accès aux conseils et recommandations de l’ANSSI, et de ses partenaires.
Rendez-vous sur :
🔗 https://t.co/f1L3lTZkHz