Ultimate regret of buying @VW Virtus 2025
Hi everyone,
I am posting here because I am completely exhausted dealing with my @VW Virtus issue and I honestly do not know what to do next.
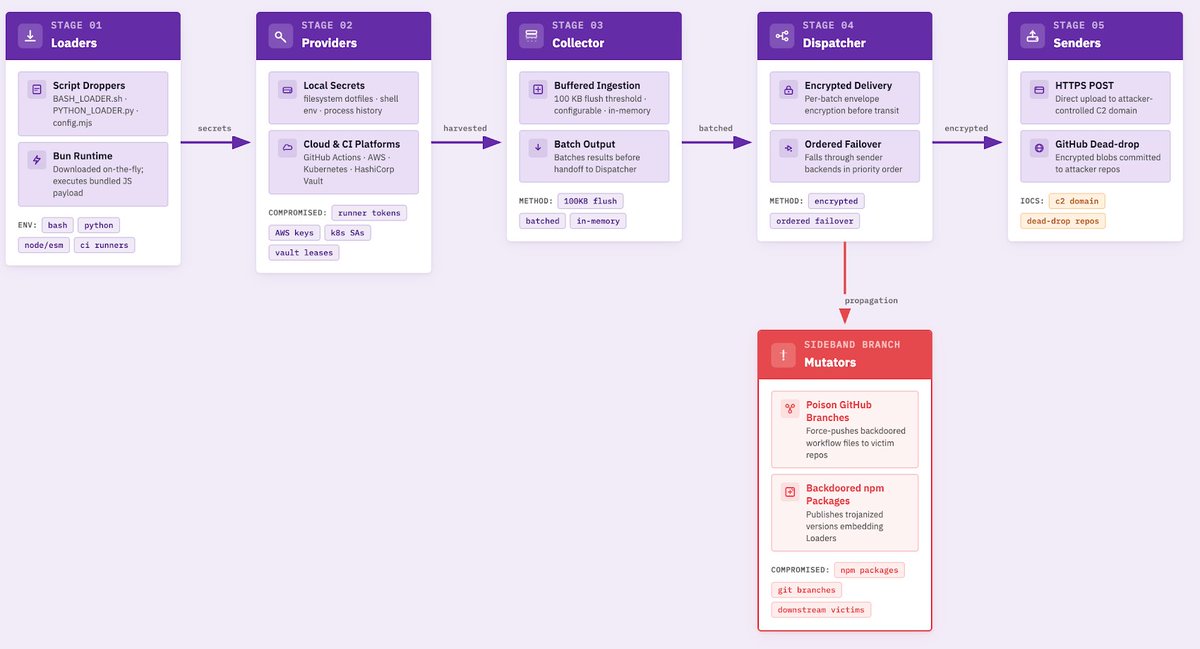
Mini Shai-Hulud npm worm is back.
This time it hit 300+ packages, including AntV packages, echarts-for-react, timeago.js, size-sensor, and canvas-nest.js.
A compromised npm account published hundreds of malicious versions in just ~22 minutes.
The payload ran through a preinstall hook.
Meaning: you didn’t need to use the package.
Installing it was enough.
It hunted for GitHub tokens, npm tokens, AWS/GCP/Azure creds, DB strings, Stripe keys, Slack tokens, SSH keys, Docker auth, Kubernetes configs, Vault tokens, and more.
It also tried Docker escape if the host socket was exposed.
And the nastiest part?
It targeted CI/CD, GitHub workflows, and even AI coding tool hooks like Claude/Codex session startup.
Modern software supply chain security is basically:
“Do you trust this dependency?”
Wrong question.
The real question is:
“If this dependency turns evil for 20 minutes, how much of your company does it get access to?”
security hot take:
most companies don’t have a vulnerability problem
they have an ownership problem
everyone knows the old admin panel exists
nobody owns it
everyone knows the staging server is public
nobody owns it
everyone knows the API key is shared
nobody owns it
attackers don’t exploit code first
they exploit the gap between “someone should fix that” and “who exactly?”