@DevJuyoung One could wonder how billionaires and top people communicate in their circles.
Imagine you have 1B+ usd.. That means power, reach, connections. You know things before most others.
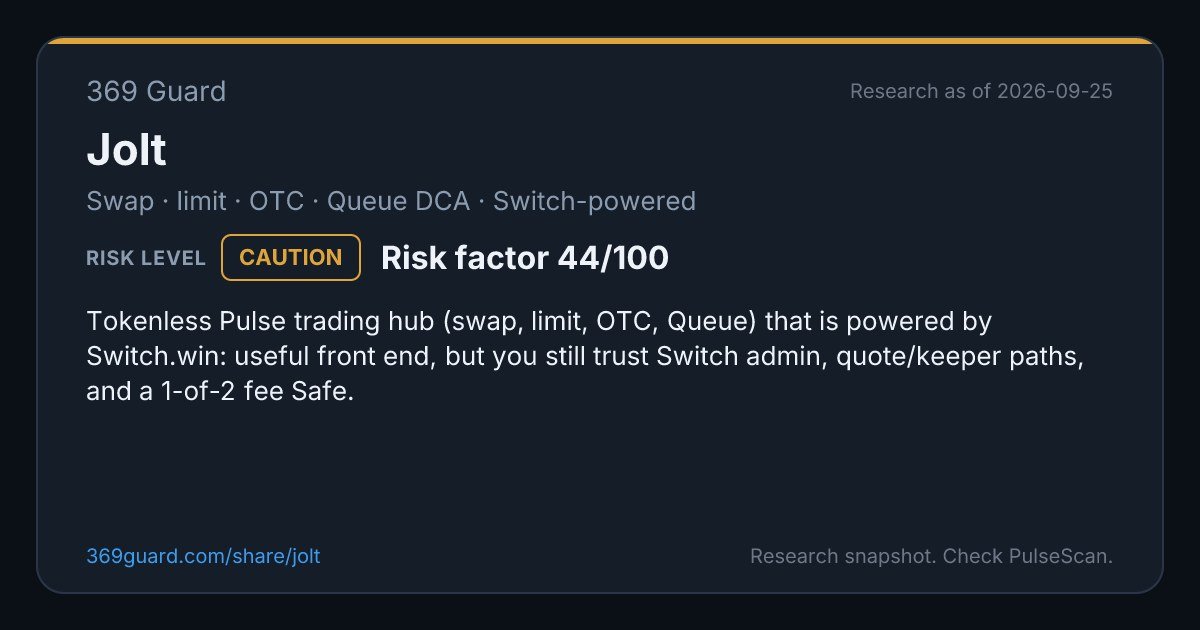
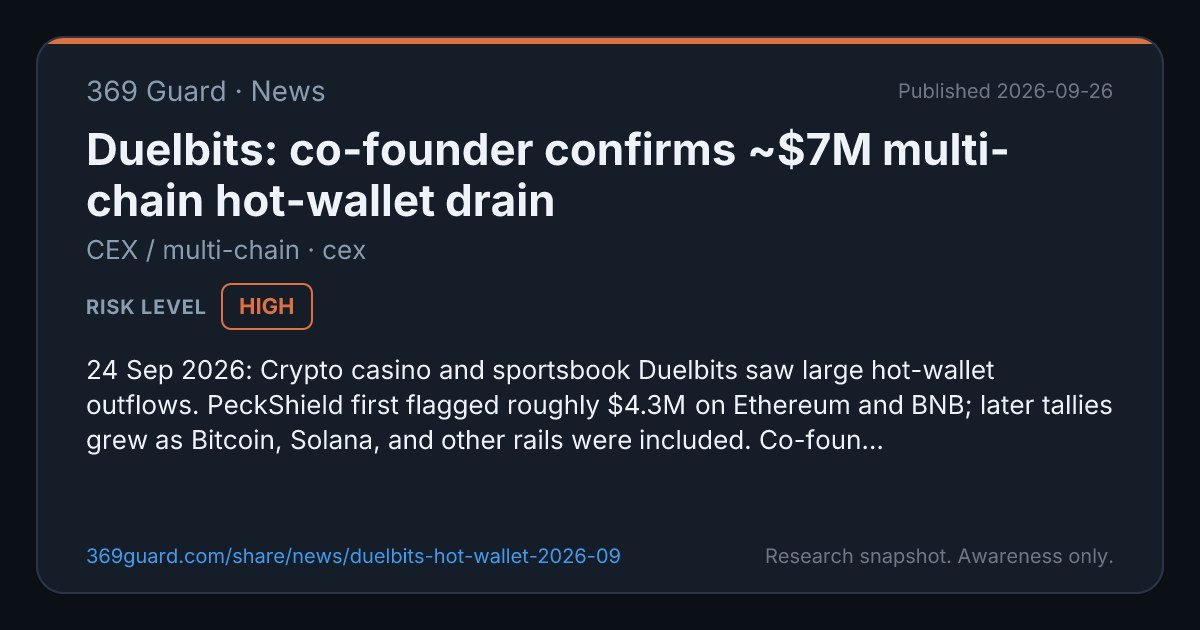
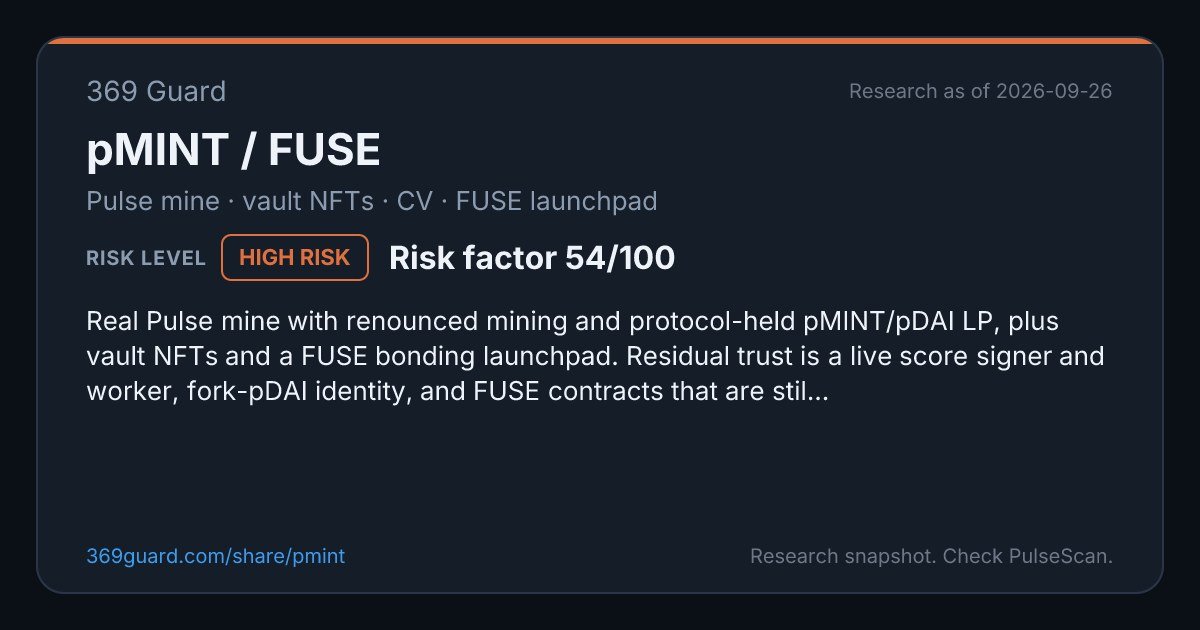
A few days of house-keeping on 369 Guard 🛡️
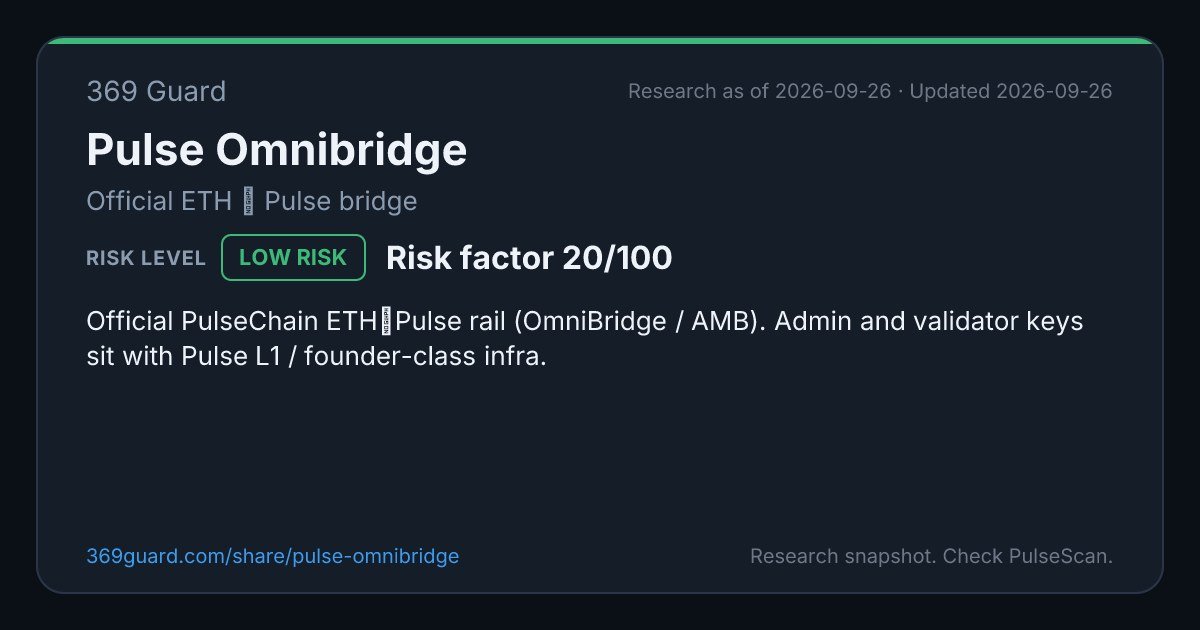
The board is easier to browse. Header been imrpoved. Live watches stay filled more reliably. Share cards show the preview art again. And www now lands cleanly on https://t.co/niVVz6ptjO with a real padlock 🔒
We also did a hardening pass: clearer official domain, stronger basics against poking and spam, and a cleaner path when someone asks for a card update.
Same idea as always:
Standing research before you ape. Research snapshot. Check PulseScan.
@Tobiwan_Hexobi It takes a while to understand Hex staking tshares fully. from weeks to a year. But once the lightbulb moment comes, there is no returning back.
369 Guard News · CEX / multi-chain
Bitget: ~$387.5M from hot and warm wallets; path claimed remediated
24 Sep 2026 ~18:31 UTC:
unauthorized spends from Bitget hot and warm wallet layers. Early press put the figure near $351.6M. Bitget’s 25 Sep support update raised the confirmed attacker take to about $387.5M after fuller Zcash and TRON accounting, and said the incident is contained with no further unauthorized transfers.
Chains and assets named include Ethereum and other EVM rails, XRP Ledger, Zcash, and TRON (XRP, ETH, USDT, USDC, BNB, AVAX, ZEC, TRX and more). Bitget says it identified the attack path, remediated the underlying vulnerability, and is working with Mandiant and SlowMist. Withdrawals were paused while validation continues; a recovery bounty and live tracing dashboard were published.
User Protection Fund coverage remains their claim. PulseChain was not hit. Research snapshot from Bitget support plus earlier on-chain press notes.
Update · 2026-09-26 · Official revise to ~$387.5M; Mandiant and SlowMist; bounty live
26 Sep Grok window digested Bitget’s 25 Sep support post: confirmed attacker take raised to about $387.5M (adds Zcash/TRON accounting, not a second drain). Bitget claims the vulnerability is remediated, investigation continues with Mandiant and SlowMist, and published a recovery bounty plus live tracing dashboard. Title and summary refreshed to match.
Why it matters:
Exchange hot and warm wallets remain a single blast radius. Bitget now says the path is fixed and Mandiant / SlowMist are on the case; treat that as their statement until withdrawals resume and users are made whole.
Bags you do not need for trading belong on keys you control.
Protection-fund and bounty programs are recovery marketing until funds land back with users.
Before you connect your wallet to another PulseChain dApp… check the risk first
Follow @369Guard for risk checks on the protocols you're using
#PulseChain $PLS $PLSX $HEX $INC $PRVX
Thanks for the Q.
There are higher scores on website. Set criteria to severe.
Projects may have a high rate, specially when newer, but they can improve, that is one of the purposes with 369guard.
Nudge to improvement and awareness to users.
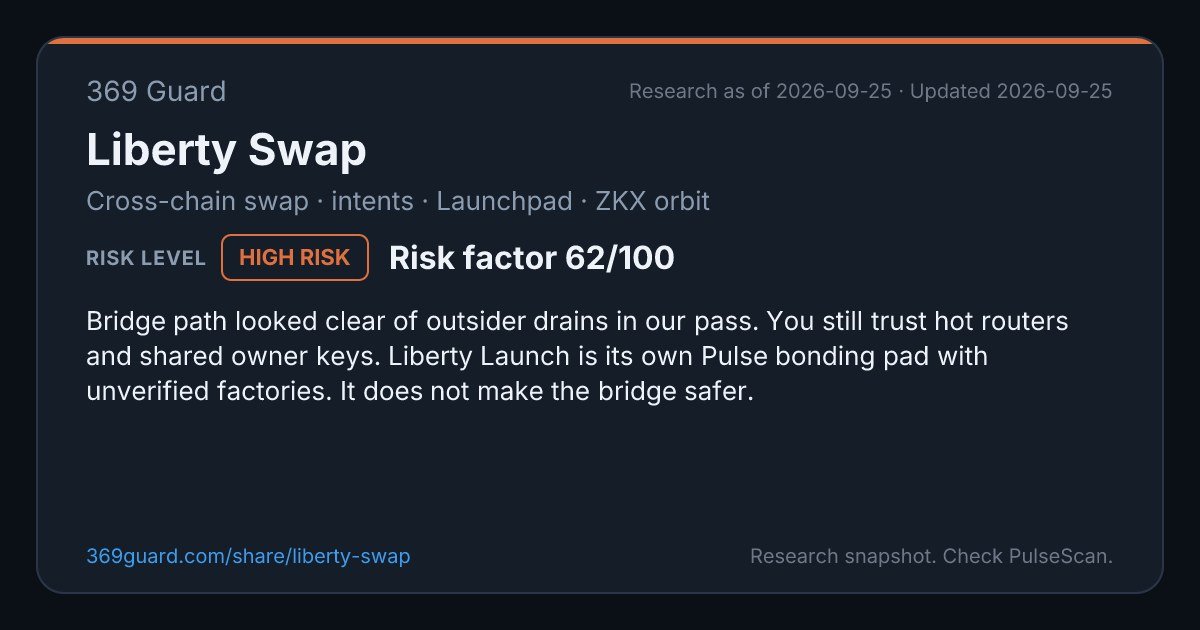
Higher score = more concern. We score surfaces with a fixed A–F checklist (price games, vault math, oracles, who holds keys, timing, code basics), then put a 0–100 on top. Liberty sits high because hot routers + shared owner keys + a separate Launchpad factory risk. Not because “bridge = bad.”
Classes that interest us most are hot-key bridges, residual LP, upgradeable vaults, oracle/keeper prints. Staying neutral on specific projects.
Tools are boring on purpose. PulseScan / Sourcify, RPC reads, pair/liquidity checks, and our own review checklists. No oracle that auto-rates for us.
Board research is free.
Coming optional tips only buy queue time for a new card or update refresh.
Paid internal deep reviews and other services do alos exist, to be announced later.
Money never buys a greener score, but can update you faster or help fix your issues.
https://t.co/niVVz6ptjO