Security and compliance tool; Detect, alert and respond to changes in your IT environment. File Integrity Monitoring #PCIDSS#cybersec#infosec#ITSecurity
A lot of Zero Trust attention goes toward who's allowed in. Less goes toward noticing when something inside quietly changes without approval.
That's the idea behind Tenet #5. Check out the full breakdown of all 7: https://t.co/nkQFR7E51w
#fileintegritymonitoring#cybersecurity #zerotrust
Network devices, databases, hypervisors, Windows, and Linux.
If your FIM tool only covers some of that, you're only getting half the picture. Which kind of defeats the point of monitoring in the first place.
Multi-platform support made our list of 9 features actually worth paying for: https://t.co/5Ce33sY94U
Secure configuration is the foundation of both cybersecurity and compliance.
Applying CIS Benchmarks in a practical, scalable way can help strengthen security posture, support frameworks like PCI DSS and NIST CSF, and move beyond point-in-time assessments toward continuous compliance.
Read the full blog: https://t.co/ErVOFKk3sl
#Cybersecurity #CISBenchmarks #CybersecurityCompliance
"Can I use agent-based and agentless FIM together?"
Actually, yes, and a lot of teams do. Agent-based on critical, high-risk systems. Agentless on lower-priority assets.
It's not always either/or. Sometimes it's both if layered right.
Learn more in the blog: https://t.co/xJLN9Wapd7
Real Zero Trust environments can generate thousands of alerts a day. Continuous monitoring only works if you can actually tell which alerts matter.
Here's how to keep that from becoming a full-time job: https://t.co/1wGuW1V2kQ
"Cybersecurity as insurance" is a pitch that stopped working a while ago.
Today's businesses run on information flows that touch every department and customer interaction, so it's time to budget accordingly.
Learn more: https://t.co/bttjA4PFit
File change detection ≠ true FIM.
This blog puts vendor claims to the test using a NIST-based benchmark analysis, clarifying what true File Integrity Monitoring really requires.
Read the blog: https://t.co/IXJ7d9vpuK
#cybersecurity#fileintegritymonitoring#FIM
Not every file change is a problem.
But every problem starts with a file change.
See how File Integrity Monitoring tells them apart: https://t.co/lSwmgK8u1A
#fileintegritymonitoring#cybersecurity
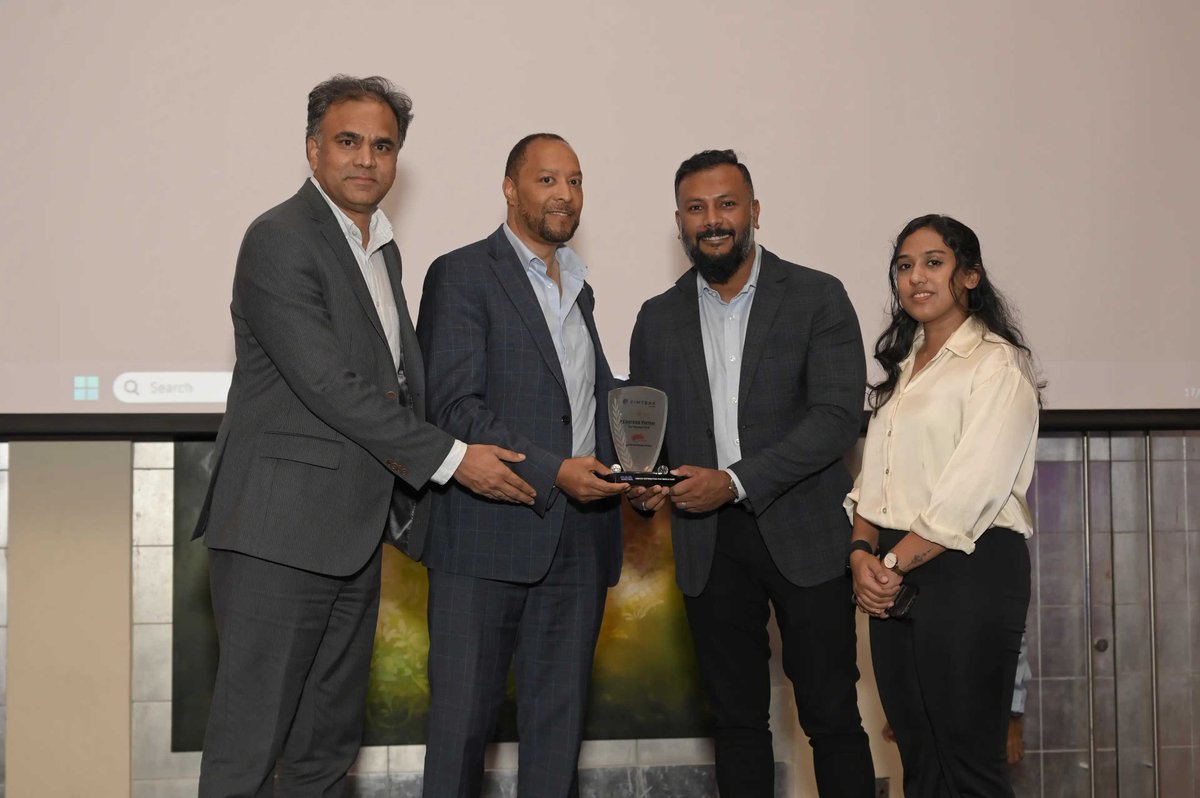
A great evening in Dubai at the @RasInfotech Meet & Greet Gala Dinner and Reseller Award Ceremony.
Thank you to RAS Infotech, our distributor across the region, for the partnership and the ongoing support that makes our work in the Middle East possible. It was a pleasure to celebrate the night with you.
Congratulations to the #CimTrak partners recognized this year:
Green Method, Best Partner 2026
Unicorp Technologies, Best Partner 2026
Visnet, Emerging Partner 2026
These awards reflect a real commitment to helping customers keep their critical systems secure, and we're grateful to have partners like you in the region.
#GISEC2026 #Cybersecurity #InfoSec #SystemIntegrityAssurance
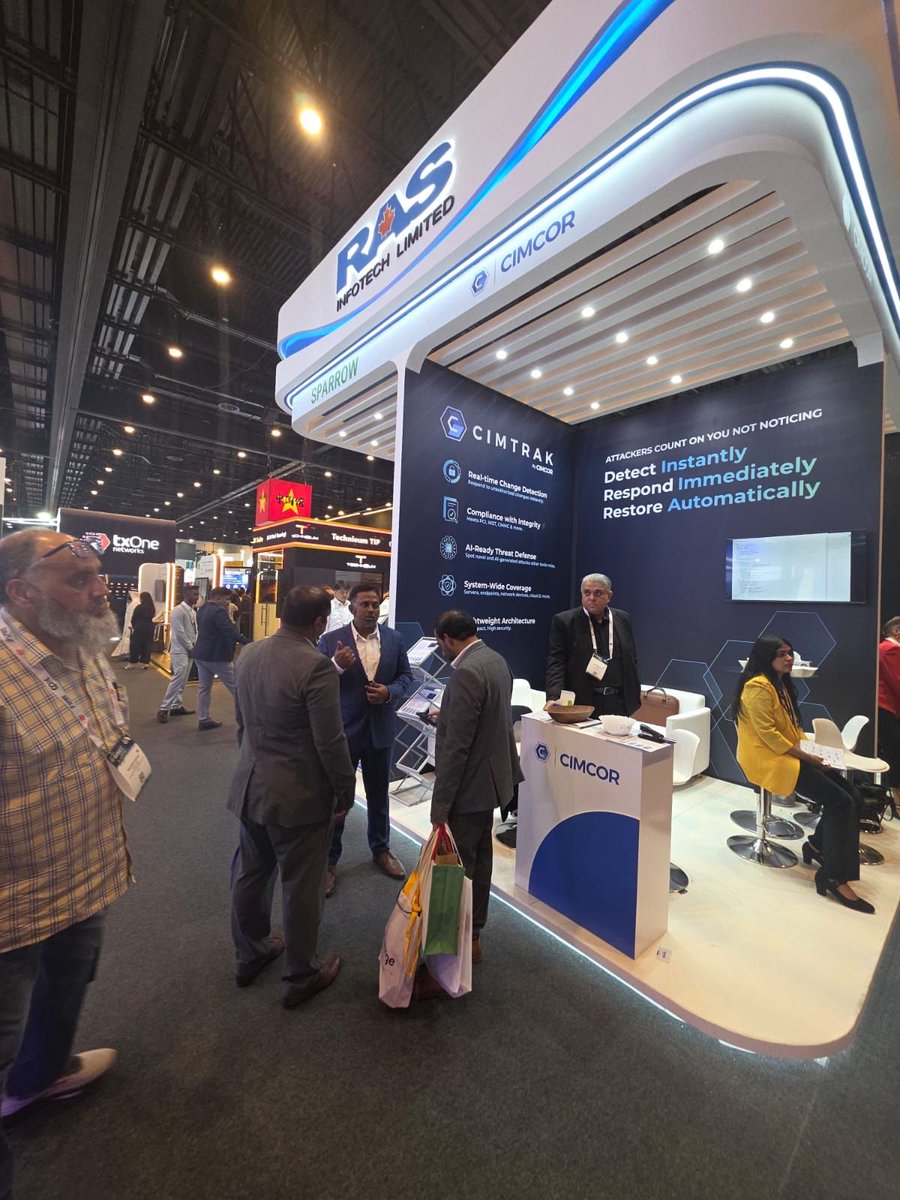
Always great to see so many of our global partners in person. Thank you to the eProcess Consulting team for stopping by our booth at #GISEC
More to come from Dubai. Come find us today in Hall 8, Booth E130 ✨
Up to 60% of attacks involve insider threats. Most perimeter security is built to stop outsiders.
See the gap? Zero Trust closes it.
Learn how to get started in your environment: https://t.co/z5TdWl9yo4
GISEC Day 1 ✅
The Cimcor team had a great first day in Dubai. Thank you to everyone who stopped by to say hello and share thoughts, challenges, and ideas. It's always the best part of these shows!
We're back at it tomorrow, and it's a big one for us: our President and CEO, Robert E. Johnson III, has two speaking sessions on the schedule:
1:00pm: Cyber Talks: Continuous Control Assurance (CCA) — From Static Assessments to Living Risk Intelligence
2:10pm: Integrity Assurance in the Age of Agentic & Malicious AI: Keeping Systems in a State You Can Trust (X-Labs Stage, Hall 7)
For some 1:1 time, come find us in Hall 8, Booth E130.
See you there!
#GISEC2026 #Cybersecurity #InfoSec #SystemIntegrity
Zero Trust principles are a bit like "eat healthier." Directionally right, but not much to act on.
NIST's 7 tenets are closer to an actual plan: specific enough to build against, which is likely why they get less attention than the philosophy does.
Learn more: https://t.co/5ZDfkpSwgg
#fileintegritymonitoring #cybersecurity #zerotrust
Before you pick agent-based or agentless FIM, ask:
1. How virtualized is your environment?
2. Compliant, or actually secure?
3. Can you grant external privileged access?
4. How much nuance do you need in reporting?
5. How stretched is your IT team?
6. Are you scaling your security program?
Your answers point you toward the right fit. Check out the full breakdown: https://t.co/e7klU6d3BE
Agentic AI is making changes across enterprise systems faster than any team can review them. Attackers are using the same technology to find new vulnerabilities just as fast, and traditional vulnerability management is struggling to keep up.
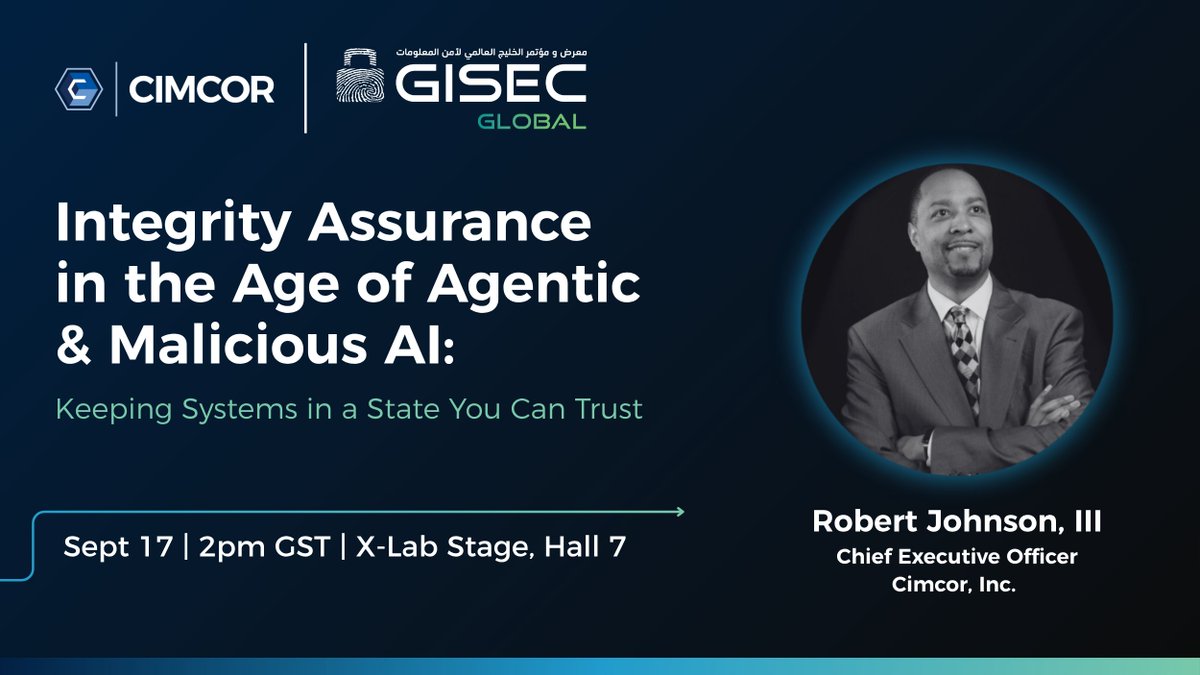
Our President and CEO, Robert E. Johnson III, is speaking at GISEC Global 2026 on how to keep your critical systems in a state you can trust.
His session covers System Integrity Assurance, a continuously verified approach that confirms your systems are in a known-good state the moment a change happens, and rolls them back automatically – even when it's an agent that made the change.
If you're putting AI agents into production, come see how integrity holds up. Details below.
#GISEC2026 #Cybersecurity #SystemIntegrityAssurance #Compliance #InfoSec
Vulnerability exploitation is now the top way breaches start.
An exploited vulnerability opens a door and usually leaves a trail of file and config changes behind it.
If your FIM tool can't pick up on that trail, it's not really doing its job: https://t.co/ZWWlHhEDRy
#fileintegritymonitoring #cybersecurity #compliance
Most breaches don't fail because attackers got in. They fail because once inside, nobody stopped them from moving around.
That's the gap Zero Trust is built to close. https://t.co/LjVnbm3lsT
Detection isn’t the same as control.
Many security tools alert when something goes wrong, but they don’t enforce whether systems remain in a trusted, known-good state.
Learn how SASE + integrity assurance creates a closed-loop security model that operationalizes Zero Trust, enables real Comply-to-Connect (C2C), and helps stop ransomware before damage occurs.
Read the blog: https://t.co/HpWGykUXiA
#ZeroTrust #Cybersecurity #RansomwareDefense #C2C
A €530 million fine. That's what happens when data governance gets treated as an afterthought.
New on the blog: why leading organizations now treat secure data governance as a strategic investment, not a compliance checkbox.
https://t.co/tpP3Oz6dkZ