Running third-party or unknown Python code is one of the fastest ways to introduce serious risk onto your system.
https://t.co/WMKPlEMeVR
#python#cybersecurity#cybersecuritytips
Obfuscation using Base64 is a simple technique to conceal malicious code in #Python projects. It enables #attackers to hide payloads that would otherwise be easily identified.
So use https://t.co/vSLq9Q5MbG
#pydata#openai#mythos#infosec#owasp
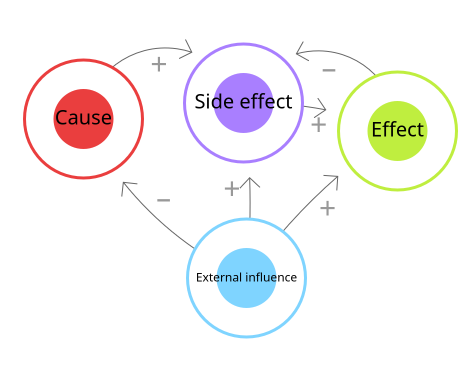
Een online tool om direct een Causal Loop Diagram(CLD) te maken. Een CLD tool helpt je om voor complexe systemen en problemen oorzaak-en-gevolg relaties snel, overzichtelijk te visualiseren en te analyseren.
https://t.co/SJyAF8WUAt
#architectuur#oplossingen#cld#ontwerp
Stop path traversal, zip bombs, and malicious file uploads before they hit your application logic.
#Python File Audit protects your code from file-based attacks with one line -> @validate_zip
https://t.co/oFdneYK3kj
#pydata#pycon#owasp#mythos#infosec#cybersecuritytips
Processing untrusted GZip files can lead to:
•Zip bombs
•Denial of service
•Path traversal
•TOCTOU attacks and more #unwanted things
So use just one line @validate_gz
To be #secure
https://t.co/oFdneYK3kj
#python#infosec#pydata#hackernews#mythos
loading csv files can result in a security nightmare. So check!
@validate_csv
def process_csv(csv_path):
text = Path(csv_path).read_text(encoding="utf-8")
return f"Processed {len(text.splitlines())} lines from {csv_path}"
https://t.co/oFdneYK3kj
#infosec#pydata#appsec
File Audit – Simplify #Python Secure Programming by adding one line! Build secure Python applications by default. Validate files before you use them.
Be resilient for #mythos and #ai#threat
https://t.co/oFdneYK3kj
#pycon#PyTorch#pydata#pandas
Research found that approximately 45% of AI-generated code failed security tests.
So check your #python apps before use! Its simple, use
https://t.co/vSLq9Q5MbG
Runs in your browser. Zero data sent to servers. No #telemetry.
#pydata#mythos#CyberSecurity