It starts on a finance workstation. By the time anyone notices, the attacker is covering their tracks. 🔎
The eCIR Skill Checks drop you into a live SIEM to trace the full attack.
👉Think you could follow the trail? Explore the path: https://t.co/KIbTRm5rdf
Attackers didn’t need a clever prompt. They went through the engine running the AI ‼️
That’s how an AI company was breached this week, exposing 18 AI agents.
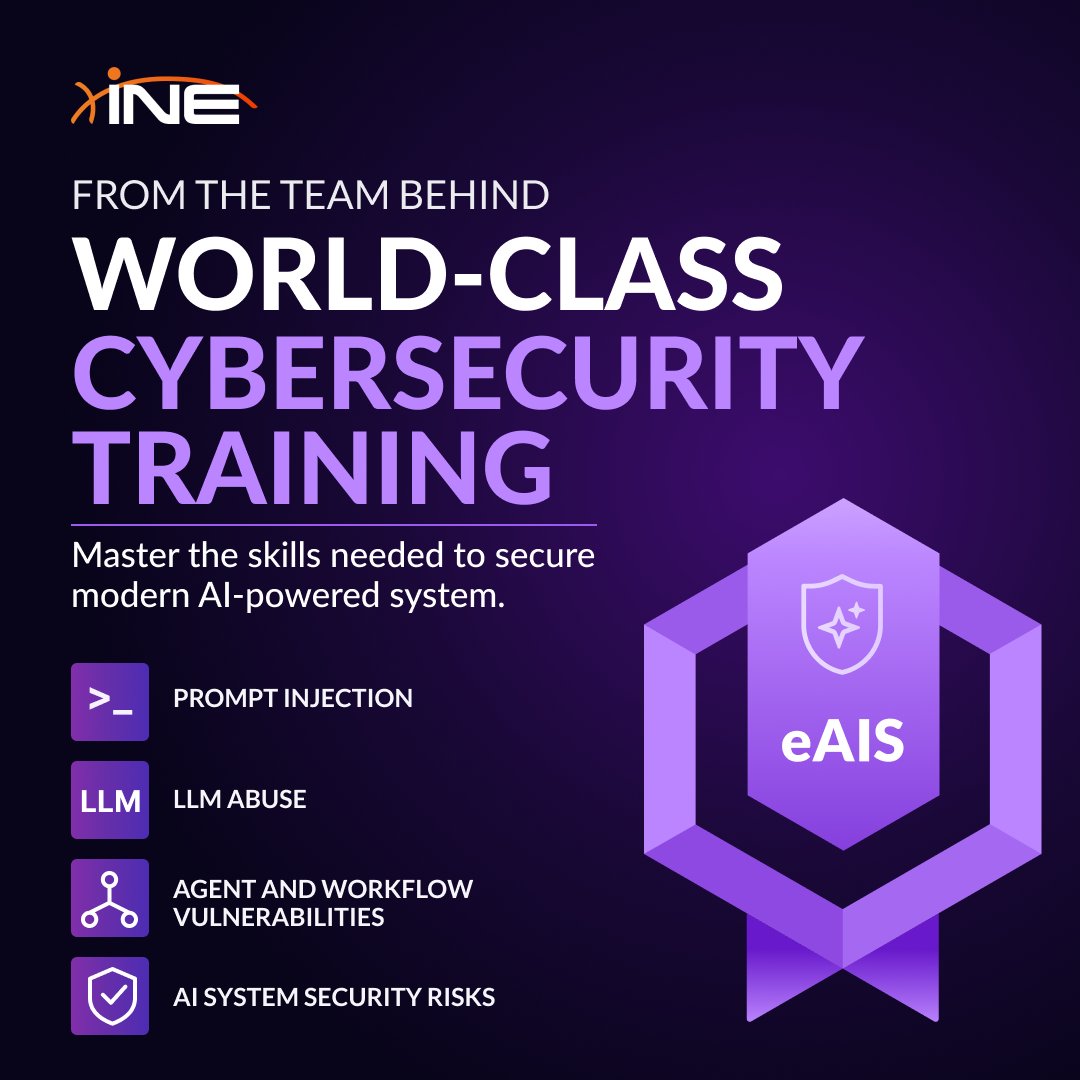
👉Would your team have spotted it? Find out with eAIS: https://t.co/P5e7XnWW7U
Responding to alerts is the job. Finding threats before they fire is the skill. 🔍
Shoutout to everyone already eCTHP certified.
👉Ready to join them? Explore the eCTHP path: https://t.co/rHFJOcMAPL
Think you’d catch these in the wild? Try running them first 🔓
New in Skill Dive: 9router, ComfyUI-Manager, and Apache ActiveMQ labs.
👉Pick a target and dive in: https://t.co/ZX1guPfiUe
Free content isn’t free. You pay for it in time. ⏳
→ Hours deciding what to watch
→ A tutorial that skips a step
→ A month on the wrong topic
Free is a great start. A plan gets you to the finish line.
🔁 Repost if you’ve lost a weekend to the wrong tutorial.
You told us you learn best by doing. Employers hire that way too. 🎯
Some entry-level certs can be memorized. The eJPT can’t. Start your pentesting path the right way 👉https://t.co/Wp9sboqLdP
Five days. 100+ companies. One shared goal: securing the hardware we all rely on. 🔌
That’s why INE is joining https://t.co/O49U463lEr NL 2026 as a strategic learning partner.
Find us in Amsterdam 👋 https://t.co/kpdZt8xakw
Two candidates. Same resume. One can explain how they exploited a real CVE the week it went public. 💼
Who gets the offer? Build your story on Skill Dive: 👉 https://t.co/8ixxeeA9P6
Repeat after me:
In 2027, I will…
→ Land my first tech job
→ Earn the cert I’ve been putting off
→ Get that promotion
→ Finally go from CCNA to CCIE
🔁 Repost if you’re checking off at least one of these.
New lab, real CVE, 30 minutes. 🧩
PHP2Shell drops you into a real PHP 8.4 use-after-free. Your mission:
→ Find the stale pointer left behind between requests
→ Reclaim the memory it points to
→ Turn it into full code execution
👉 Take on PHP2Shell: https://t.co/5v8As0F6U6
A company that tracks criminals for a living just had to lock out every one of its customers.
Chainalysis confirmed all users’ credentials and live tokens were exposed.
When attacks start with a login, eIAMA helps your team protect it 👉 https://t.co/GKo0h8zFZI
Cyber skills are universal. Learning them shouldn’t depend on your language. 🌍
👉See what the partnership includes and what’s next for learners in the region: https://t.co/k0h8cWBNKE
You ignored the sketchy email. Your AI summarized your inbox and called it urgent. 👀
That’s prompt injection, hidden instructions only AI can see. The eAIS Learning Path shows you how to stop it.
👉 Before you trust the summary, learn the attack: https://t.co/asTMzkDw2f
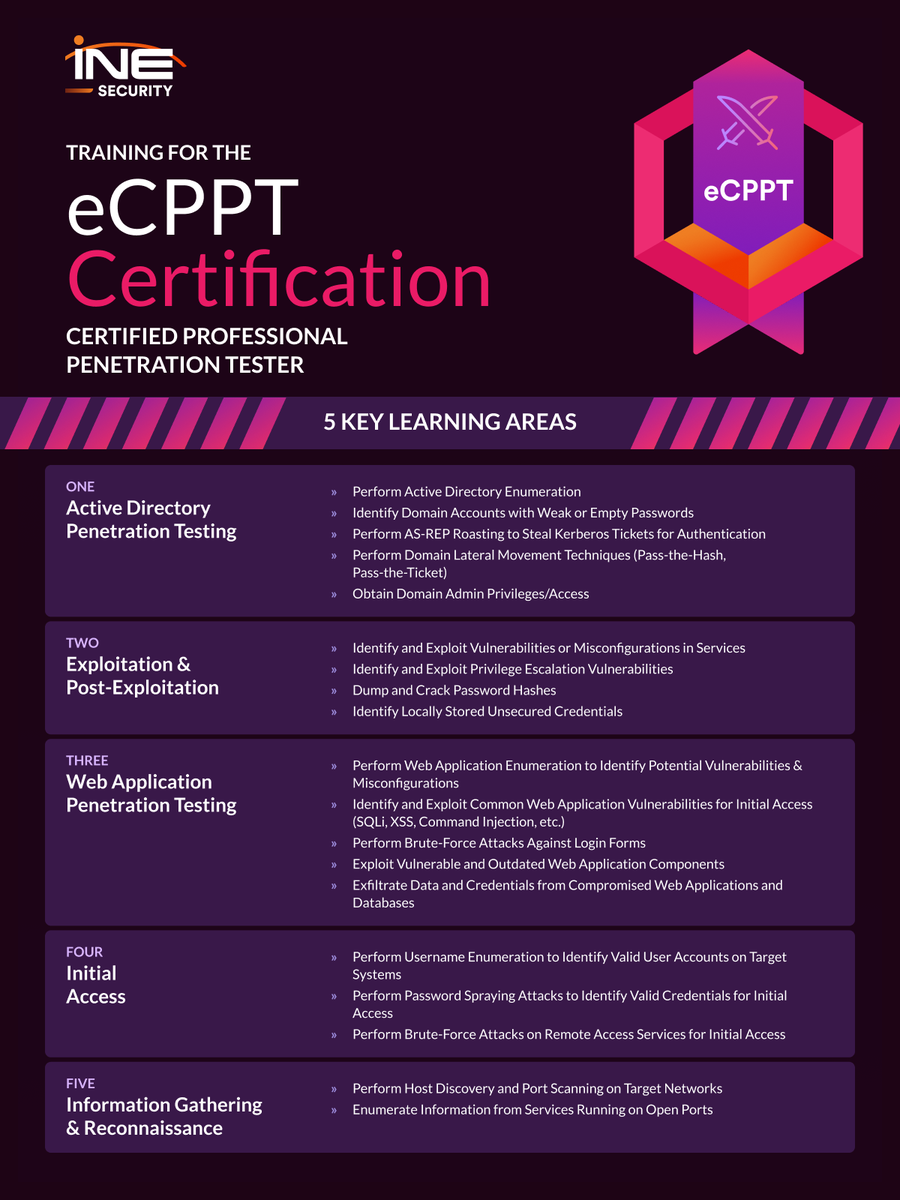
How many of these could you do today? 🤔
- Network recon
- Password spraying
- SQLi, XSS, command injection
- Privilege escalation
- Active Directory pass-the-hash
Checked most? The eCPPT proves you can run a full pentest.
👉 See the eCPPT exam: https://t.co/Wc364ipbuY
Think you’re up for the challenge? 👀
Jump into 31 free hands-on labs across cybersecurity, networking, cloud, and DevOps, all running right in your browser with zero setup and no credit card needed.
👉Start now: https://t.co/DZN0TbpF12
Most people waste months learning the wrong things before applying for tech jobs. 👀
INE Fundamentals Annual covers paths in cybersecurity, networking, cloud and data science, with hands-on labs and a free eJPT or ICCA voucher.
👉 https://t.co/LR6QRfWRVd