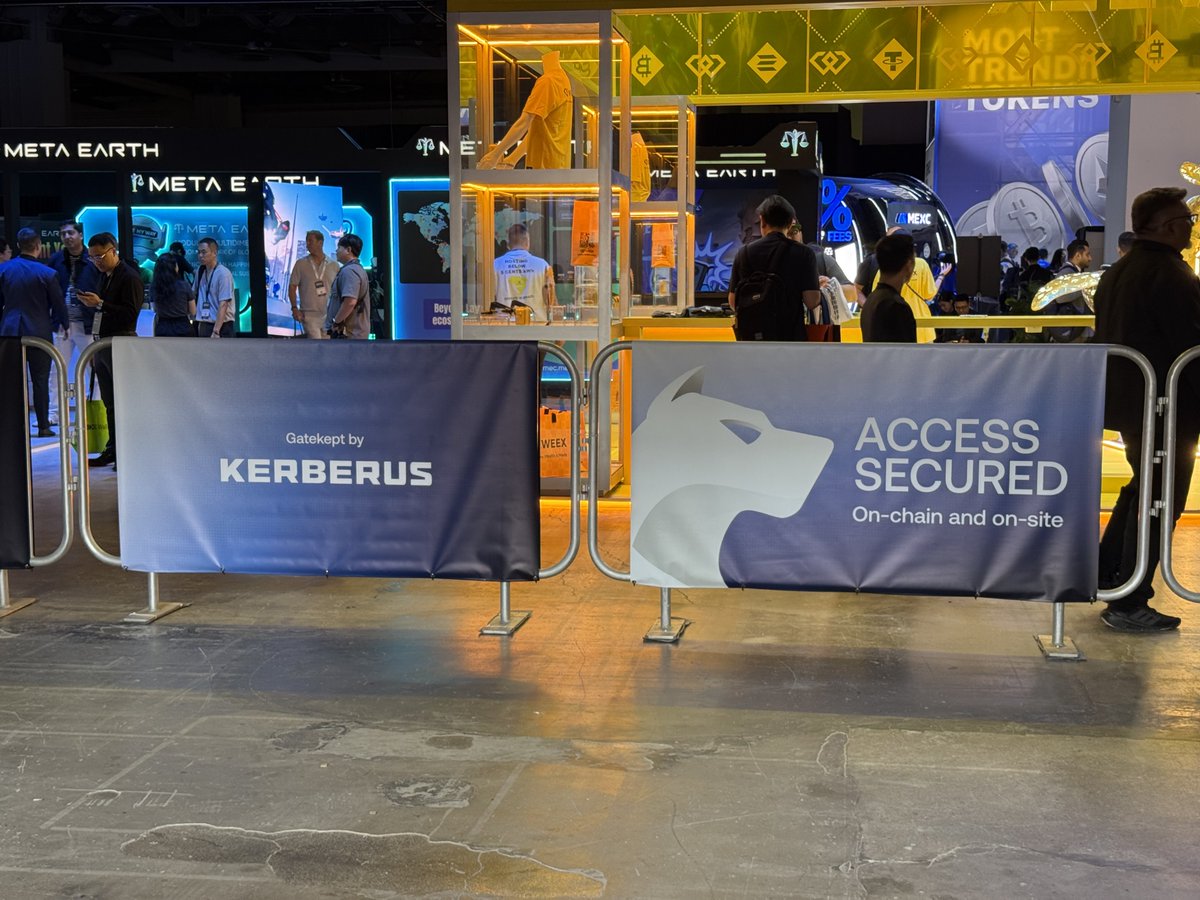
3 years ago we started MintDefense and I attended #TOKEN2049 as a crypto tourist
Today, we’re branding all the security barricades and tables
@Kerberus went from a humble project to the leading and only (after acquiring Fire and Pocket Universe) Web3 user security solution
🚨 CRITICAL CRYPTO ALERT 🚨
Two critical vulnerabilities ("PHP2Shell") were just disclosed in PHP, the language behind a huge share of the web, including WordPress, and crypto sites.
Both let attackers run code on servers without logging in, and exploit attempts are already live. A compromised site can quietly swap in a wallet drainer.
Don't connect your wallet or sign anything on a site unless you fully trust it, or it has confirmed on its official socials that it's patched.
Dramatic Update: The NSA & FBI now call site owners worldwide to patch or take sites down; several government sites have already gone down.
https://t.co/BMPlB9wFSG
https://t.co/LAzJCM9IET
Blur is shutting down in 30 days
Revoke approvals ASAP to avoid potential future losses
Head to https://t.co/jeaBKQjF2K, search for Blur on the ETH chain for all your wallets, and revoke all approvals
Be careful reading posts of people getting drained due to Ledger.
Some are true, but a lot of them are just engagement farming or people not understanding how they got drained and pinning it on a 3rd party to feel better about themselves.
They also seem to want to destabilize Ledger more than they already have been destabilized.
Ledger deserves part of the backlash, just don’t believe everything you read online.
Yes, but in this case with the reseller, a chip was implanted inside the device that monitors and records what's shown on its screen (the seed phrase) and then transmits it to an attacker. Because the attack targets the hardware layer, there's NO need for the threat actor to modify the firmware, so Ledger Wallet treats the device as valid when running the genuine check. From @PabloSabbatella
This seems to be the source.
Always, always buy directly from the manufacturer.
Where I live I pay more than if I bought from the resellers, and I still do it.
Ledger is investigating reports of loss of funds from users in South East Asia who purchased products from a reseller named CryptoBillis. As a precaution, and pending the results of our investigation, we have asked CryptoBilis to pause all sales and shipments of Ledger devices. We recommend Ledger users who purchased from this reseller in the last 90 days to not initiate set up if you have not done so yet. If you have set up your Ledger device, consider moving assets to a new Ledger signer (with new seed). We will continue to inform customers of updates as the investigation progresses.
Reach out to Ledger customer support through official channels with any questions: https://t.co/4p918UH8yb
@poesdec Yes but it’s one thing to compromise a device in a span of days while it’s traveling to you, and another to buy from a reseller that had undefined time to swap a device
Your fear mongering will never end. It’s a fact that you should buy from the manufacturer and not a reseller
@poesdec Same for your computer or phone you operate it on :)
It’s a fear mongering mindset that has no end. Either you manufacture every component or you subsidize and trust some companies to do it for you
Ledger is investigating reports of loss of funds from users in South East Asia who purchased products from a reseller named CryptoBillis. As a precaution, and pending the results of our investigation, we have asked CryptoBilis to pause all sales and shipments of Ledger devices. We recommend Ledger users who purchased from this reseller in the last 90 days to not initiate set up if you have not done so yet. If you have set up your Ledger device, consider moving assets to a new Ledger signer (with new seed). We will continue to inform customers of updates as the investigation progresses.
Reach out to Ledger customer support through official channels with any questions: https://t.co/4p918UH8yb
Re: Ledger hack: highly doubt it’s Ledger related
Don’t trust mass reports and retweets from news accounts who have no security expertise and live for engagement
Wait for a credible security person to confirm or deny it
Re: Ledger hack: highly doubt it’s Ledger related
Don’t trust mass reports and retweets from news accounts who have no security expertise and live for engagement
Wait for a credible security person to confirm or deny it
Re: Ledger hack: highly doubt it’s Ledger related
Don’t trust mass reports and retweets from news accounts who have no security expertise and live for engagement
Wait for a credible security person to confirm or deny it
Crypto is planning for AI that can break wallet signatures.
All the fixes on the table share one flaw.
Our CTO Danor @An7i21 Cohen on what actually holds. https://t.co/YBHCy3GXIZ