AI is arriving in GRC faster than most organizations are ready for it, but it's not really an AI problem.
Most teams are running on hidden institutional knowledge and manual workarounds. Your people know which spreadsheet is current, how to navigate disconnected systems, and how to work around gaps. AI can't improvise like people do.
Our latest research at The GRC Journal reveals what AI is actually exposing: whether your governance foundations work.
Here's a great piece from Onspring's PMM Ryan Redman on what this means for your AI strategy.
➡️https://t.co/Znw4mHiqRA
#AI #GRC #Governance #Compliance #RiskManagement
Without strong governance, scaling help desk operations becomes a liability. Overwhelmed teams burn out. Service becomes inconsistent-- customers don't get the same quality twice. Security risks spike when you don't have standardized verification processes or compliance controls.
We've seen organizations solve this by embedding governance into their service desk operations: standardized workflows, clear escalation tiers, automated routine tasks and continuous compliance monitoring.
Scaling doesn't mean sacrificing control. It means building it in from the start.
Read the full blog for how mature organizations do this: https://t.co/C4yyDzpE5w
#GRC #ServiceDesk #OperationsManagement #Governance #ComplianceFirst
Most business solution evaluations focus on features and cost. But cyberattacks are up 47%, compliance pressure is rising, and only 12% of transformation initiatives actually hit their targets.
The missing piece isn't the solution itself. It's governance.
Organizations that reach their transformation goals build governance into their evaluation process from the start. They assess regulatory alignment, data governance, security standards, and auditability before implementation. That due diligence becomes a defensible record that gives decision-makers confidence and reduces risk exposure.
A governance-driven evaluation framework helps you compare options against consistent criteria and adopt solutions that improve operations without introducing new risk.
Read the full blog ➡️ https://t.co/2IcRidlDra
#GRC #Governance #BusinessTransformation #RiskManagement #Compliance
Today's the day. Visit Onspring at the Internal Control & Fraud Prevention Training (The Ronald Reagan Building, D.C.) to explore solutions designed for government accountability.
Stop by our table to discuss control frameworks that reduce risk and improve organizational compliance. We're here Sept 22-23.
#InternalControl #FraudPrevention #GovernmentCompliance #GRC #AGA #onspring
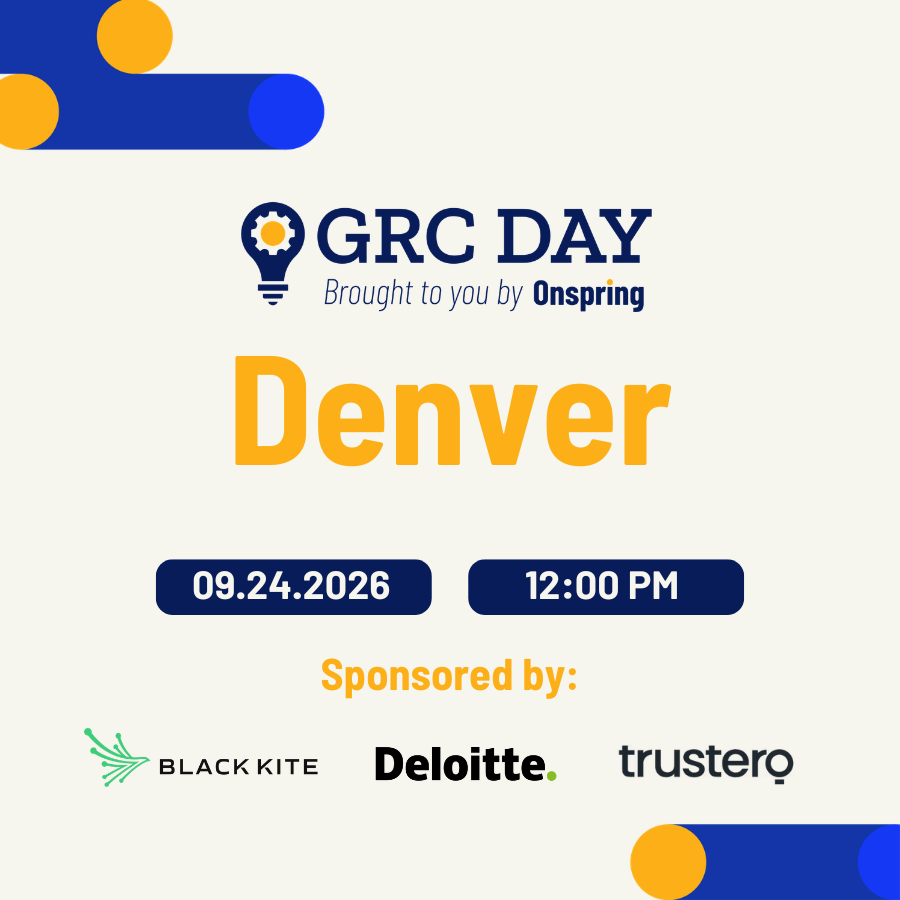
GRC Day Denver is this week! If you haven't registered yet, grab your spot now. Spend the afternoon stepping away from the day-to-day to dig into risk quantification, emerging AI applications for GRC, and third-party cyber risk management with your peers.
Stick around for happy hour at Oskar Blues Grill & Brew to keep the conversation going.
Last chance to register: https://t.co/hLXtT9ADkd
#GRC #Onspring #Denver #Cybersecurity #TPRM
95% of orgs have an AI strategy, but only 8% are seeing ROI.
Why? AI scales in GRC when you prioritize operational readiness first, not just technology.
Read Onspring Product Marketing Manager Ryan Redman's piece on what GRC teams actually need to move beyond pilots.
https://t.co/2dgKIbvcVN
#GRC #AIGovernance #complianceautomation #enterpriseRisk #GRCmodernization
Unmanaged customer care costs more than you think. Comcast learned that when one unscripted agent call went viral. Carrefour learned it when a $3.6M GDPR fine landed due to lost data erasure requests. Every day without customer care governance increases your risk of SLA breaches, data handling violations, and regulatory scrutiny. But governed operations deliver 2x the revenue growth while keeping your team compliant and audit-ready.
Read the full breakdown of real-world governance failures and how to prevent them → https://t.co/SvevZ33Ebm
#CustomerCare #Compliance #GRC #Governance
Exciting news: We're partnering with Trustero to bring continuous evidence management and control testing directly into Onspring.
Our latest research shows evidence collection takes up 25.9% of GRC teams' http://time., but this integration changes that. Trustero's autonomous AI agents now run continuously in the background pulling evidence, mapping controls, and re-testing them in real time. Your compliance status stays current without the manual grind.
One platform with, real-time visibility, less busywork, and more focus on what actually matters.
Learn more: https://t.co/pCy0LpeWJr
#GRC #compliance #AI #riskmanagement #automation #trustero #onspring
We're excited to announce that Serge Stines will be speaking at InfoSec World this October!
If you're building your GRC program, scaling compliance operations, or looking for smarter ways to build internal workflows, be sure to mark your calendar:
Get 20% off registration with code ISW26-ONSPRING20:
https://t.co/wIoOwRJpPL
See you there.
#InfoSecWorld #GRC #Compliance #Governance
Every unnecessary data point creates risk.
Data minimization helps organizations reduce breach exposure, strengthen privacy controls and support compliance with evolving data protection regulations. By collecting only what is needed-- and retaining it only as long as necessary-- teams can improve risk visibility and build more resilient data governance practices.
Explore why data minimization is a critical first line of defense against breaches: https://t.co/3CuVZTmlKe
#DataMinimization #Cybersecurity #DataPrivacy #GRC #Compliance
Don't forget to secure your spot!
SheLeads Tech is just around the corner. This is your opportunity to connect with ambitious women redefining what leadership means in GRC and tech. Whether you need a confidence boost, fresh perspectives, or time with likeminded people, this is it.
Be sure to top by our table, and say hello!
Register today: https://t.co/Nn1Y1lRSoM
#WomenInGRC #TechLeadership #SheLeadsTech
Stop by Onspring's table at the AGA Internal Control & Fraud Prevention Training, Sept 22-23 in Washington, DC.
Discover how to strengthen internal control systems and minimize fraud, waste, and abuse across your organization. While there, connect with government and industry leaders sharing discovery techniques, lessons learned, and strategies for effective risk management.
Register:https://t.co/dQRGD6YeWL
#InternalControl #FraudPrevention #GovernmentCompliance #GRC #AGA #onspring
Managing GDPR, CCPA, and overlapping privacy regulations requires more than manual tracking and institutional knowledge.
Centralized GRC software helps compliance teams improve visibility, reduce process gaps, support audit readiness, and respond more effectively as regulations evolve.
Read the full article to learn how organizations can build a more scalable and defensible compliance management program. ➡️ https://t.co/hZ2DZj7PeF
#GRC #ComplianceManagement #RiskManagement #DataPrivacy #RegulatoryCompliance
We're excited to welcome Elle James to Onspring as a Senior Software Engineer.
Elle brings years of experience as a back-end developer with strong full-stack capabilities. Proficient in many code languages and modern web frameworks, Elle built a deep technical foundation across both front-end and back-end development. Elle's comfort working across web and native development environments, paired with a focus on usability practices, brings practical depth to platform design and delivery.
Welcome to Onspring, Elle. We're glad you're here!
#teamonpspring #newhire #grc #growingtogether
58% of business leaders rely on gut instinct for critical decisions. In GRC, that means inconsistent risk assessment, missed emerging threats and misallocated resources. Performance analytics flips the script. By measuring the right KPIs, centralizing your data and establishing clear reporting cadences, your team makes faster, more confident decisions backed by evidence. Learn the four steps to implement performance analytics in your GRC program-- without needing advanced data science or complex dashboards.
Read the full blog: https://t.co/IzGDAEL3xd
#GRC #ComplianceAnalytics #RiskManagement #GovernanceRiskCompliance #DataDriven
🚨 Last Call: Our room block is closing! 🚨
You have just one week left to book your room at Green Valley Ranch at the special Connect attendee rate, and our room block is nearly sold out.
Get your Vegas plans squared away and reserve your room today: https://t.co/w6kfcKBa0G
See you in Vegas October 13–14!
#OnspringConnect2026 #GRC #LasVegas
West Michigan GRC and cybersecurity leaders, join us for GRC Day 2026 this week!
We’re bringing local practitioners together to dig into some of the biggest questions surrounding AI and GRC, including emerging AI threats, vendor risk, data governance, and the role human judgment plays when the hype gets louder than the reality.
The event is free to attend, with lunch, networking and a happy hour on Crowe’s rooftop to close out the day.
Reserve your spot:
https://t.co/AaWiiJqmim
#GRCDays #GRC #Onspring #WestMichigan #Cybersecurity
We're excited to welcome Lillian Fleming to the Onspring as a Senior Software Engineer.
Lillian brings years of engineering experience designing and delivering enterprise-grade solutions at scale. With deep expertise in coding, cloud platforms, and distributed systems architecture, she's built her career solving complex challenges. We're looking forward to the architectural depth and engineering rigor she'll bring to our platform.
Welcome to Onspring, Lillian. Glad to have you here!
#teamonspring #newhire #grc #growingtogether
Two third parties. Two very different diligence needs.
A critical third party needs a SOC 2 report date, a BC/DR test date, and an exit plan on file. A low-tier third party doesn't. Add a second condition — does this third party touch personal data? — and you're building sections to fit every combination instead of the actual due diligence.
Now, Field Visibility Outcome (v37.2) does both in one section. Show the fields that matter, skip the sections that don't. Same logic, fewer sections, less scrolling.
#OnspringAI #TPRM #GRC
91% of tech leaders struggle with CRM data governance. Yet most don't realize the stakes: regulatory fines, insider risks, inconsistent data, compliance headaches. You need clear standards, defined ownership, controlled access and audit trails that work. We published a guide breaking down four key governance elements and a step-by-step implementation framework.
Whether you're tightening compliance or reducing breach risk, this covers the moves.
Read the full blog ➡️ https://t.co/6XvFGkgtMv
#DataGovernance #CRM #Compliance #GRC #RiskManagement