Plunder Academy is now LIVE!
The islands are awake… the quests are real… and the path from deckhand to developer begins today.
Immerse yourself in the world of Plunder Academy.
Dive in: https://t.co/hJys7CpMBg ⚡️🏝️
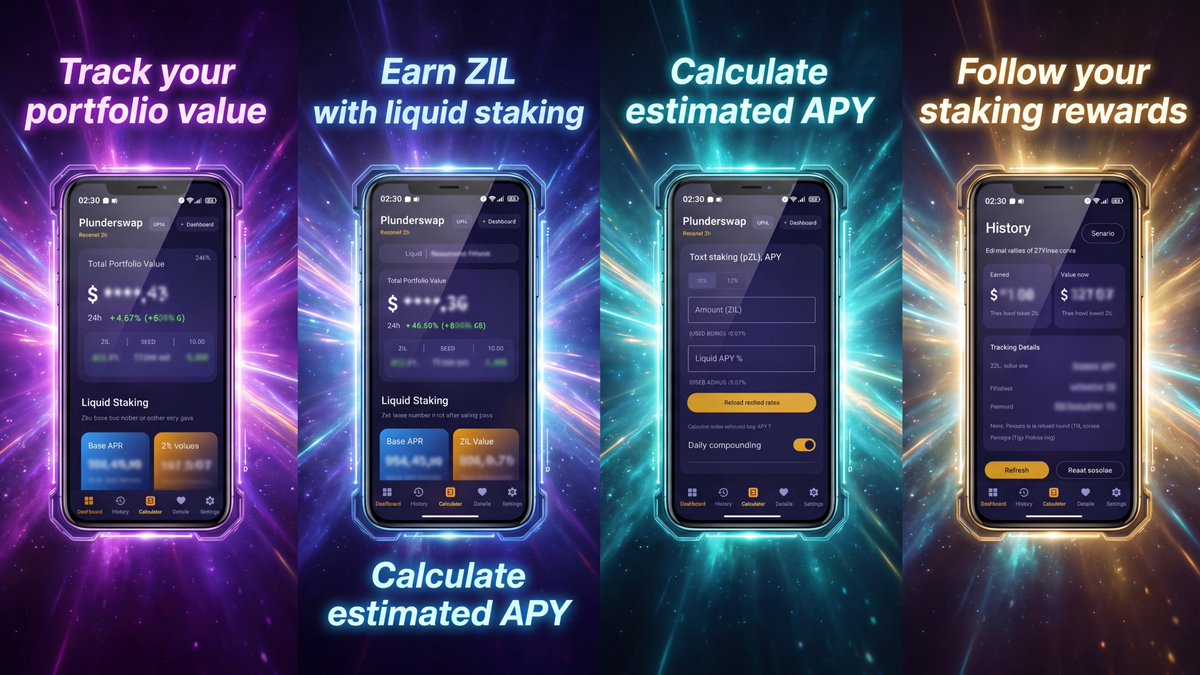
Plunderswap Rewards v1.2.44 is rolling out 🚀
What’s new since v1.2.37:
• Improved Read-only wallet reliability
• Added Multicall with RPC fallback
• Better cached / last-known data handling
• Added full Diagnostics in Settings
• Added Copy & Send diagnostics
More down below
NEWS!
1. Added Read-only mode for viewing wallet data without connecting or signing.
2. Improved multi-wallet support and wallet switching.
3. Fixed SEED bonus APR.
4. Calculator now include seed.
5. Projected earnings are now more accurate.
6. MILESTONE with estimated time
Zilliqa staking, right in your pocket. 📲✨
PlunderSwap Rewards is a mobile app that gives you a clean dashboard for your balances, staking positions & claimable rewards, just connect your wallet and go.
Built by the community, for the community. 🏴☠️
https://t.co/SvmENbCICq
An update has been added to the Ledger incident hub, outlining the recovery and transition plan. https://t.co/ZlEqAjMGIX
The legacy (non-EVM) side of Zilliqa is being retired, with recovery taking place through migration to Zilliqa EVM.
🧵1/4
Nonce-Generation Vulnerability in the Zilliqa Ledger App: A critical vulnerability has been identified in the Zilliqa Ledger application affecting the generation of Schnorr signatures for native (non-EVM) Zilliqa transactions. The vulnerability causes signatures to be generated with a predictably weakened ephemeral nonces, from which an attacker can recover the signer’s private key using only publicly available on-chain data.
Protective measures are already in place to prevent further loss, and a coordinated remediation plan is being finalised. Users who have signed native Zilliqa transactions with a Ledger device should await official guidance before taking any action.
Impact: The vulnerability affects private keys used to sign native Zilliqa transactions with a Ledger device. Any account that has broadcast approximately five or more native transactions signed through the Zilliqa Ledger app should be considered compromised. Its private key can be reconstructed from signatures already recorded on-chain, regardless of any subsequent software update.
The issue is confined to the Ledger app’s native signing path. EVM transactions are unaffected. Zilliqa software development kits, including zilliqa-js, gozilliqa-sdk and pyzil, generate nonces correctly and are not affected.
Root cause: Zilliqa native transactions are authenticated using EC-Schnorr signatures over secp256k1. Each signature requires a fresh, uniformly random 256-bit ephemeral nonce, (k). The secrecy and full-width randomness of (k) are essential, as any systematic bias can allow the private key to be recovered.
The signing routine generated 40 bytes of randomness and reduced them modulo the curve order, correctly producing a uniform 256-bit value. However, when copying this value into the nonce buffer, the code copied the wrong 32 bytes of the 40-byte output. This retained the eight zero-padding bytes introduced by the reduction and discarded eight bytes of entropy.
As a result, the most significant 64 bits of every generated nonce were fixed at zero, meaning (k < 2^{192}).
A nonce with 64 known bits leaks information about the private key with each signature. With five or more affected signatures, the private key can be recovered in seconds using commodity hardware by solving the resulting Hidden Number Problem through lattice reduction - a well-documented technique for attacking biased-nonce signatures.
Because the affected transactions are permanently recorded on-chain, this exposure cannot be reversed by updating the signing application. The affected keys must be retired.
Timeline
2019-2026: The defect was present in every released version of the Zilliqa Ledger app across all supported devices.
19 July 2026: On-chain activity consistent with active exploitation was observed.
21 July 2026: The root cause was isolated to the app’s nonce-handling code and confirmed by reproducing the issue against on-chain signatures.
Ongoing: A corrected version of the app is being prepared in coordination with Ledger. Release details will be announced separately.
Remediation: As soon as the issue was identified, native (non-EVM) transactions were suspended as a protective measure. This has halted further draining of affected accounts while a solution is prepared.
Affected accounts cannot be secured through an ordinary transfer. Because their private keys can be derived from data already recorded on-chain, an attacker with access to the same key could attempt to front-run a legitimate transfer as soon as transactions resume. Advising users simply to move their funds would therefore be ineffective and potentially unsafe.
A corrected build of the Ledger app has been prepared, restoring full-width nonce generation and preventing further weakened signatures from being produced. However, this does not protect keys that have already been used to sign affected transactions. Those keys must ultimately be retired.
A coordinated remediation plan to secure affected balances is being finalised and will be published separately. Until then, users who have signed native Zilliqa transactions with a Ledger device should take no independent action and should rely solely on official Zilliqa channels for instructions.
Users who hold or transact with ZIL exclusively through EVM-compatible tooling are not affected.
Acknowledgments: @kucoincom played a key role in pinpointing the root cause in the Zilliqa Ledger app nonce generation, recovered affected private keys from publicly available on-chain signatures, and confirmed ongoing exploitation.
KuCoin’s timely reporting and responsible collaboration enabled rapid protective measures, helping safeguard users, ecosystem participants, and the broader Zilliqa ecosystem while the remediation plan was being developed.
We sincerely appreciate the KuCoin team’s professionalism, technical expertise, and cooperation throughout this process.
PlunderSwap just got a serious speed boost
We’ve made the app lighter, pages and balances load faster, swap quotes update instantly as you type, and mobile feels smoother and more reliable
Less waiting. Faster swapping. A better PlunderSwap experience from start to finish ☠
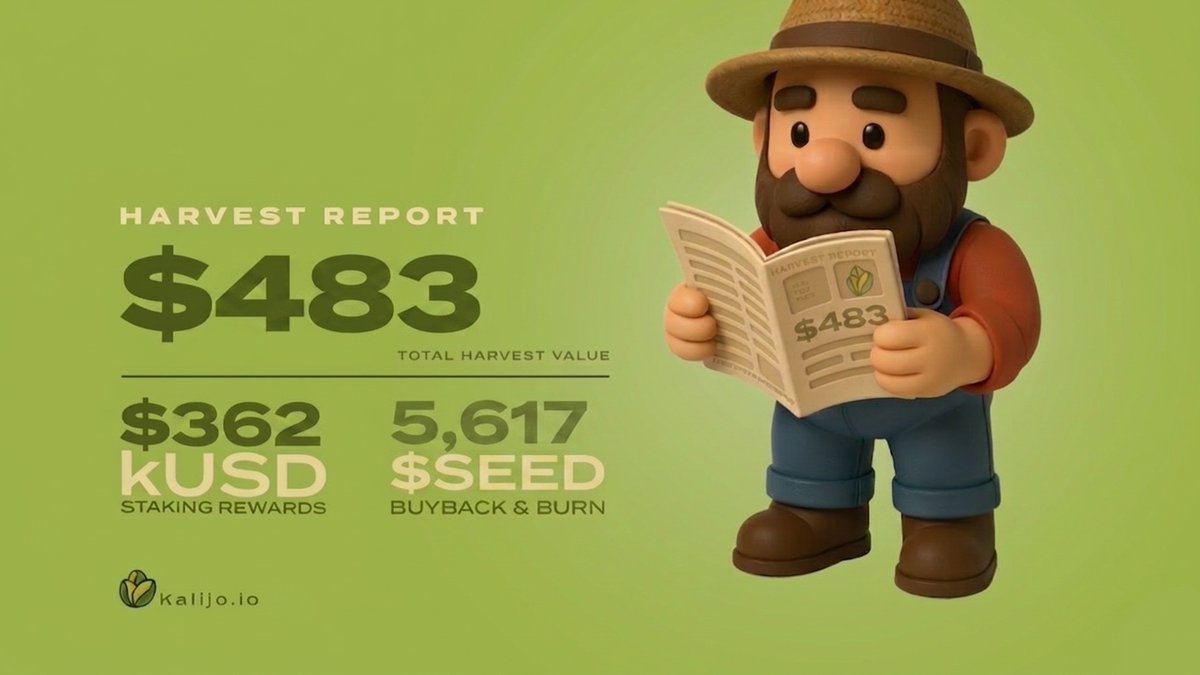
Our Latest Harvest Report is In!
The sun has set on another cycle, so it’s time to share the fruits of our labour.
Thank you for being part of the Kalijo acreage. Whether you're planting, staking, or just watching the green grow, we’re glad to have you in the barn!
Keep those tractors running! https://t.co/Y1eLb3h1mu 🌽✨
NEW: Kalijo Games is LIVE with 3 game modes.
1 platform. 1 NFTree across all of them.
Cosmic Grove ➜ Multiplayer survival.
Cosmic Mines ➜ Cash out or push your luck. Up to 10x.
Plinko Nebula ➜ Pick your risk. Up to 50x.
Every bet feeds a 4-tier progressive jackpot. Own an NFTree? Your Cosmic Luck stat boosts your jackpot odds across all 3 games.
Provably fair. 100% on-chain. Built on @zilliqa.
🍀✨Play now ——> https://t.co/NqTodAFpo4 ✨
Provably fair gaming with progressive jackpots, fully on-chain on @zilliqa.
Which one are you playing first?
🌀 Cosmic Grove
💣 Cosmic Mines
🟣 Plinko Nebula
NEW: Kalijo Games is LIVE with 3 game modes.
1 platform. 1 NFTree across all of them.
Cosmic Grove ➜ Multiplayer survival.
Cosmic Mines ➜ Cash out or push your luck. Up to 10x.
Plinko Nebula ➜ Pick your risk. Up to 50x.
Every bet feeds a 4-tier progressive jackpot. Own an NFTree? Your Cosmic Luck stat boosts your jackpot odds across all 3 games.
Provably fair. 100% on-chain. Built on @zilliqa.
🍀✨Play now ——> https://t.co/NqTodAFpo4 ✨