🧵 New report from our #TDR team: #APT29 ran a large-scale watering hole campaign against iOS and Android users via compromised legitimate sites, cloned high-profile sites, and a one-week supply-chain compromise of the Ukrainian analytics tracker Plerdy.
https://t.co/ojAXHndAim
What operators should do: take controllers off the internet, use secure remote access, change default credentials, update firmware, and monitor configuration changes.
Full investigation 👇
https://t.co/SW6EkiqUTT
French authorities’ attribution 👇
https://t.co/H9xVgTg8c6
French authorities have attributed the attacks on internet-exposed Danfoss refrigeration controllers to Iran’s #IRGC, specifically the Shahid Kaveh unit, aka #CyberAv3ngers.
That matches one of the hypotheses in our private report shared on 15 October.
https://t.co/SW6EkiqUTT
We gave the captured request and public #Danfoss firmware to an LLM. Within minutes, it confirmed an unauthenticated rename of the admin account, the first step of a password reset.
The lesson: LLMs make reliable #ICS exploits much cheaper to build.
🧵 New report from our #TDR team: #APT29 ran a large-scale watering hole campaign against iOS and Android users via compromised legitimate sites, cloned high-profile sites, and a one-week supply-chain compromise of the Ukrainian analytics tracker Plerdy.
https://t.co/ojAXHndAim
The n-day exploit chains (including the CSV-grade #DarkSword kit) stole cookies, Wi-Fi passwords or full iPhone data: iMessage, WhatsApp, Telegram, Keychain, photos…
Every CVE was patched before the campaign started. A fully updated phone was safe.
👀 New original @SecurityBreakAI research!
Inside Omega AI: An All-in-One Underground AI Platform
@pedrinazziM investigated Omega AI, an underground platform that combines unrestricted AI models, jailbreak prompts, offensive security tools, and malware monetization guidance in one place.
An all-in-one platform that have one goal: lower the barrier to entry for less experienced threat actors.
Read our research 👇
https://t.co/pjER8Bh2Mf
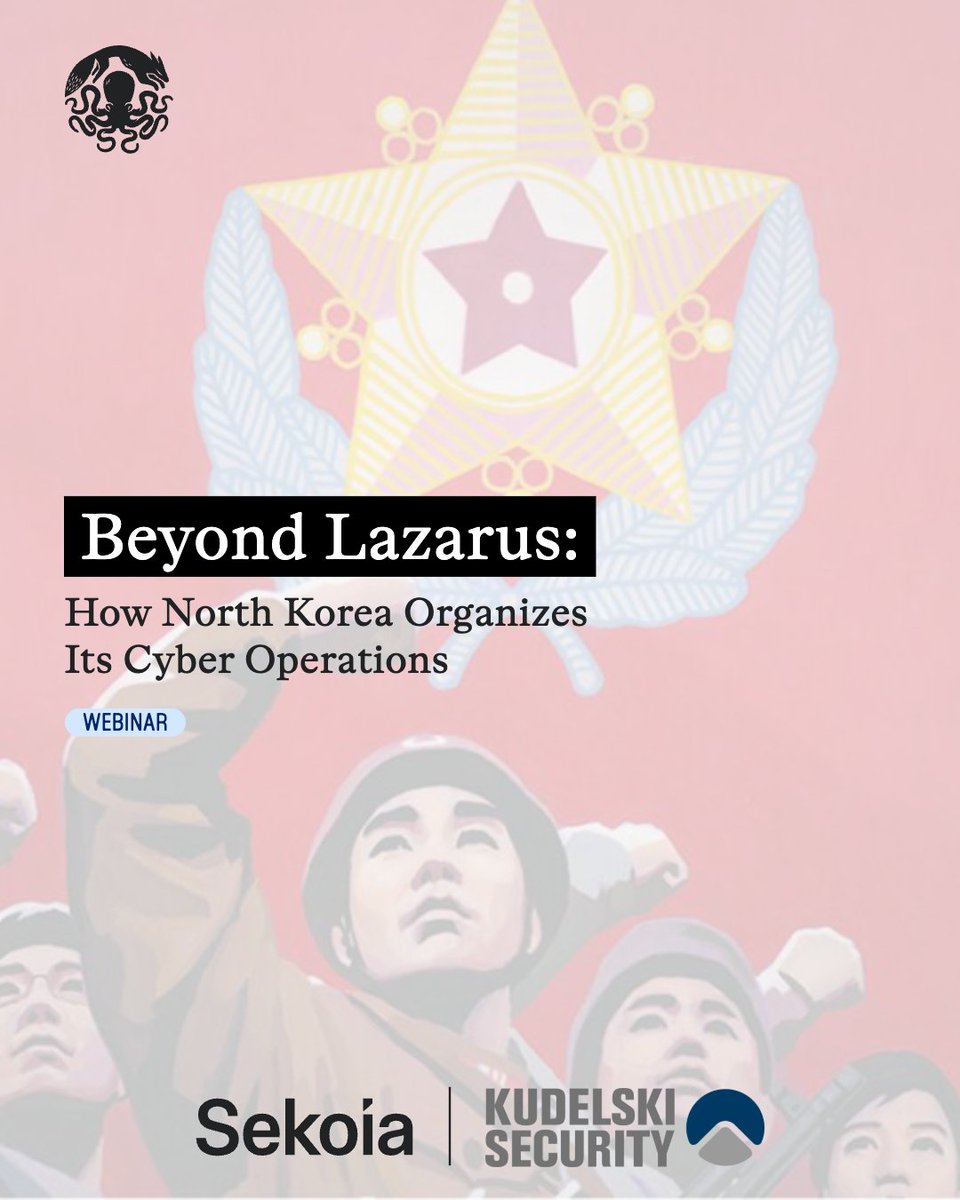
Oct 29, 3PM CET: Sekoia and @KudelskiSec walk through our joint research on North Korea's cyber capabilities.
45 minutes on attribution, IT workers placed abroad, and the financial channels behind Pyongyang's operations.
https://t.co/SV6YqSi2bx
#webinar
An attacker found our Flowise #honeypot, a decoy #AI platform, and literally tried to turn the agent into its very own attack assistant.
They pulled credentials, planted a callback, and fed the model data from a likely iGaming target.
https://t.co/jGfReO8agr
Sekoia #TDR team traces how the operation reached cloud and SaaS environments, then turned trusted access into money. Written with @BeazleySecurity, the report also draws on first-hand incident response from a zero-day Oracle PeopleSoft compromise.
What makes #ShinyHunters hard to stop? Well… the name can survive the people using it. Since 2020, changing operators have used the name to steal data and run extortion schemes.
https://t.co/GemIB7f8TU
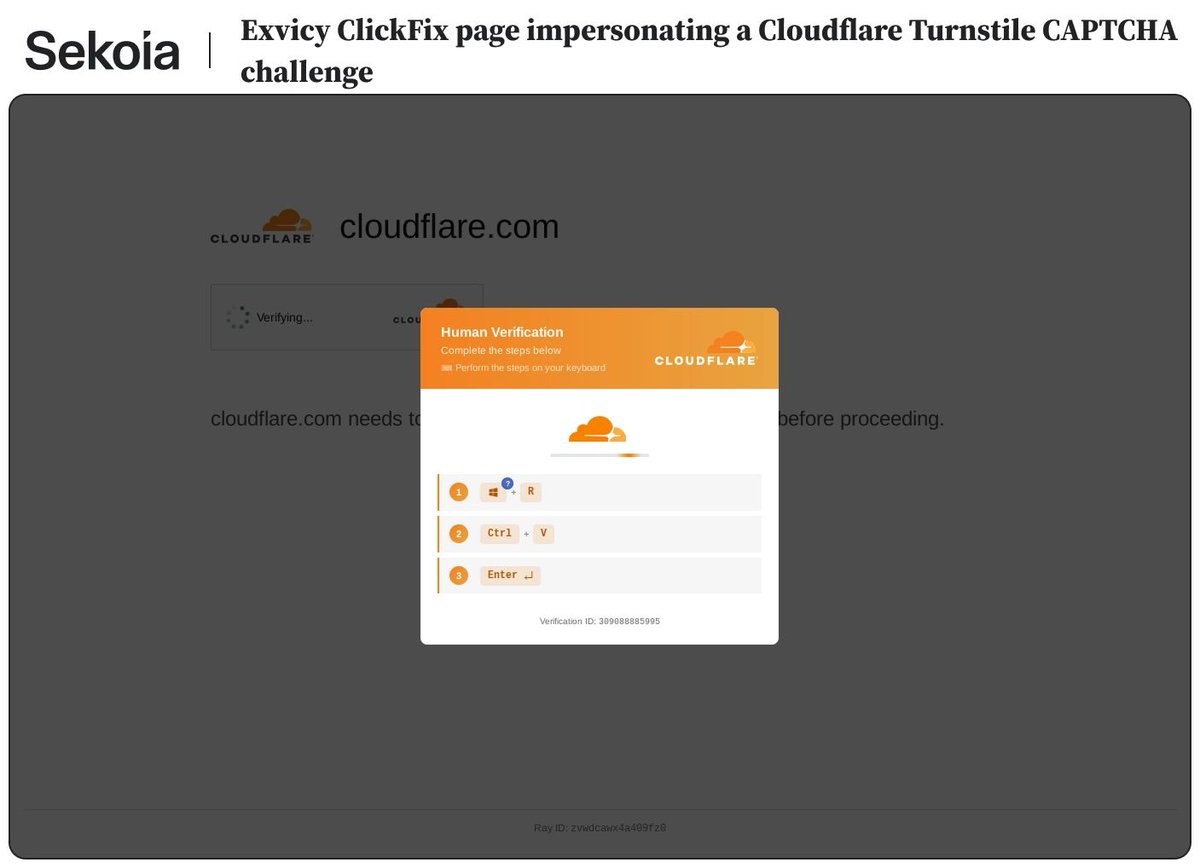
TDR analysts uncovered #Exvicy, an emerging #ClickFix MaaS sold on https://t.co/Tqclvugg2p since May 2026.
We assess with high confidence that Exvicy is a copycat of #ErrTraffic, reusing its injected JavaScript, ClickFix HTML, and C2 communication logic.
https://t.co/s8lkagBueu
Exvicy is already widespread in the wild. We identified dozens of active administration panels and more than 100 C2 servers.
Its monthly price also jumped from $1,200 to $2,000 in mid-August 2026.
@KudelskiSec IT workers operating under false identities are part of this model too, functioning as a revenue channel and an insider threat.
Read the full report, Beyond Lazarus: Organization of DPRK Cyber Capabilities
https://t.co/RjGf6yCsAK
North Korea’s cyber program was built to serve two purposes: intelligence collection and revenue generation.
A new joint report from Sekoia #TDR and @KudelskiSec examines how that system is organized.
https://t.co/RjGf6yCsAK
@KudelskiSec One finding runs throughout the research: espionage and revenue generation are closely linked.
Access obtained for financial gain can be reused for intelligence collection. Shared infrastructure can support both missions.