Break/fix IT profits from every incident. An MSP profits when nothing happens.
That single incentive difference changes how every problem gets approached, documented and prevented next time.
Full breakdown of MSP vs break/fix ROI → https://t.co/fIOO3LHz9Z
Break/fix IT gets paid when your systems fail. That is the whole model.
A managed service provider earns the same either way. So prevention becomes the priority.
Incentive alignment changes everything about how IT gets managed.
https://t.co/SOvtv2KHGU
Your IT environment has been accumulating risk since the last time someone reviewed it.
Our IT spring cleaning guide covers exactly what to fix first → https://t.co/F6iCYh4Xw2
#ManagedIT#CyberSecurity#ITStrategy#SMB
Your email filter is not enough to stop today’s phishing attacks.
Gateway. Machine learning. Defender for Office 365. Three independent layers.
And when one still gets through, automated remediation pulls it from every mailbox before it causes damage.
https://t.co/O3dv7ejnoY
Your offboarding process probably left someone’s access active.
Wrong person. Still in the system. Nobody noticed.
Stale accounts and forgotten app consents compound fast.
We cover the fix in our latest blog post.
https://t.co/z9v2dcWhk4
Do you know exactly what data your backups are protecting?
During onboarding, we often find backup systems and Office 365 data that are running but have never been fully validated.
That gap only becomes visible when recovery is suddenly needed.
https://t.co/EafBOqPCSg
Your Microsoft 365 environment probably has access that shouldn’t be there.
Former employees. Forgotten app consents. Admin roles nobody owns.
Every IT environment we onboard has them. Most organizations have no process to catch them.
https://t.co/ktw9RLyrhW
After sharing our recent WatchGuard firewall deployments, we saw a lot of interest and great conversations around performance, throughput, and what modern firewalls actually need to handle.
So we decided to go deeper.
https://t.co/R6kHCHpLnj
When SonicWall accelerated the end-of-support timeline for SMA 100 devices, organizations relying on those systems were suddenly facing a tight deadline to replace their remote access infrastructure.
https://t.co/VkZzRRYIyA
Do you know exactly why every firewall rule in your environment exists?
We still see rulesets during onboarding that allow far more traffic than necessary, often layered with redundant access.
We break this down in the next post of The Red Flag Series.
https://t.co/JJmONRQ1m7
Are your production systems, user devices and wireless networks all on the same network?
We break this down in the next post of The Red Flag Series. https://t.co/zPjnM2A27W
#ManagedIT#CyberSecurity#ITStrategy#SMB
Are standard users running day to day work as local administrators in your environment?
We see this configuration regularly during onboarding, usually without a clear reason it still exists.
We break this down in the first post of The Red Flag Series.
https://t.co/9x0iEiZPTa
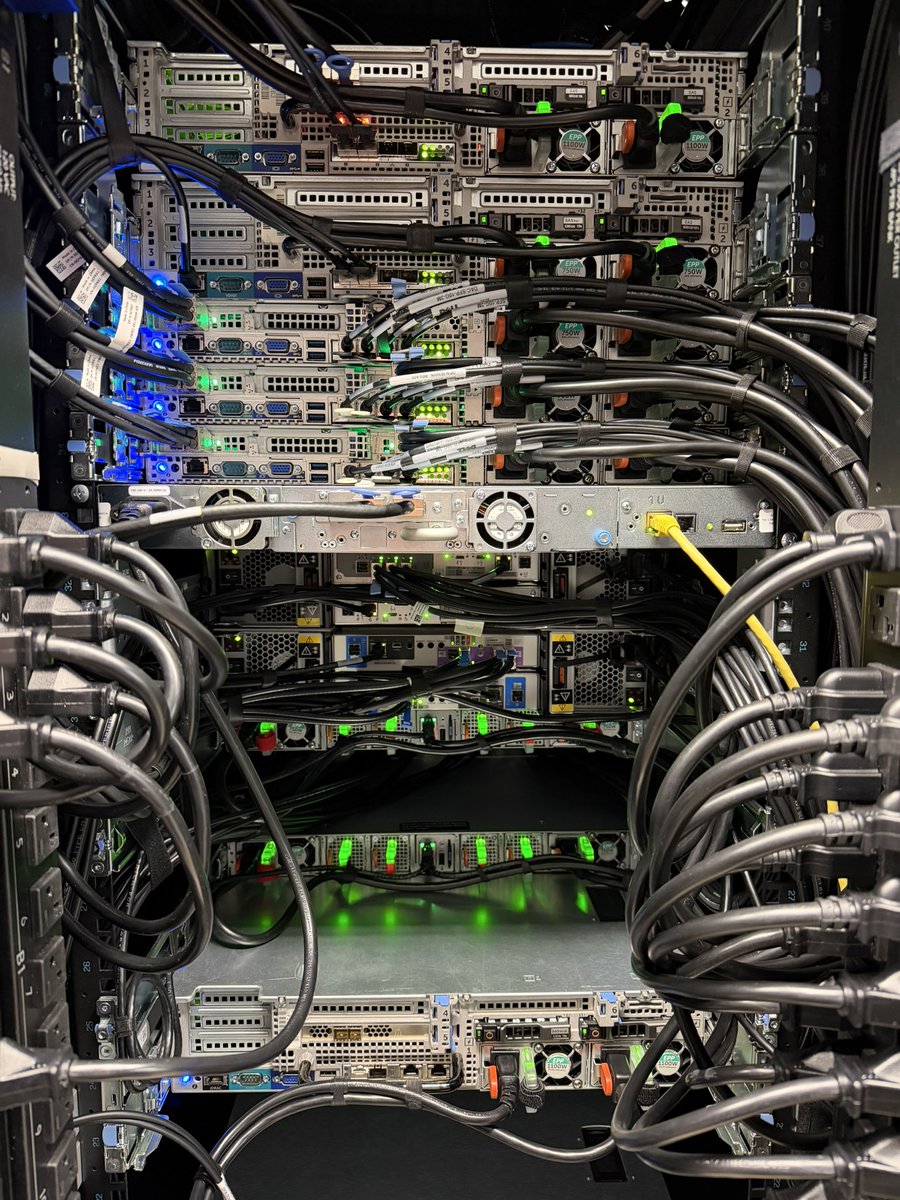
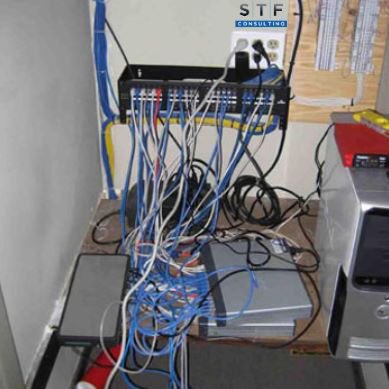
These are before and after pictures of a previously disorganized wiring closet. #STFConsulting#BeforeandAfter https://t.co/PdX6BGZn2D I 732-872-1911 Option 1
With 6,000 new viruses created each month, it is vital to keep your computer systems protected! #STFConsulting https://t.co/PdX6BGZn2D | 732-872-1911 Option 1
Stop SPAM, viruses, worms, and other email-borne malware BEFORE they arrive in your inbox with STF consulting! We can help you establish an email security system that will help keep you and your business protected. https://t.co/x7EnFO1Z7z #STFConsulting#EmailSafety