All your vulnerabilities, one platform. 🔒
CSPM, DAST, SAST & integrations give full visibility across cloud, apps & code.
Faster fixes ✅ Better prioritization ✅ Lower costs ✅
Learn more: https://t.co/jcVpKdqWRt
Compliance shouldn't mean choosing between high consulting fees and tedious manual work.
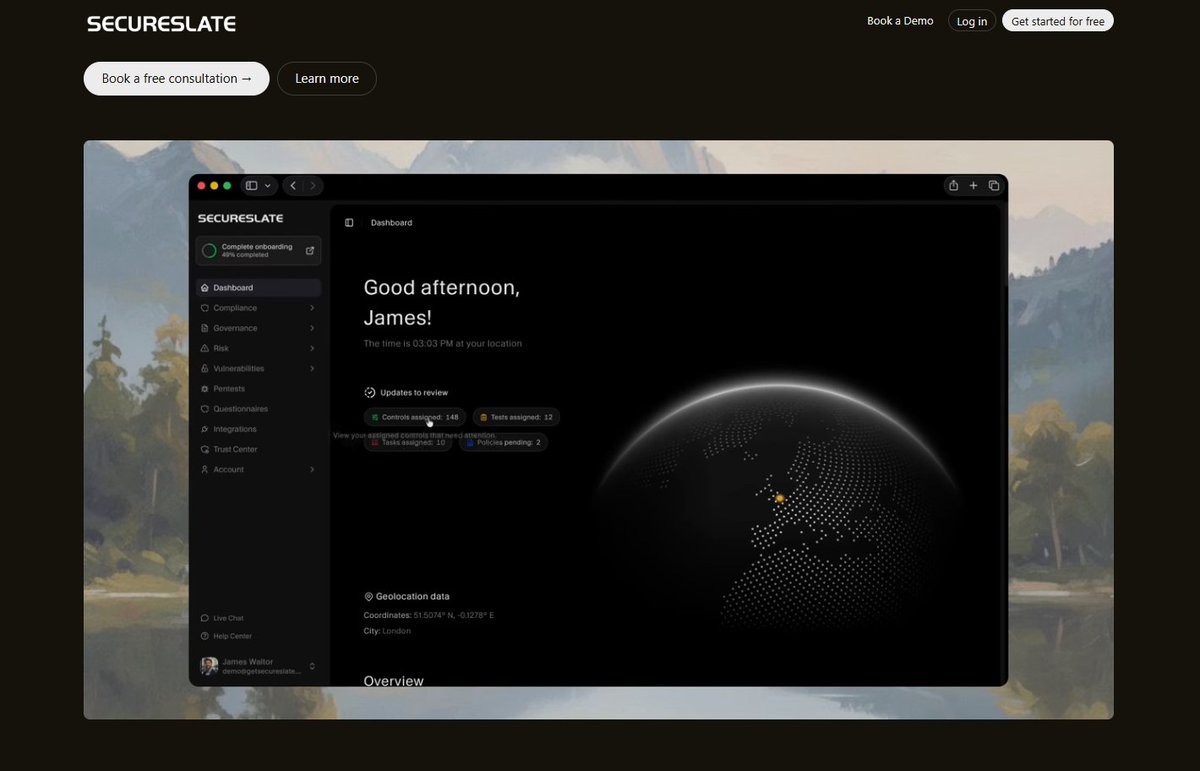
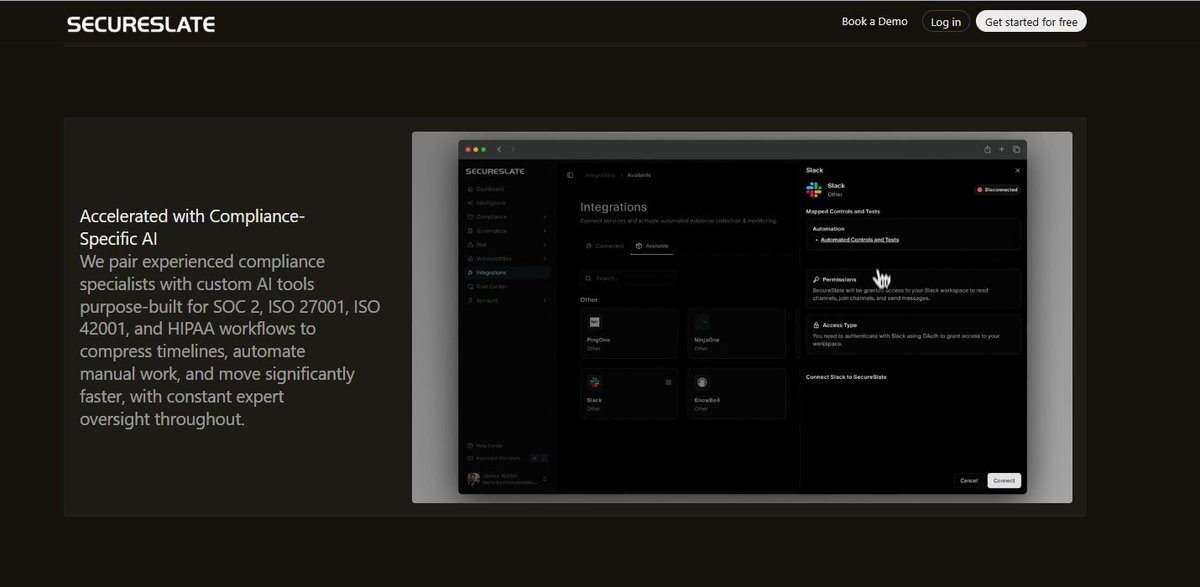
SecureSlate combines AI automation with human expertise to streamline gap analysis, policy creation, and evidence gathering, accelerating the path to SOC 2, ISO 27001, ISO 42001, and HIPAA.
Security incidents don’t always start with sophisticated attacks.
Sometimes, it starts with one click, one weak password, or one overlooked phishing email.
Security Awareness needs to be an ongoing process—not a once-a-year training session. 👇
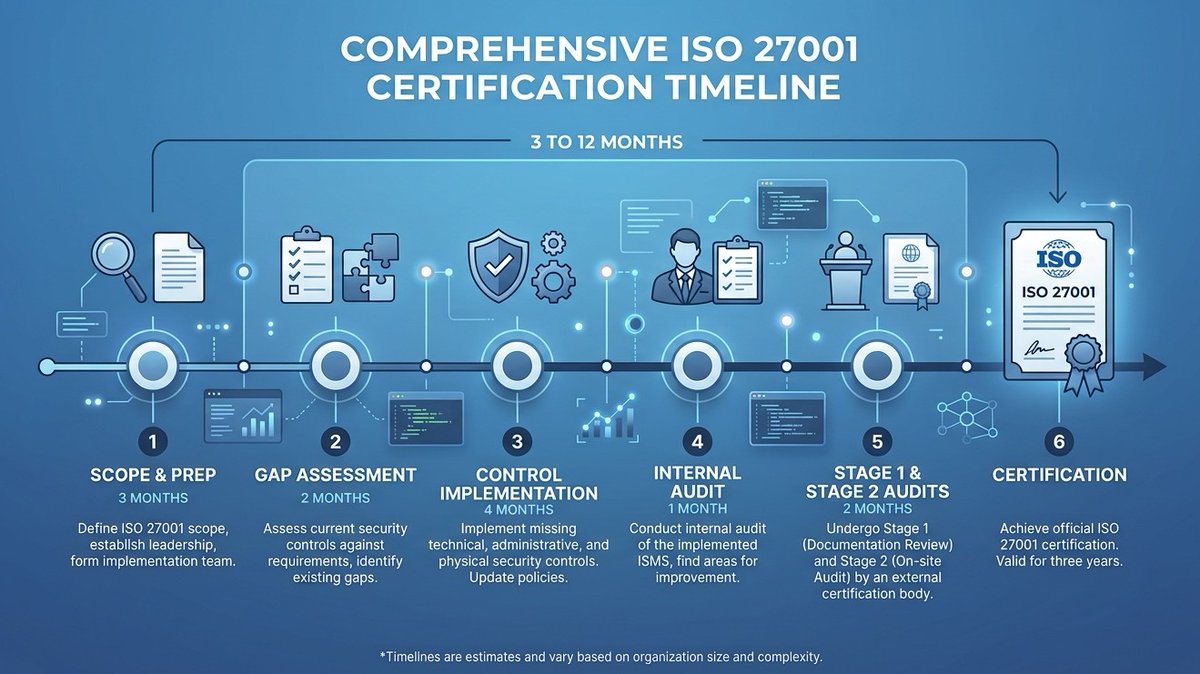
How long does it take to get ISO 27001 certified? 🗓️
Most tech teams think it’s a quick 1-month sprint, but the real timeline looks like 3 to 12 months.
The audit itself isn't the long part; it’s defining scope, implementing controls, and building proof.
#ISO27001#GRC
What if compliance didn’t just flag the problem, but helped fix it? 🤖
That’s the shift toward agentic compliance: AI that analyzes control gaps, finds the right evidence, and prepares the fix for your approval.
Less chasing. More doing.
#GRC#Compliance#AI#Cybersecurity
Everyone is talking about AI.
Very few are talking about how AI should be applied to compliance.
The real opportunity isn't generating policies with ChatGPT.
#ISO27001#ComplianceAI#AISecurity#CyberSecurity#GRC
Still managing ISO 27001 compliance with spreadsheets?
Compliance automation changes the workflow:
→ Less manual work
→ Better visibility
→ Continuous evidence
→ Faster audit readiness
#ISO27001#ComplianceAutomation#GRC
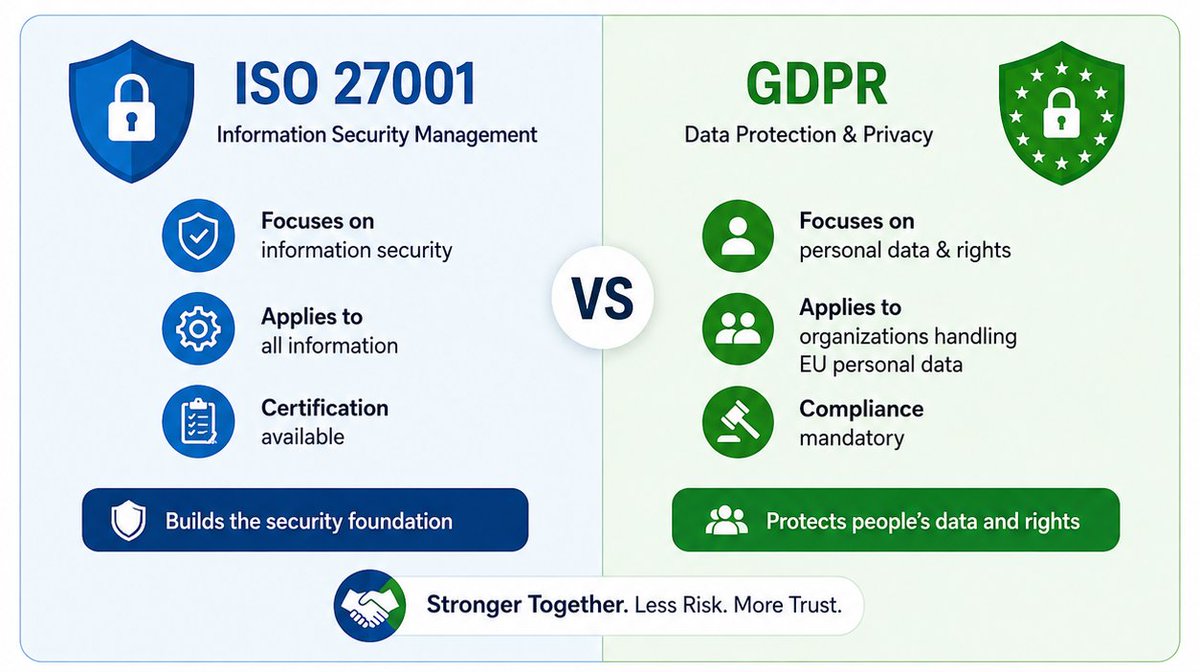
ISO 27001 vs GDPR isn’t really a competition.
ISO 27001 helps build the security foundation.
GDPR focuses on protecting personal data and privacy.
The smart approach? Make them work together.
Better risk management. Stronger trust.
#ISO27001#GDPR#Cybersecurity#Compliance
ISO 27001 vs GDPR isn’t really a competition.
ISO 27001 helps build the security foundation.
GDPR focuses on protecting personal data and privacy.
The smart approach? Make them work together.
Better risk management. Stronger trust.
#ISO27001#GDPR#Cybersecurity#Compliance
Deciding between ISO 27001 vs SOC 2?
ISO 27001 provides a global ISMS framework, while SOC 2 delivers an auditor attestation tailored for US enterprise deals.
Find out which report your business actually needs:
👉https://t.co/KF0GfUdCJm
#ISO27001#SOC2#Compliance
The strongest security program isn’t built only with technology.
It’s built with technology + processes + people who understand their role in protecting the organization.
Start strengthening the human layer of security.
#SecurityAwareness#Cybersecurity#Compliance
Security incidents don’t always start with sophisticated attacks.
Sometimes, it starts with one click, one weak password, or one overlooked phishing email.
Security Awareness needs to be an ongoing process—not a once-a-year training session. 👇
That’s where SecureSlate’s Security Awareness Training can help.
It gives organizations a structured way to train employees, strengthen security awareness, and make security education part of the company culture.
And here’s the important part:
Security training shouldn’t end after an employee watches a video or completes a quiz.
It should be continuous, measurable, and easy to manage.