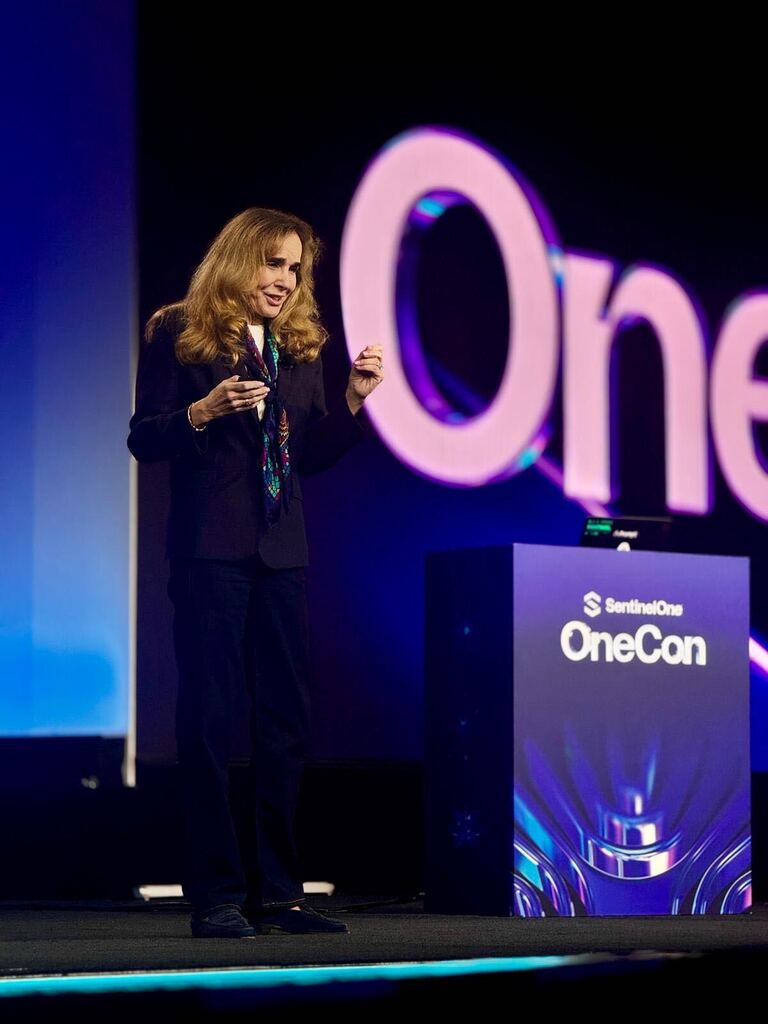
AI agents now hold credentials and act across the enterprise. At OneCon, we unveiled:
🛡️ Singularity™ ADR to stop rogue and malicious agents at machine speed
⚡ Singularity ASOC brings security superintelligence to the SOC
🤝 An expanded PartnerOne program to equip partners to build and scale AI Security practices
Learn more 👉 https://t.co/ZyfduZwHTs
AI research keeps pushing for more powerful models. Harvard professor James Mickens thinks it's time to rethink that priority.
At LABScon26, Mickens made a provocative case: right now, the only good AI research is safety research.
Read: https://t.co/vvYzedVWPF
🚨 Various vulnerabilities and security events took over this past week in what’s being called “Black October”, which attackers reportedly chaining flaws to root firewalls and cyber defenders releases emergency patches for Node2SHELL.
🔗 https://t.co/n5CndeBjs2
The SentinelOne plugin is live in the Plugin marketplace in Google @Antigravity! 🔌
Connect Purple AI to Antigravity agents to query Singularity Console, triage vulnerabilities next to the code, investigate alerts, and hunt threats in natural language. https://t.co/9cDSG3XPwY
#AI is finding vulnerabilities faster than teams can triage them. Wayfinder Frontier AI Services is adding Claude #Mythos 5.1, Anthropic’s most capable model class for cybersecurity, to find what exists, validate what’s exploitable today, and set the order for fixes. https://t.co/oSGQyXApvA
With PHP2SHELL, eMudhra, LiteLLM and more, AI is helping attackers move faster and cheaper. That was the message at #OneCon: fundamentals and defense in depth win, and behavior is the signal that holds up ⚡
Join us on Wednesday for a deeper look into the threats we are monitoring: https://t.co/QuYUjFbVIy
🚨 This week, a Nigerian man was sentenced to eight years for spearphishing and tax fraud, while a China-linked actor deployed agentic AI to compromise cloud supply chains and PHP warns of two critical-level RCE flaws.
🔗 https://t.co/RElld7bh38
PHP2Shell: two critical PHP flaws (CVSS 9.2) let unauthenticated attackers execute code on web servers. Patch first. SentinelOne stops post-exploitation activity at runtime in protect mode. https://t.co/gmAYNJJv7S
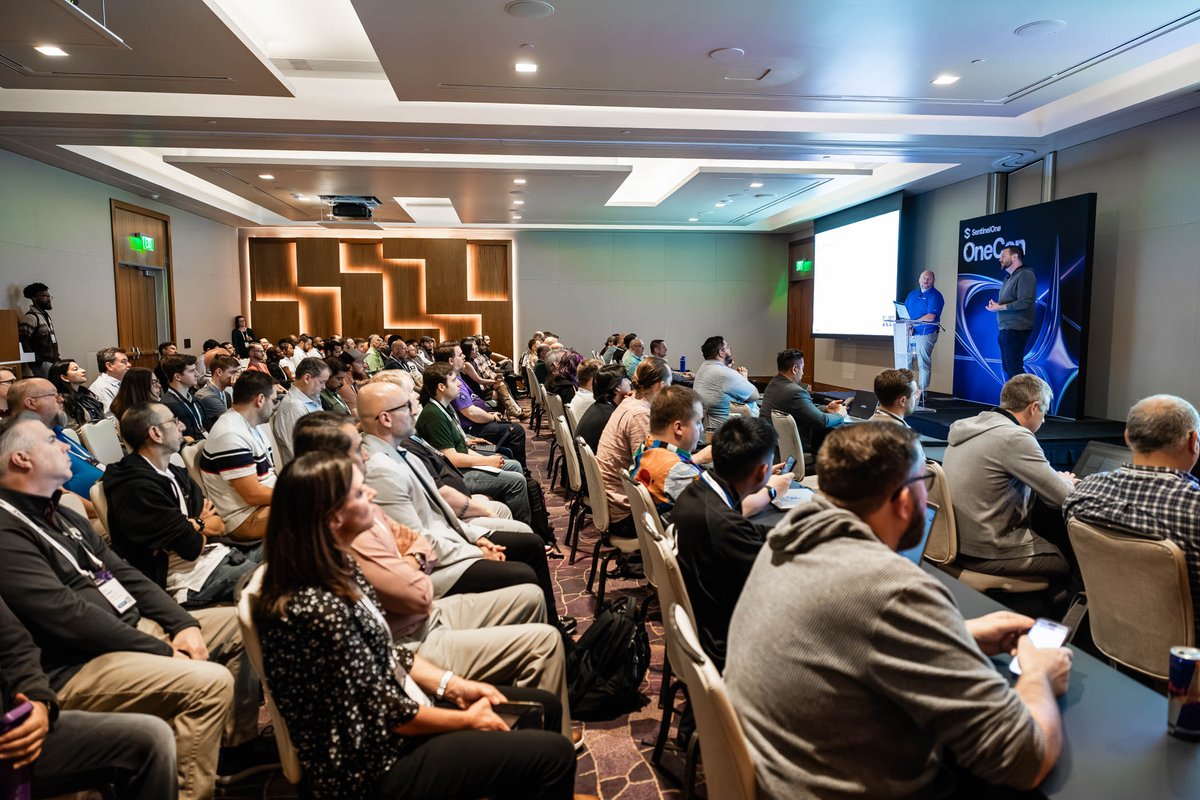
Connections are happening all over the #OneCon expo hall. 🤝 Great conversations on AI Security, new ideas, and the people who make this community strong. 🛡️
"Automation only works if you can trust it. It has to be reliable, and its confidentiality has to be preserved. You can't automate security on data that leaves your control." - Dr. Nicandro Scarabeo, Bell Canada Technical Director, Cyber Security and Architecture
#OneCon
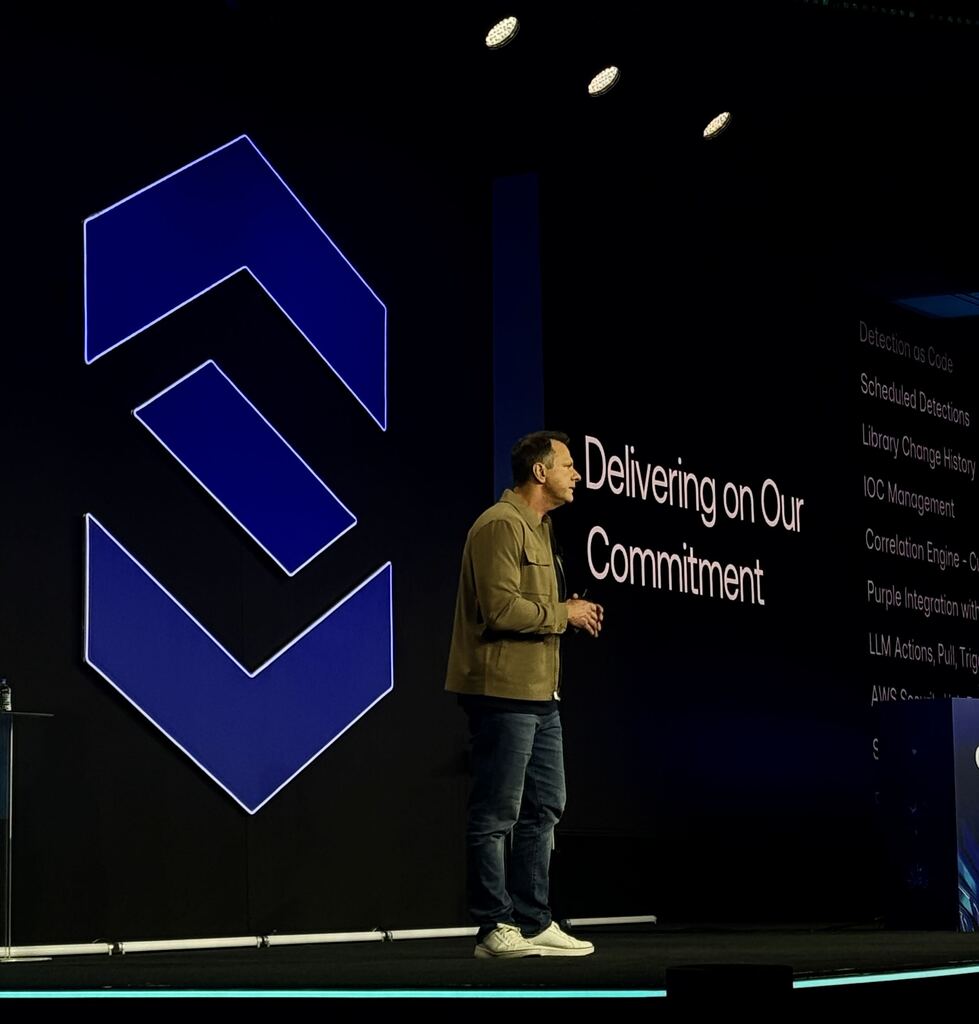
"We’ve improved our platform detection functionality by delivering over 2000 new AI-powered detections, increasing coverage across new threat actors, campaigns, and TTPs." - Chris Corde, SentinelOne Chief Product Officer
#OneCon
"Our responsibility is to make security strong enough and fast enough for our future.
Today, agents run inside your business with credentials, tools, identities, and the ability to act independently.
We plan to solve this completely new actor in the enterprise." - Tomer Weingarten, SentinelOne co-founder and CEO
#OneCon