#SpecterBash is back! 😎
Join us October 5-8 in Denver, CO for four days of adversary tradecraft courses, evening events, and the most fun you’ll have leveling up your infosec skills.
🎃 Registration is open: https://t.co/aPi6KVhdIw
Introducing Ghostwriter Skills 👻
The first release helps with report templates, template QA, report readiness checks and executive summary drafts. Practitioners remain responsible for the final analysis.
Read more from @cmaddalena & explore each skill: https://t.co/WkOYpOxjk2
Introducing SO:Brief, our new series delivering quick insights from SpecterOps experts. 🎥
First up: @MGrafnetter breaks down what passkey phishing can actually look like.
Watch the brief, then go deeper in tomorrow’s webinar 👉 https://t.co/o563r9Bmzb
We’re up and running at the Gartner Security & Risk Management Summit in London 🇬🇧
Stop by booth #615 to meet our team and learn how BloodHound Enterprise helps organizations eliminate identity attack paths before attackers can exploit them.
Come say hello! #GartnerSEC
This is your sign to reserve your spot for @MGrafnetter's webinar this week!✨
Hear about Pass-the-Passkey, a novel & actively researched category of malware-initiated attack techniques targeting passkey auth that can enable cloud user impersonation.
👉 https://t.co/NNXkvbBqcp
New #BloodHoundBasics post c/o @ScoubiMtl! 🎉
As of v9.7 BH supports multiple destinations in Pathfindings. You can force a path to traverse a specific node. It is also possible to rearrange the order of the nodes a path must traverse.
For more info 👉 https://t.co/KZmm5amecb
Don't miss @JustinKohler10's session at Infosec Nashville TOMORROW!
Justin will explore why defenders need to shift focus to the identity layer as agents, non-human identities, and hidden trust introduce new risk. https://t.co/FglBct3Ibx
Our team is at #InfosecNashville 🤠
Stop by to say hi to the team, discuss your burning questions on identity attack path management & BloodHound, and grab some swag!
Introducing CiliumHound, a new BloodHound OpenGraph extension from @Sw4mp_f0x!
Feed it your Cilium network policies (YAML/JSON), get back a searchable graph scoped to each K8s namespace.
Check it out ⤵️ https://t.co/HrfBDPDjfw
Don't miss @JustinKohler10's session at Infosec Nashville TOMORROW!
Justin will explore why defenders need to shift focus to the identity layer as agents, non-human identities, and hidden trust introduce new risk. https://t.co/FglBct3Ibx
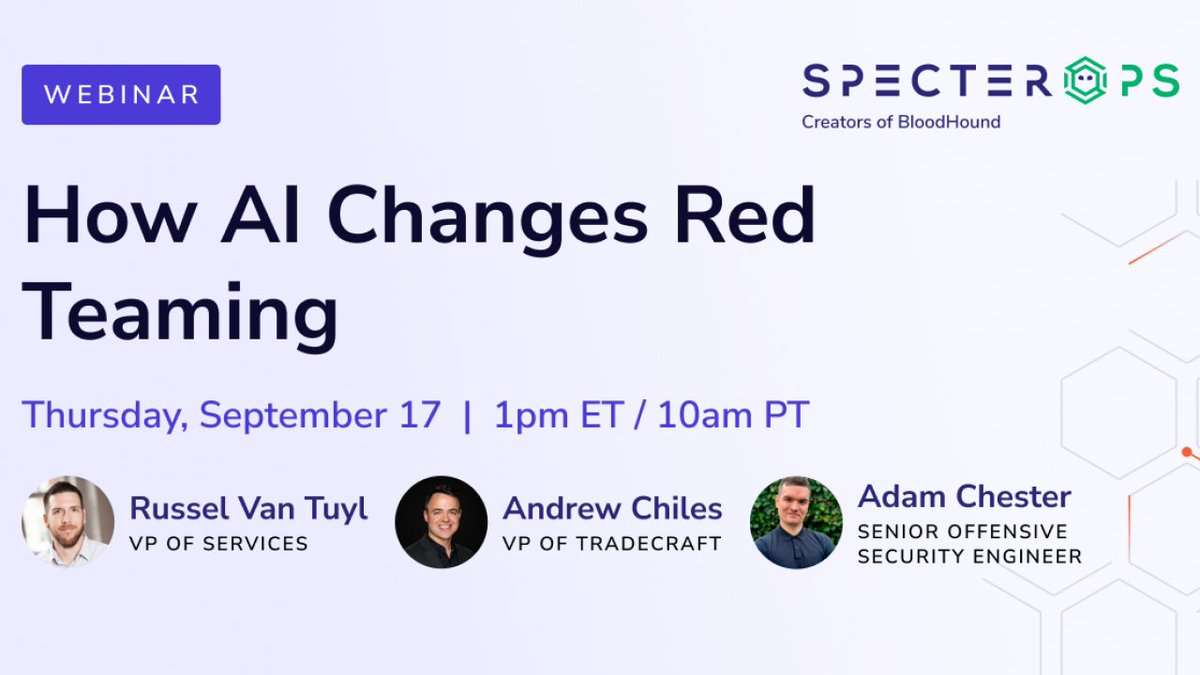
Don't miss our webinar TOMORROW!
Hear from @ne0nd0g, @AndrewChiles & @_xpn_ on how AI is reshaping how adversaries operate and what red teams need to evaluate.
➡️ https://t.co/7gDwdyQbm2
Don't miss our webinar TOMORROW!
Hear from @ne0nd0g, @AndrewChiles & @_xpn_ on how AI is reshaping how adversaries operate and what red teams need to evaluate.
➡️ https://t.co/7gDwdyQbm2
Ghostwriter v7.3.0 is currently in testing through September 30, and we want your feedback. Try it out and let us know what you think!
https://t.co/uAvU05fBVb
A fresh new look is coming to Ghostwriter. 👻
v7.3.0 brings a redesigned dashboard, new engagement bar, customizable sidebar, accessibility improvements, and a UI refresh across the application.
@cmaddalena unpacks what’s new. 👇 https://t.co/3wtbEMbMXB
New #KnowYourAdversary 🚨
Visibility is the foundation of effective exposure mgmt.
Vlad Rotshteyn joins @jaredcatkinson & @JustinKohler10 to discuss prioritizing risk w/ context, Attack Path Management, AI & why security fundamentals still matter.
🎧: https://t.co/jeQcjINGZo
Identity-driven attacks are among the most critical threat vectors in modern environments.
Identity-driven Offensive Tradecraft at #SpecterBash covers the methodology for discovering & exploiting identity attack paths across on-prem & hybrid environments. https://t.co/xxqSOSJOqT
AI is speeding up attacks while expanding the enterprise attack surface.
At Infosec Nashville, @JustinKohler10 will explore why defenders need to shift focus to the identity layer as agents, non-human identities, and hidden trust introduce new risk. https://t.co/FglBct3Ibx
AI is reshaping how adversaries operate and what red teams need to evaluate.
Join @ne0nd0g, @AndrewChiles & @_xpn_ next Thursday to explore assumed breach, attack paths, AI deployments & more.
Save your spot: https://t.co/7gDwdyQbm2
This works for all node types, and current built-in nodes can be found here: https://t.co/IZKUVUCkQG, or under the respective extension (e.g., Github, Okta, etc.) here: https://t.co/dJhS9Bk2X1
🧵: 2/2
Happy #BloodHoundBasics Friday from @Sec_Distilled! 🙌
Got a lot of like-named Principals showing up in BloodHound? Try using the node type to filter on specific objects: Domain:PHANTOM.
🧵: 1/2
Ad sim tradecraft, live defense data, enterprise-scale labs.
Red Team Operations at #SpecterBash doesn't just teach you how to attack. It teaches you how to think, adapt & operate under pressure. The scariest part? How much you didn't know going in.
🎃 https://t.co/aPi6KVhdIw