Claude Code, Codex or Gemini CLI for Bug Bounty? 🤔
We put all three through blind PortSwigger labs 🧪
These tests aren’t benchmarks, but the patterns observed say a lot about where each agent could fit in your workflow 👇
https://t.co/0loI0IMtAj
“Both sides can win” 🤝
@BancoGalicia returned to Ekoparty 🇦🇷 for another live Bug Bounty earlier this month, bringing diverse hacking techniques and plenty of collaboration.
Read the recap, see the photos and hear from the winners 👇
https://t.co/zHFlnJvGrn
Cache poisoning gets a lot more interesting when the poison goes straight into the key 👀
@Brumens2's DEF CON talk explores cache key injection, scheme fragments and the unexpected bugs that can follow!
Read the full research below 👇
https://t.co/dnbn4NLiyu
🔒 Precautionary Security Update
Following the recent disclosure of two critical PHP vulnerabilities (CVE-2026-109618 and CVE-2026-109619, "PHP2Shell"), we have proactively placed our platform in maintenance mode.
To safeguard the data and security of our clients and users, access is temporarily blocked while our team applies the necessary patches across our infrastructure.
We will provide an update here as soon as maintenance is complete and platform access is restored. Thank you for your patience and understanding.
Want to sharpen your IDOR, stored XSS and information disclosure skills? 🧠 The hunters who topped our 2025 leaderboards for these bugs – @XelBounty, @Chackal__, @drak3hft7 – shared their best-practice tips 👇
https://t.co/uhs59KkXWG
🏁 #SPIRITCYBER26 has come to a close after weeks of persistence, creativity and pushing the limits.
Huge congratulations to the top five:
🥇nullIoT
🥈One Prompt to Pwn Them All
🥉Peenoise
🏆Hamtarou
🏆Undefined Behavior
👏 Big shoutout to all the team that took part in the qualifiers. Every valid report helped push the challenge further and strengthen the connected technologies supporting Singapore’s #SmartNation.
🤝 Proud to have joined forces again with @CSAsingapore for another round of hacking for a good cause.
Till next year!
Hello,
We are unable to provide any information regarding this subject.
We invite you to contact [email protected] who are in communication with the relevant teams.
If you've already contacted them, they'll treat your ticket in due course.
Thank you for your understanding,
The YesWeHack team
⌛ Last chance to shake up the leaderboard.
The #SPIRITCYBER26 finalists know their targets well, but one overlooked detail or breakthrough could still change everything. ⚡Final day starts now!
#SICW2026@CSAsingapore
��� Behind every finding: trial and error, dead ends, and sometimes another hunter asking, “Have you tried this?”
That’s the power of the #BugBounty community. Different minds with a shared goal of making digital systems safer for all.
Leading the pack at #SPIRITCYBER26: @bytehx343 @0xakm, @mgthura404 from Team nullIoT🔥
Stay tuned for the final push tomorrow.
#SICW2026 @CSAsingapore
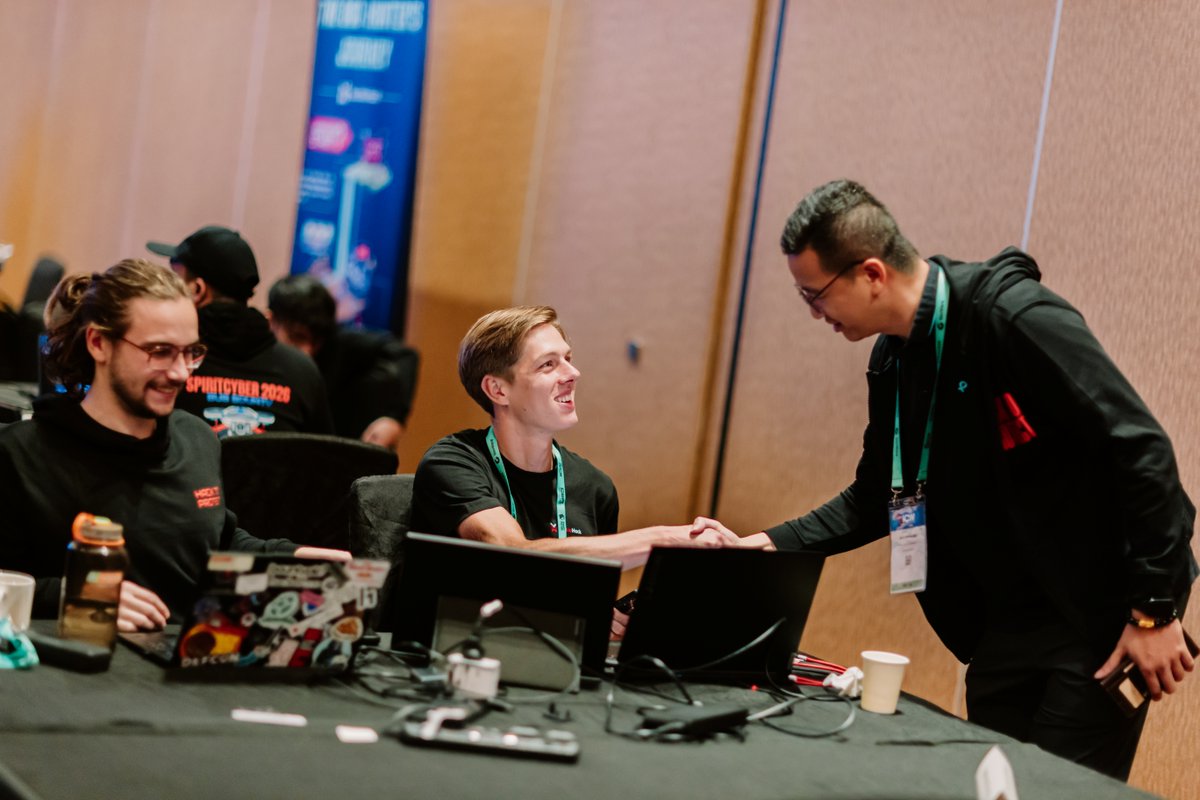
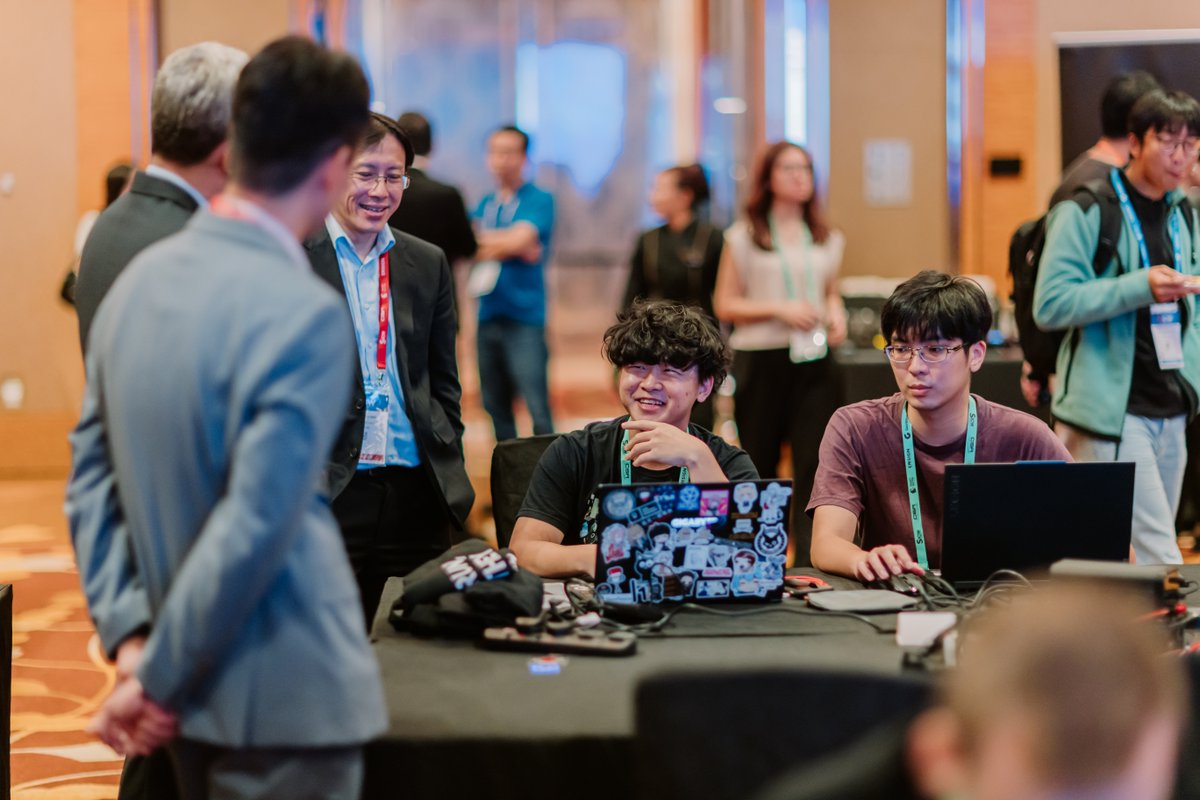
👀 #SPIRITCYBER26 so far: 10% typing, 90% staring intensely at the screen.
Our 5 finalist teams spent the day pulling apart these IoT devices and refining their exploits. Some findings come quickly, but the interesting ones usually don’t.
Back tomorrow for Day 2! 🔎
#SICW2026@CSAsingapore