I’m done being a ghostwriter.
Okay, maybe not the writer part. I’m just done being the ghost behind the pen.
I’ve been writing for years, mostly through referrals. I’d get a gig, research, write, deliver, get paid and disappear.
No portfolio. No documentation, because my clients never asked for one. Barely any public proof that I even write.
As an introvert, I love working behind the scenes 🤭
But I’ve been making money from writing for years, and recently I thought: why not be more intentional about it and make even more?
So I’m finally building my writing portfolio publicly.
I’m also building my skills in Web & API Security, so I’ll be bringing both worlds together:
Cybersecurity + Technical Writing.
Expect security write-ups, technical articles, walkthroughs and plenty of learning in public.
And yes, I’m open to writing opportunities. If you need a writer or know someone who does, my DM is open.👏
No more hiding behind the work. Time to let the work introduce me.
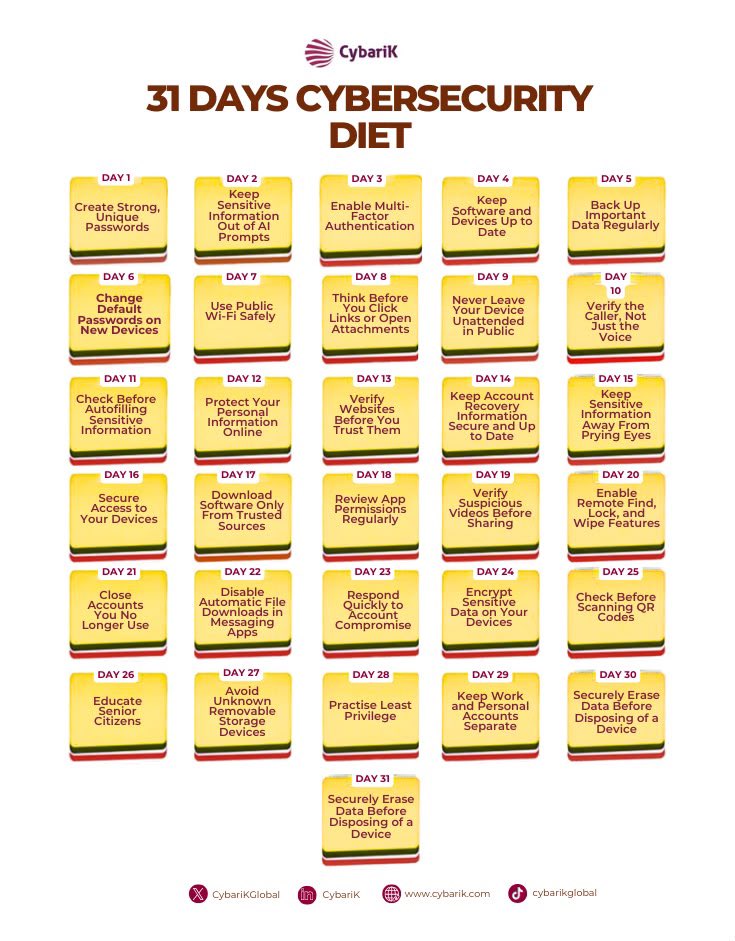
Day 1 - Create Strong, Unique Passwords ✨
“Same passwords everywhere? That’s an attackers’ buffet 👀”
Your password is your first line of defence, so don’t make it easy to guess. Use at least 16 characters, avoid personal or predictable information, and most importantly, never reuse the same password across different accounts.
Think of it this way: if you use the same password for your email, social media, and work accounts, if an account is compromised, it’s like you have handed over the keys to your digital life. Instead, create a unique password (or a passphrase) for each account and use a password manager if keeping track becomes difficult.
Quick tip: A random phrase like “PurpleBananasDanceAtMidnight-!” is stronger than “P@ssw0rd!”
What’s one password habit you think everyone should practice?
@CybarikGlobal #CybersecurityDiet
Imagine someone trying to guess your password, and all they need is a quick look at your profile.
Your name is there. Your birth year is there. And your password? A combination of both.
You chose it because you wouldn’t forget it. Unfortunately, someone else might find it easy to guess.
“Okay, let me add a capital letter and an exclamation mark.”
That’s a change, but the predictable pattern is still there.
A stronger approach is to use a long, unpredictable password. Aim for at least 16 characters. A password manager can generate and store one for you, or you can use a long passphrase made from randomly chosen, unrelated words.
Now you have a strong password.
You’re pleased with it, so you decide to use it for your email, Instagram, LinkedIn, and that shopping website you visit occasionally.
After all, it’s strong, right? 👀
Then the shopping website suffers a breach, and your login details are exposed.
An attacker doesn’t have to guess your strong password anymore. They can simply try those same details on other platforms.
That’s why a strong password also needs to be unique to each account. One exposed password shouldn’t put several accounts at risk.
Today is Day 1 of Cybarik’s 31 Days Cybersecurity Diet, and I’m starting with a habit we can all practise: creating strong, unique passwords.
Your task today: pick one account. If its password is weak or used elsewhere, give it a strong password of its own.
#CybersecurityAwareness #31DaysCybersecurityDiet #Cybarik
Throughout the month of October, I will be engaging in a 31 days Cybersecurity Diet as part of my contribution to the conversations regarding Cybersecurity Awareness.
Each day, I will post a basic Cybersecurity topic, share few tips and ask a question. I want to encourage everyone doing Cybersecurity to join me by using the Cybersecurity diet to also educate people about basic Cybersecurity awareness. Let’s continue to spread the word and support the ecosystem to reduce Cybersecurity breaches 💪
I made a conscious decision not to engage with posts about politics, religion, tribe, or gender wars.
But honestly, it’s so difficult because I keep seeing annoying things here every single day. 😭
Throughout the month of October, I will be engaging in a 31 days Cybersecurity Diet as part of my contribution to the conversations regarding Cybersecurity Awareness.
Each day, I will post a basic Cybersecurity topic, share few tips and ask a question. I want to encourage everyone doing Cybersecurity to join me by using the Cybersecurity diet to also educate people about basic Cybersecurity awareness. Let’s continue to spread the word and support the ecosystem to reduce Cybersecurity breaches 💪
Tomorrow by 7PM WAT . Discord.
@Dghost_Ninja takes us from recon to exploitation, live.
Quick poll before we start: What's your first move when testing an API?
🔍 Recon the docs
🚪 Probe the endpoints
🔑 Attack the auth
Reply below 👇
@apisecu#TechnicalTuesdays#APIsecUNija
My book launch on X space is coming up next week Sunday. You are all invited….i will be moderating it myself and talking through the chapters in the book.
Then we do one space between November and December for people who might have questions after reading the book 🥳
https://t.co/GVjyotrAuU
You encounter certain people and you immediately become grateful for how your parents raised you. I overheard this girl talking about being sleepy and wishing she had gum, I immediately offered mine and she took 5 out of it, threw one into her mouth and wrapped 4 in a paper🤦🏾
I passed my Security+ Exam!!! 🤭
Several weeks of grinding, and it paid off
Thank you to my study partners @ritewealth, @TheCloudSE & @Sumayyyyyyyah. Our late night grinding 🔥
To my accountability partner @cyberjeremiah, thank you for the constant push & mandatory check-ins🤲🏼