Their cloud. Your data. Your keys should be under your control.
Simplify encryption key management across hybrid and multicloud environments with #Thales CipherTrust Cloud Key Management.
Learn more: https://t.co/epFibjEE79
#DataSecurity#CloudSecurity
Smarter AI agents. Greater API exposure.
CISOs need stronger visibility, access controls, and governance to stay ahead.
📘 Get @Thales’ guide to API security in the AI era. DM us!
#AI#Cybersecurity#APISecurity#AdwebTech
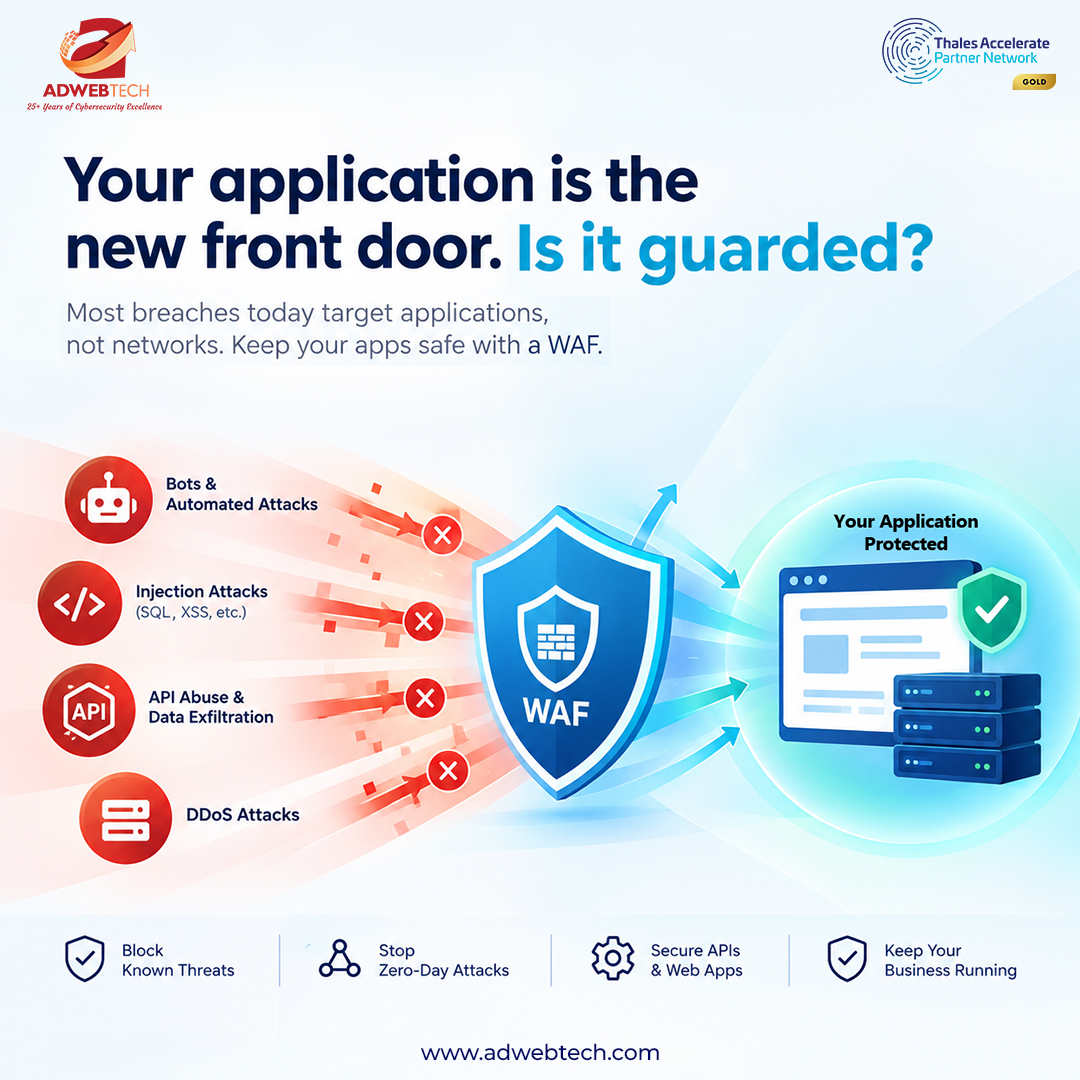
Your app & APIs are the most attacked surface today — not your network.
A WAF blocks bots, OWASP Top 10 exploits & API abuse in real time, before they hit your systems.
#WAF#AppSec#CyberSecurity
Shorter certificate lifecycles are changing the game.
More certificates. More renewals. More opportunities for something to be missed.
Visibility + automation + governance can help organizations stay ahead.
Is your certificate strategy ready?
#CLM#PKI#DigitalTrust
More certificates. More renewals. More risk.
Stop scaling certificate management with spreadsheets. Scale it with automation.
#CLM#Cybersecurity#CertificateManagement
47 days isn't far away. Is your certificate strategy ready?
Less validity. More renewals. More risk.
CLM = visibility + automation to discover, monitor & renew certificates before outages happen.
📩 [email protected]#CLM#SSL#TLS#PKI#CyberSecurity
Still managing #SSL/#TLS certificates with spreadsheets?
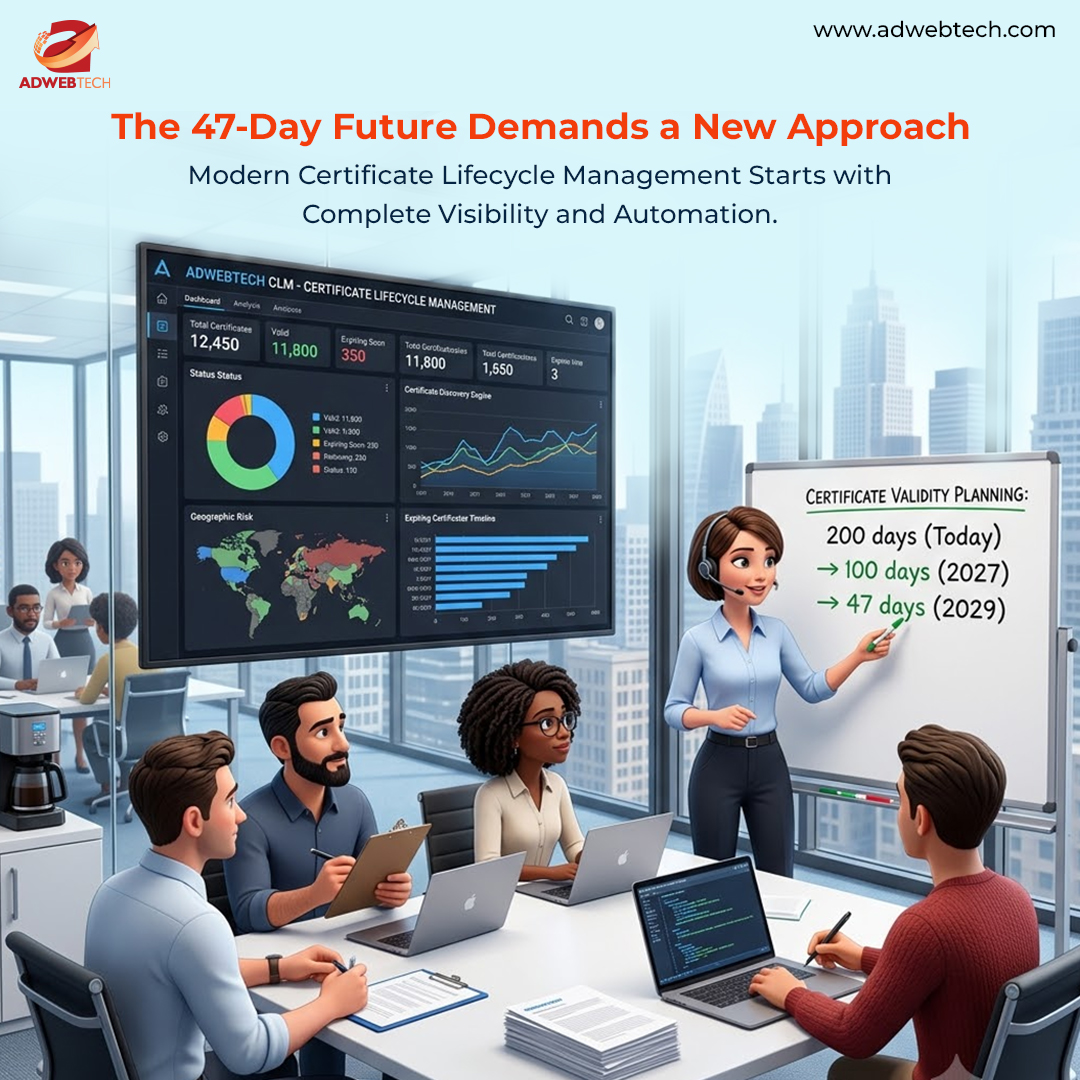
100-day certificates are coming. 47-day certificates aren't far behind.
It's time to automate certificate discovery, monitoring & renewals before manual tracking becomes a business risk.
📩 [email protected]
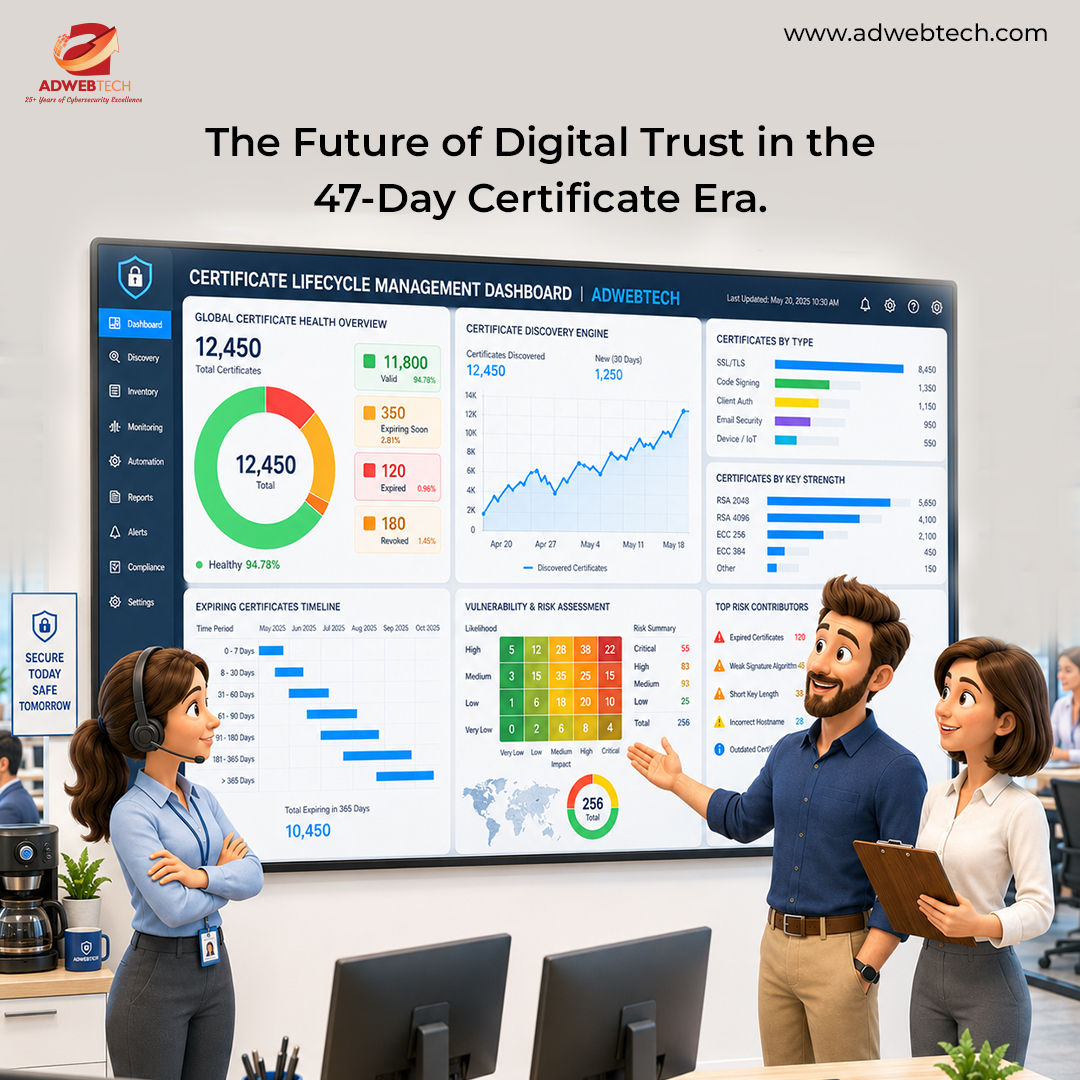
47-day SSL/TLS certificate validity is coming.
More renewals. More monitoring. Less room for error.
Manual tracking won't keep up.
Automate certificate discovery, monitoring, and renewals with AdwebTech CLM before outages happen.
#CLM#SSL#TLS#PKI#CyberSecurity
Still managing SSL/TLS certificates with spreadsheets?
📅 2027: 100-day validity
📅 2029: 47-day validity
Can your current process keep up?
Don't wait for missed renewals and outages. Automate with CLM before the countdown begins.
#CLM#SSL#CyberSecurity#PKI#Automation
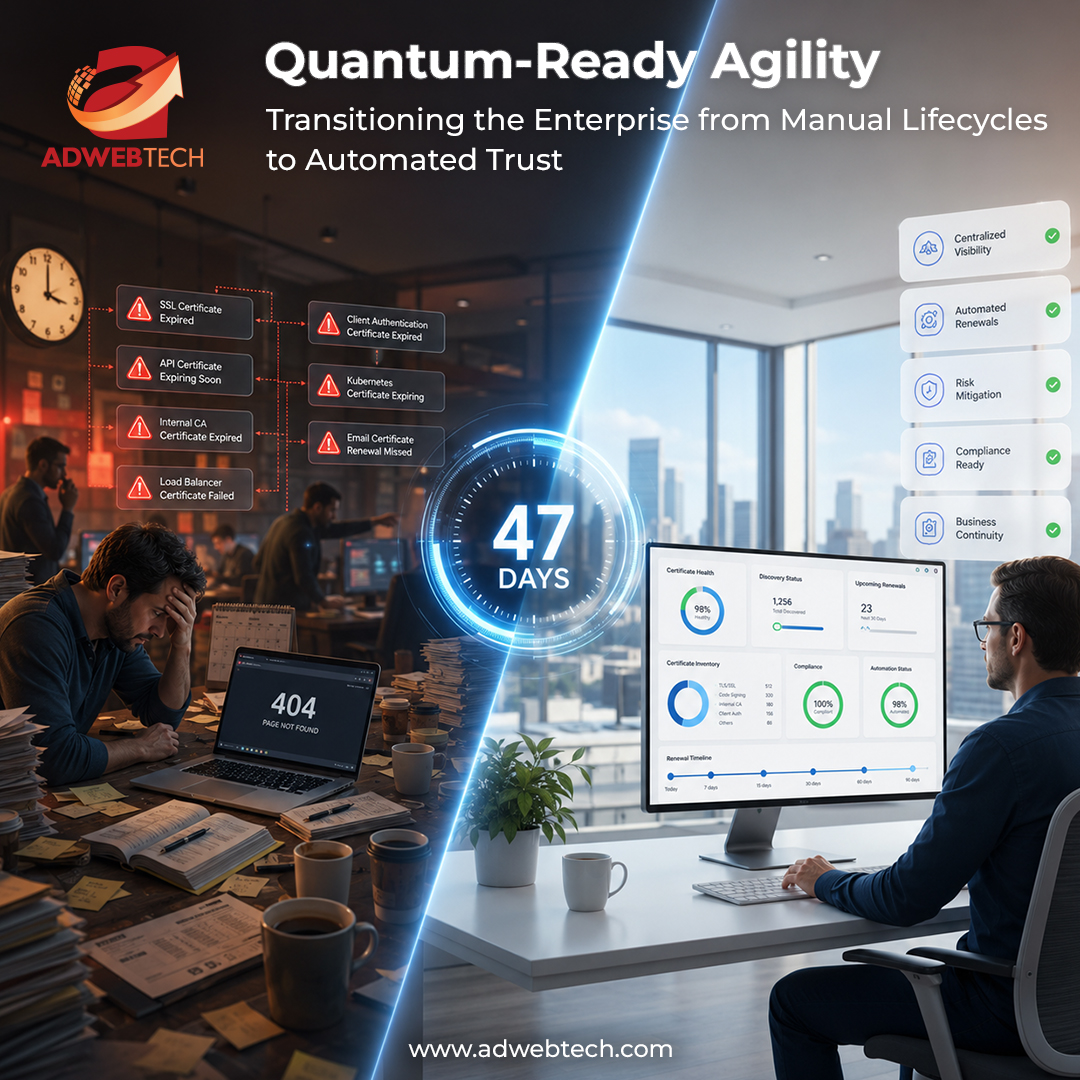
Two IT teams. Two different mornings.
One is fixing expired #SSL certificates, outages, and missed renewals.
The other is innovating because Certificate Lifecycle Management is automated.
With 47-day certificate validity, manual management won't keep up.
#CLM#CyberSecurity
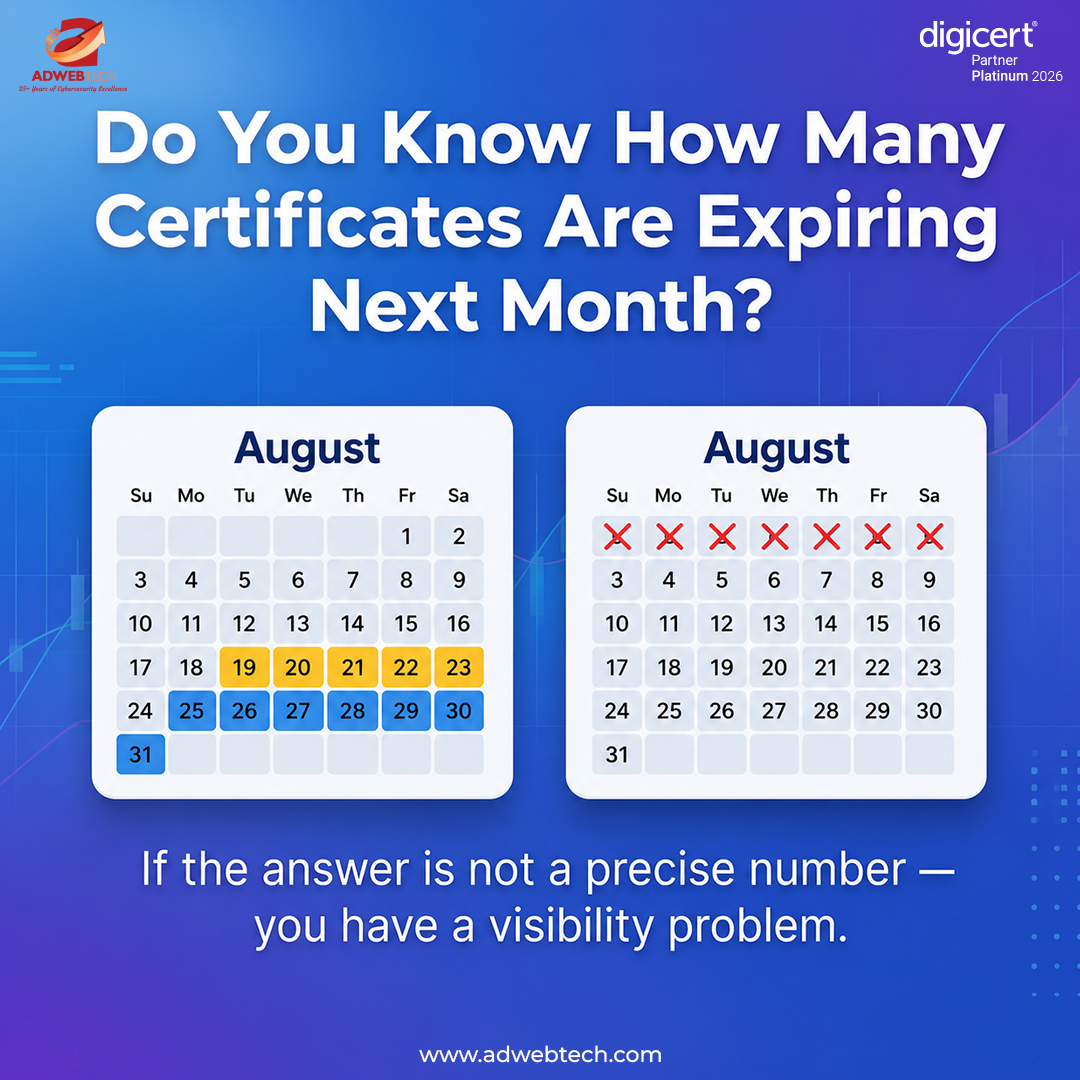
How many SSL/TLS certificates expire next month?
If you don't know the answer, you have a visibility problem. Hidden certificates and missed renewals can lead to outages and compliance risks. Automate with CLM.
#CLM#SSL#CyberSecurity#PKI#Automation
⏳ 47 days.
That's the future of #SSL certificate validity.If you're still managing certificates manually, it's time to rethink your strategy. Automate with CLM and stay ahead of outages and compliance risks.
#CertificateLifecycleManagement#CyberSecurity #Automation
Who owns your encryption keys in the cloud?
With BYOK and HYOK on Thales HSMs, you stay in control of your keys while leveraging the scalability of the cloud. Secure your data without compromising ownership.
#Thales#CloudSecurity#BYOK#HYOK#CyberSecurity#Encryption
How many #SSL certificates does your organization have?
Now imagine renewing every one of them every 47 days.
That's where the industry is heading.
Without #automated Certificate Lifecycle Management, manual renewals become a serious business risk.
#CyberSecurity#Adwebtech
What happens when SSL certificates expire every few weeks instead of every year?
More renewals. More risk. More outages.
Manual certificate management won't scale. #Automated Certificate Lifecycle Management (#CLM) is the future.
Is your organization ready?
#PKI#SSL#TLS
One certificate expiring isn't a problem.
Hundreds expiring every 47 days is.
Manual certificate management won't survive the 47-day era. Continuous renewals mean higher operational risk, more downtime.
Automate with #Certificate Lifecycle Management and stay ahead.
#technews
How many digital certificates are protecting your business today?
If you don't know, that's a security risk. One expired certificate can lead to downtime, compliance issues, & lost trust.
Gain complete #visibility with AdwebTech's Certificate Lifecycle Management.
#CyberSecurity