Building PixelQ, a self-hosted image optimization service that processes uploads through background workers.
Stack: Fastify, PostgreSQL, Drizzle ORM, and Redis.
Learning Docker Compose, job queues, failure recovery, and worker scaling by building a real system.
#DevOps#Docker
Day 10 answer: zip the project, run an Architecture Review.
The 24h auto-scan only covers deployed resources. Pre-deployment code needs the separate review feature built for exactly that.
That's 10 days. Thanks to everyone who voted, argued, and corrected me.
Day 10/10
You've got a Terraform project that hasn't been deployed yet. You want AWS's new Well-Architected Agent to catch architecture issues before any of it touches real infrastructure.
What do you actually do?
#AWS#LearnInPublic
Day 10/10
You've got a Terraform project that hasn't been deployed yet. You want AWS's new Well-Architected Agent to catch architecture issues before any of it touches real infrastructure.
What do you actually do?
#AWS#LearnInPublic
Day 9 answer: deactivate the key immediately.
Terminating instances doesn't help, the key can just spin up new ones elsewhere. Kill the credential first, clean up the damage second, figure out the leak third.
Day 10 tomorrow. Last one.
Day 9/10
2:47 AM: an AWS access key got pushed to a public GitHub repo by accident. By breakfast, crypto miners were running in 6 regions and the bill hit $47,000 overnight.
The key is still active right now. What's your first move?
#AWS#LearnInPublic
@kidtsang Agreed, and AWS's own disclaimer backs this up, it's generative AI, so the recommendations can be wrong. That's exactly why understanding the fix matters as much as applying it. A diff you don't understand is a risk whether a model suggested it or a person did.
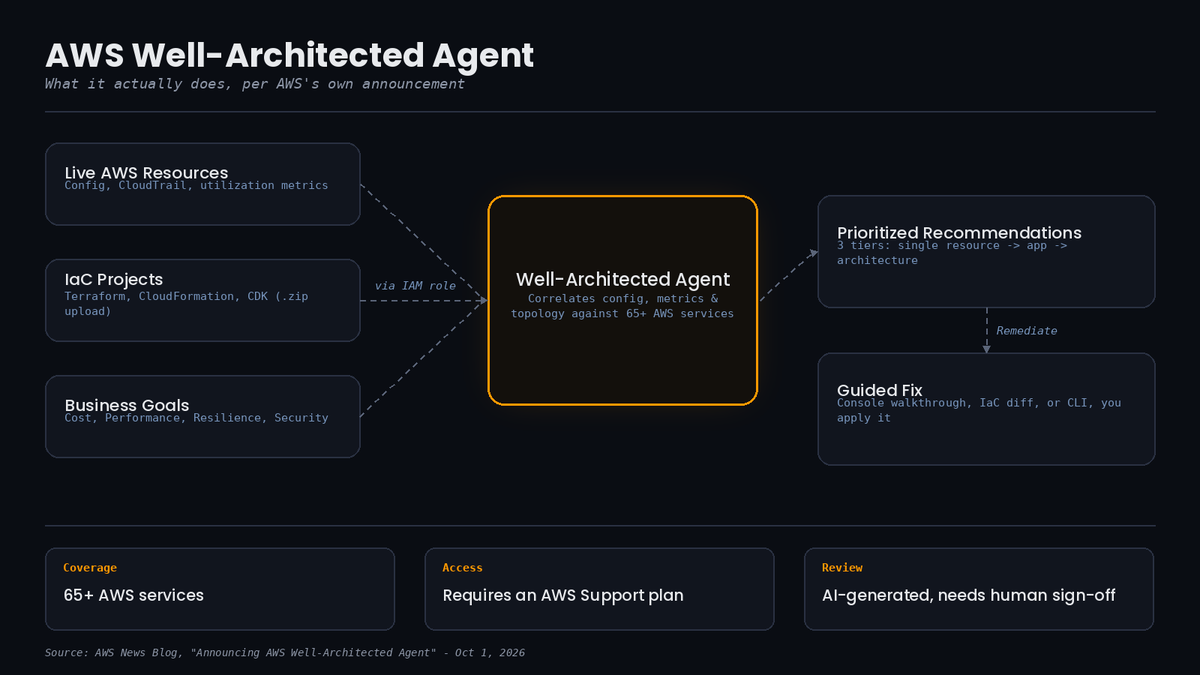
AWS Well-Architected Agent just hit public preview.
It scans live resources and IaC across 65+ AWS services, then hands back fixes as Terraform/CFN/CDK diffs or CLI commands, you apply them yourself.
Needs an AWS Support plan.
https://t.co/G2PvDm6jw4
#AWS#CloudArchitecture
@twtayaan Worth flagging: it's gated behind an AWS Support plan, not an open preview. You still provision your own IAM role before it can read anything, and AWS's own disclaimer says the recommendations can be wrong, so still a human review step before you ship the fix.
Day 9/10
2:47 AM: an AWS access key got pushed to a public GitHub repo by accident. By breakfast, crypto miners were running in 6 regions and the bill hit $47,000 overnight.
The key is still active right now. What's your first move?
#AWS#LearnInPublic
Day 8 answer: API Gateway's 29-second limit.
It's a hard ceiling on sync REST calls, no setting changes it. Lambda running 15 minutes doesn't matter. Long jobs need to go async: return a job ID now, poll for the result later.
Day 9 up shortly.
Day 8/10
Your API triggers a Lambda that builds a report, taking about 2 minutes. Every call returns a 504, but CloudWatch shows the function finishing fine a minute later. Lambda's timeout is set to 5 minutes.
What's the real problem?
#AWS#LearnInPublic
Day 8/10
Your API triggers a Lambda that builds a report, taking about 2 minutes. Every call returns a 504, but CloudWatch shows the function finishing fine a minute later. Lambda's timeout is set to 5 minutes.
What's the real problem?
#AWS#LearnInPublic