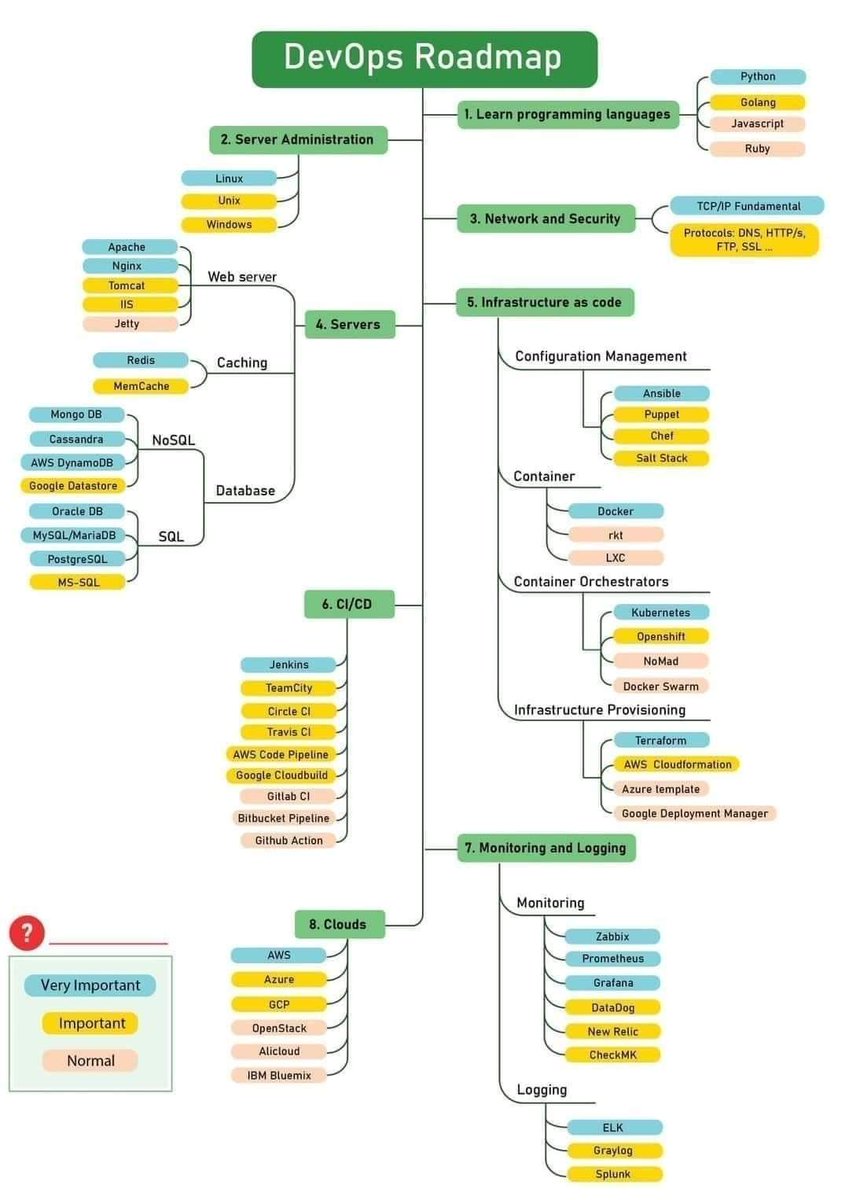
DevOps Roadmap. You'll notice that the #DevOps roadmap covers a lot of concepts within software development. That's because #DevOps covers the entire software creation and maintenance process from development to operations.
#GitOps#DevOps#DevSecOps#DevOpsTools
Your devs are using Shadow AI and you don’t know.
Cloudflare’s 2025 report:
- 44% of employees use unapproved LLMs
- 31% paste customer data into ChatGPT
- Avg org has 87 unsanctioned AI apps New AI Gateway Policies
#CloudSecurity#AI#DevSecOps
This is DevSecOps at light speed — security becomes a feature, not a bottleneck. For GitOps teams: #DevSecOps#GitOps#AIinDevOps#GitHubCopilot Full details: https://t.co/DAVN2iwLzk"
🚨 GitHub just dropped Copilot Autofix — AI that doesn’t just find vulnerabilities, it explains and fixes them in your PRs with one click. Here’s how it works:
Scans code via SAST, SCA, and secret detection
Generates a fix PR with full context and diff
Integrates natively into GitHub Actions and CodeQL
Supports Python, JS, Java, Go, and more Early benchmarks: 87% of fixes accepted, 62% faster remediation.
Azure DevOps updates: Secrets retire Sept 2025—migrate to Key Vault for encrypted storage; TFS 2015 support ends Oct 14, urging upgrades. This enforces shift-left security, cutting exposure 20% via automated vaults in CI/CD. For cloud teams, Prep now to avoid disruptions.
DevSecOps core: Unites dev/ops/sec for early automated checks in pipelines, catching issues pre-deploy; GitOps automates via Git for versioned, consistent infra mgmt. Speeds fixes 40%, ensures compliance in cloud-native. With threats rising, integrate for secure delivery.
Why k9s is a Kubernetes game-changer for DevOps: This CLI tool provides a single-screen dashboard for viewing pods, deployments, and services in real-time; allows quick context switching between clusters/namespaces;
ffers keyboard shortcuts for instant access to logs, shell execution, resource editing, and deletions—streamlining troubleshooting. It reduces command-line chaos from kubectl, speeding up workflows by 10x and minimizing errors in complex environments
Think your managed K8s is secure?
Staggering new data: 54% of GKE clusters and 39% of EKS are exposed to the internet. An unnecessary risk for your cloud environment.
#Kubernetes#DevSecOps#CloudNative#KloudCenter https://t.co/ksglyk4iiH
Cloud Security warning from Datadog's report:
54% of Google Kubernetes Engine (GKE) clusters and 39% of Amazon Elastic Kubernetes Service (EKS) clusters are unnecessarily exposed to the internet, increasing vulnerability to attacks like unauthorized access or data breaches
This highlights the need for regular audits, implementing least-privilege access, and using private endpoints or firewalls. In DevSecOps, proactive checks can secure environments without sacrificing functionality—essential for hybrid cloud ops
Core principle of #DevSecOps:
Integrate security from the very beginning of the software development lifecycle, rather than bolting it on later. This means incorporating automated vulnerability scans, code reviews, and compliance checks into CI/CD pipelines during planning,
coding, and testing phases. Benefits include early threat detection, reduced remediation costs (up to 90% savings), faster delivery of secure applications, and stronger overall resilience against evolving cyber threats.
2025 CI/CD: GitHub Actions 62% personal, enterprises love Jenkins. Multi-tools in 41%, AI unused by 73% over security. #DevOps#CICD Link: https://t.co/6WQ8hD9SCZ
Switched to GitLab CI/CD Haven’t Looked Back . Moving from Jenkins and GitHub Actions to GitLab CI/CD was a game-changer. One platform for code, build, test, and deploy—no plugin chaos like Jenkins, no complex setup like GitHub Actions.
#gitops#devops#devsecops