THIS IS F**KING DANGEROUS
FOUND 7 REPO’S FOR ANYONE LEARNING NETWORKING,CYBERSECURITY.
CONTAINERLAB —> spin up real network topologies in containers, test routing and design without touching physical hardware.
Awesome Networking (nyquist) —> curated networking courses, tools, and learning resources in one list.
Multiplayer Networking Resources —> the definitive collection for game netcode: latency, jitter, packet loss, rollback, all the hard synchronization problems.
Scapy —> the Python packet manipulation library most security courses actually teach on.
Awesome Networking (facyber) —> a second, differently curated collection of networking courses and books.
System Design 101 (ByteByteGo) —> bite sized visual breakdowns of system design and networking fundamentals.
Sniffnet —> real time network traffic monitoring, visualized, a cleaner alternative to raw packet dumps.
REPO’S BELOW
You CAN JAILBREAK iOS 18 / iPadOS 18 On Exactly ONE Device!
⚠️ NEW VIDEO: https://t.co/ecWx1s30Uc
Yes, one single device survived the iOS 18 killing, making it the best device to purchase if you can find it for cheap as you'd have both a jailbreak and iOS 18. I can't believe Apple let this happen but boy am I glad. #jailbreak #ios
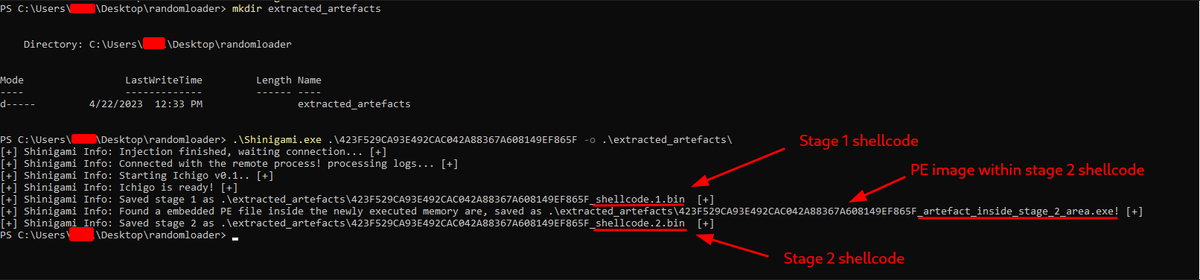
Excited to announce the latest update to Shinigami - now with a generic unpacker module! It hooks memory allocation/protection functions & adds guard pages to track shellcode execution/PE image mapping. https://t.co/GAVAMBwUQB #unpacking#reverseengineering
Disclosed today at @Disobey_fi - psexec from #impacket expose the target system for authenticated command execution as SYSTEM. That means any user that can authenticate over the network (usually Domain Users) can run code as SYSTEM over the network.
I got a lot of questions about this cause this don't make no damn sense. You telling me you can auth to AAD just using an application ID for an unconfigured app?
Just gimme the CVE now, fam. 😭
https://t.co/PmSp55GKXN
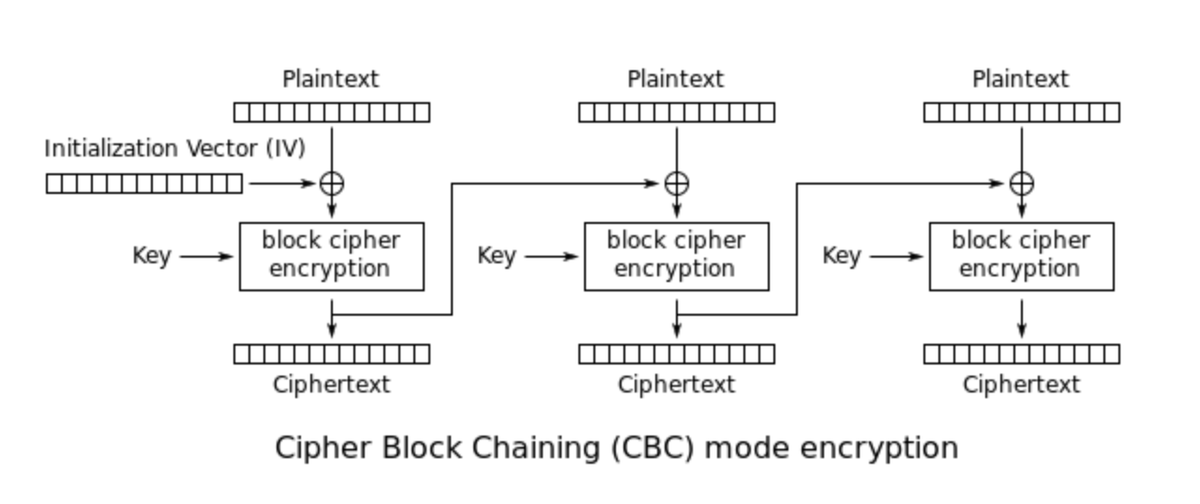
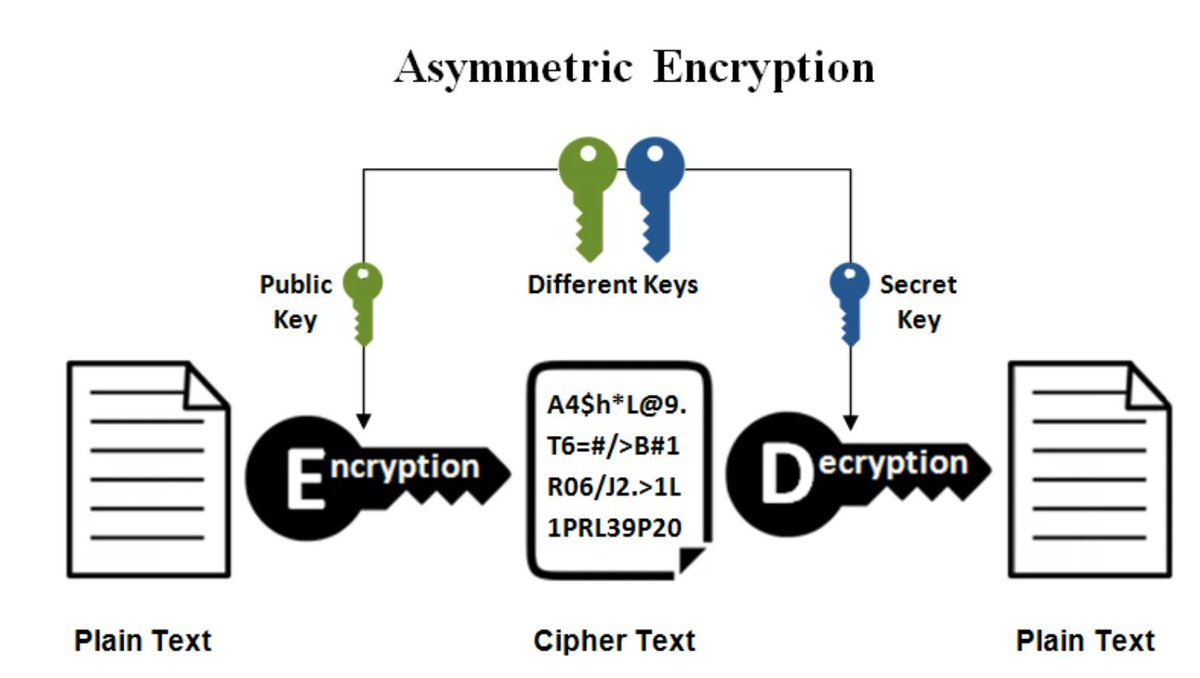
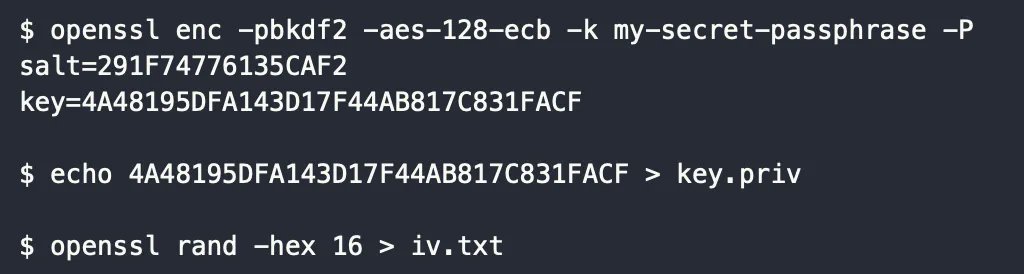
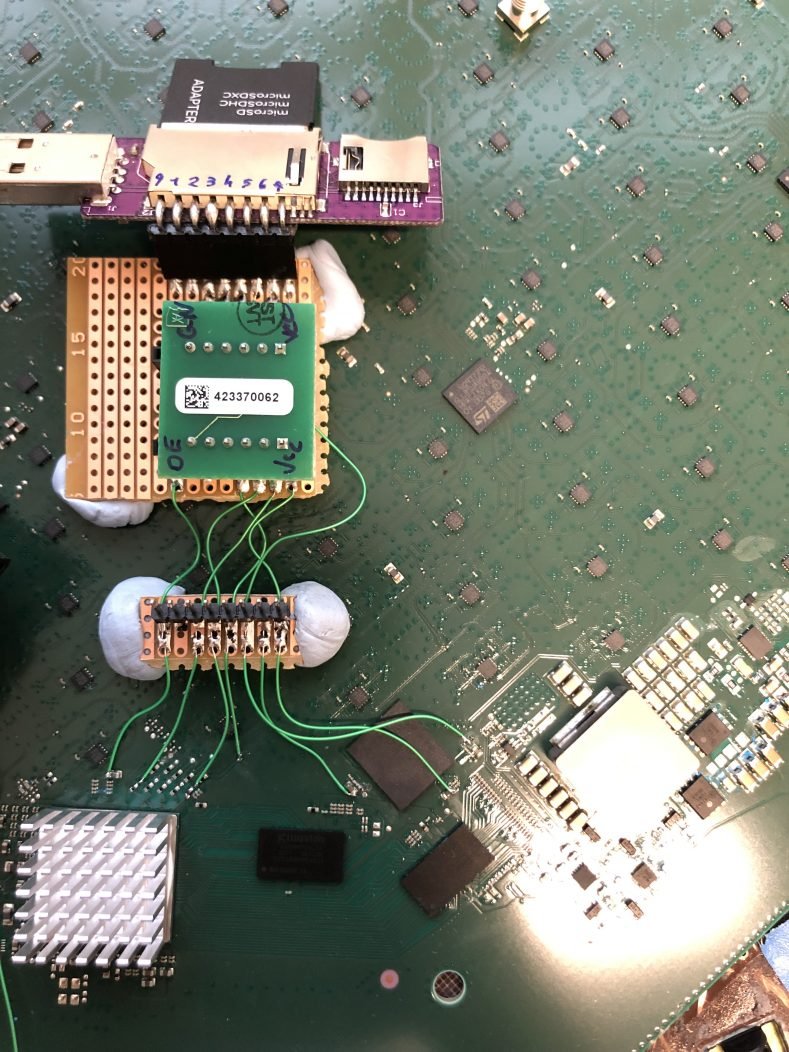
Nice series introducing cryptography concepts for beginners
(credits @sergioprado)
Part 1: https://t.co/2GoJH5Uqdp
Part 2: https://t.co/mhkaDWoQ5J
Part 3: https://t.co/HR5lsJThb9
#cryptography
10 weaponised XSS payloads to turn your alert(1) into a P1! 🔫
😱 JS files that can be loaded in XSS payloads to perform sensitive functions on popular CMS platforms within the victim's browser!
🪲 XSS bug > Account takeover?💥
#hacking#bugbounty
https://t.co/9jnkfg2xan