📎 Sources and on-chain records:
Unocoin | Historical wallet disclosure, 2023
https://t.co/L8E3DEsEq0
XRP | November 9 transfer of 39,167.149115 XRP
https://t.co/NquYAnn7zM
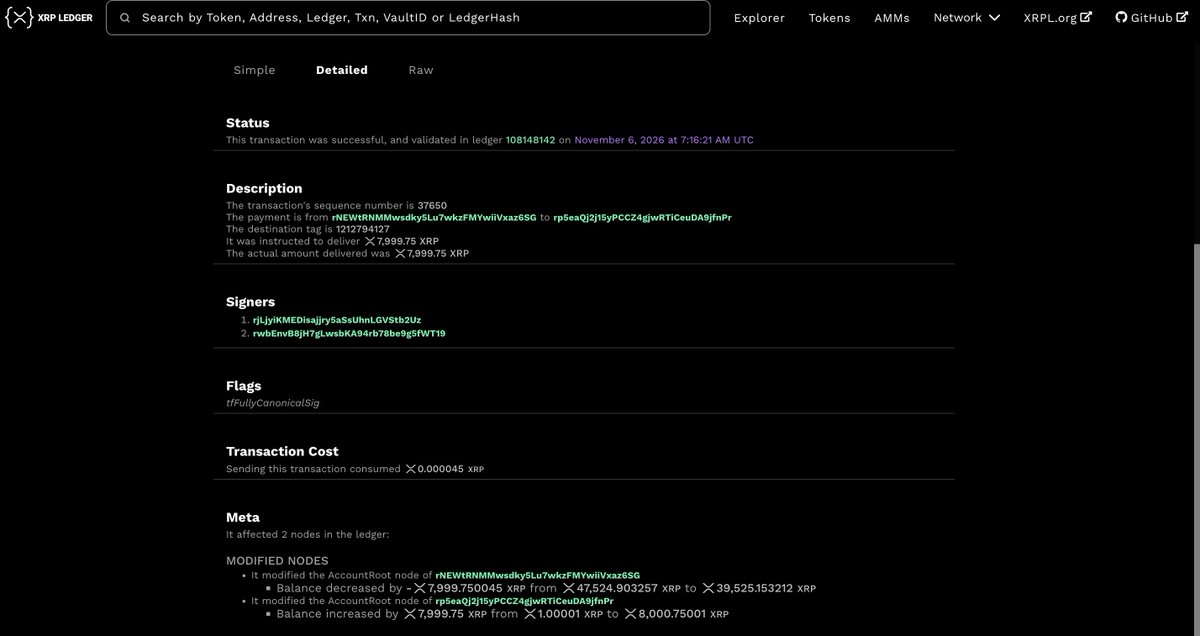
XRP | November 6 transaction used for the signer comparison
https://t.co/BksQfu8xoX
Ethereum | Transaction history of the wallet examined
https://t.co/kt7EnaK9ec
🔎 Long-established Indian crypto exchange @Unocoin suspended services following a security incident. Our review found that several cold-wallet addresses disclosed by the exchange in the past still held assets, alongside two sets of concentrated outgoing transfers that warrant further investigation.
In its November 12 update, Unocoin said it had identified outgoing transactions from an ETH address within its BitGo wallet infrastructure. It had not yet published the specific address, transactions, or a complete assessment of losses.
We checked the cold-wallet addresses Unocoin publicly disclosed in 2023. On November 13, four of those addresses respectively held:
• 991.10373 ETH
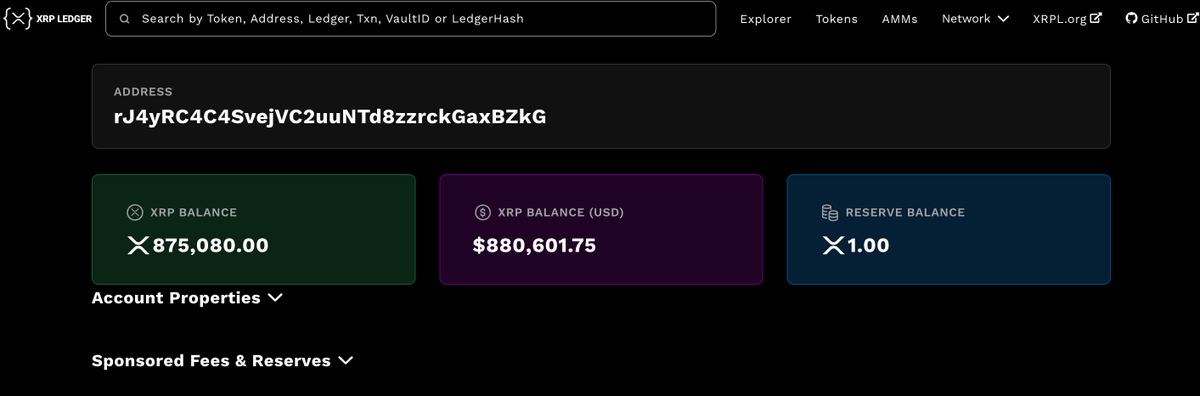
• 875,079.999924 XRP
• 1,250.0001 LTC
• 30.00001094 BCH
For the Ethereum address in that historical disclosure, balances of ETH, USDT, USDC, TUSD, FUN, and BAT were unchanged between the two snapshots taken on November 5 and November 13. The five tokens also showed no nonzero outgoing transfers from November 6 through the review cutoff.
Two BTC addresses in the same disclosure had zero balances, but their funds had already been transferred out in 2023. Those transfers cannot be counted as part of this incident.
These records do not support the claim that all publicly disclosed wallets had been emptied. The historical list does not cover all of the exchange’s current wallets, and these balances alone cannot establish the overall status of its assets or customer funds.
We also found that one of Unocoin’s XRP wallets transferred its entire spendable balance in a single transaction, while an Ethereum wallet with a historical funding connection to a disclosed cold-wallet address sent multiple assets to the same recipient.
In both cases, the signer combinations differed from those in the pre-incident transaction samples we examined.
#Unocoin #OnChainAnalysis #CryptoSecurity #AML #Arisk
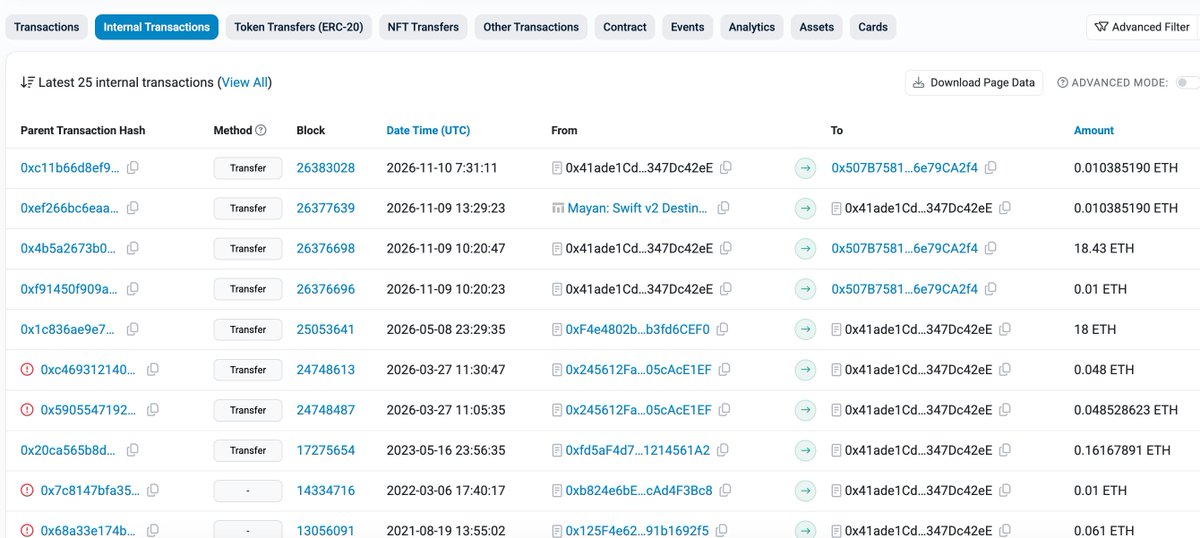
On Ethereum, 0x41ad…42eE sent ETH, USDT, and USDC to the same recipient between November 9 and November 10.
This multisig wallet drew our attention because, on June 7, 2022, it directly received 49,000 USDT from a cold-wallet address Unocoin later publicly disclosed. The concentrated outflows began on November 9, the same date the exchange reported detecting further unauthorized activity.
The historical funding connection and timing gave us leads to investigate. However, we have not confirmed that this wallet is the affected ETH address mentioned in Unocoin’s update, or that these outflows are connected to this security incident.
At 10:20:23 UTC on November 9, 0x41ad…42eE first sent 0.01 ETH, followed 24 seconds later by approximately 18.43272 ETH, and subsequently transferred USDT and USDC.
By the following day, it had sent the following amounts to 0x507B…A2f4:
• Approximately 18.45310 ETH
• 36,264.91506 USDT
• 6,727.75645 USDC
The authorization records for these transfers also warrant attention.
The wallet contract requires the address submitting a transaction to be an authorized signer and to supply a valid signature from a second, distinct authorized signer.
Compared with a November 6 outgoing transaction, the submitter for these concentrated outflows changed to 0x11b1…8D48F, while the other signer remained the same. Historical on-chain permission records confirm that 0x11b1…8D48F was already on the authorized signer list before these transfers.
The submitter also received 0.00547768 ETH just 48 seconds before its first operation, then began calling the wallet to transfer assets out.
Both the Ethereum and XRP records show a change in the combination of existing authorized signers. This is a shared feature of the two leads, but we have not established a direct funding link between them or confirmed whether they were initiated by the same operator. The amounts also cannot simply be added together as losses from this incident.
Valid signatures show that a transaction met the on-chain execution requirements. They do not, on their own, establish that it went through the exchange’s normal approval process.
#Unocoin #Ethereum #WalletSecurity #OnChainAnalysis
What makes this XRP transfer worth examining?
We reviewed Unocoin’s XRP wallet rNEW…az6SG and identified a November 9 transfer with two notable features: the amount transferred and the signer combination used.
1️⃣ The transfer left exactly the required account reserve.
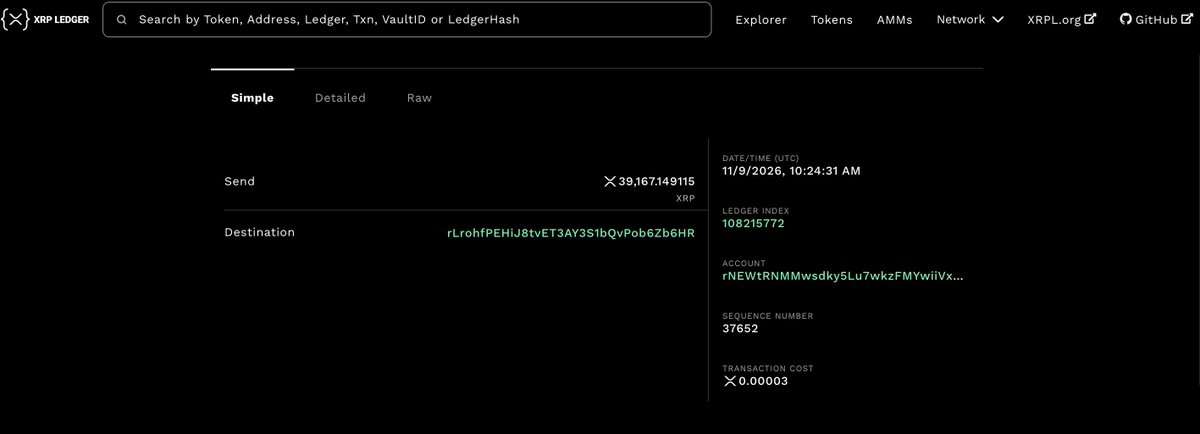
At 10:24:31 UTC on November 9, the wallet sent 39,167.149115 XRP to rLro…6HR, activating the receiving account.
Before the transfer, the source account held 39,169.149145 XRP. After the payment and transaction fee, exactly 2 XRP remained, matching the account’s reserve requirement at the time. The transaction therefore transferred its entire spendable XRP balance.
The recipient subsequently sent a total of 39,100 XRP in four payments to the same intermediary account.
2️⃣ A different combination of existing signers authorized the transaction.
The source account had a two-of-three multisignature configuration at the time.
We examined 200 pre-incident records covering September 4 through November 6. Among them, 82 outgoing transactions used the same signer pair. The November 9 transfer was signed by another existing signer together with one member of that previous pair.
Although this transaction used a different signer combination from the earlier sample, both participants were already on the authorized signer list, and the transaction met the existing multisignature requirements. The change in signer combination alone does not establish that multisignature controls were bypassed or that anyone was newly granted permissions.
The available on-chain records do not yet establish whether this was a routine transfer, an emergency transfer, or an unauthorized operation.
#Unocoin #XRP #OnChainAnalysis
📎 Relevant addresses and transaction records:
Attacker’s THORChain address:
thor10twjklsmm4e8wnl0e7f2rhtz7urv66yrjjmggk
Ethereum address used to fund the attacker and receive ETH:
0x911c3BF11dFc5497A53A7A04Ff7980532516f176
THORChain | Swap and cross-chain transaction records
https://t.co/8P9xrSkqrj
Ethereum | Pre-attack funding and ETH received after the attack
https://t.co/nQ8XbswwqD
Tron | USDT transfer history of the cross-chain recipient address
https://t.co/mulNUajrze
BSC | USDT transfer history of the cross-chain recipient address
https://t.co/D5HkBOMbLK
🔎 On November 10, Rujira Trade, a decentralized exchange on #THORChain , was exploited. @RujiraNetwork estimated losses in the BTC/USDC market at about $200,000.
Our analysis found that the attacker created liquidity positions with extreme parameter values, sold BTC for USDC at abnormal prices, then closed the positions and submitted separate transactions to buy back BTC. The attacker completed three such rounds in about 24.5 minutes.
After six successful transactions, the attacker’s address recorded a net increase of about 1.69965304 BTC and 71,092.20 USDC. Both assets here are Secured Assets: on-chain representations of the corresponding assets on THORChain.
After the attack, the attacker swapped the relevant holdings for ETH and sent the funds back to the Ethereum address that had provided the initial funding. We traced subsequent transfers from that Ethereum address to Tron and BSC, with USDT from both routes reaching Binance hot wallets.
#Rujira #AML #DeFiSecurity #Arisk
🔁 Before the attack, #Ethereum address 0x911c…6f176 sent about 13.59709 ETH across 11 transactions. The funds were swapped via #THORChain to fund the address that executed the attack.
On the evening of the attack, that address converted BTC, USDC and other holdings into ETH across 10 transactions, sending a total of about 108.08228 ETH back to 0x911c…6f176. This included assets gained through the attack, along with the original capital and other holdings.
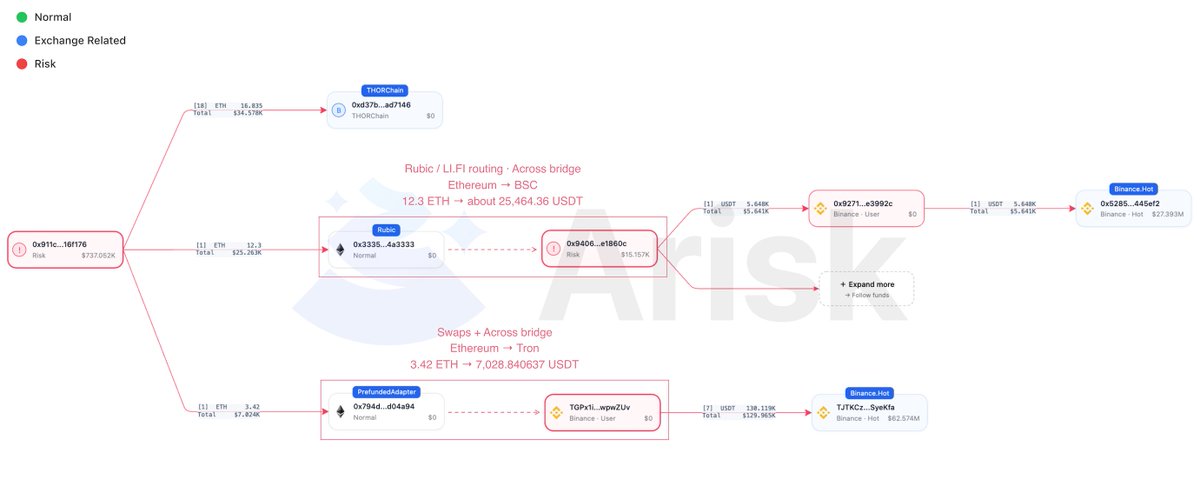
0x911c…6f176 also held other funds received earlier. On November 11, it moved part of its funds to Tron and BSC:
1️⃣ Ethereum → Tron → Binance
0x911c…6f176 converted 3.42 ETH into 7,028.840637 USDT through swaps and bridging via Across, sending the USDT to TGPx1…wpwZUv on Tron.
About 12 minutes later, TGPx1…wpwZUv sent the full amount to a Binance hot wallet.
2️⃣ Ethereum → BSC → Binance
0x911c…6f176 also swapped 12.3 ETH through Rubic and https://t.co/HWG1bEcGm0 routing and bridged the funds to BSC via Across. Address 0x9406…E1860C received about 25,464.36 USDT.
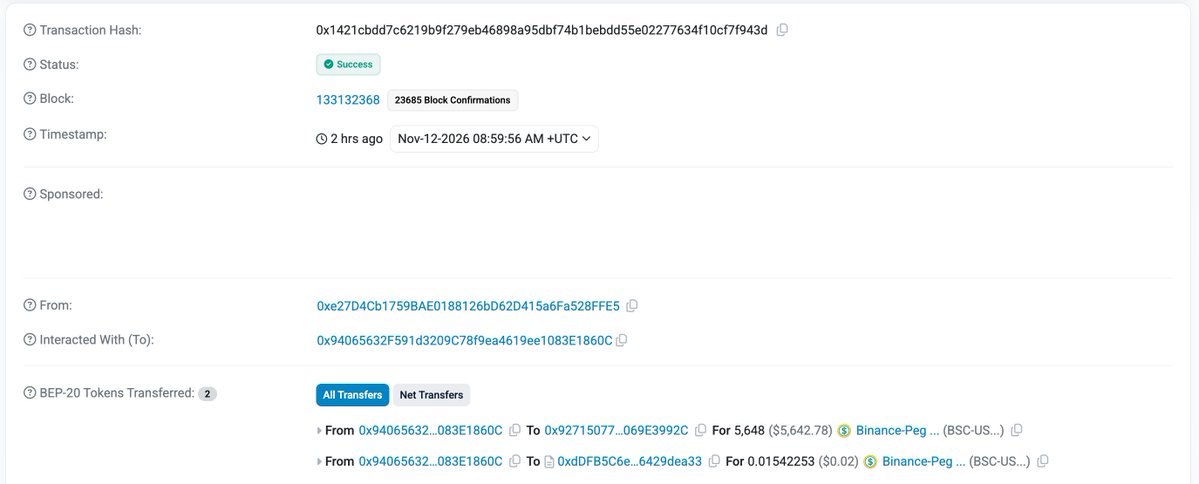
0x9406…E1860C already held other USDT. At 08:59 UTC on November 12, it sent 5,648 USDT to 0x9271…3992c, which forwarded the full amount to a Binance hot wallet about three minutes later.
At 10:40 UTC the same day, 0x9406…E1860C sent another 22,598.88 USDT to 0x9276…7a3e9.
USDT from both the Tron and BSC routes has reached Binance hot wallets, while a separate transfer on BSC went to another address. Further movements of these funds are worth tracking.
#Rujira #CrossChain #AssetTracing
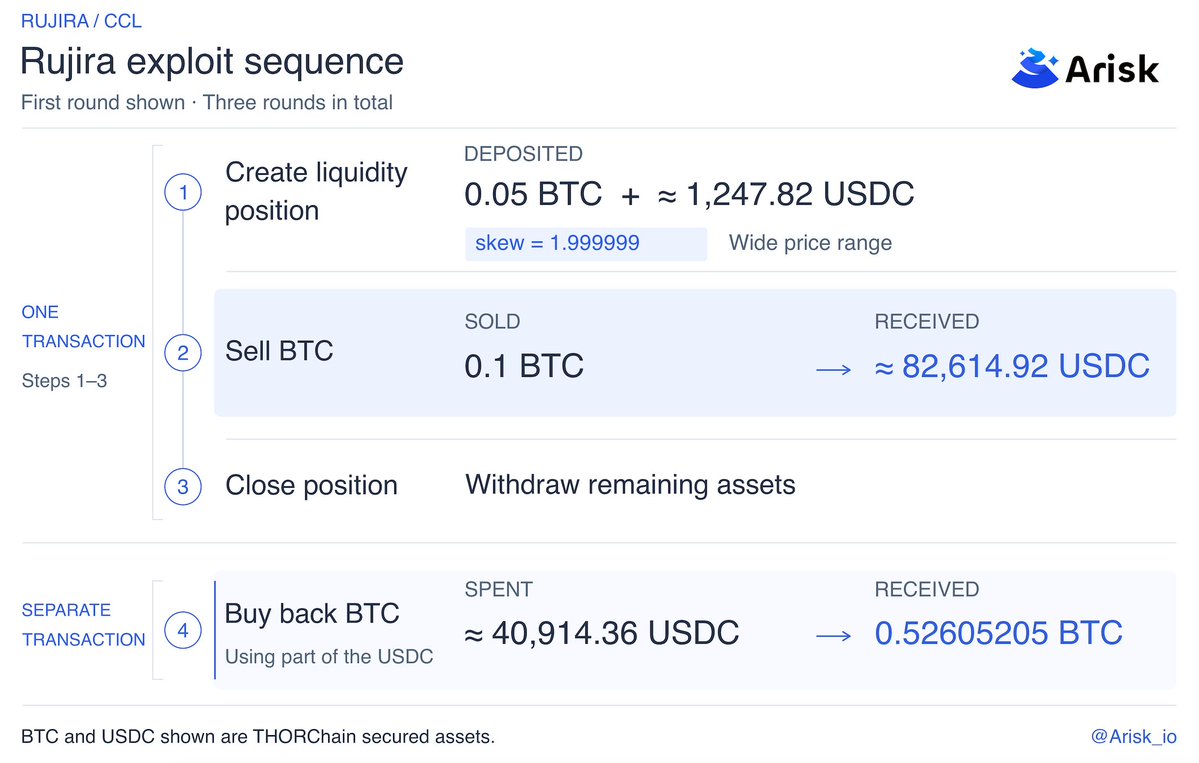
The attack involved CCL, or Custom Concentrated Liquidity. This market-making strategy lets liquidity providers set a trading price range and use the skew parameter to adjust how liquidity is distributed across that range.
The attacker set skew to 1.999999, close to the upper limit of 2, and selected an extremely wide price range. In the first round, the attacker:
1️⃣ Created a liquidity position with 0.05 BTC and about 1,247.82 USDC.
2️⃣ Sold 0.1 BTC, receiving about 82,614.92 USDC.
3️⃣ Closed the position and withdrew the remaining assets.
All three actions took place in the same transaction. The attacker then submitted a separate transaction to buy back 0.52605205 BTC with about 40,914.36 USDC, before moving on to the next round.
These abnormal trades drew USDC from existing liquidity positions. After three rounds, the attacker’s address held more BTC and USDC than before, while existing liquidity providers incurred losses.
The attack exploited an issue with CCL’s skew calculations, causing existing BTC/USDC liquidity positions to become imbalanced.
#Rujira #THORChain #SmartContractSecurity
@arcus_xyz Sorry to hear about the losses. We traced about 100 ETH in stolen funds to a Binance hot wallet on Nov 12. Another 50 ETH went to a wallet that previously swapped ETH for BTC via Relay.
Fund flows and analysis:
https://t.co/VdoikidMGU
🔎 About 100 ETH stolen from decentralized exchange @arcus_xyz has reached #Binance.
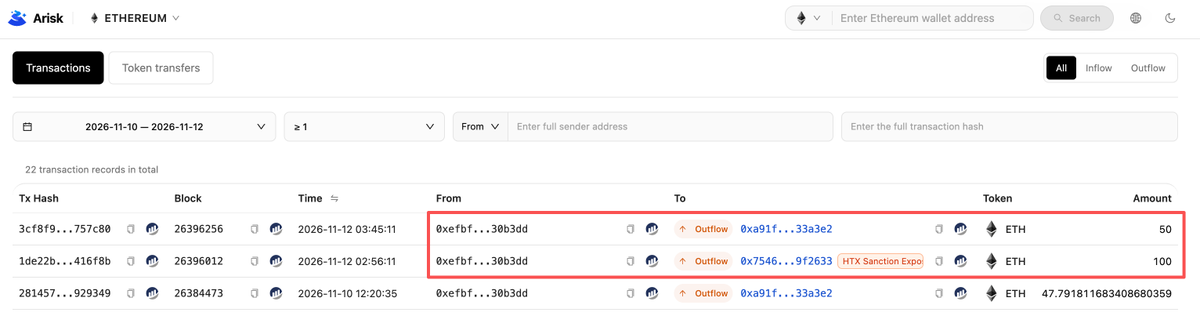
On November 12, the attacker’s address 0xefb…0b3dd transferred out a total of 150 ETH. Of this, 100 ETH went to 0x7546…9f2633, which forwarded about 100 ETH to a Binance hot wallet four minutes later.
Another 50 ETH went to 0xa91f…33a3e2. This wallet previously used Relay to swap ETH for BTC.
The newly received 50 ETH remains at 0xa91f…33a3e2, while 0xefb…0b3dd still holds about 325.06128 ETH.
#Arcus #Ethereum #AssetTracing #Arisk #AML
🔎 About 100 ETH stolen from decentralized exchange @arcus_xyz has reached #Binance.
On November 12, the attacker’s address 0xefb…0b3dd transferred out a total of 150 ETH. Of this, 100 ETH went to 0x7546…9f2633, which forwarded about 100 ETH to a Binance hot wallet four minutes later.
Another 50 ETH went to 0xa91f…33a3e2. This wallet previously used Relay to swap ETH for BTC.
The newly received 50 ETH remains at 0xa91f…33a3e2, while 0xefb…0b3dd still holds about 325.06128 ETH.
#Arcus #Ethereum #AssetTracing #Arisk #AML
🔎 On November 10 (UTC), decentralized exchange @arcus_xyz was hacked. The attacker exploited an accounting bug in transfers between subaccounts belonging to the same user, inflated their account balance, and withdrew 2,234,391 USDG.
The bridge’s on-chain withdrawal limit blocked another roughly $3 million in withdrawal requests. Those funds were not transferred out, and the requests were later canceled. Arcus Labs said it had covered the shortfall with its own funds and that other users’ balances, positions, and orders were unaffected.
The main recipient address, 0xefb…0b3dd, then combined the withdrawn USDG with a small existing balance and swapped the funds for ETH across chains via Relay.
Two swaps were not completed, resulting in refunds of about 560,000 USDG and about 58,500 USDG to the same main address on Robinhood Chain. The refunded funds were then used for further swaps.
In total, the same address on Ethereum received about 1,052.21 ETH through seven successful swaps.
Further tracing showed that some of the ETH was swapped for about 1,008,900 DAI and sent to a new recipient address. Other funds were swapped for about 2.83 BTC via THORChain and Relay, with both routes delivering BTC to the same Bitcoin address.
#Arcus #Ethereum #Bitcoin #AssetTracing #AML
📎 On-chain records:
Lookalike address:
0x8B1Fdda74283D4d86E4a4F213eD5B6cbc2B73200
It sent ETH to:
0x46dcD177508fA5c16051B274e39e8f5A382be7A6
The victim sent 50,019.557647 USDC to the lookalike address:
https://t.co/MQIaC6E3fg
Onward ETH transfer:
https://t.co/6YDiMAmEKm
🔎 Another address poisoning case: 50,019.557647 USDC mistakenly sent to a lookalike address.
On November 10, the victim’s #Ethereum address, 0x0058…bed855, made the transfer. Our tracing found that the lookalike address had been repeatedly sending small amounts of USDC to the same victim since October 5.
The attacker’s address shared the same opening and ending characters as the victim’s intended recipient address:
Intended recipient address:
0x8B1f5FF294702Da5B6f04cB1F964dA3446b73200
Lookalike recipient address:
0x8B1Fdda74283D4d86E4a4F213eD5B6cbc2B73200
Ignoring capitalization, both addresses begin with 0x8b1f and end with b73200. Checking only those characters is not enough to tell them apart.
Between October 5 and November 9, the lookalike address sent the victim 16 transfers of just 0.0001 USDC each. The attacker used these small transfers to make the lookalike address appear repeatedly in the victim’s transaction history, attempting to trick the victim into using it for a later payment.
After the mistaken transfer, the address sent the victim another five transfers of the same amount, bringing the total to 21.
#AddressPoisoning #USDC #FakeAddress #Arisk
Before the mistaken transfer, a legitimate payment was followed by a small poisoning transfer just 48 seconds later.
At 19:35:23 UTC on November 9, the victim sent 10,004.772276 USDC to the intended recipient address. At 19:36:11 UTC, the lookalike address sent the victim another 0.0001 USDC.
At 15:54:59 UTC on November 10, the victim sent 50,019.557647 USDC to the lookalike address.
Just 96 seconds later, at 15:56:35 UTC, the lookalike address swapped the entire USDC amount through Uniswap, receiving about 24.76115 ETH.
At 13:24:35 UTC on November 11, the lookalike address combined the swap proceeds with its other ETH balance and sent about 24.76333 ETH to a new address, 0x46dc…2be7a6.
0x46dc…2be7a6 still holds about 24.76333 ETH.
Before sending funds, verify the full recipient address, especially the characters in the middle. Avoid copying addresses directly from transaction history.
#Ethereum #USDC #AssetTracing
📎 Relevant addresses and transaction records:
Across | Official approval revocation guide
https://t.co/F8J0TvM0QM
Chainflip | ETH → SOL swap record
https://t.co/Jd28GMmY8x
THORChain | ETH → BTC swap records
https://t.co/3MiiX9wp4L
Relay | ETH on Ethereum → USDC on Arbitrum swap records
https://t.co/O0VoxsHbRb
Hyperliquid | XMR1 purchase and transfer records
https://t.co/TAHnHq5btw
https://t.co/OIPWWud9lR
https://t.co/IeuMuDrsbt
🔎 On November 10, attackers hijacked the official website domain of cross-chain bridge @AcrossProtocol and used a phishing page to steal victims' assets.
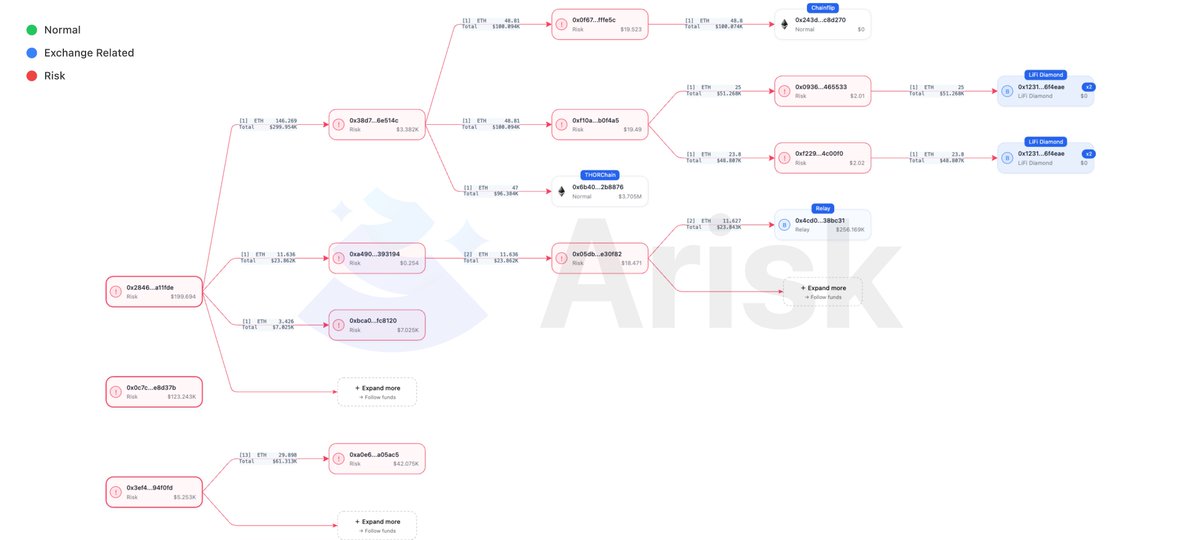
Our tracing found that some stolen assets were transferred directly to wallets on Ethereum, while other funds reached Ethereum through cross-chain swaps. 0x284…11fde received funds from multiple sources and later transferred them out in batches. Some were swapped for BTC and SOL, while other funds were bridged to Arbitrum and transferred into Hyperliquid to buy XMR1.
Across said the attackers gained control of the domain through a social engineering attack targeting domain registrar Namecheap. On November 11, the team announced that services had been restored and pledged to compensate victims.
We analyzed the transactions and found that assets were taken through signed token approvals, permissions to manage liquidity positions, and direct transfers.
In one aEthWETH transfer, the attacker used a permit signed by the victim to send the tokens to two addresses within the same transaction.
Another transaction involved a Uniswap v4 liquidity position. After the victim granted permission to manage the position, the authorized address withdrew USDC and LIT, then split the assets between two addresses.
Details of the transfers and swap routes below ⬇️
#Across #Phishing #Ethereum #AssetTracing
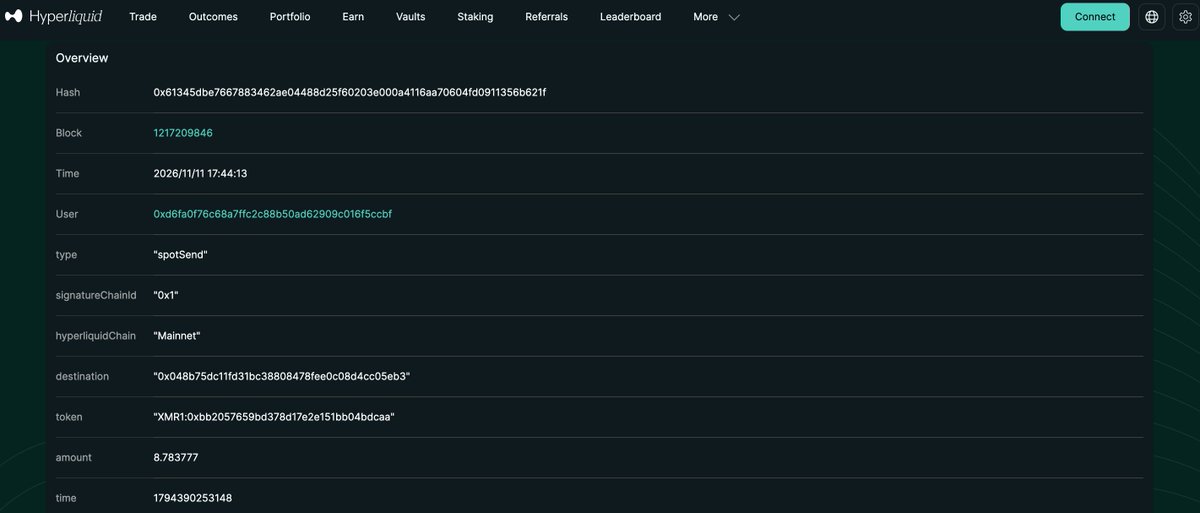
Other funds were bridged to Arbitrum via Relay and then transferred into Hyperliquid to buy XMR1.
On November 10, 0x284…11fde sent 11.63613796 ETH to 0xa49…93194. On November 11, 0xa49…93194 sent a total of 11.636 ETH to Ethereum address 0x05d…30f82 in two transactions.
0x05d…30f82 then used Relay to bridge some of that ETH from Ethereum to Arbitrum and swap it for USDC. The two swaps returned 5,100.352811 USDC and 18,676.398314 USDC, totaling 23,776.751125 USDC.
Both amounts were received by Arbitrum address 0x684…e26b6. The USDC was then transferred in three transactions into the Hyperliquid account corresponding to the same address and used to buy XMR1.
Within Hyperliquid, 0x684…e26b6 transferred the purchased XMR1 out in batches. The intermediate accounts that received the tokens then forwarded their respective amounts to the same account, 0x048…5eb3, totaling 41.360810 XMR1.
0x048…5eb3 also received XMR1 from other accounts.
We will continue to track where these funds move.
#Across #Hyperliquid #AssetTracing #Arisk
🔁 On November 10, 0x284…11fde sent 146.26868582 ETH to Ethereum address 0x38d…e514c.
The funds were then moved through intermediate addresses along three main routes:
1️⃣ Via Arbitrum to Hyperliquid to buy XMR1
A total of 48.8 ETH was bridged from Ethereum to Arbitrum and swapped for USDC in two transactions, routed through https://t.co/HWG1bEcGm0 using LayerSwap.
Arbitrum address 0x093…65533 received 51,378.430969 USDC from the 25 ETH swap, while Arbitrum address 0xf22…c00f0 received 48,985.187209 USDC from the 23.8 ETH swap.
Each address then transferred the USDC into its corresponding Hyperliquid account to buy XMR1.
2️⃣ Via Chainflip, swapping ETH for SOL
Another 48.8 ETH was swapped from Ethereum to Solana via Chainflip. Solana address G47n6…a4uSa received 1,197.033564583 SOL.
3️⃣ Via THORChain, swapping ETH for BTC
A further 47.00020186 ETH was swapped for 1.30506375 BTC via THORChain. The BTC was received by Bitcoin address 3EQ9R…GfAQs.
#Across #CrossChain #AssetTracing
@CoinEdition We traced the stolen funds:
about 1,008,900 DAI from token swaps was transferred to a new address. Five swaps via THORChain and Relay sent about 2.83 BTC in total to the same Bitcoin address.
Routes and full recipient addresses:
https://t.co/1rkRLk6jVb
🔎 On November 10 (UTC), decentralized exchange @arcus_xyz was hacked. The attacker exploited an accounting bug in transfers between subaccounts belonging to the same user, inflated their account balance, and withdrew 2,234,391 USDG.
The bridge’s on-chain withdrawal limit blocked another roughly $3 million in withdrawal requests. Those funds were not transferred out, and the requests were later canceled. Arcus Labs said it had covered the shortfall with its own funds and that other users’ balances, positions, and orders were unaffected.
The main recipient address, 0xefb…0b3dd, then combined the withdrawn USDG with a small existing balance and swapped the funds for ETH across chains via Relay.
Two swaps were not completed, resulting in refunds of about 560,000 USDG and about 58,500 USDG to the same main address on Robinhood Chain. The refunded funds were then used for further swaps.
In total, the same address on Ethereum received about 1,052.21 ETH through seven successful swaps.
Further tracing showed that some of the ETH was swapped for about 1,008,900 DAI and sent to a new recipient address. Other funds were swapped for about 2.83 BTC via THORChain and Relay, with both routes delivering BTC to the same Bitcoin address.
#Arcus #Ethereum #Bitcoin #AssetTracing #AML
@OnchainLens We checked the records: both subaccount balances flipped signs after an internal transfer. A 1 USDG withdrawal debit then turned Subaccount 1’s negative balance into a huge positive balance, consistent with integer wraparound.
Analysis and fund flows:
https://t.co/1rkRLk6jVb
🔎 On November 10 (UTC), decentralized exchange @arcus_xyz was hacked. The attacker exploited an accounting bug in transfers between subaccounts belonging to the same user, inflated their account balance, and withdrew 2,234,391 USDG.
The bridge’s on-chain withdrawal limit blocked another roughly $3 million in withdrawal requests. Those funds were not transferred out, and the requests were later canceled. Arcus Labs said it had covered the shortfall with its own funds and that other users’ balances, positions, and orders were unaffected.
The main recipient address, 0xefb…0b3dd, then combined the withdrawn USDG with a small existing balance and swapped the funds for ETH across chains via Relay.
Two swaps were not completed, resulting in refunds of about 560,000 USDG and about 58,500 USDG to the same main address on Robinhood Chain. The refunded funds were then used for further swaps.
In total, the same address on Ethereum received about 1,052.21 ETH through seven successful swaps.
Further tracing showed that some of the ETH was swapped for about 1,008,900 DAI and sent to a new recipient address. Other funds were swapped for about 2.83 BTC via THORChain and Relay, with both routes delivering BTC to the same Bitcoin address.
#Arcus #Ethereum #Bitcoin #AssetTracing #AML