@yeswehack@Ch0pin Too bad it's named like those two pre-existing security tools: https://t.co/xwbLJ54O5p (login network cracker) and https://t.co/BSETRTxWUK (interactive disassembler) and thousand of other non-infosec projects.
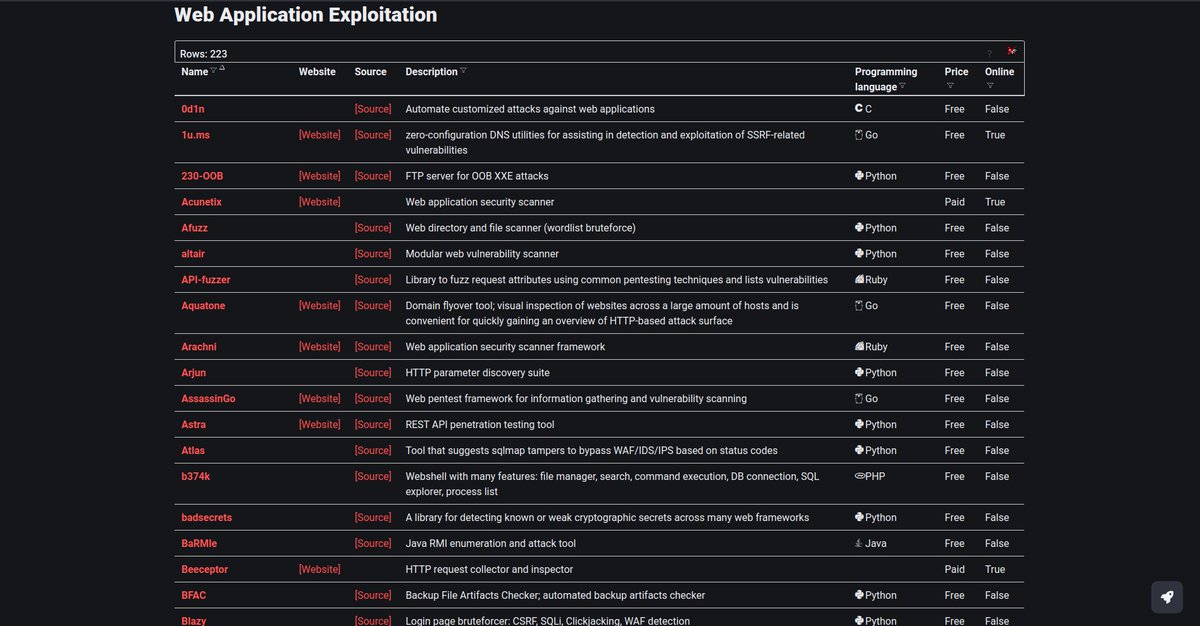
Rawsec Cybersecurity Inventory https://t.co/P9NJ6fsQzN exists since 2016, is open-source and has 200 times more tools.
Other similar projects were created recently like https://t.co/nUi12GubIn and https://t.co/DmSFfHMaox.
This awesome 'FFuf Advanced Tricks' article by @noraj_rawsec needs a shoutout. I created my own FFuf script based on his tricks, and here is the result. #BugBounty
https://t.co/5l4RMlmhV5
Tool / ressource of the day
name: FEDERACY
website: https://t.co/DgAoBQ7rHN
description: Crowdsourced pentest & bug bounty platform
price: Free
Find out more on https://t.co/fKHtB5KoQS
haiti (Hash type identifier tool) v1.4.1 released:
🍾 Reached 500 hash types supported
📈 17 new hash types
🥇 added new samples
☑️ many enhancements (add JtR or HC ref/id, better description, fixes)
https://t.co/h31wqYT9yC
A thread🧵
💸Secrets of automation-kings in bug bounty💸
Finding 1day (or 1month) web exploits that haven't made their into scanners yet can make you big money.
Read more to understand where and how to get an edge in this area!
🚨Retweet, follow, & like for more! 🚨
1/x