RBI didn't issue one cyber framework on 31 July 2026. It issued seven.
One set of Directions per entity class — commercial banks, small finance banks, payments banks, urban co-operative banks, all-India financial institutions, NBFCs and credit information companies. Each has its own reference number, and its own paragraph numbers.
Pick your entity class and this names the Directions that bind you, with a link to the RBI's own notification:
https://t.co/BgmLPT10Tc
#RBI #CyberSecurity #BFSI https://t.co/kIIrJdJnVJ
Your board cyber pack, from one prompt.
BitScoreCoWork is our open-source Claude plugin that turns your Bitsight data into the documents security teams actually have to file.
Ask for a board pack and you get a slide deck and a one-page executive brief, built from your own ratings.
It has 16 skills. Four that CISOs and boards ask for most:
— Vendor due diligence: a go / no-go before you sign, with the contract clauses to negotiate
— Incident notifications: drafted for CERT-In's six-hour clock, plus RBI, SEBI, IRDAI, IFSCA and DPDP
— Cyber exposure in rupees: a range, with every assumption shown
— Board crisis simulation: a tabletop exercise built from your own attack surface
It works inside Claude, runs on your Bitsight data and is MIT licensed.
#CISO #AI #ThirdPartyRisk
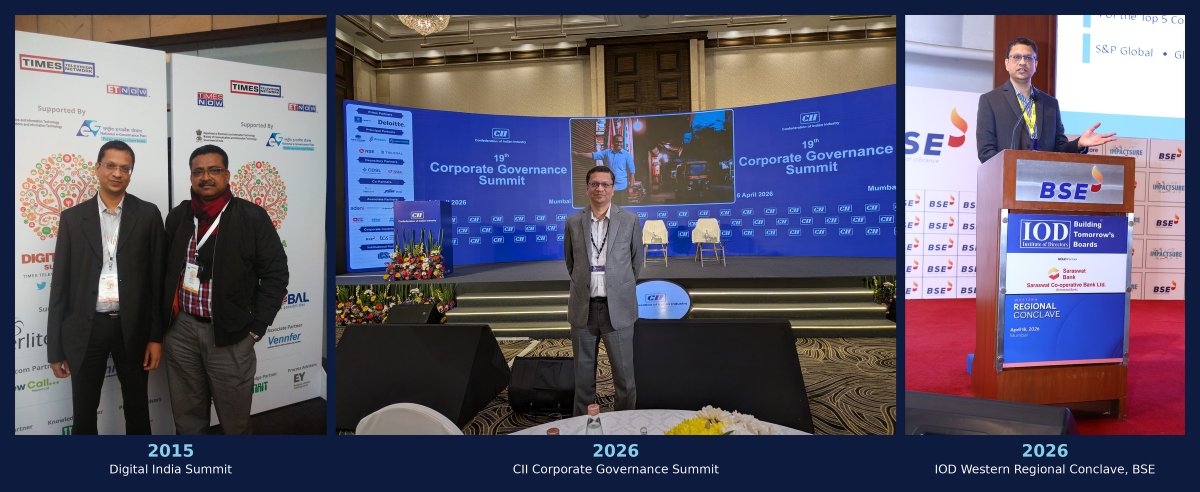
Eleven years. One continuous thread.
📍 4 March 2015 — Digital India Summit, New Delhi: An observer, trying to understand where India's digital future was headed.
📍 6 April 2026 — @Confederation of Indian Industry 19th Corporate Governance Summit, Mumbai: Engaging with India Inc's boardrooms on the next frontier of governance — cyber risk.
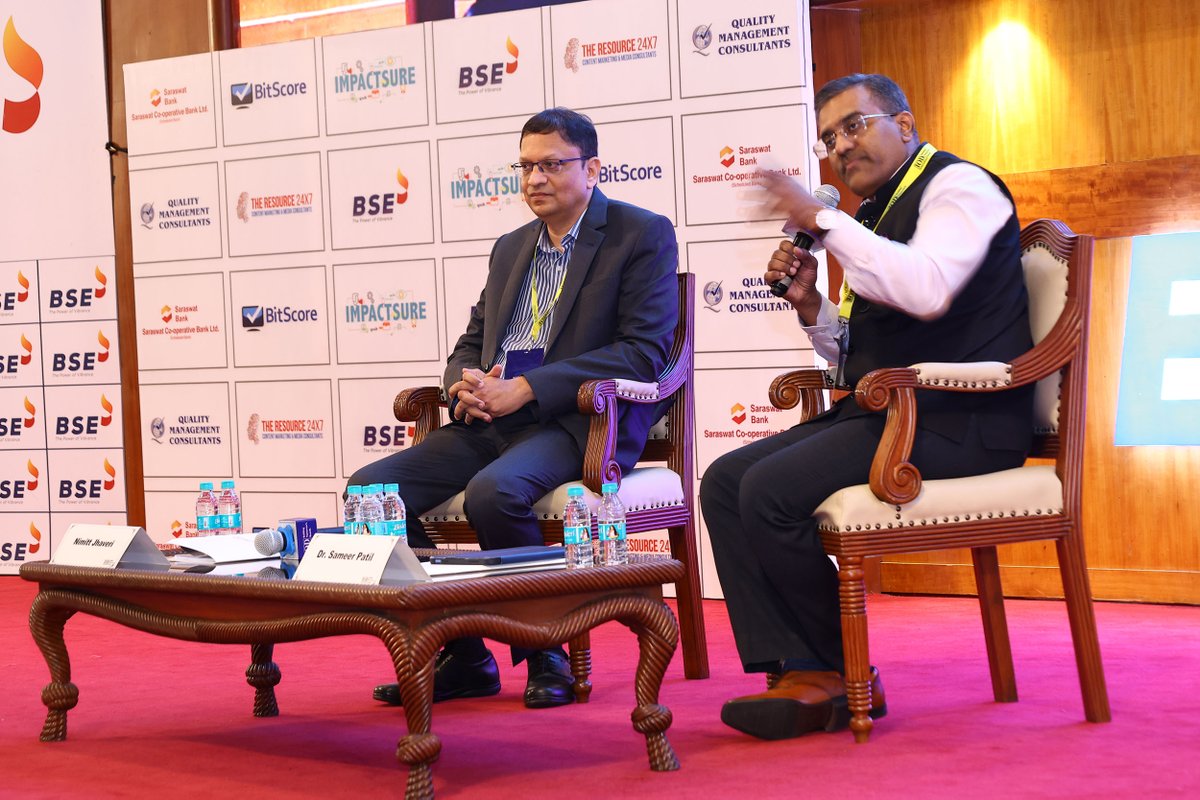
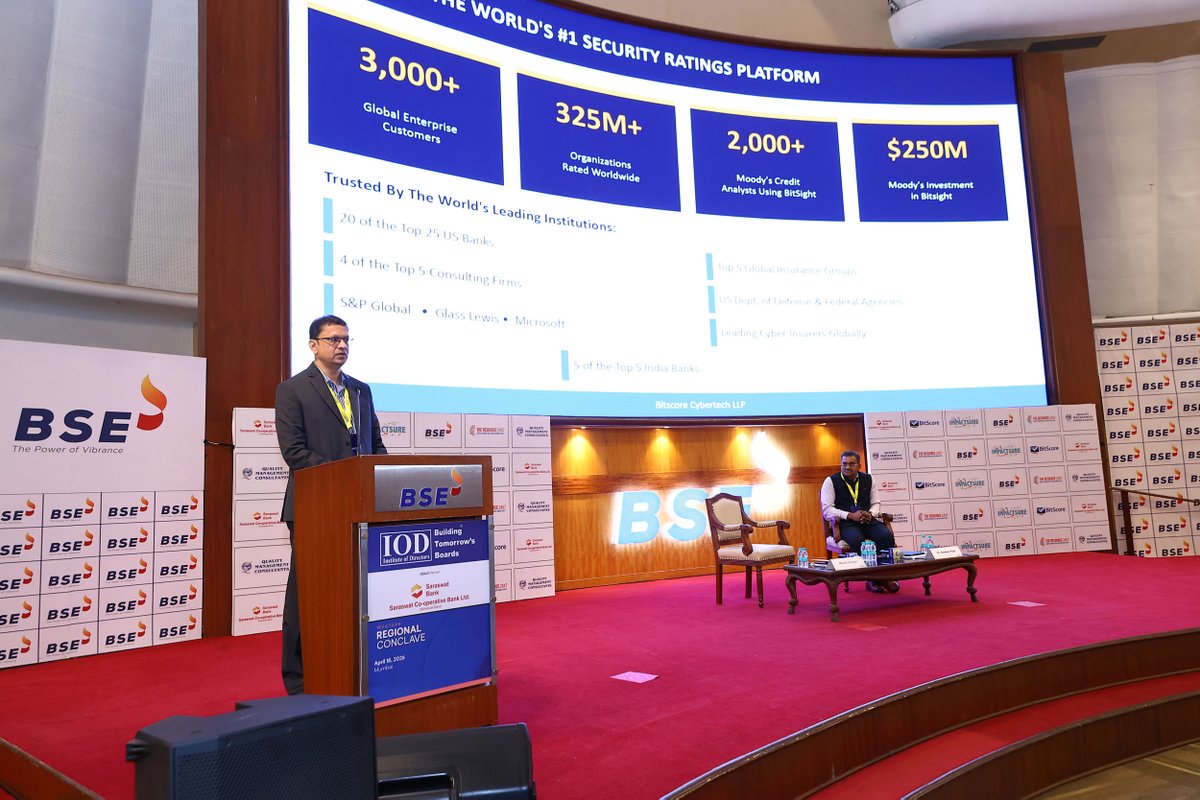
📍 18 April 2026 — @Institute of Directors (IOD), India in MUMBAI , BSE Mumbai: Representing Bitscore Cybertech as Official CyberSecurity Rating Partner, addressing directors on why cybersecurity ratings belong on every board agenda.
Somewhere between these frames, a thesis took shape: India's BFSI and critical infrastructure sectors need a transparent, objective, continuous measure of cyber risk — the cybersecurity equivalent of a CIBIL score. That thesis became Bitscore and the conversations we are now privileged to lead with regulators, CISOs, and boards.
Grateful to everyone who has been part of this journey — and looking forward to what the next chapter brings.
What a day at BSE Mumbai.
BitScore on stage at the IOD Western Regional Conclave 2026, presenting on cyber resilience and cybersecurity risk ratings to a room full of India's board of directors and CXOs. When governance leaders start treating cyber risk as a boardroom priority, you know the conversation in India has evolved.
Thank you @Institute of Directors (IOD), India in MUMBAI @Institute of Directors (IOD), India
#IODConclave2026 #cybersecurityratings #cybersecurity #cyberrisk
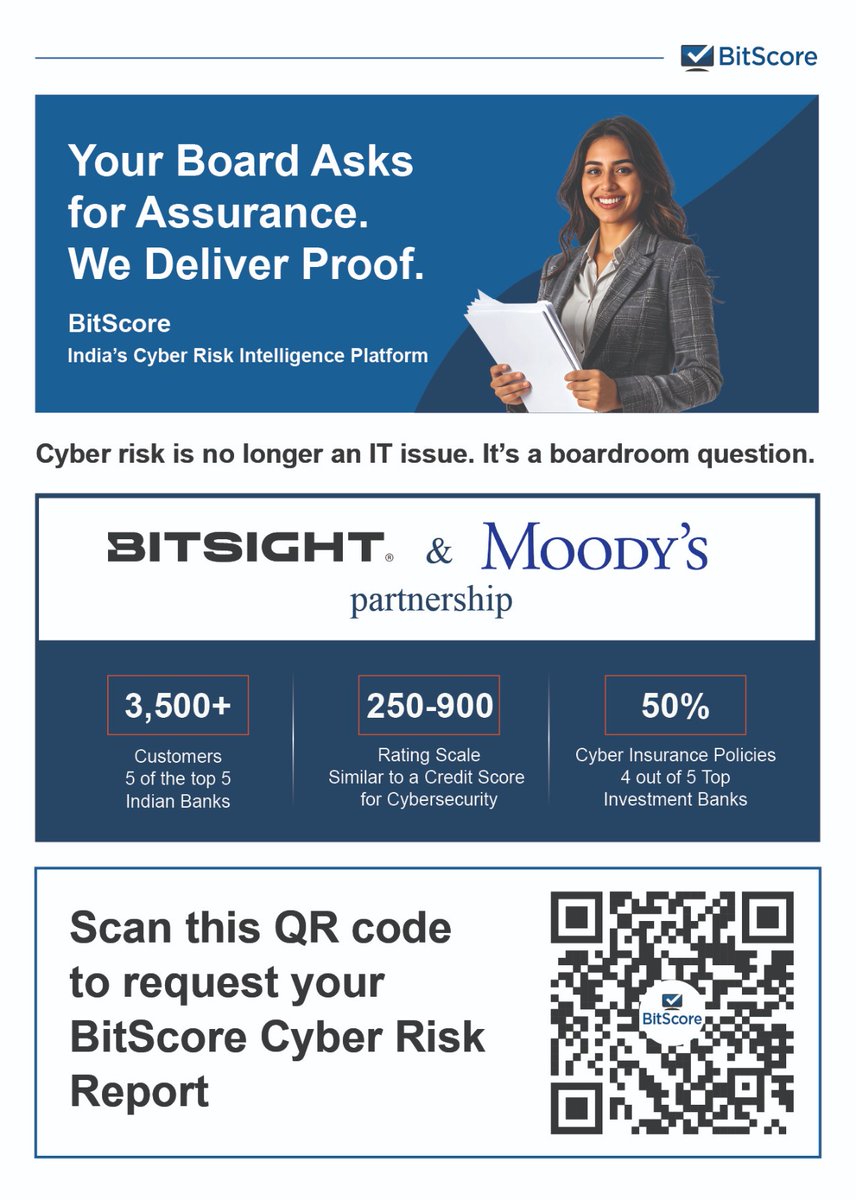
Cyber risk is no longer invisible, but is your board seeing it clearly?
BitScore transforms complex security signals into simple, board-ready insights.
Watch the full video to learn more.
And make sure you stay till the end for a surprise.
#cybersecurityratings#cybersecurity #cyberrisk
🇮🇳 A message every Indian Board Member should read today.
At SEBI's 38th Foundation Day, Hon'ble FM Nirmala Sitharaman didn't mince words:
"A single successful cyberattack on a major exchange, depository, clearing corporation, or large broker could disrupt markets at national scale, erase wealth, and shape public confidence in ways that take years to reveal."
She also said the quiet part out loud — regulation must move from reactive to anticipatory, and AI is now actively being used by attackers to find vulnerabilities at machine speed.
Cyber is no longer an IT line item in the CTO/CISO update. It sits where credit risk, audit, and fiduciary duty already sit — on the Board agenda.
Two questions worth asking at the next Board meeting:
1️⃣ Do we have a cyber rating — or just a cyber report?
A report tells you what was done. A rating tells you where you stand versus peers.
2️⃣ Would our cyber posture survive the FM's test — disruption, wealth erosion, loss of public confidence? If the answer needs a slide deck to explain, the answer is no.
Cyber risk now needs the discipline credit risk already has — measurable, benchmarked, trended quarterly.
How is cyber risk showing up on your Board agenda in FY26-27? 👇
#cybersecurityratings #cybersecurity #cyberrisk #BoardGovernance #IndependentDirectors #FiduciaryDuty
Is your Board ready for the governance challenges of 2026?
In an era defined by rapid AI disruption, evolving ESG mandates, and rising stakeholder expectations, the role of a director has shifted from simple oversight to active stewardship.
I am pleased to invite you to our upcoming edition of the Board Stewardship Monthly Webinar Series: "Stewardship in the Boardroom."
📅 Date: Friday, 8 May, 2026 Time: 4:00 PM - 6:00 PM IST
Panel Discussion 1: "Cyber(IN)Security for Boardrooms"
Panel Discussion 2: "Significance & Importance of the Minutes of Board and Committee Meetings"
🔗 Register here: https://t.co/VMPcB5SNdV
Whether you are an Independent Director, a CXO, or a governance professional, this session is designed to provide you with actionable frameworks to elevate your boardroom impact.
Join us as we catalyze a movement toward more purposeful, value-driven leadership.
See you there!
Thank you, Board Stewardship!
It was a privilege for Bitscore Cybertech LLP to be part of the Boardroom Insights Monthly Live Webinar on 8 May 2025, where we joined an insightful conversation on "Cyber(IN)Security for Boardrooms."
Our sincere thanks to the hosts — Shri Vikesh Wallia (Managing Director & Editor, Board Stewardship), Shri Emmanuel David for his thought-provoking inaugural address, and Shri Ashok D Murthy for the gracious vote of thanks — for curating such a timely and important discussion.
A special thank you to our esteemed co-panelists, Smt. Radhika Chennakeshavula (CISO, Silicon Labs) and Shri Dr. Rajiv Yadav (Board Strategy & Governance Advisor), for the rich exchange of perspectives. We also extend our appreciation to the panelists of the second session — Shri Sudhakar Saraswatula, Shri A.G.S Manikantha (Infosys), and Shri K Randhir Singh (Dr. Reddy's Laboratories) — for an equally compelling discussion on the significance of Board minutes.
Representing Bitscore, our Co-Founder & Managing Partner Shri Nimitt Jhaveri emphasized a critical shift Indian boardrooms must reckon with:
"AI has changed the game by collapsing the amount of time, skills and cost required to launch or mount a cyberattack."
"Cybersecurity can no longer sit within IT operations alone — it is a Board-level fiduciary responsibility. Indian boards need to build cyber resilience as a leadership capability, not just a technical control."
Grateful to Board Stewardship for the platform, and we look forward to continuing this conversation on advancing cyber governance in Indian boardrooms.
https://t.co/kxiir3T6zg
#cybersecurityratings #cybersecurity #cyberrisk
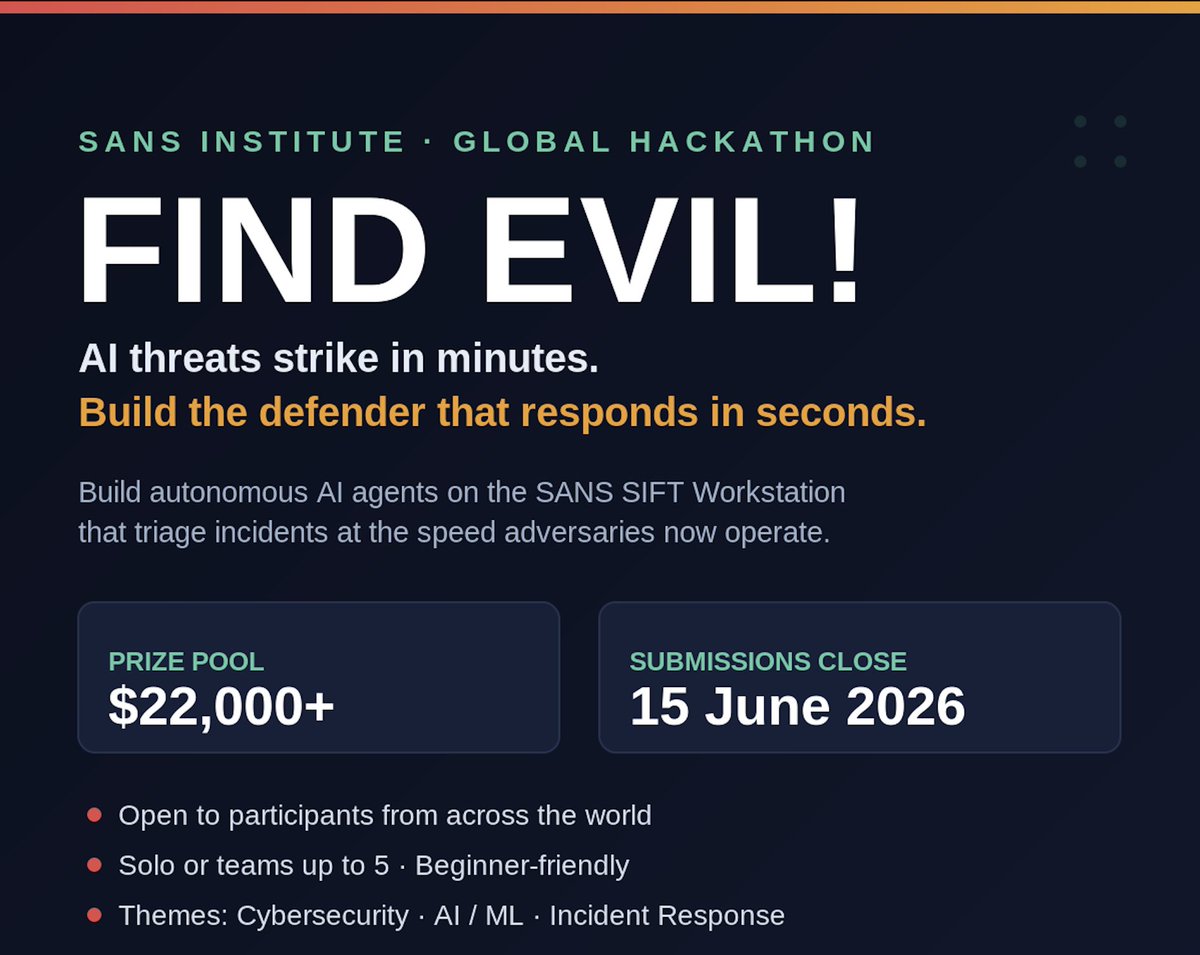
I am pleased to announce that I will judge the Find Evil! Hackathon sponsored by SANS Institute.
I look forward to seeing the entries from across the globe from over 3,700 registrants, including full-stack developers, data scientists, cybersecurity experts, and those new to AI or experienced.
The hackathon is a tremendous opportunity to learn, start using AI and grow in your skills.
It's not too late to join the hackathon, and get your submission in by June 15! No experience necessary and learners welcome.
Join the Hackathon: https://t.co/FvEz4DGTr3
AI attackers now go from first access to full domain control in under 8 minutes. The fastest human responder is still opening their toolkit.
That gap is the most dangerous problem in cybersecurity right now — and I'm proud to be a Judge for FIND EVIL!, the global SANS Institute hackathon built to close it.
The challenge from Rob T. Lee is simple to state and hard to solve: build autonomous AI agents on the SANS SIFT Workstation that can triage, correlate and report at the speed adversaries now operate. Teach an agent to think like a senior analyst — to sequence its approach, notice when something doesn't add up, and self-correct when it's wrong.
What makes me genuinely excited is who this is for. You don't need to be an incident response expert. The SIFT Workstation handles the domain tooling. Whether you're a security professional, an AI/ML engineer, a student, or an open-source contributor, there's a seat at this table.
A few things worth knowing:
🌍 Open to participants from across the world
💰 $22,000+ in prizes
🗓️ Submissions close 15 June 2026
🛡️ Themes: Cybersecurity · AI/ML · Beginner-friendly
🤝 Solo or teams up to 5
This is a rare chance to put the entire practitioner community on a defensive problem at once. Wherever you are, whatever your background, I'd love to see what you build.
Register and learn more: https://t.co/x1TJlsQEpj
#CyberSecurity #AI #IncidentResponse
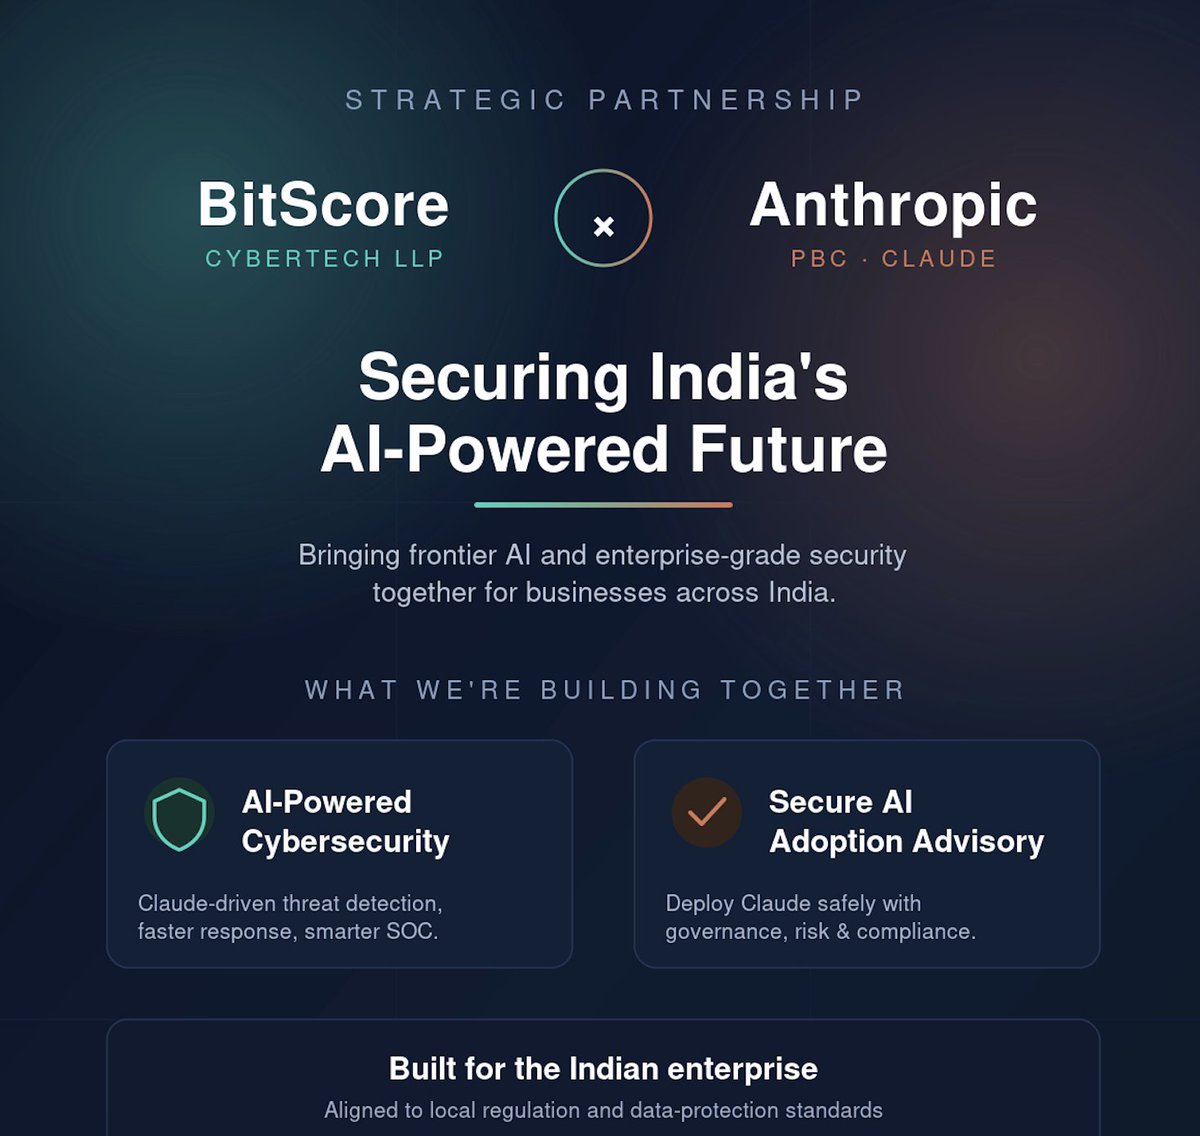
Bitscore Cybertech LLP is partnering with Anthropic PBC — the makers of Claude.
We're bringing the world's most capable AI together with serious cybersecurity to help Indian enterprises do two things at once: move fast, and stay safe.
Our focus:
🛡️ AI-powered threat detection and security operations, powered by Claude
🔐 Advisory to help enterprises adopt AI securely
AI will define the next decade of Indian business. We intend to make sure it's secure by design.
Grateful to the Anthropic Partner team, and to every client who's trusted us this far. The best is ahead.
Bitscore is partnering with Anthropic to bring Claude to our clients.
With this today's launch of Claude Fable 5 and Claude Mythos 5 — Anthropic's most intelligent generally available models, in a new tier above Opus — frontier AI is now a board-level decision, not a pilot project.
For CISOs and leadership teams in India, the question isn't capability anymore. It's deployment: The cyber security posture regulated sectors including critical national infrastructure demands. That's the gap Bitscore closes.
If frontier AI is on your 2026 agenda, let's talk.
https://t.co/G0dYeqSBy6
#EnterpriseAI #Cybersecurity #Claude #CISO #India
2026 is shaping up as the year third-party cyber risk stops being a checkbox.
From the SEC's Reg S-P and CMMC in the US to NIS2 and DORA in Europe, regulators are converging on one message: you own your vendors' risk.
For Indian firms serving global clients ... the takeaway is the same. Move beyond point-in-time audits to continuous monitoring.
How ready is your supply chain?
🔗 https://t.co/ZvkVkXaHJG
Declining breach numbers in 2025? Don't be fooled. Bitsight's State of the Underground 2026 shows the threat landscape didn't shrink—it shifted. Ransomware is going for bigger blast radius, hacktivists and APTs are hammering critical infrastructure, and attackers are weaponising AI for faster exploits.
The takeaway for defenders: sharpen prioritisation, harden identity, watch your supply chain closely.
https://t.co/3jl39G79Vl
🚨 A wake-up call for #India.
In Bitsight TRACE's latest research backing Operation Endgame (Europol + Microsoft DCU), sinkhole data revealed ~200,000 Amadey-infected machines in just 90 days — and India had the highest concentration of victims globally.
Loaders drop stealers. Stealers harvest credentials. The chain fuels fraud.
Patch, monitor, share telemetry. Disruption is a team sport.
https://t.co/sAcMB4fm7t
Electricity doesn't just run our homes — it runs hospitals, water treatment, banking, and defense. Bitsight's latest research provides a perspective: globally, 170,000+ monthly ICS/OT exposures were observed across 2025, and grid attacks aren't theoretical anymore.
For India, this hits close to home. Our power sector runs on a mix of legacy SCADA systems and newly connected smart grids — exactly the gap attackers exploit. Add rising geopolitical tension in our neighbourhood, and utilities become high-value targets — not just for outages, but for quiet, long-term access.
The grid will always be hard to defend. Awareness without remediation is just a false sense of safety.
https://t.co/vLxnUtPHg9
AI Man-in-the-Middle: the trust gap hiding in plain sight.
AI now sits between your people, your vendors, and your data. Handy for us — and just as handy for attackers, who use it to move faster and slip past MFA.
The lesson is old: you can't protect what you can't see. Map where AI lives in your supply chain before someone else does.
https://t.co/qNC9gUuzUn
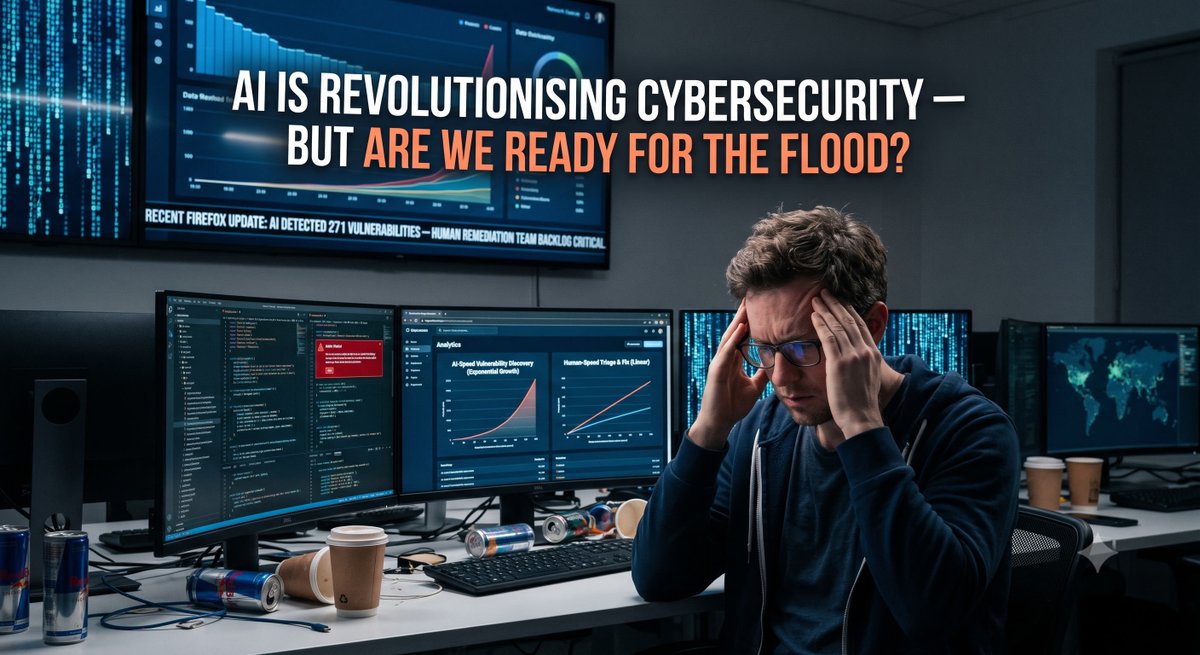
AI Is Revolutionising Cybersecurity — But Are We Ready for the Flood?
For decades, finding software vulnerabilities was a cat-and-mouse game built on human intuition and manual testing. AI is rewriting that playbook — and creating a new problem while it does.
Cybersecurity AI tools now triage crash reports, pinpoint root causes, and even recommend precise fixes. The results are real: during a recent Firefox update, Mozilla used advanced AI models to find and patch 271 vulnerabilities — far more than a human team could handle in the same window.
But that leap exposed a new bottleneck. Humans can't keep up.
AI surfaces bugs faster than developers can review and fix them. The volume of AI-generated reports got heavy enough that the Linux kernel maintainers issued fresh guidelines just to manage the backlog.
The point is simple. Our security workflows were built for human speed. If we want AI in our defences without burning out our teams, we have to redesign how we triage and remediate — at machine speed.
AI-speed discovery only pays off with AI-speed response. How is your organization building for it?
https://t.co/ve588d6IiG