SOMEONE JUST DROPPED A SERIOUS WEAPON FOR RED TEAMERS.
An open source red team platform that automates multi step attack paths across complex environments.
Meet ARES.
Give it a target and a goal like domain_admin or full_compromise, and it plans an attack path to get there.
→ 66 active modules covering 60+ MITRE ATT&CK techniques
→ Targets Active Directory, Windows and Linux
→ Supports AWS, Azure and GCP
→ Uses BloodHound data to map attack paths
→ Built in scope guard restricts testing to approved IP ranges
→ Generates detailed reports in PDF, HTML, Markdown and JSON
MIT licensed. Self hostable. Completely open source.
One platform. Multiple attack paths. Automated red team testing.
Only test systems you own or have permission to assess.
REPO BELOW
‼️ Hacktober – Cyberattack Wave Hits PHP, Node.js, Binance, LiteLLM, Pentagon, and a Few More
Details: https://t.co/nm8kBuRF96
October brought a heavy run of cybersecurity disclosures involving cryptocurrency exchanges, web servers, AI tools, software packages, government records, and grocery chains.
Binance investigated billions of dollars in unauthorized transactions, PHP issued emergency fixes, and a malicious LiteLLM release put developer credentials at risk. Other incidents involved Railway, OpenCode, Polymarket, Coinbase, Cursor, eMudhra, and Capcom.
Together, these reports show how exposed credentials and trusted software channels can turn a limited intrusion into a much larger security problem.
#CybersecurityNews
🚨 Yesterday, PHP2Shell made headlines. Today, we're already teaching you how to exploit it. Yeah, we're THAT fast⚡ Two critical PHP vulnerabilities. 9.2 CVSS. Unauthenticated RCE.
And you can already exploit the chain, bypass ASLR, and pop a shell in our latest recent threat room.
Hackers don't wait. Neither do we 🟢 Go Get hands-on: https://t.co/76TcpTLxpr
🔐 Claude AI Solves 25-Year NSA Cryptography Mystery in Just 30 Minutes
Details: https://t.co/BpRJ7Pn7nz
Anthropic says an internal Claude research model has traced the origins of five NSA-suppxaxxlied elliptic curve seeds in under 30 minutes, answering a cryptography question that remained open for roughly 25 years. The finding explains how important public security parameters were chosen, rather than exposing secret keys or breaking encryption.
In a report published October 16, 2026, researchers said the seeds behind NIST curves P-192, P-224, P-256, P-384, and P-521 came from lrand48, an older C library random-number generator initialized with Unix timestamps. The result challenges a long-running theory that the values were hashes of humorous phrases.
#cybersecuritynews
THIS IS F**KING INSANE
i found an open source AI pentesting tool that deploys multiple agents to automate security testing.
and it does more than just scan.
PENTEST-SWARM-AI can:
→ discover subdomains and live hosts
→ scan ports and find vulnerabilities
→ validate findings with evidence
→ generate exportable reports
→ connect to Claude Desktop and Cursor
→ automate scans through GitHub
Actions
multiple AI agents. one security testing workflow.
only test systems you own or have permission to assess.
REPO BELOW
Try running a standard STRIDE threat model on a multi-agent system where Agent A delegates to Agent B, who calls a tool, who spins up Agent C — and nobody scripted that path. Traditional frameworks assume a fixed app boundary. Agentic AI doesn't have one. MAESTRO threat-models all 7 layers of the stack: foundation models, data ops, agent frameworks, deployment, observability, security, and the ecosystem around them. https://t.co/3w93oo29WO #AgenticAI
🌐🔍 What Can Your Public IP Reveal?
A quick demo showing how public IP information can reveal an approximate location, ISP, and timezone. 🔐
🛡️ Privacy awareness only. Protect your IP address.
#CyberSecurity#OnlinePrivacy#Linux#CyberAwareness
⚠️ Microsoft Teams Vulnerability Allows Hackers to Perform Spoofing Attacks
Source: https://t.co/DtB6z8Ni05
A newly disclosed security vulnerability in Microsoft Teams could allow attackers to spoof local devices, raising concerns for enterprises and individual users who rely on the platform for daily communications.
The flaw exposes a critical weakness in how Microsoft Teams handles file and directory access, potentially allowing an attacker to manipulate or impersonate trusted elements within the application.
At its core, the vulnerability stems from files or directories in Microsoft Teams being accessible to external parties.
#cybersecuritynews #Microsoftteams
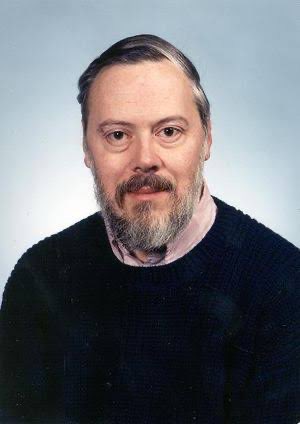
Dennis Ritchie created C in the early 1970s without Google, Stack Overflow, GitHub, or any AI ( Claude, Cursor, Codex) assistant.
- No VC funding.
- No viral launch.
- No TED talk.
- Just two engineers at Bell Labs. A terminal. And a problem to solve.
He built a language that fit in kilobytes.
50 years later, it runs everything.
Linux kernel. Windows. macOS.
Every iPhone. Every Android.
NASA’s deep space probes.
The International Space Station.
> Python borrowed from it.
> Java borrowed from it.
> JavaScript borrowed from it.
If you have ever written a single line of code in any language, you did it in Dennis Ritchie’s shadow.
He died in 2011.
The same week as Steve Jobs.
Jobs got the front pages.
Ritchie got silence.
This Legend deserves to be celebrated.