How can frontier AI models be trained to exploit real-world targets without getting tricked by reward hacking?
Our Chief AI & Science Officer, Dr. David Brumley, explains why traditional cybersecurity benchmarks fail and how redesigning RL environments enables effective training and evaluation of offensive AI capabilities.
Watch the full talk: 👇
https://t.co/kQU4XkyeCs
Are you getting continuous validation, an exploitability/risk score, and predictive intelligence in one place? Watch the on-demand webinar to learn how Bugcrowd can help. https://t.co/shaNuXKGSj
Come join Bugcrowd's Reddit community, where you can brag about the bugs you found, vent about the ones that got marked as "duplicate," and pretend you're not just refreshing your inbox every five seconds for a bounty.
➡️ DELETE /api/user/999 → 403 ❌
Try this:
➡️ POST /api/user/999 + X-HTTP-Method-Override: DELETE → 200 ✅
➡️ POST /api/user/999?_method=DELETE → 200 ✅
Gateways/auth middleware often match on verb+path. Frameworks (Laravel _method, Express method-override, Rails) may accept overrides at the router level.
Same for edge rules that only guard GET/POST. Try HEAD/PATCH/OPTIONS too.
"Managing the PHP threat involves striking a balance between the risk of a severe cyberattack and the business impact of downtime." ⚖️
In the wake of PHP2Shell, our CI&SO Nick McKenzie shares a CISO perspective about how security and business leaders made decisions under pressure, what works, and what other CISOs can take into the next critical vulnerability.
https://t.co/DUHza8PwA9
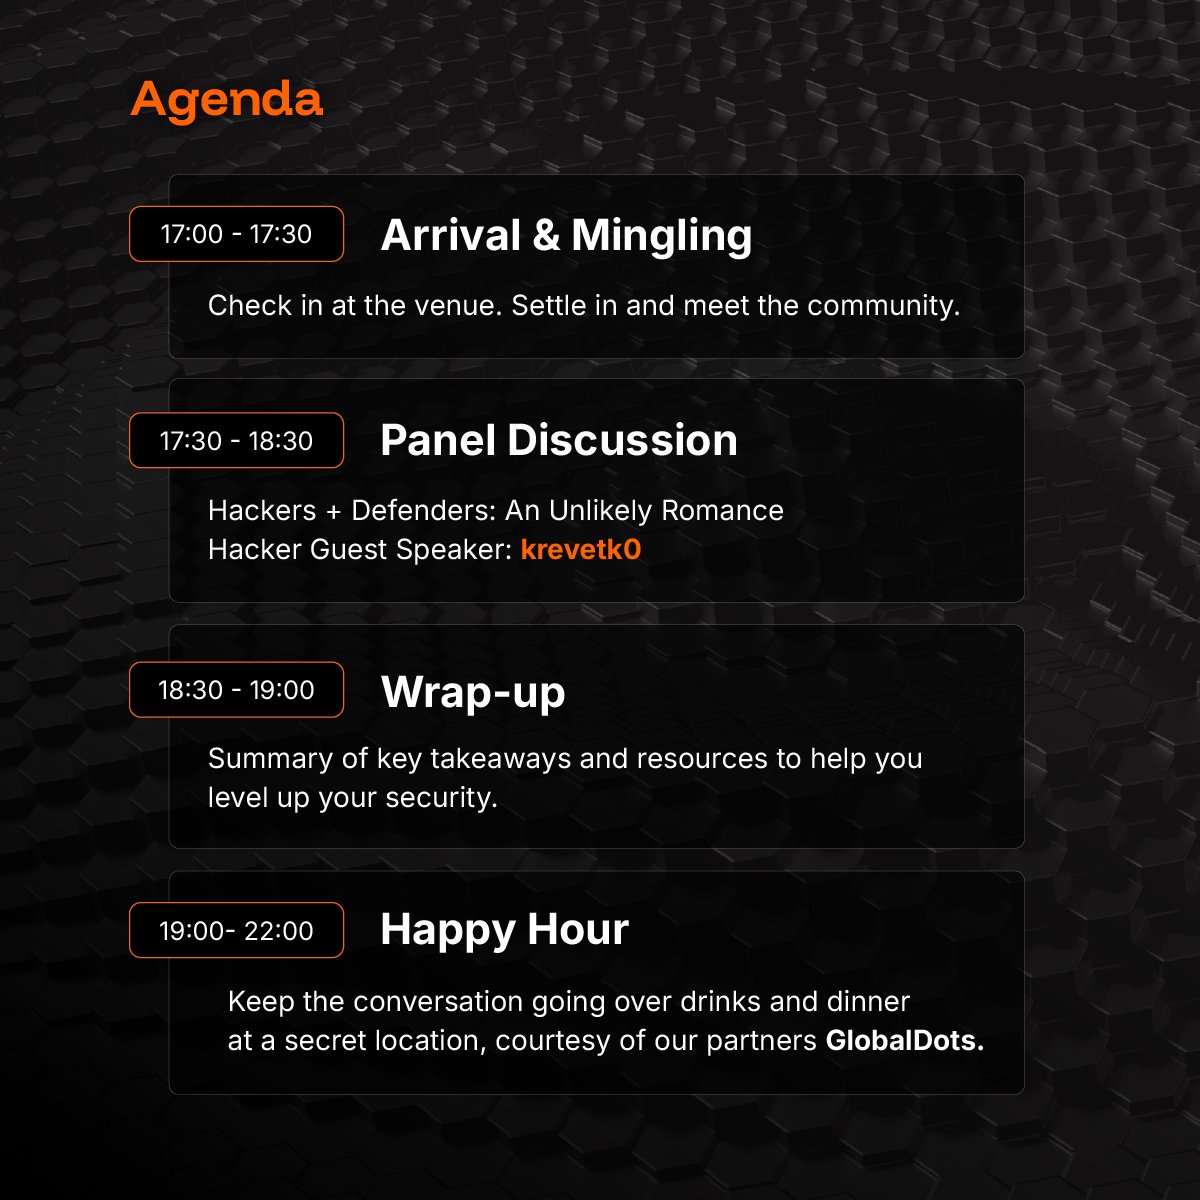
Exactly one week from right now, you could be:
🟠 Meeting CISOs and expert hackers
🟠 Learning how to uncover vulnerabilities faster
🟠 Networking over drinks and dinner
It's your last chance to sign up for the Hive Exchange Nuremberg! Don't miss it 🚀 https://t.co/m7lMu3SUnM
You can never go wrong with recon. 🔎
Here are some tactics you can try:
🟠 Scope company domains
🟠 Scope target company acquisitions
🟠 Enumerate ASNs
🟠 Run reverse WHOIS lookups
🟠 Enumerate subdomains
🟠 Analyze open ports
🟠 Check ad/analytics trackers
🟠 Use Shodan to find exposed assets
🟠 Google copyrights, terms of service, and privacy policies
Just make sure to test only in-scope assets. ✅
UPCOMING EVENT: Join us on October 21 for the RSA Conference, where Alistair G, our Director of Red Teaming, will participate as a panelist in the Innovation Showcase: "Countering AI-Powered Fraud Before It Happens."
Register here:
https://t.co/eKT9okdgqx
You can now scroll X and Reddit at the same time! ⏬
If you’re interested in:
➡️ Bug bounty
➡️ Security news
➡️ or anything hacking-related
Follow us here and on Reddit! 🔔
Here’s our official subreddit: 👇
https://t.co/0G6cI75xhF