The official threat intelligence account for @Cloudflare. Follow for threat research, incident assessments, WAF rule updates for emerging threats, and more.
AI-orchestrated penetration testing platforms like ARTEX have become increasingly powerful tools enabling effective attacks on exposed infrastructure. https://t.co/cMcZPTgamd
These tools have also begun chaining stolen customer credentials in some of the more complex attacks, such as lateral movement chaining throughout an environment.
https://t.co/6bVbA9RpP6
ARTEX: We observed activity in excess of 69 requests per minute across multiple unique parts of their Cloudflare infrastructure and 400 database dump requests in an hour.
https://t.co/6bVbA9RpP6
Security alerts don't arrive one at a time. They flood in.
To solve alert fatigue, we built an evidence-grounded agentic security harness for Cloudflare Managed Defense.
How it works:
• Locks down scope boundaries in code before inference
• Delivers consolidated, evidence-backed insights with zero hallucinations
•Taps advanced models like GPT-5.6 Cyber and Mythos with @OpenAI and @Anthropic
Full breakdown: https://t.co/08YZKVla6U
Your scanner just flagged 4,000 vulnerabilities. 78 are critical. Which one do you fix first?
We built a service that answers that question using production evidence. Early access starts today. (1/6)
https://t.co/TkfTWPq5Lk
We are expanding access to Cloudforce One's Threat Events Platform to every Cloudflare account and introducing Threat Signals. Threat Signals automatically parses open-source threat reporting, extracts structured indicators, and connects threat context directly to your WAF rules. https://t.co/4cACzfyVe4 #BirthdayWeek
We break down the technical architecture behind our multi-stage vulnerability discovery harness and automated triage loop. Learn how we manage state controls, squash false positives through adversarial review, and route around LLM context limits.
https://t.co/qFWmgEgwXP
Cloudforce One conducted research into how linguistic deception and file structure can be used to bypass AI-driven code auditors across 18,400 API calls. The findings show that malicious detection rates drop when deceptive comments make up less than 1% of a file and that burying payloads in files larger than 3MB effectively blinds models to malicious intent. Read the full report here: https://t.co/70M380p6W8
Cloudflare has released a new emergency WAF rule addressing the following CVE to enhance customer protection.
cPanel - Auth Bypass (CVE-2026-41940)
https://t.co/orEfADhF2X
Cloudforce One has identified a fundamental shift in the threat landscape: the era of industrialized cyber threats. This era focuses on high-trust exploitation and prioritizes results at all costs.
To help organizations counter these changes, today we are releasing the 2026 Cloudflare Threat Report. This report equips organizations with the intelligence they need to build a strategic 2026 roadmap.
Get the report: https://t.co/ie8MLQJQEf
Cloudforce One has successfully disrupted the criminal enterprise known as Tycoon 2FA, one of the most popular Phishing-as-a-Service (PhaaS) kit providers, in coordination with industry partners. Read here: https://t.co/nIMA83dyfv
Cloudflare has released new WAF rules addressing the following CVEs to enhance customer protection.
SmarterMail - Arbitrary File Upload (CVE-2025-52691)
SmarterMail - Authentication Bypass (CVE-2026-23760)
https://t.co/PZnybPuWA1
Why waste a zero-day when session tokens grant direct access?
Why build a custom server when a reputation shield provides nearly untraceable infrastructure with a high delivery rate?
Why attack the network when you can use deepfakes to embed insiders directly within your target?
Introducing the 2026 Cloudflare Threat Report.
The top finding? Threat actors have industrialized, and they’re prioritizing ROI at all costs.
https://t.co/SRvUJ5HfZG
The top metric? Measure of effectiveness.
In 2026, the most dangerous actors aren’t the ones with the most advanced code; it’s the ones who can integrate intelligence and technology into a single, continuous system that achieves their mission in the shortest time possible.
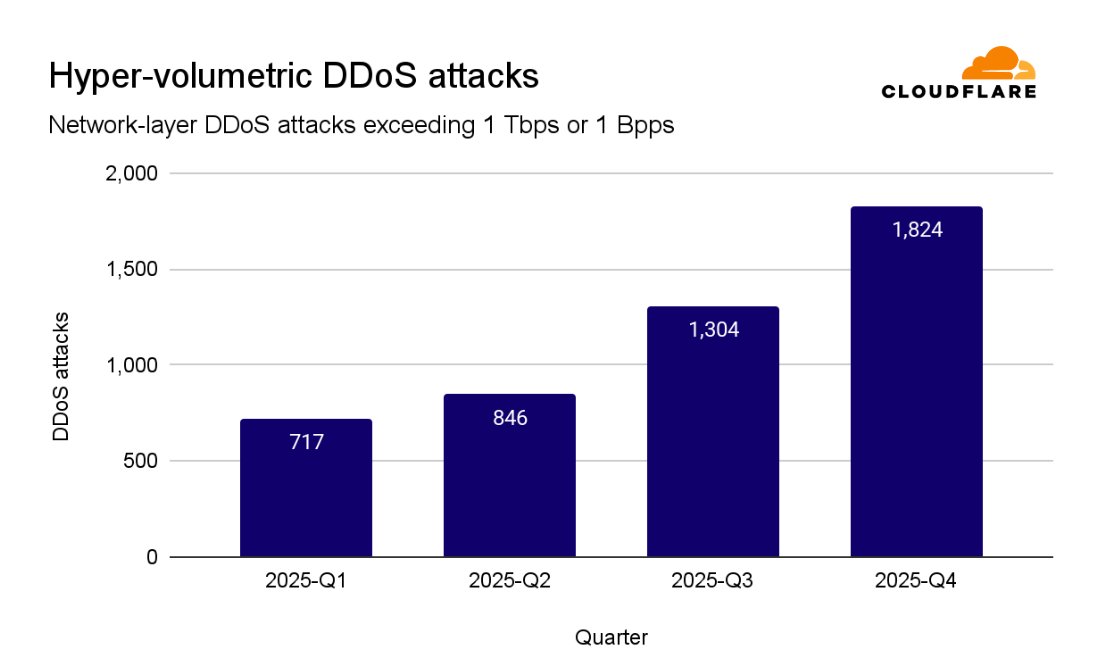
NEW: The total number of DDoS attacks more than doubled in 2025. And the world-record for largest DDoS attack observed by @Cloudflare was broken 19 times this year, with the current record-holder at 31.4 Tbps
https://t.co/02ycASkpT7