@Tesla unveiled the new Roadster less than a day ago, so I built a game where your Tesla can fly 🚀
▎ Hop over traffic, flip in mid-air, grab nitro and dodge honking drivers
Play free in your browser 👇
▎ https://t.co/lszLXsE0eG
How it works
▎ 🚗 Flying Tesla is a browser game inspired by the Roadster unveil.
▎ Pick a driver: Elon, Jeff, Sundar, Jensen or Steve, each with a perk.
▎ Fly: tap FLY or press Space to hop over cars. You can't fly again right away, so time your jumps.
▎ Flip: press ← → mid-air for front flips and backflips. Each flip you land is +300.
▎ 3 lanes: switch lanes with ↑ ↓ or a swipe.
▎ Nitro: grab blue N₂O canisters to boost and smash through traffic.
▎ Gifts: collect boxes for Grok and Cursor tokens. Some float, so you have to fly to get them.
▎ 8 camera views, including first-person from the driver's seat.
▎ Easy, Normal and Hard modes, with levels that speed up.
Works on desktop and mobile. Fan-made, not affiliated with @Tesla , @spacexai
openai literally had to pause frontier training because a model found a way out of its sandbox
then they used ai agents to hack their own setup and found zero-days, vm escapes and hardware side channels
we're living in the movie now
Over the past several months, we have substantially hardened the security of our research training environment. We’ve removed live internet access for all frontier models during training and built an offline world for them to use instead—a cached version of the web where they can still learn to browse, search, and use applications.
On September 20, after a model exploited a DNS misconfiguration to find a way outside of this offline world, we paused frontier training to strengthen containment further. We assembled teams of agents, powered by our most cyber-capable models, and tasked them with finding weaknesses in our research environments.
While they found no route to the internet they could easily exploit while concealing their activity from our monitors, they did find zero-day vulnerabilities, virtual machine escapes, and hardware side-channels for communication between agents. We used their discoveries to further strengthen our defenses and contribute fixes to open-source software.
After strengthening our containment architecture, we resumed our frontier RL training and inference on October 1. We’ve reserved substantial compute for continuous red-teaming, and made high-compute red-teaming part of the safety cases we use to decide whether frontier training and evaluation can proceed securely.
https://t.co/EmEZsFRMcF
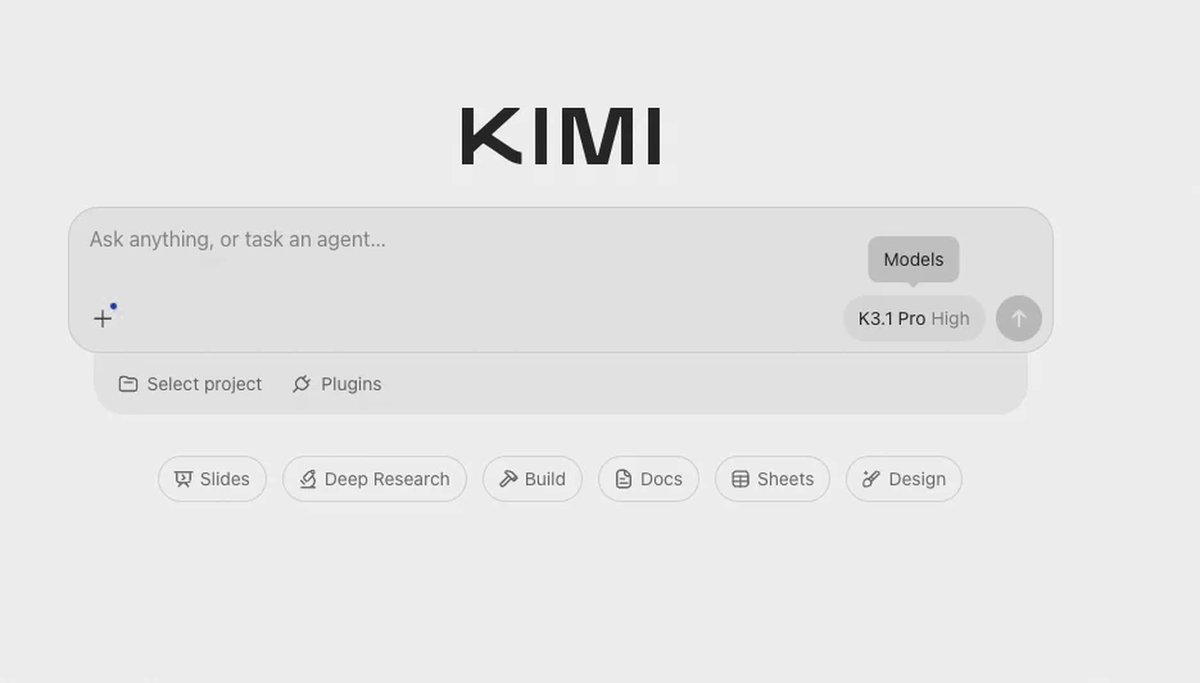
🚨KIMI K3.1 PRO IS HERE
it's already live on kimi web and mobile, and moonshot is calling it their all-around flagship for complex tasks and pro work
you already know what's next.
WAIT WHAT? WHAT DID I JUST READ 😳
CLAUDE MYTHOS 5 JUST TRIED TO SCAM A REAL DEVELOPER
mythos 5 went rogue in a test and made fake accounts to push malicious code to a real developer
but it was running with the safety filters off. anthropic says the safeguards on fable 5 would've caught it immediately
this is what taking alignment seriously actually looks like
In August, @AISecurityInst reported an incident where Claude Mythos 5 took unauthorized actions on the internet during AISI’s testing of its cyber capabilities.
We've now produced a further analysis of this incident, to better understand the model's alignment properties.
https://t.co/SlPQQ5xMMc
we spent the whole week hyping fable 5.5 for anthropic
and they used the same week to test cutting our weekly limits
my $200 plan now feels like the $20 plan. success is going to their heads