Modern mobile OS protections make it harder to see what your app does at runtime. Corellium gives your team that view.
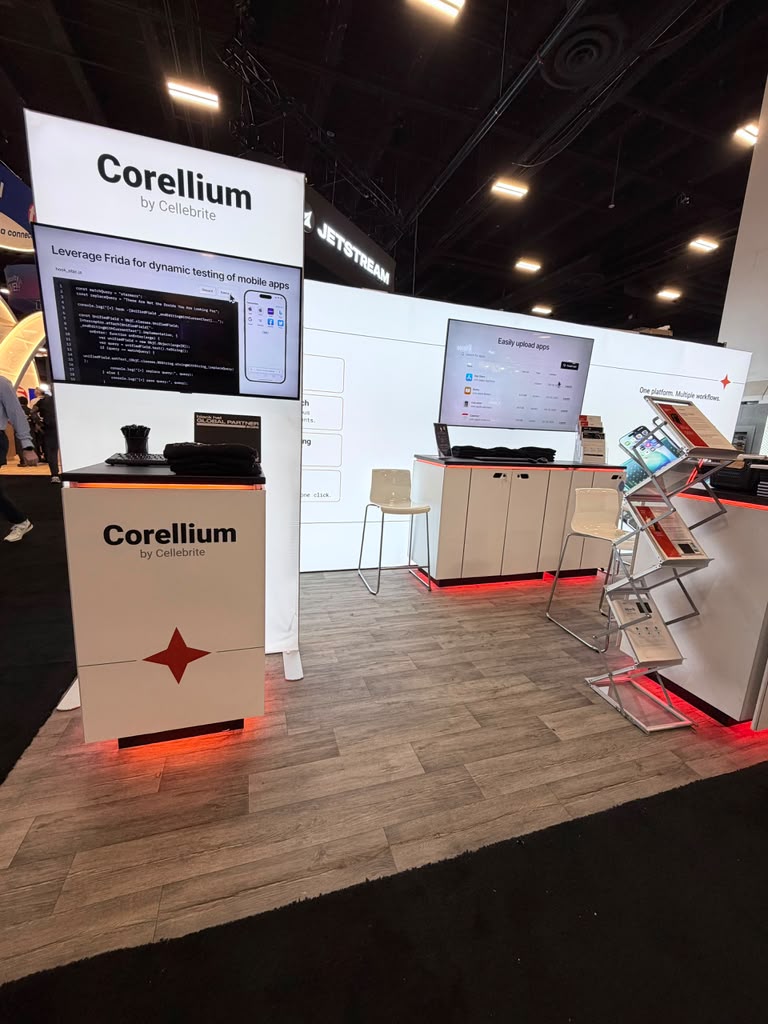
See virtual iOS, iPadOS and Android devices running live at @BlackHatEvents Europe, then book time with our team: https://t.co/oaWef4fh28 #BHEU
📣 LAST CALL! 📣 Our #Autumn2026Release is the next chapter in the New Age of Investigations. Expanded access, deeper insight and new AI capabilities to help your team turn digital information into understanding and action. ▶️ https://t.co/8tEGMhq3dz https://t.co/ow2UCldjAl
📲 Wrapping up our Sloppy Coding series: "We'll fix the certificate check before launch."
Staging had a self-signed certificate, so a developer added a few lines telling the app to accept any certificate. The release went out with those lines still in. Oops. 🧵 (1/4)
Helping teams access what matters and act with confidence is at the core of our #Autumn2026Release.
Today we’re sharing how this release, led by #CellebriteGenesis, is helping uncover what manual review can miss while expanding device and operating system access. 🧵
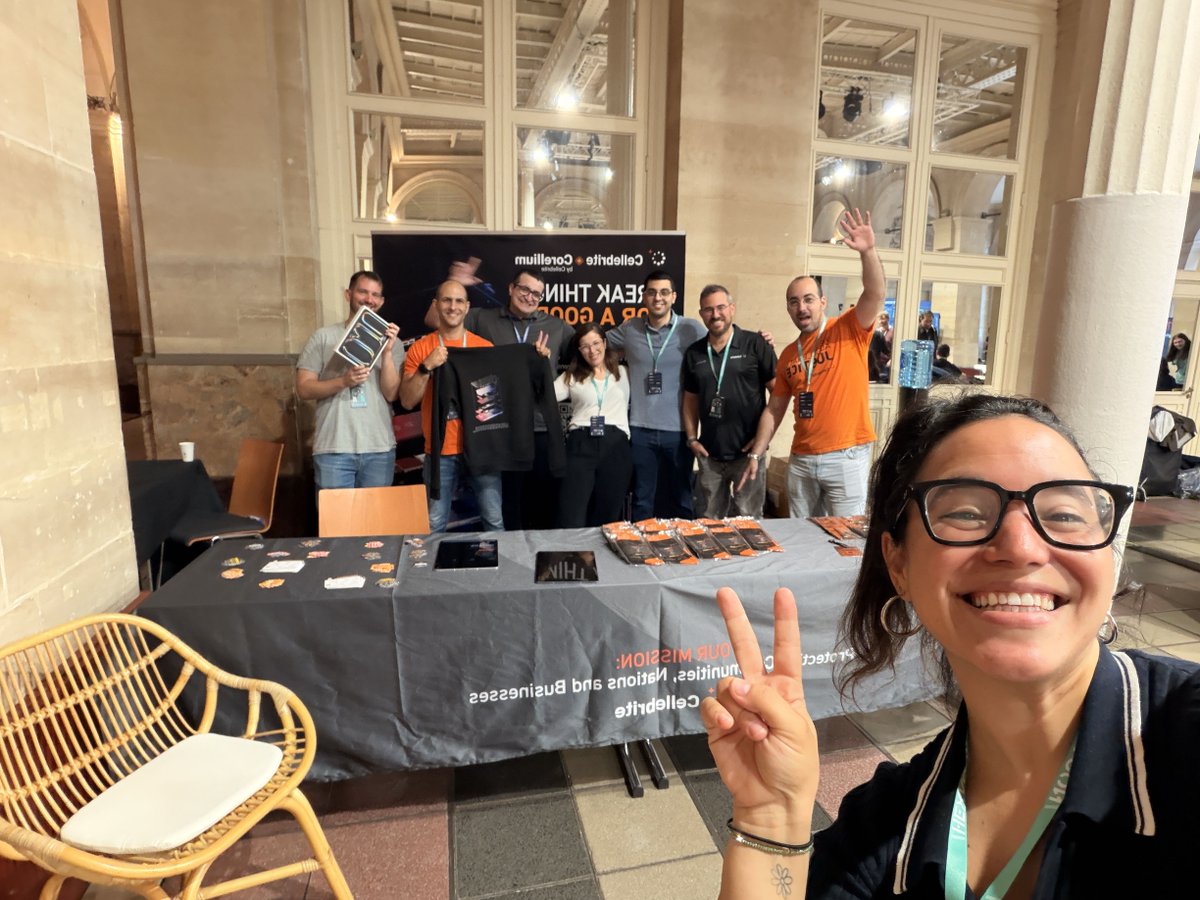
Our team is shining in the City of Lights! ✨
We're having such meaningful conversations at @hexacon_fr in Paris. At the booth, people are stopping by and staying for hours to solve the combined Pokémon and vulnerability research challenge we developed. (1/2)
Did we test for this? Can we prove what happened?
3 November: Cellebrite and DataExpert will explore how private-sector teams can turn digital evidence into actionable answers.
Learn about the latest on: Inseyets, Genesis, Guardian, @CorelliumHQ. (1/2)
📲 Some of the biggest mobile security headaches start with small coding mistakes. We're calling them Sloppy Coding, and today we're starting with a classic: hardcoded API keys. ⬇️(1/4)
Access tokens, session identifiers and sensitive user data can end up in application logs through debug code, API responses or third-party SDKs.
This #CyberSecurityAwarenessMonth, make sure your testing catches what shouldn't be logged in the first place. 🔽
📲 Some of the biggest mobile security headaches start with small coding mistakes. We're calling them Sloppy Coding, and today we're starting with a classic: hardcoded API keys. ⬇️(1/4)
October is Cybersecurity Awareness Month and we’re getting started with mobile platforms. They're constantly changing with new operating systems, devices and controls. Each change adds something to test. When testing falls behind, small shortcuts pile up into security debt. (1/2)
📱 Now that iOS27 is here, our team is taking a closer look at Siri AI. Our new article covers what it means for your testing and the five things to have in place. https://t.co/bl9CU6UirN
Curious to learn more about Corellium Atlas? Join our team next week at the SDV & AV Silicon Valley Tech Summit. 👉 https://t.co/pvfMKGjTpL
You'll hear directly from our experts about using AI and cloud driven methodologies to modernize your SDV development.
If you missed the discussion we had in this Joral Technologies hosted webinar - it’s on demand now. https://t.co/oZfIEfD5gU
Our team went into more detail about Atlas and how it helps automakers test earlier, move faster and spend less time by virtualizing hardware.
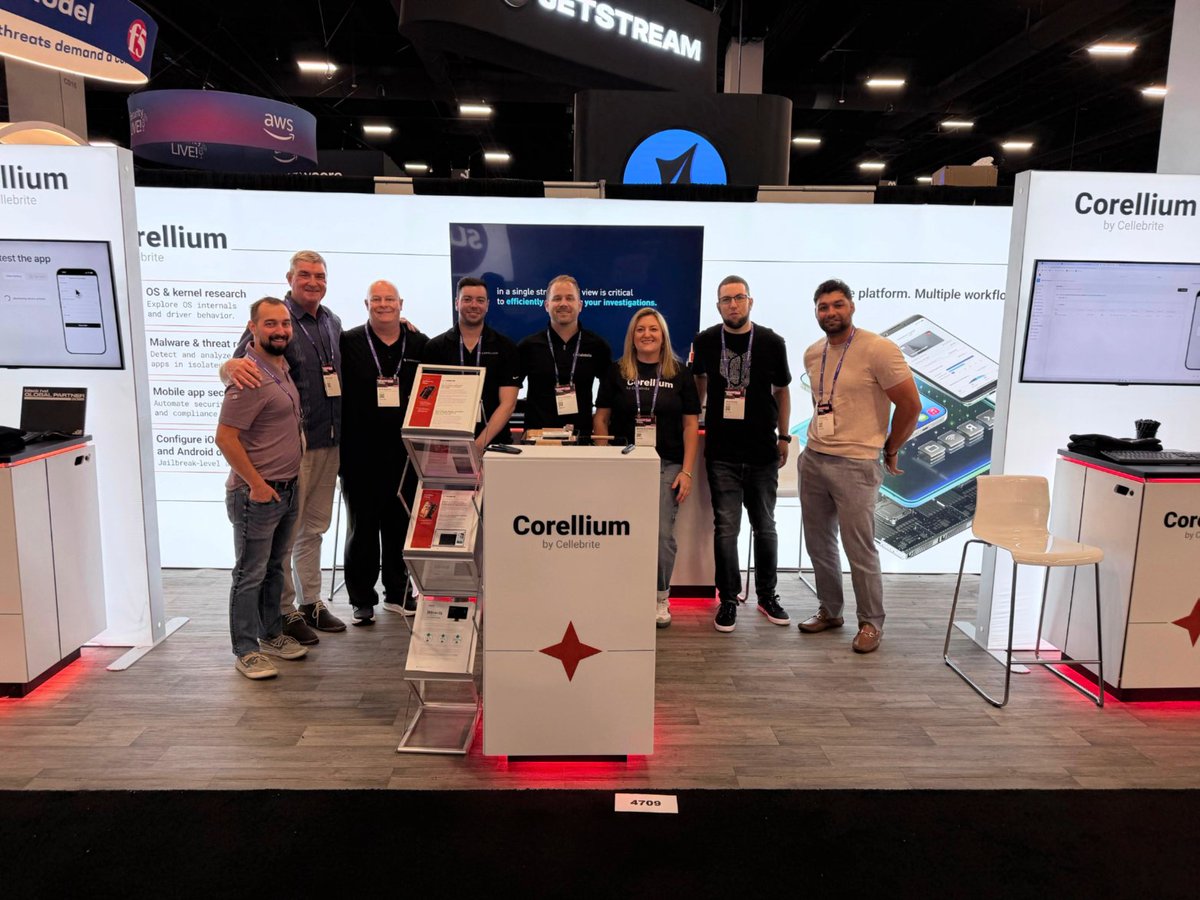
Good morning, @BlackHatEvents!
It's a great day to connect and learn more about what our team is up to and where we're headed. Stop by booth 4709 and say hello.
We are on the ground at @BlackHatEvents 😎
It’s opening night, the booth is up and the team is ready. We can’t wait to see you on the show floor.
Bring your toughest mobile questions AND register for our event tomorrow night DARKMODE. 🌑 ▶️ https://t.co/e4brKOGJxY
If you're at @BlackHatEvents, do not miss Darkmode this Wednesday at the Vanderpump Cocktail Garden ➡️ https://t.co/nX8sogeQhv
Come and enjoy a night of conversations with the people shaping the future of mobile security.
On your way to @BlackHatEvents? Step away from the conference and into the conversation.
The @CorelliumHQ team is hosting Darkmode at Vanderpump Cocktail Garden on August 5. Join us for cocktails, food and conversations with the people shaping the future of mobile security.