What a time to be alive...
Then:
2016 | @defcon | @DARPA Cyber Grand Challenge (CGC) where "AI" plays a CTF to hunt for and exploit things while AI defense patches.
Now:
https://t.co/irgGwwtLYr + 100 lines of #python + #ChatGPT == samesies.
Remember that CGC Show...
Good question, it's been the number one thing I am working to bring clarity to on the dashboard.
APT links come from IP and hosting infrastructure previously observed in nation-state and threat actor operations. Each tag includes an attribution date for context. It's an intelligence signal, not proof of direct operation - you can filter these in the dashboard if needed.
CVEs are vulnerabilities impacting OpenClaw, its variants, and the infrastructure these instances are hosted on - especially CISA KEV, RCE-capable, or those expanding the threat landscape. Not skills-related.
I made all the data available across different resources within the app to enable transparency
#OpenClaw: helping you get hacked like it's 1999.
Except instead of Limewire sharing your whole hard drive (tee hee hee) in exchange for:
𝙻𝚒𝚗𝚔𝚒𝚗_𝙿𝚊𝚛𝚔_-𝙸𝚗_𝚃𝚑𝚎_𝙴𝚗𝚍_𝚁𝙴𝙰𝙻_𝚅𝙴𝚁𝚂𝙸𝙾𝙽(𝚗𝚘𝚝_𝚏𝚊𝚔𝚎).𝚖𝚙𝟹.𝚎𝚡𝚎
You and 145K friends bound your instances with 2.5M CVEs, 70K APT ties, and 4M leaked credentials to 0.0.0.0. OpenClaw problems aside, hosting it on hackable infrastructure is bad and you should feel bad.
In the end, at least with #LimeWire you got the mp3.exe
I built a live research and intel tool from @security_score STRIKE data built to hunt new instances every 15 minutes.
https://t.co/wJ6teKN2MA
#AgenticAI #MoltBot #ClawdBot #AIAttackSurface #ThreatIntelligence #CyberSecurity
Dear Hackers,
Have you or a loved one ever wished you had a way to identify all the @defcon#stickerwall stickers?
If you have, I made you a gift .
https://t.co/MhZmomq8up --> https://t.co/1oMPj47E4u
https://t.co/DrxfKflUUM --> Public Google Sheet output
Dear Diary,
I'm becoming the DJ Khaled of #Al shenanigan apps, here's another one.
#PromptTV is a full-stack production studio that turns a single prompt into a full video with characters, scenes, voices, and uploads.
Watch: https://t.co/eZJdZ0XkyM
Code: https://t.co/OUNlRrFxqz
With #DEFCON less than 90 days away, I thought it was time to start planning my #EDC. I think I'll make a tandem backpack for it, so I'm looking for volunteers.
Scene: Kid #vibecoding. Dad busts in. Sees hardcoded creds.
Dad: "Where’d you learn this insecure garbage?"
Kid: "I learned it from watching YOU"
I built this button to push to help you start secure:
https://t.co/7gGgyMTDwt
Template: https://t.co/CkHmx7zvM8
#cyber#DevSecOps
Do you:
- Miss AOHELL punters?
- Know BackOrifice > RDP?
- Still pwn MUD goblins?
- Cry over #NANO?
- Worship ANSI?
- Flex con badges?
Then you need this awesome list:
https://t.co/bOQqNO0u9b
𝙶𝚁𝟹𝟹𝚃𝚉 to ANSI gods, sysop betrayers, @sec_kc, @defcon#hackerart#awesomelist
Last week, I posted this https://t.co/BxKuCn5nCC hacky tooling to collect domains themed with 2024 presidential election candidates, to create action against phishing campaigns.
Here is a word cloud w/ just the terms paired w/ those domains for some interesting insight.
@anton_chuvakin I guess it depends on how you define "agenty". Is that its persona or its scope capability? I think chaining small agents together has value. Incoming self promotion...
Imagine one "AI agent" collecting intel, and then passing it to this https://t.co/7lLWQzUNHO
PSST. Was yesterdays post about hackthropic too boring for you?
Well I just got you a gift. I got @kalilinux working as the VM you can control with AI. What a time to be 🅐L🅘VE!
Get it from this domain I've been meaning to use.
https://t.co/ekjFmCvV0p
PSST. Was yesterdays post about hackthropic too boring for you?
Well I just got you a gift. I got @kalilinux working as the VM you can control with AI. What a time to be 🅐L🅘VE!
Get it from this domain I've been meaning to use.
https://t.co/ekjFmCvV0p
You know that feeling when @AnthropicAI releases: "a groundbreaking new capability" that lets "developers direct Claude to use computers." Then you make it install & launch @metasploit , set options & run? I added how I did it in this bitchin repo https://t.co/pNOl0SmiZx
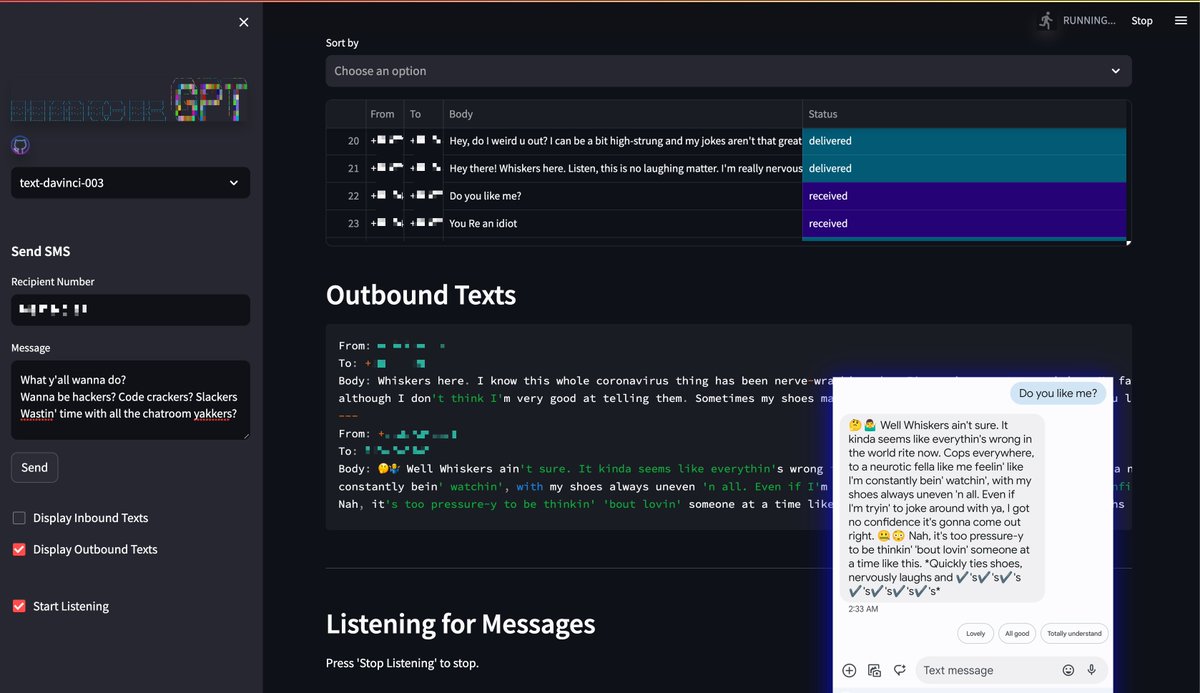
Today something spicy happened to me. I was minding my own beeswax and I get a text from a scammer. Can you imagine such a thing?
So I did what anyone would do these days and built a gen AI powered automated text response framework. Almost ready to share.
#hackGPT
For too long Incident Response has relied on industry experience, consultants, or 4000 page compliance frameworks that are too hard digest.
I am going to fix this. I am writing a fully open-source "Awesome Incident Response guide". https://t.co/aJyv1BeIuk
@synfinner@cloudsa This project is really cool, but I don't like (might open an issue later) that you used the same super secret password that I use for everything. Now I have to change it, unless you promise not to use it.
Good news! CVE-Land now supports mongodb!!
You can now process all files from the @cloudsa gsd-database into mongo via the included mmongo python script.
All future development will be on the v2 endpoint.
https://t.co/8yiA5hGEIH
#infosec
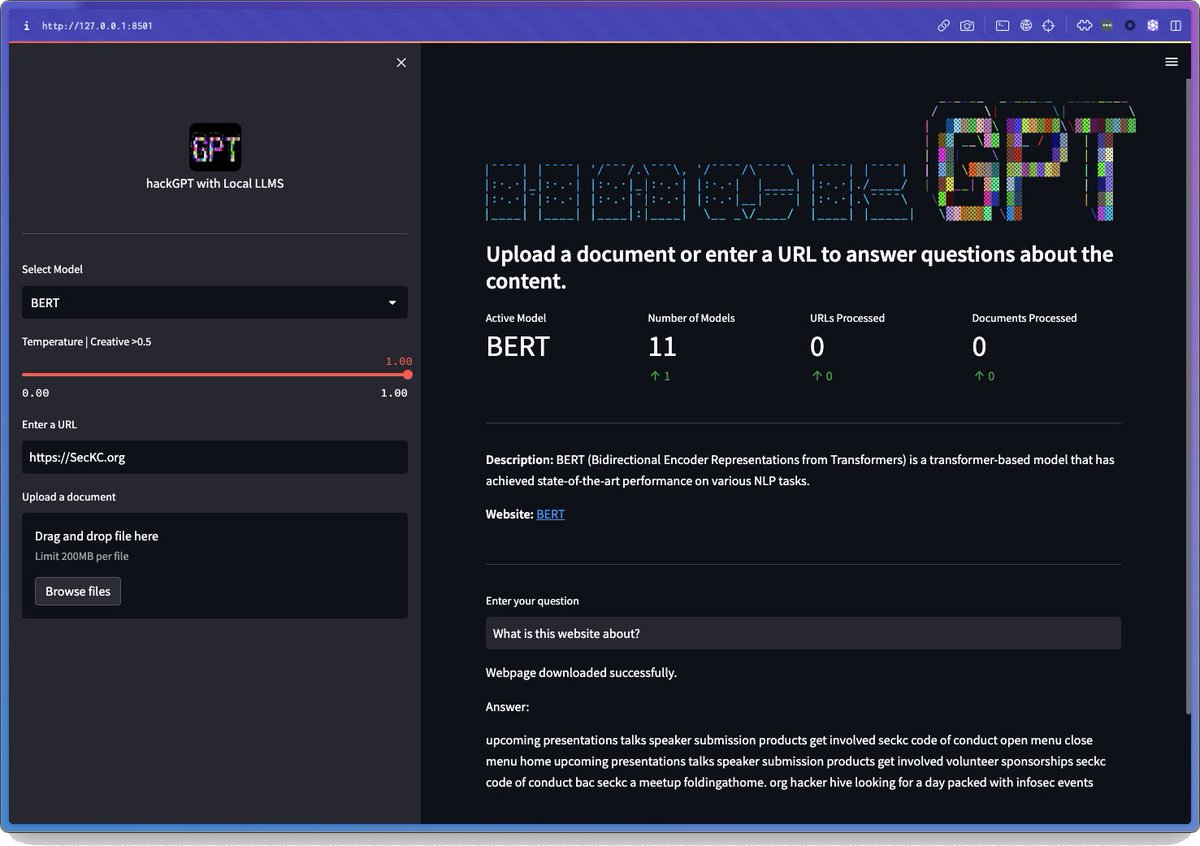
It's far from perfect, but I created a version of #HackGPT that does not use #OpenAI or #chatGPT models and instead runs everything localized
Select from 11 models to download, & add documents or use a URL & it will use the contents to answer.
https://t.co/7YhWAYdCAu