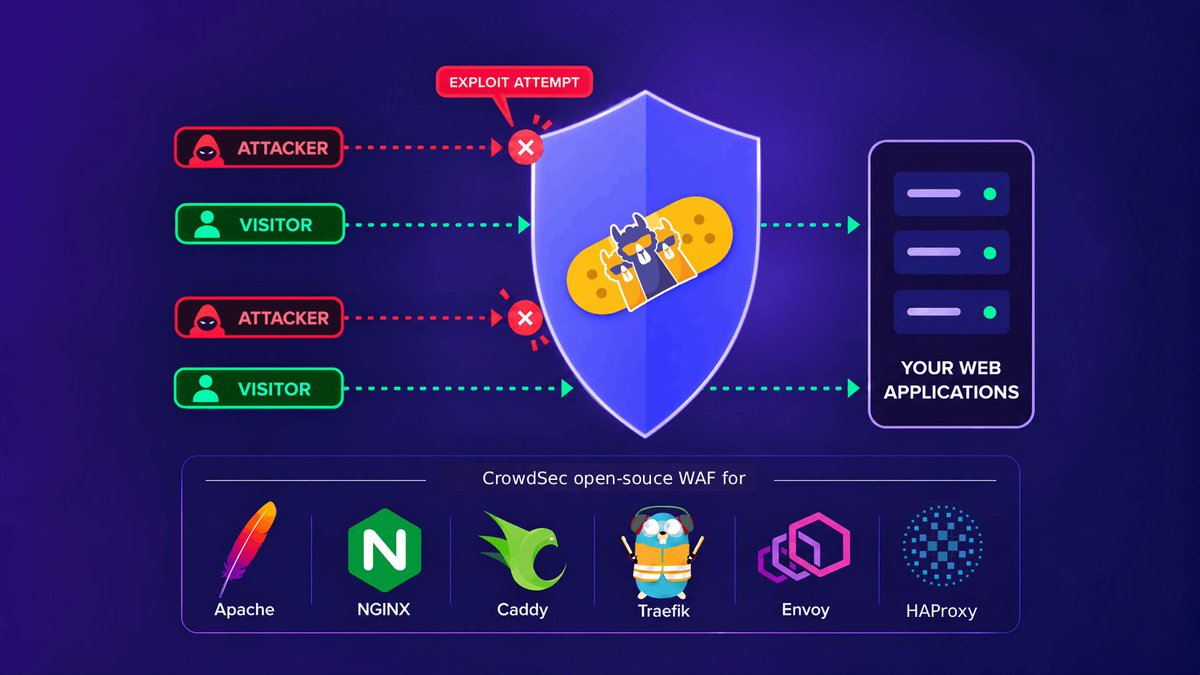
In just 3 steps, you can set up the CrowdSec WAF, a free and open-source web application firewall:
1. Install the rule collections
2. Turn on the AppSec Component
3. Point your bouncer at it
#WAF#opensource
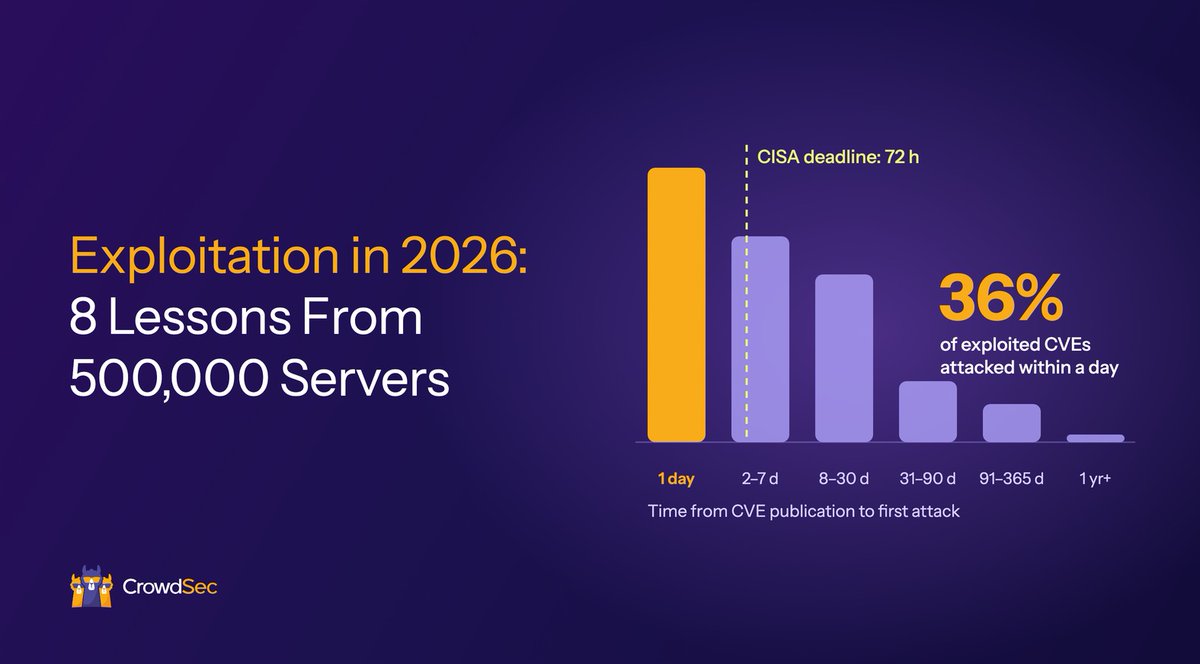
36% of exploited CVEs were attacked within a day of publication. Another 27% within the week.
CISA gives US federal agencies 72 hours to fix the most urgent ones. For more than a third, the attack starts first.
What our network saw in 2026 👇
#cybersecurity #vulnmanagement
PHP2Shell hasn't turned into mass exploitation. Not yet.
5 days of CrowdSec Network data: the first attempts were blocked before the CVEs were even published, and half of the 1,187 IPs sent a single request.
What happened, and what to watch 👇
When you can patch PHP2Shell depends on your PHP version:
8.2–8.5: today
7.4–8.1: source backports only
5.4–7.3: nothing from the PHP project
~48% of PHP sites have no full release to upgrade to.
How to cover the wait 👇
Don't wait for a sign of attack: the request returns a normal HTTP 200. In our network data, 36% of exploited CVEs were attacked within a day of publication:
https://t.co/hvM6R62Fzb
PHP2Shell (CVE-2026-109618/109619): Unauthenticated attackers can run code on a PHP server. No login, no vulnerable app code needed.
Patch now: 8.5.12, 8.4.27, 8.3.36, 8.2.35.
PHP 8.1 and older: no fix from the PHP project.
https://t.co/doWm8giAMS
Can't patch every box today? The CrowdSec WAF has free, tentative virtual patches for both CVEs:
cscli appsec-rules install crowdsecurity/vpatch-CVE-2026-109618
cscli appsec-rules install crowdsecurity/vpatch-CVE-2026-109619
A stopgap, not a fix: still update PHP.
What is bot detection, in 30 seconds? 🤖
It's how your site tells real visitors from automated ones before they can scrape your content, buy out your stock, or hammer your login page.
CrowdSec's WAF Bot Detection does it with fingerprinting and proof of work, without getting in the way of real customers.
Watch the quick explainer 👇
Set it up: https://t.co/RFBaauFATo
#WAF #botdetection #cybersecurity #opensource
Console notifications now go straight to your inbox. 📨
Notification rules now support email, so you can create a rule without connecting Slack or Discord first. Set a rule, add your address, done.
Set up your first rule: https://t.co/1NVH9LURuM
Available on Premium.
CrowdSec saw the first requests matching CVE-2026-88771 on September 22, five days before Citrix published it with a fix (and before @watchtowrcyber shared details). It's a CVSS 9.5 flaw in NetScaler ADC and Gateway: no login, default configuration, root on the box.
Our signal counts are low, but don't read that as low risk. Careful operators pick their targets first, and two of the addresses we saw went after this CVE and nothing else.
Patching won't remove anyone already inside. The full story is in this week's Threat Alert 👉https://t.co/P8Jj15tYmB
#cve #cve202688771 #threatalert #cybersecurity
On the night of 7–8 October, a drone attack hit Yandex's data center in Sasovo, Russia.
Our sensors saw it from the other side of the internet: the YandexBot traffic hitting our network went dark.
Here's what the CrowdSec map showed 👇 https://t.co/BEOuLRa6z2
Two visitors hit your site. Same browser, same clicks, same speed. One of them is a bot.
Which one? CrowdSec 1.8's WAF can tell, and on October 29, our experts will show you how, live, along with everything else in 1.8.
📅 October 29, 4 PM CET
Get a reminder → https://t.co/JXTew4LzqW
#webinar #WAF #botdetection #cybersecurity
5 years of data science at CrowdSec, told by Matthieu Mazzolini (Data Team Lead).
How do we count our network? Why do we run honeypots, and why only 30? Why are there canaries in our blocklists? And why does the team call malicious IPs "pokemons"? 🙂
An honest look behind our IP reputation, and at what our code really shows, from one of the people who builds it.
Read it here: https://t.co/8fkZ2vrMUI
#datascience #threatintelligence
The holiday season brings a predictable increase in malicious bot activity, from scraping and scalping to more aggressive attacks. With Black Friday and Christmas approaching, now is a good time to make sure your infrastructure is ready.
🤖 CrowdSec’s bot detection uses fingerprinting and proof of work to distinguish legitimate users from unwanted bots, helping you protect your applications without getting in the way of real customers.
Handle distributed attacks, scraping, scalping, and other aggressive automation with a production-ready approach.
Learn more → https://t.co/HzdQNFXgtk
#WAF #botdetection #opensource
Full story on the GhostAction campaign, including how the workflow works and what to check in your repos, from @TheHackersNews: https://t.co/3Z8qD6gmSM
👻 GhostAction is back: attackers push a fake "Security Audit" workflow to GitHub repos and let your own CI send your secrets (cloud keys, AI API keys, tokens) to one hard-coded IP: 193.32.204[.]199.
Our network has known that IP for a month. It's malicious, very aggressive, and already on the CrowdSec blocklists.
Running self-hosted runners? Alert on outbound traffic to known-bad IPs, and rotate anything these workflows could reach.
Get all the details here → https://t.co/tebPc4U5N7
#supplychainsecurity #threatintelligence