ICYMI: In October 2024, we released the CTI Research Guide.
It aims to help practitioners learn more about how to effectively perform the collection, processing, analysis, and production stages of the CTI lifecycle.
🔗https://t.co/OMToNzb8vS
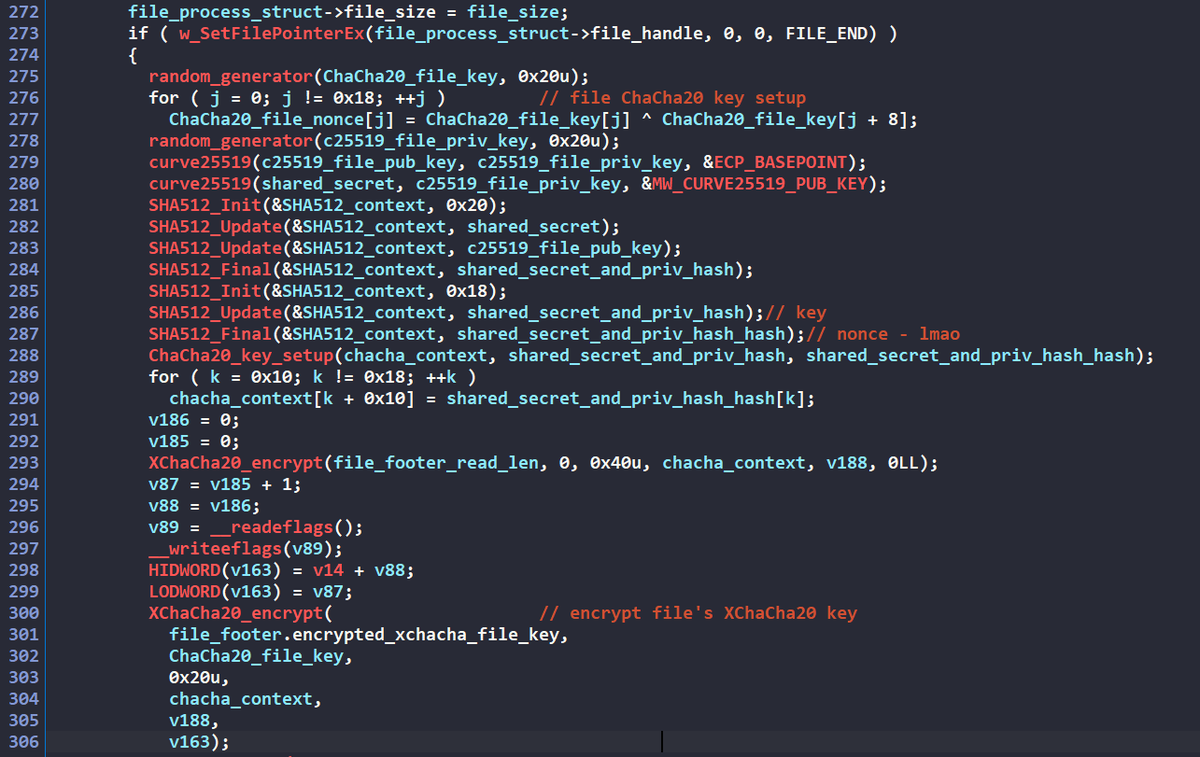
Reviving my blog with a complete analysis of the latest #LockBit#ransomware v4.0 Green! 🤠
https://t.co/BXID8ryR4R
h/t to @fwosar & @demonslay335 for all the crypto helps! Huge thanks to @BushidoToken & @CuratedIntel for the threat intelligence insight too! 🙏
⚠️PSA: VPN & RDWeb password guessing attacks have been observed originating from IP addresses consistently across the following subnets:
85.239.59.0/24
85.239.58.0/24
85.239.57.0/24
85.239.56.0/24
➡️ Check for low & slow password guessing attempts and successful logins.
⚠️PSA: Curated Intel members in DFIR have noticed a trend in exploitation of CVE-2024-57727 in the SimpleHelp RMM tool to deploy Medusa ransomware.
➡️ This tool is often used by IT Managed Service Providers (MSPs) to remotely control customer endpoints and have been impacted.
Got a new project to share later this year which will be published via @CuratedIntel — a community of researchers that are awesome at providing great feedback and insights. Keep a look out for it in the next few months! 📝
Last time we did, we made this:
https://t.co/GfXxRQOPNG
⚠️PSA: Curated Intel DFIR has noticed a new trend among Akira Ransomware cases in Summer 2024. For a while, Akira has been exploiting Cisco ASA devices.
➡️ They are now targeting SonicWall SSL-VPNs for access with no MFA (!) and weak passwords (!). Other TTPs remain the same 🔍
⚠️PSA: Curated Intel DFIR teams noticed a severe uptick in Akira Ransomware cases in Jan 2024.
Same repeated TTPs:
- Dwell times of < 4 hours on average
- Cisco ASA VPN for Access
- WinSCP for exfil / WinRAR for compression
- AnyDesk RMM for persistence
- 'w.exe' Akira payload
🌐 Curated Intel is tracking hacktivist, cybercriminal, and regional APT groups surrounding the war in Israel. We describe the types of campaigns and attacks we've observed so far and have also provided recommendations for CTI analysts monitoring the war.
https://t.co/ezeyTLV9LC
We had some good convos in the @CuratedIntel community today based on this @thecyberwire interview
Really interesting that @C_C_Krebs says the *most important skill* he looks for in a CTI analyst is their “ability to communicate risk to businesses” 🗣️⚠️
https://t.co/P9udeP8KDG
@BushidoToken@aejleslie@Gi7w0rm@AlvieriD@AJVicens@kevincollier@ddd1ms The thing that makes this profession hard sometimes is that victims lie about attacks, the criminals are lying pieces of shit, and randos on Twitter lie about what they know.
Trying to get through the lies to the truth is a big challenge.
@phillmoore and I posted a blog on a TTP observed in an #Akira Ransomware case.
➡️ Actor gains access to Hyper-V server (with EDR) and creates a fresh VM
➡️ Turns off server VMs and mounts Hyper-V data disk on new VM
➡️Starts encrypting vhdx files!
https://t.co/et3wfhsxlj
TL;DR of ALPHV/BlackCat's essay on the MGM breach
- The attack began ~8 Sept.
- They stole data and gained admin on their Okta SSO & Azure cloud tenant
- ~100 ESXi hypervisors were hit by ransomware on 11 September
- No ransom was paid
Read in full here:
https://t.co/nrqvnyWT8m
⚠️ Use Microsoft Teams? Watch out for TeamsPhisher!
While it is not usually possible to send files to MS Teams users outside your org, by security researchers found a bypass by manipulating Teams web requests 🔥
https://t.co/r7Yzj8fqLC
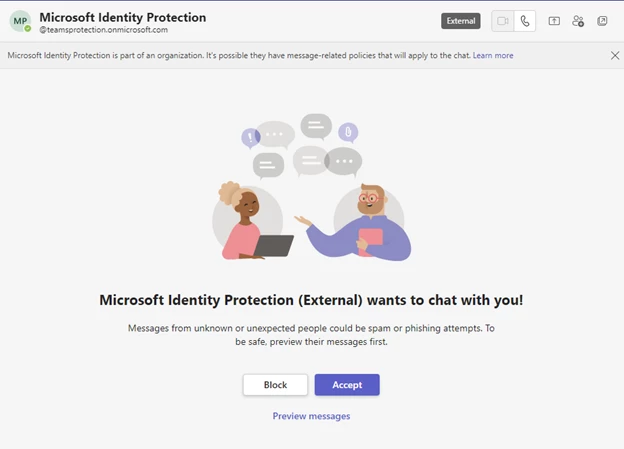
Examples of MS Teams phish lures ⬇️ 1/3