I think someone hacked my fridge too! Yeah, that’s why there’s all that the ice cream in the freezer and multiple cheese blocks. Definitely not me trying to fill a void.
https://t.co/7wS6Z0he9E
⚠️ ThreatLabz has uncovered another new Anatsa installer that is distributed via the Google Play Store. The application is disguised as an Android PDF reader that currently has over 10,000 installs.
The IOCs for this campaign are listed below:
Google Play Store URL
hxxps://play.google[.]com/store/apps/details?id=com.railforge.footplate.documentreader_pdfviewer
Anatsa Installer from Google Play Store
MD5: 152d8649a03667dbf4b94312d185c41d
C2: https://railforgefootplate[.]com/disclaimers.txt
Anatsa Payload
MD5: 2451fae883ec7a4e7876d6abe486e1eb
C2s:
http://193.24.123[.]18:85/api/
http://162.252.173[.]37:85/api/
Pretty cool technical analysis of APT activity related to a North Korea-backed threat group. Please read. I do all the editorial and images myself 💁🏻♀️💅
Zscaler ThreatLabz uncovered a suspected TraderTraitor campaign that uses a trojanized Terraform provider to deliver FLATROOF and ROOFDECK. The FLATROOF backdoor deploys cross-platform Python scripts to steal sensitive data from the victim before ultimately dropping the ROOFDECK backdoor to gain full remote control.
Read the full analysis here: https://t.co/rJ4fo33jRo
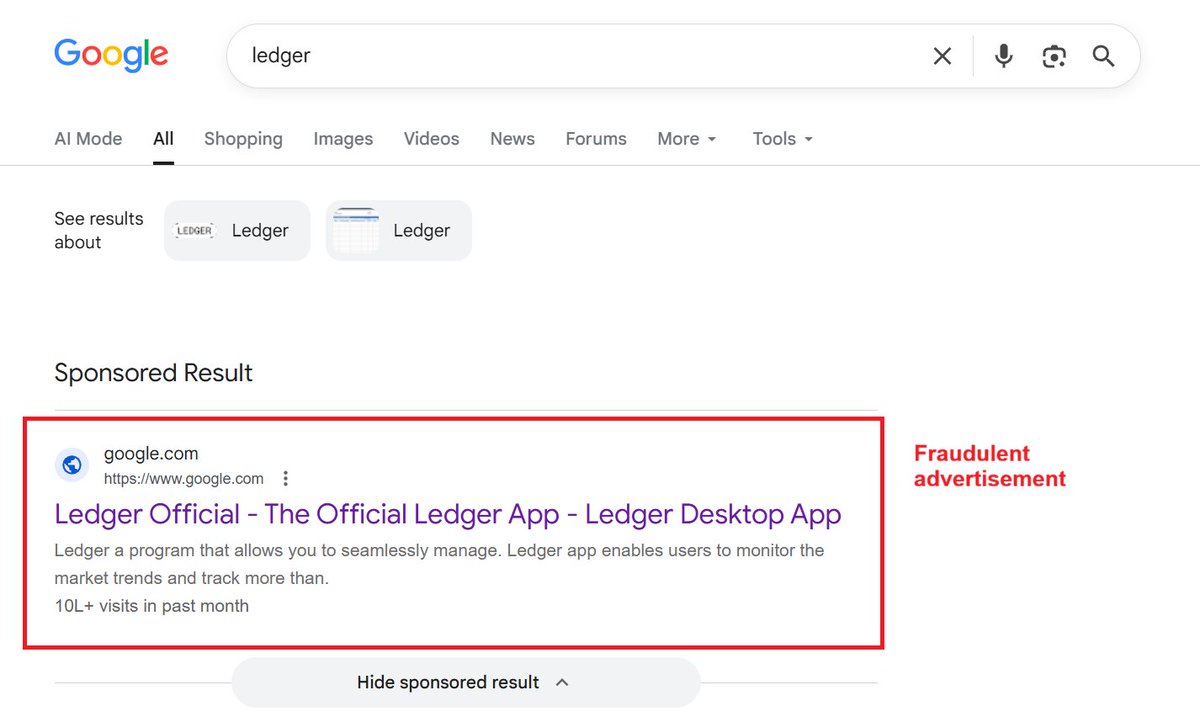
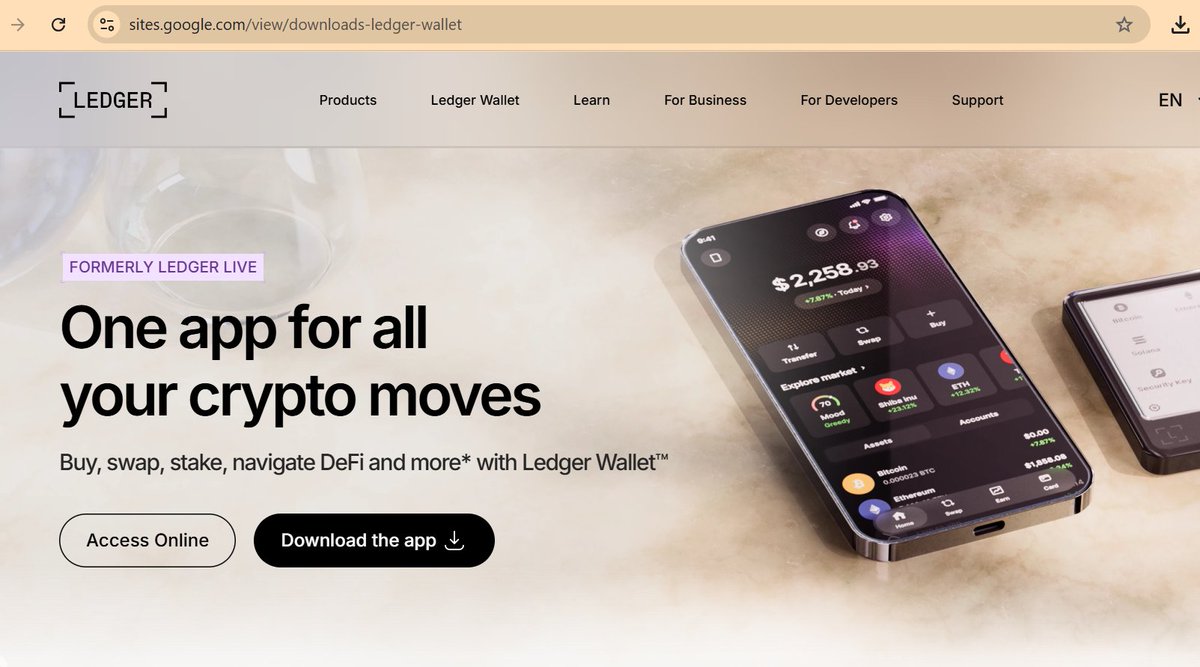
🚨ThreatLabz has identified an active phishing campaign that is targeting Ledger Secret Recovery Phrases to gain access and drain funds from cryptocurrency wallets. The attack abuses a compromised, verified Google Ads advertiser account with a clean history to push a fake Ledger website.
The campaign uses a 4-hop chain built entirely on trusted platforms. The process is the following: a malicious Google ad leads to a Google Cloud Storage redirect script, followed by a rotating Vercel subdomain that refreshes every 15-20 minutes, which then redirects to a phishing page hosted on Google Sites that mimics Ledger. The page then loads fraudulent content via an iframe from a second rotating Vercel domain.
The following IOCs are associated with this Ledger phishing campaign:
GCS Bucket URL: https://storage.googleapis[.]com/apf-leg-ad-23798/
GCS Bucket URL: https://storage.googleapis[.]com/ledg-leg1-79230/
GCS Bucket URL: https://storage.googleapis[.]com/apf-leg-ad-22076/
Google Sites URL: https://t.co/WkbMOc8uV0[.]com/view/start-ledger-wallet
Google Sites URL: https://t.co/WkbMOc8uV0[.]com/view/apps-ledger-wallet
🦠ACRStealer remains under active development, with new versions appearing almost weekly. The latest variant by identified by ThreatLabz is 4.3.7-alpha2.
IOCS are listed below.
SHA256 hash:
769d06b54576c6beab2d33c7d4c05b679156c051652a843d6cc61de2cc9c58f9
CNCs:
https://stream[.]echovale[.]cc
https://145[.]249.109.147
DDR: https://telegra[.]ph/C-Introduction-08-21
🐀ThreatLabz has identified a new Android-based RAT distributed through apps hosted outside of the Google Play Store that impersonates and targets cryptocurrency services such as 1inch Wallet, Binance, Circle, and MyCrypto. The RAT’s loader uses a malformed manifest header to evade analysis. ThreatLabz reverse engineered the RAT's capabilities, which include collecting SMS messages, call logs, clipboard data, contacts, image files, and device screenshots. The RAT also supports screen monitoring, live remote control, installing APKs, and remote shell execution.
The following Indicators of Compromise (IOCs) are associated with this new Android RAT:
Loader (installer) hash: 0be6d372e1a4983dcee845730bdff286
Loader download URL: https://download.cctoken[.]us/apk/1inchWallet.apk
Loader download URL: https://download.vvtoken[.]top/apk/BINANCEPOOL.apk
Loader download URL: https://download.cctoken[.]us/apk/SewaOnlineBD.apk
Loader download URL: https://download.vvtoken[.]top/apk/Swapped.apk
Loader download URL: https://download.cctoken[.]us/apk/MyCrypto.apk
RAT config URL: http://stripl.win-win[.]buzz:5188
RAT payload URL: https://dl.vvtoken[.]top/a/1w8381938.apk
RAT payload hash: D803f9945509d0eaf4d9b31b46abc199
RAT C2: https://api.us8266iw[.]xyz
Do you know too much about #truecrime? Get too excited when someone brings up #hhholmes and ruin the vibe? Yeah, me too. Check out some of these #california based cases.
Support my #delulu: https://t.co/p6LvX0Uu4y