Me alegra que alguien como Donald Knuth siga en activo y preocupado por avanzar.
Leí “El arte de programar ordenadores” hace mil años, si no recuerdo mal comprada en Diaz de Santos.
Stay hungry, stay foolish (Steve Jobs).
Prof. Donald Knuth opened his new paper with "Shock! Shock!"
Claude Opus 4.6 had just solved an open problem he'd been working on for weeks — a graph decomposition conjecture from The Art of Computer Programming.
He named the paper "Claude's Cycles."
31 explorations. ~1 hour. Knuth read the output, wrote the formal proof, and closed with: "It seems I'll have to revise my opinions about generative AI one of these days."
The man who wrote the bible of computer science just said that. In a paper named after an AI.
Paper: https://t.co/juSOmK9vOt
🚨Data Breach Alert‼️
🇪🇸Spain - Mapfre
The threat actor known as SkryllX claims to have breached Mapfre and allegedly compromised a massive database containing 21 million records.
According to the post, the leaked data includes comprehensive insurance policy details, such as policy numbers, names of policyholders (both individuals and organizations), national ID or tax ID numbers (NIF/CIF), addresses, phone numbers, and policy start dates.
Discover more at https://t.co/yiQ1nOhPjb
🚨Cyber Attack Alert ‼️
🇪🇸Spain - InfoJobs
InfoJobs recently identified that cyberattackers have used stolen user credentials to access its service and obtain a significant amount of data from candidate profiles.
😃 The Natasha neural network turned out to be 700 Indian programmers
The startup BuilderAI offered to write any application, like in a constructor, by selecting the necessary functions.
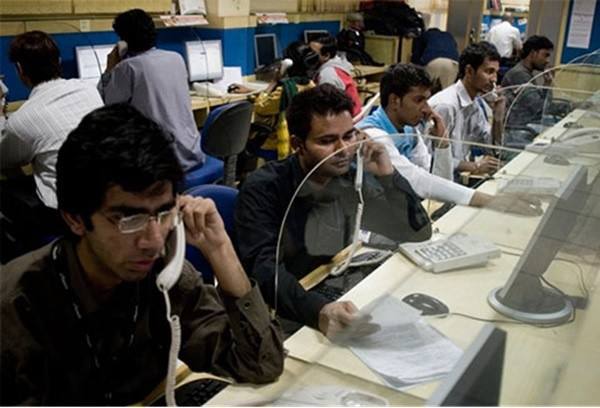
In reality, customer requests were sent to the Indian office, where 700 Indians wrote code instead of AI.
With the help of this scam, the startup attracted $445 million in investments from major IT giants, including Microsoft, over eight years.
At the same time, the applications “written by AI” constantly glitched, the code was unreadable, the functions did not work — in general, everything was like real artificial intelligence.
After the deception was exposed, the startup officially went bankrupt 🤷♂️
🚨Cyber Attack Alert‼️
🇪🇸 Spain - Ayuntamiento de Níjar
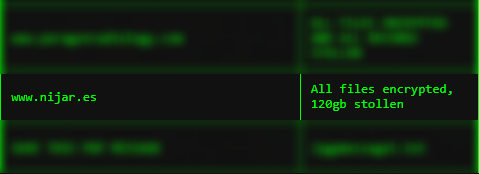
Devman ransomware group claims to have breached the Ayuntamiento de Níjar.
According to the post, the cybercriminal group managed to encrypt the data and allegedly exfiltrated 120GB. The ransom demand has yet to be defined.
Discover more on https://t.co/yiQ1nOhPjb
CVE-2025-31650 : TomcatKiller
Una herramienta diseñada para detectar la vulnerabilidad CVE-2025-31650 en Apache Tomcat (versiones 10.1.10 a 10.1.39)
https://t.co/Tb9RfNX4Dk
El diputado delegado de Universidad @JRomero_Imbroda ha calificado como “día histórico” la aprobación por el consejo de Gobierno del convenio que permitirá la implantación de Ciencias de Datos e Inteligencia Artificial.
Ya se avisó en 2021 que de 120 dominios estatales el 95% se podían suplantar por mala implementación de DMARC (entre ellos el de @policia), y se mencionó a @dsn, @INCIBE, @incibe_cert y @CCNCERT
En el segundo 6 aparece https://t.co/0ph6MTS9jm
+ info👇
https://t.co/L8aoAw9DZm
🚨 La plataforma de ciberseguridad CrowdStrike está caída a nivel mundial, causando problemas de TI, fallos en Microsoft, interrupciones del 911 en estados de EE.UU. y afectaciones en aerolíneas españolas, bancos y grandes empresas. ¿Qué es CrowdStrike y qué está pasando?🧵
- Guía del autoestopista galáctico (Douglas Adams)
- Sin noticias de Gurb (Eduardo Mendoza)
- El bastardo recalcitrante (Tom Sharpe)
Son libros para reír y releer aunque la respuesta sea siempre 42 😀
Dime un libro con el que hayas llorado de la risa. El mío es "La conjura de los necios" de John Kennedy Toole, y con diferencia. Creo que la comedia en literatura es dificilísima, y las desventuras de Ignatius Reilly son puro delirio desternillante. Un clásico inmortal.
#DataLeak Alert 🚨
🇪🇸#Spain: Comisiones Obreras (CC. OO.) Allegedly Breached
A database containing 21,988 full credentials (login, pass) belonging to Comisiones Obreras (https://t.co/iYYwOwMaNe), officially named Confederación Sindical de Comisiones Obreras, has been leaked in a hacking forum.
The threat actor with the alias "fpa" claims that some time ago, they defaced all their pages, and now they are publishing the credentials they were able to steal from their server.
The passwords are hashed, but a quick analysis shows that some are easily decryptable, therefore Comisiones Obreras users are advised to preemptively change their login credentials.
Confirmation or denial of these claims has yet to be verified.
#DataBreach #DarkWeb #Security #Infosec #CyberAttack