5 AD misconfigurations to check today:
• Excessive privileges
• Dormant accounts
• Over-privileged service accounts
• Nested groups
• Misconfigured delegation
Small gaps become major attack paths. Find and fix them early.
https://t.co/C0sJWQdGEo
#DelaSecurity
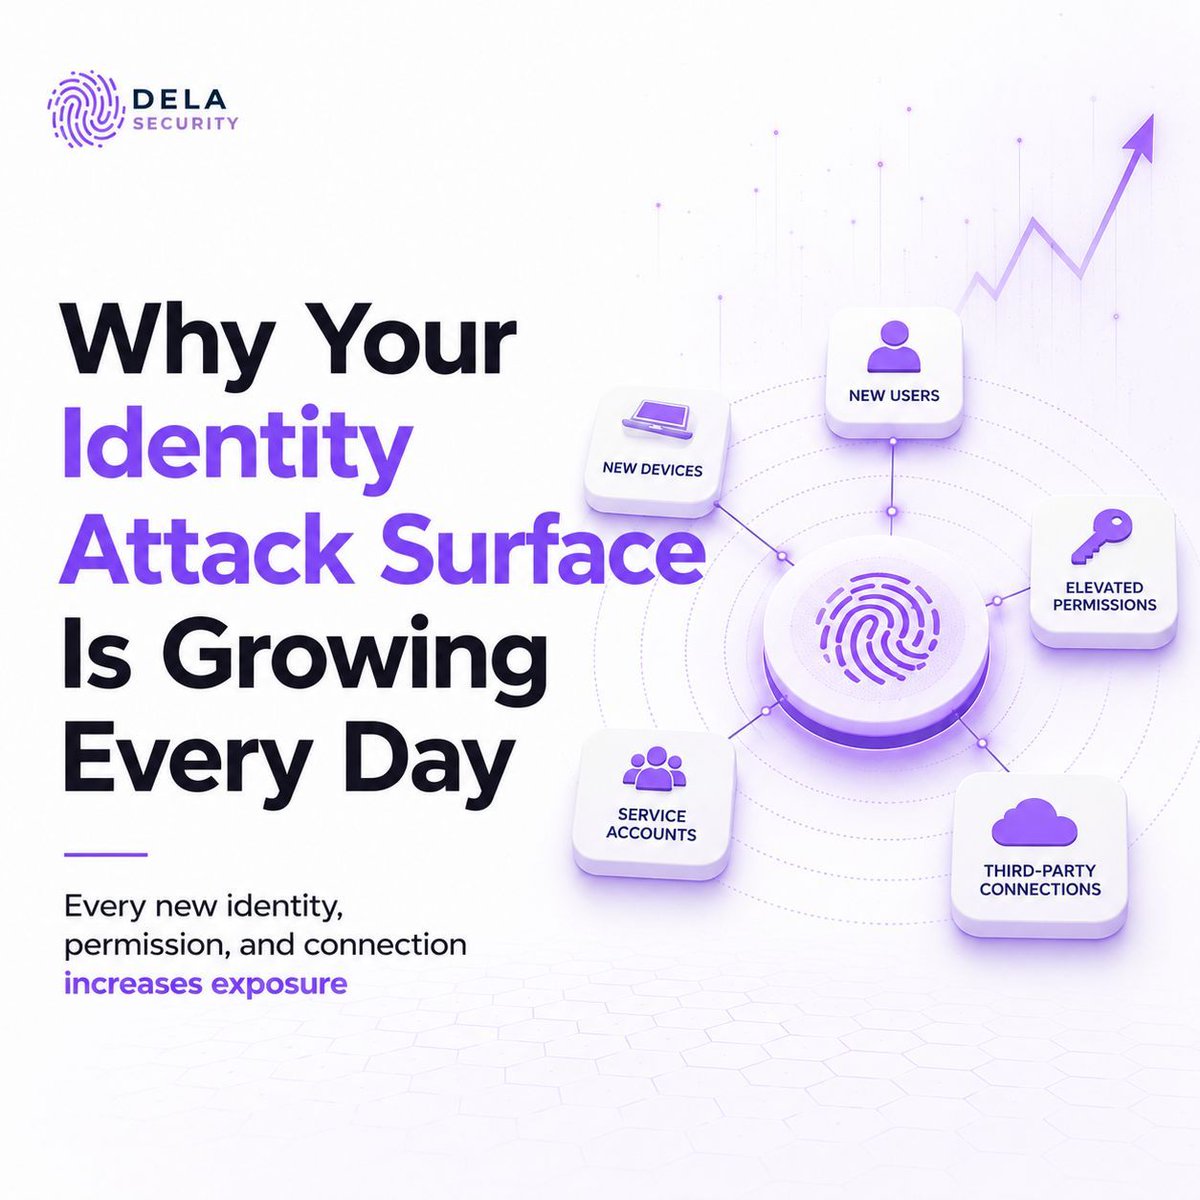
Your identity attack surface grows every day.
New users, apps, service accounts, and permissions create hidden attack paths attackers are quick to exploit.
Continuously review and reduce identity exposure.
https://t.co/C0sJWQdGEo
#DelaSecurity#IdentitySecurity#EntraID
Your identity attack surface grows every day.
New users, apps, service accounts, and permissions create hidden attack paths attackers are quick to exploit.
Continuously review and reduce identity exposure.
https://t.co/C0sJWQdGEo
#DelaSecurity#IdentitySecurity#EntraID
Your identity attack surface grows every day.
New users, apps, service accounts, and permissions create hidden attack paths attackers are quick to exploit.
Continuously review and reduce identity exposure.
https://t.co/C0sJWQdGEo
#DelaSecurity#IdentitySecurity#EntraID
You can't reduce identity risk if you can't see it.
Hidden attack paths, excessive privileges, and dormant accounts create opportunities attackers exploit first.
Get visibility before they do.
https://t.co/C0sJWQdGEo
#DelaSecurity#IdentitySecurity#ActiveDirectory
Attackers don't just target accounts—they target the relationships between them.
Hidden permissions, group memberships, and trust relationships create attack paths to privileged access.
Map them before attackers do.
https://t.co/C0sJWQdGEo
#DelaSecurity#IdentitySecurity
Most attack paths start with a standard user—not Domain Admin.
Attackers exploit hidden permissions and identity relationships to move laterally and escalate privileges.
Map your attack paths before they do.
https://t.co/C0sJWQdGEo
#DelaSecurity#IdentitySecurity
The most dangerous attack paths are often hidden in plain sight.
Over-privileged service accounts, nested groups, and dormant accounts can quietly lead to Domain Admin.
Find the path before attackers do.
https://t.co/C0sJWQdGEo
#DelaSecurity#IdentitySecurity
Not every breach starts with an exploit. Most start with legitimate access.
Attackers abuse hidden permissions and identity relationships to move laterally and escalate privileges.
Find your attack paths before they do.
https://t.co/C0sJWQdGEo
#DelaSecurity#IdentitySecurity
Nobody had Domain Admin. The path already existed.
Attackers don't need exploits—they abuse hidden permissions, nested groups, and over-privileged accounts to reach Domain Admin.
Discover your attack paths 👇
#DelaSecurity#DelaIEM#IdentitySecurity#ActiveDirectory#EntraID
200+ security audits. Same problems every time.
One of the biggest? Visibility.
Many teams don’t know how many accounts exist in their environment—leaving old accounts, stale identities, and hidden privileged access exposed.
New video 👇
https://t.co/mY1jBn9MR1
80% of breaches start with stolen credentials. Not malware. Not exploits.
Identity is now the primary attack path—and most defenses miss it.
🎥 https://t.co/Mh36Zxbh2t
80% of breaches start with stolen credentials. Not zero-days. Not malware.
Just a login.
Attackers don’t break in—they log in.
If identity isn’t secure, nothing else matters.
New video 👇
https://t.co/Mh36Zxbh2t
Attackers reach domain admin in minutes.
Most orgs take days—or weeks—to respond.
That gap isn’t tooling. It’s process.
See where delays happen—and why they put you at risk
🎥 https://t.co/PGbAPzXloc
Attackers move in minutes. Teams take days.
They can reach domain admin fast—while response lags behind.
The gap isn’t tools. It’s process.
🎥 See how to close it 👇
https://t.co/PGbAPzXloc
98% MFA coverage isn’t security.
Attackers don’t bypass MFA — they find the accounts without it.
In one case: 67 accounts had no MFA despite “98.7% coverage.”
Find the gaps. Enforce MFA everywhere.
🎥 Watch the full video: https://t.co/hiuSiJmoWj
Most teams focus on MFA bypass. That’s not how breaches happen.
Attackers don’t break MFA — they find accounts without it or ones you can’t see.
98% coverage isn’t enough. Watch how it actually works 👇
🎥 https://t.co/hiuSiJmoWj
Global Admins without MFA are a direct path to full tenant compromise. Attackers can steal creds, bypass controls, and persist unnoticed. Enforce MFA, use conditional access, and audit privileged accounts now.
#DelaSecurity#DelaIEM#EntraID#IdentitySecurity
Orphaned or unlinked GPOs can still enforce risky settings. Attackers can exploit forgotten policies for privilege abuse or persistence. Audit, remove, or re-link to stay secure.
#DelaSecurity#DelaIEM#ActiveDirectory#IdentitySecurity