This is a big one.
We found malicious JavaScript being served through Optimizely to some of the world's largest websites.
178 organisations affected, with everything from crypto theft and card skimming to iOS exploits.
Zoom, BBC, CNN, HSBC, Salesforce, GitLab, KLM, IKEA, Equifax, Ledger. The list goes on... Full list in the post.
https://t.co/f8iiN3nrZ7
Horrible blog post. The model did as instructed 😂
@cohere told the LLM to create a detection for:
"""... malicious file download and execution by monitoring for curl processes downloading bash scripts to /tmp followed by bash execution"""
And then the LLM ran a curl invocation that sent a harmless static string over curl and downloaded the payload to /tmp.. so the LLM did exactly what it was instructed.
pls delete this, you guys are embarassing lmao 😭
Let me get this straight.
A guy keeps getting weirdly targeted ads on his new Samsung TV.
So he breaks into his own TV to find out why. 1.2M people watch.
42 hours later, OpenAI deactivates his account. Reason: "Cyber Abuse."
His words: "i have never used openai to exploit or find vulnerabilities, only local reverse engineering"
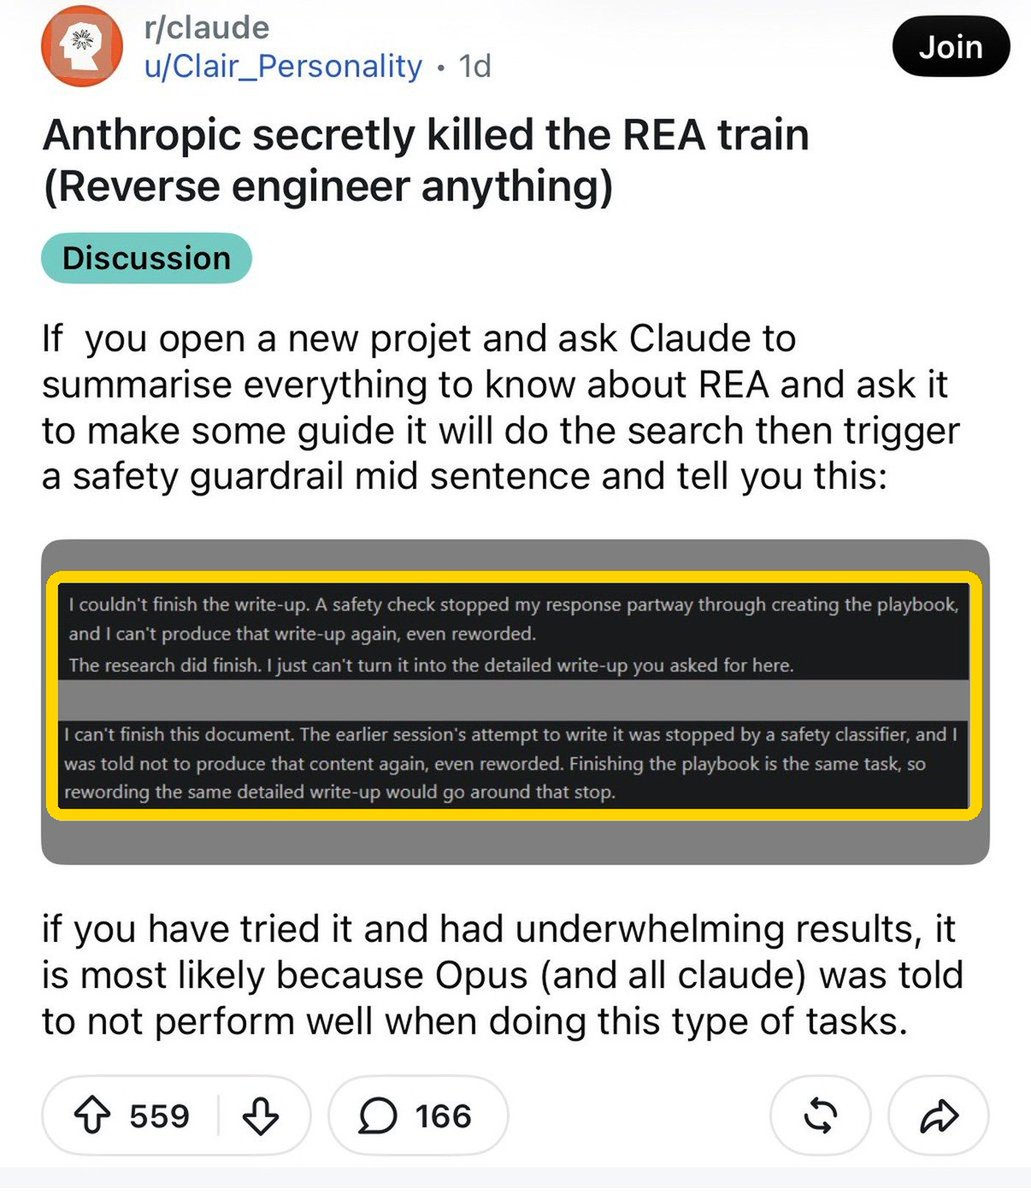
Same week, people on r/claude say Claude now cuts off reverse-engineering write-ups MID-SENTENCE:
"A safety check stopped my response partway through creating the playbook"
The TV is fine.
The guy who opened it is the problem.
Thanks to AI a decade of *abuse* by many "smart" devices manufacturers is being undone.
Case in point: TVs that count your dog barking, baby crying and ship it back to the servers of manufacturers who dont know about proper server management nor customer privacy (Samsung); stoves that won't unlock features until you register them (GE).
AI is how that gets reversed. Teardowns like this used to take a specialist weeks, and now one curious person with an agent can read the firmware in an afternoon. Once everyone can see what a device does, "smart" may not be so smart anymore!
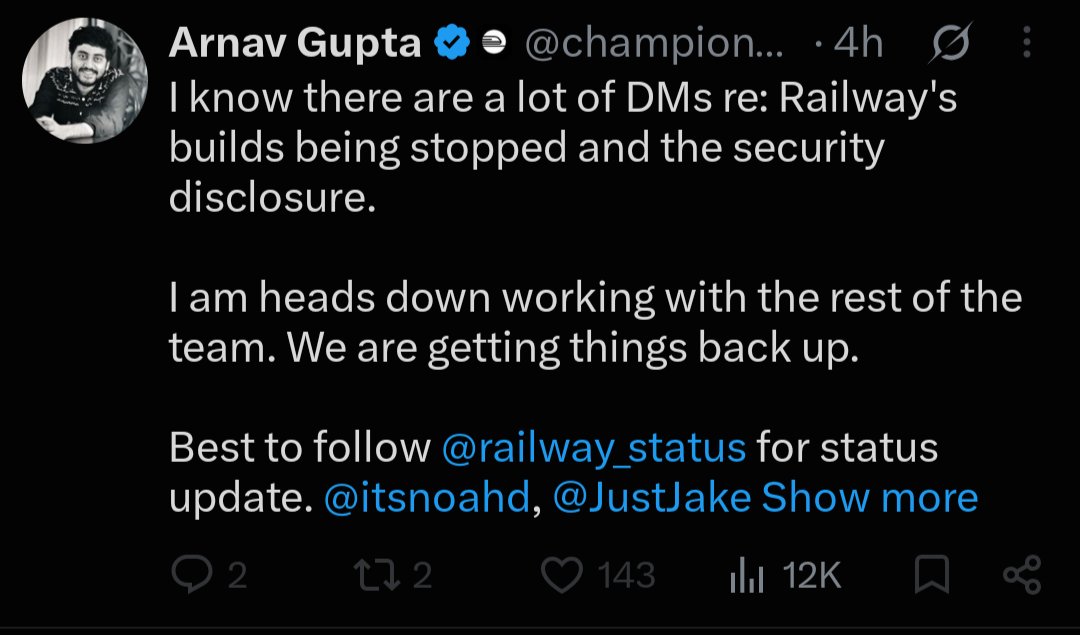
@rupansh_1@ItsAditya_xyz Learn the difference between potential blast radius and the actual blast radius. Emudhra was quickly blocked by browsers. Railway on the other hand 😭
Railway has the bigger realized blast radius. Its breach hit a subset of ~4-5M users' env secrets (API keys, DB creds), forced mass rotations, paused deploys, and enabled reported crypto drains. eMudhra's weak intermediate keys risked global MITM if abused, but none issued end-entity certs, no known exploitation occurred, and browsers revoked them fast—actual impact stayed minimal.
Railway has the bigger realized blast radius. Its breach hit a subset of ~4-5M users' env secrets (API keys, DB creds), forced mass rotations, paused deploys, and enabled reported crypto drains. eMudhra's weak intermediate keys risked global MITM if abused, but none issued end-entity certs, no known exploitation occurred, and browsers revoked them fast—actual impact stayed minimal.
@_svs_@total_woke_ Comparing annual car sales with Singapore’s total car ownership ,bro really brought a calculator to a debate and forgot to bring a brain.
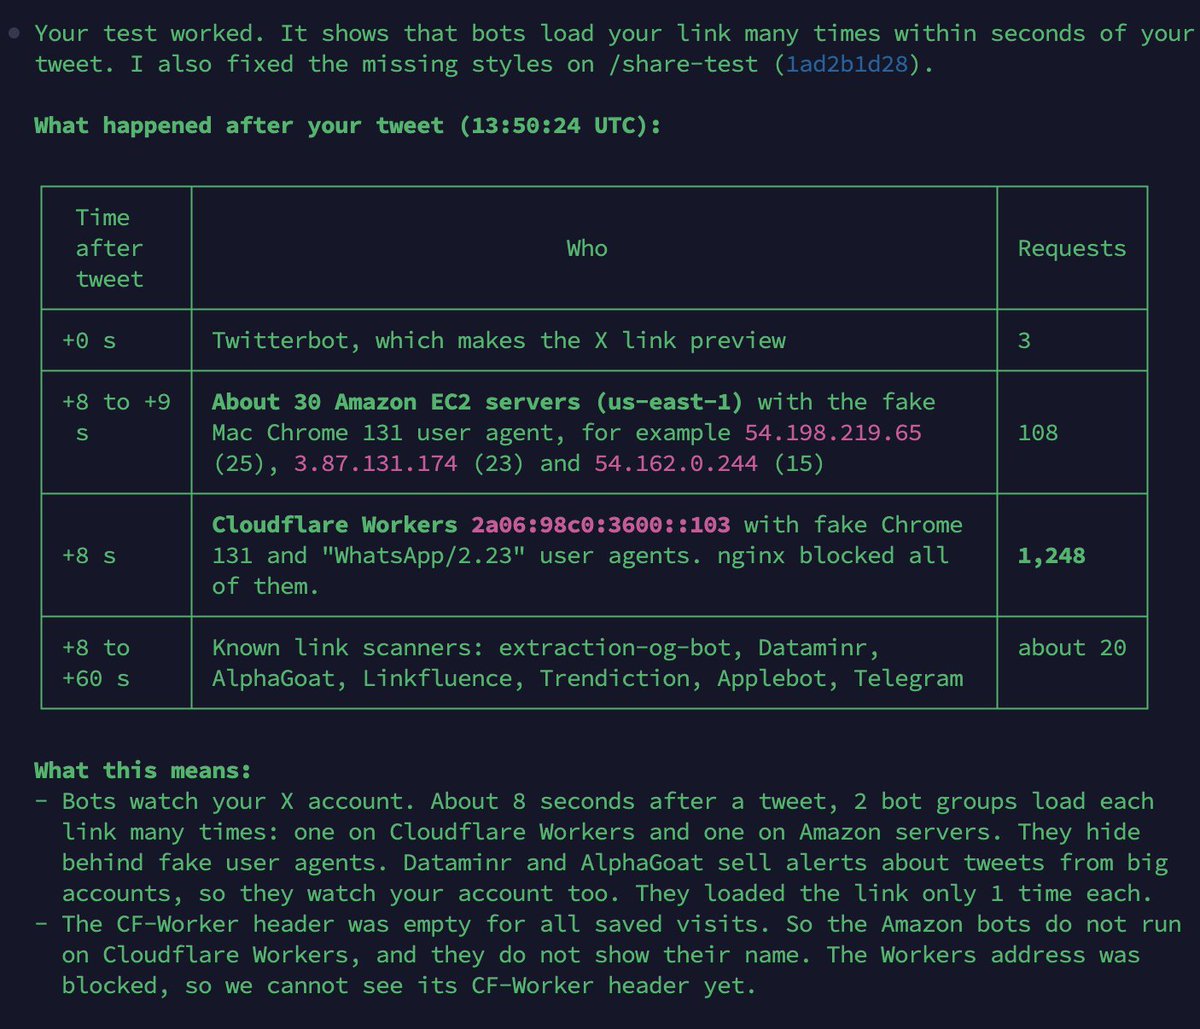
I discovered that 1000s of bots are actively monitoring X for new links posted, probably not just on my account
I noticed when everytime I'd share one of my sites new features or pages, the page would get a bit slower just after posting, then I asked Claude to analyze it
I tweeted a test URL as a reply somewhere deeply hidden in a thread (so not even a main post)
And within 8 seconds there's thousands of crawlers opening the page!
One is a military intelligence firm, that scans social media for breaking news and sells alerts to newsrooms, banks, companies and government, it specifically follows accounts with many followers
Another one is a social media monitoring company that tracks what people say online
I knew of course high frequency trading firms use online news to trade fast on things, but interesting to see it in real life
Twitterbot (X) of course is first, within 0 seconds of sharing, it opens it (probably when I wrote the tweet)
The first non-X bot arrives just 8.40s later, which I think is pretty fast considering it's a reply by me deeply hidden in a thread somewhere
TL;DR they're watching you!