Day 6 of #100DaysOfCode
Today I went deep into completing a resume layout I found online, and honestly, it taught me more than I expected.
While building it, I spent a lot of time working with HTML list tags (ul, ol, li) and understanding how they’re used in real projects.
Are you a beginner in Cybersecurity struggling to understand Linux?
I just published detailed notes on Mastering Linux Fundamentals.
Perfect for anyone building a solid Linux foundation.
🔗 https://t.co/TGjUCsBG9W
#Linux#Cybersecurity#TryHackMe#LinuxFundamentals#InfoSec
Happy New Month!
Knowing the right network ports helps you troubleshoot faster and secure systems better. Each port has a specific role.
#Networking#Cybersecurity#SysAdmin#ITSupport
Day 63 Hands-On Practical: Nmap scan types, OS & version discovery, port filtering, and outputs
completed a pen test for a client, focused on active reconnaissance using Nmap.
#Pentest#Nmap#VulnerabilityManagement#InfoSec
Day 60 of Learning:
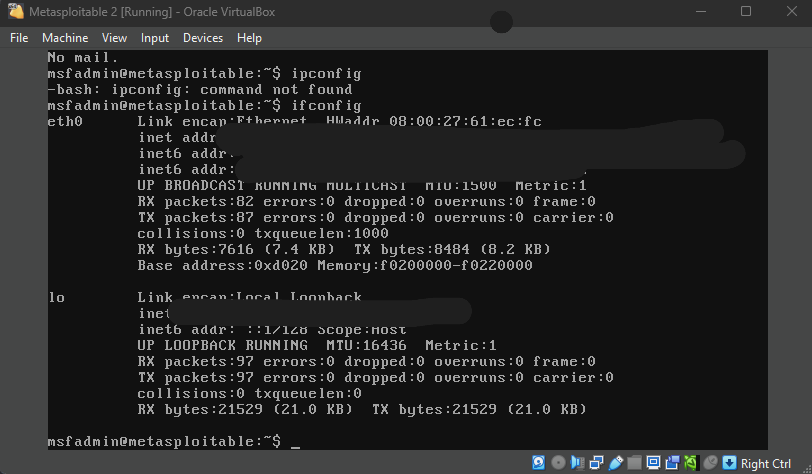
I’ve been applying hands-on reconnaissance techniques using open-source tools and platforms. The goal: practice structured information gathering and validate how different tools complement each other.
#Recon#Cybersecurity
Day 58 of Learning:
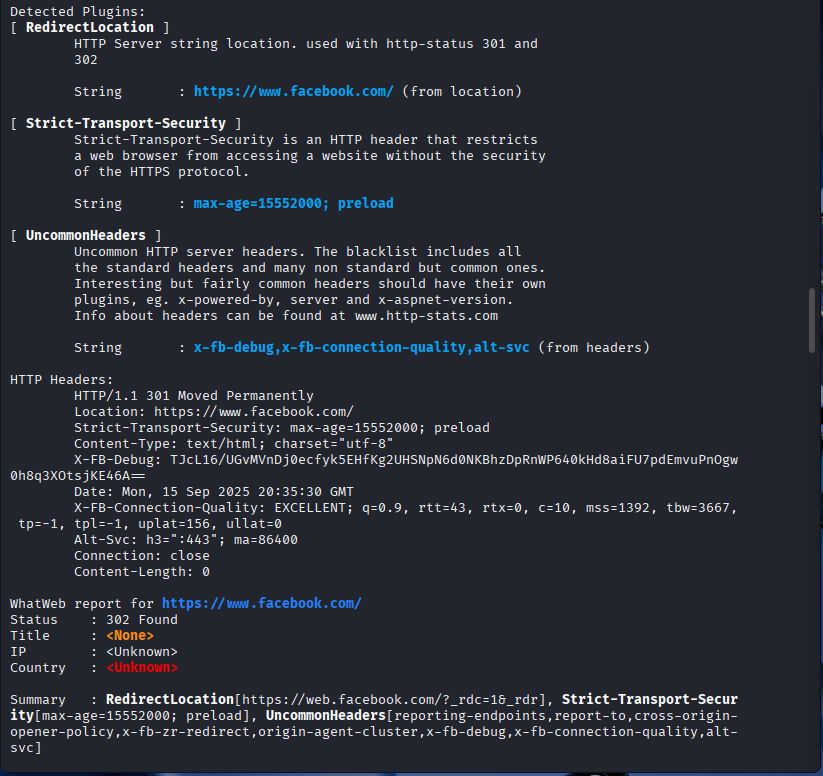
I explored WhatWeb in stealthy mode as part of hands-on learning (not authorized reconnaissance).
It revealed passive signals such as:
🔵 Tech stack clues
🔵 Headers & banners
🔵 Third-party integrations
#Cybersecurity#EthicalHacking#InfoSec#WebSecurity
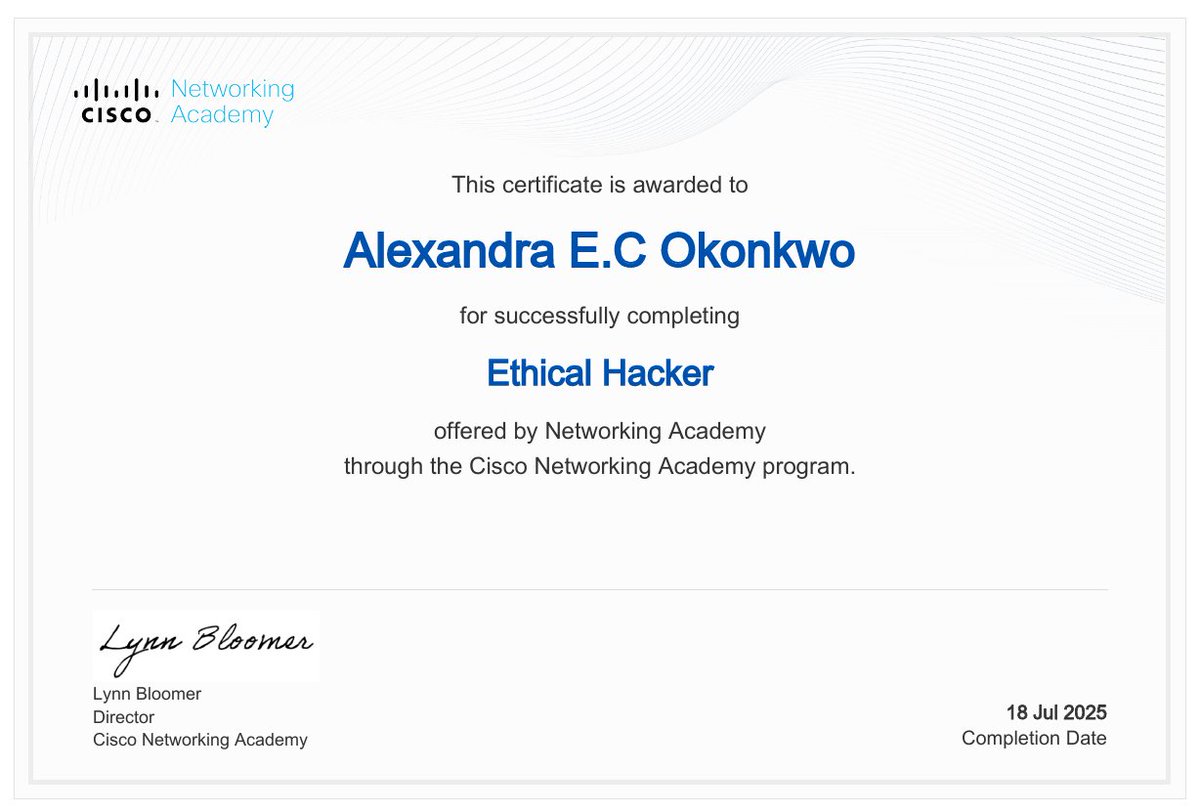
I’ve officially completed the @CiscoNetAcad Ethical Hacker course and earned the certificate 🎉
It built a solid foundation in ethical hacking and offensive security.
Excited to keep learning and growing in cybersecurity.
#CyberSecurity#EthicalHacking#Cisco
Day 57: Post-Exploitation, Persistence & Evasion
Today’s focus in my ethical hacking journey was on what happens after gaining access to a system: staying in, moving around, and avoiding detection. 🧵
#EthicalHacking#RedTeam
Day 56: Penetration Testing Tools & Exploit Code Analysis. ✍️
Today, I focused on understanding when, why, and how different tools are used across four major categories of a penetration test.
#Cybersecurity#LearningInPublic
Day 55: Understanding Scripting Logic in Cybersecurity.
Today was all about the fundamentals of scripting and how they tie directly into cybersecurity tasks like automation, analysis, and tool building. 🧵
#CyberSecurity#BlueDotLogs#Day55
Day 53–54 of My Cybersecurity Journey: From Vulnerability Discovery to Strategic Remediation
During a pentest on a vulnerable DVWA server (10.6.6.13), I shifted focus from just scanning to what separates beginners from professionals:
Let’s break it down. 👇🧵
Day 52 of My Cybersecurity Journey �� The Power of Reporting:
Let’s talk about something that separates script kiddies from professionals.
How we report findings after a penetration test.
It’s not just what you find - it’s how you communicate it.🧵👇
#CyberSecurityJourney
Day 50 – 51 of My Cybersecurity Journey: Post-Exploitation, Persistence & Lateral Movement.
Happy New Month, everyone! 🫂
Initial access is the start. The real challenge begins with maintaining control, moving across systems, and avoiding detection.
Let’s break it down. 🧵👇