SQLi on API Key
Authorization: Bearer x' OR (SELECT pg_sleep(3)) IS NOT NULL-- -
Inject into the Bearer, pre-auth. Don't ever prefix with "sk-".
Dead key, instant 401. SQLi hangs 3s, then 401.
Swap the sleep for a CASE and read everything char by char.
(CVE-2026-42208)
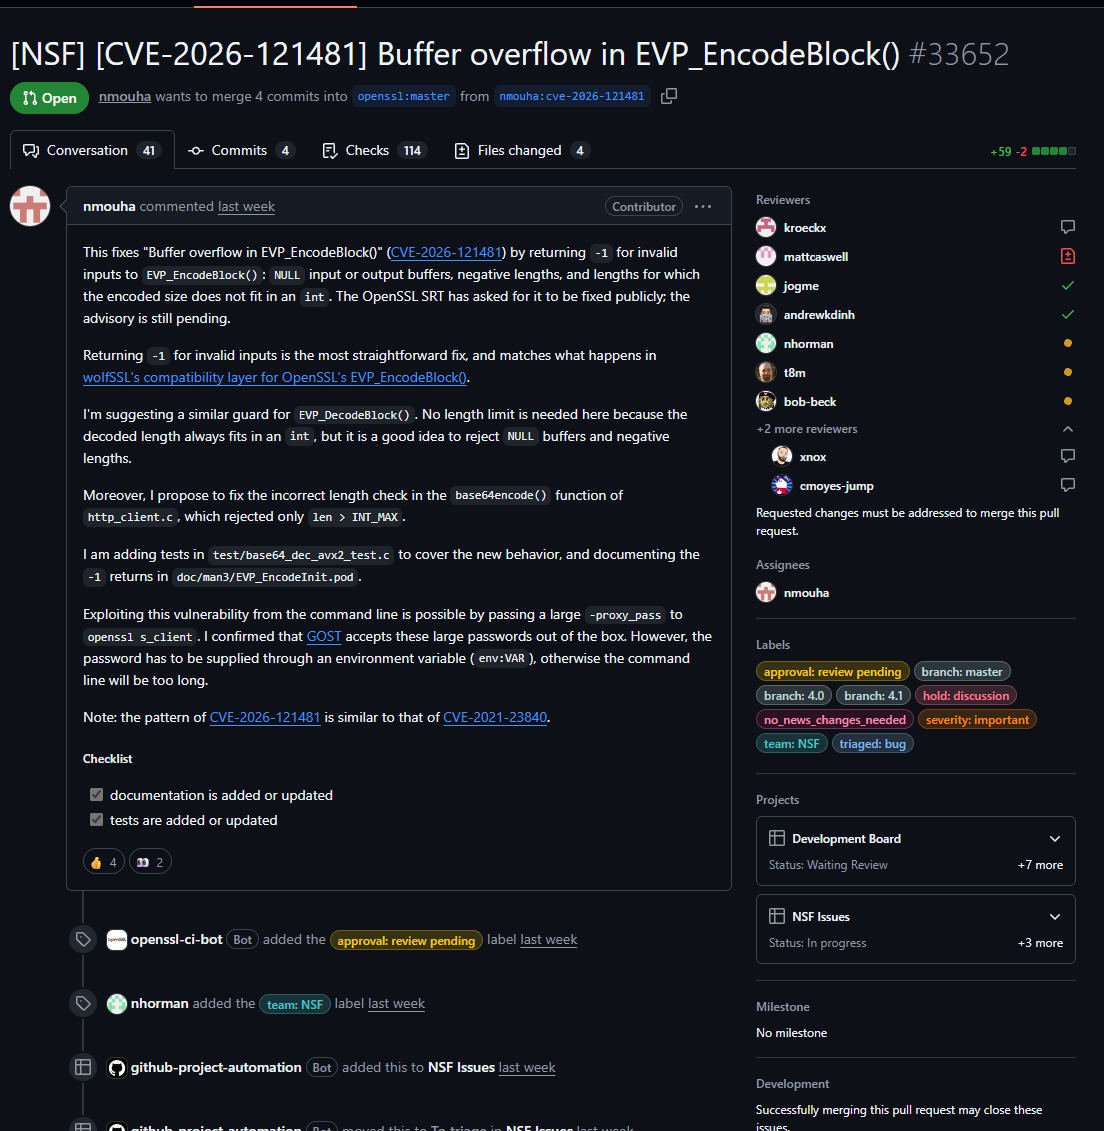
OpenSSL flaw CVE-2026-121481 scores 9.8, but exploitation appears highly constrained.
The Base64 buffer overflow requires unusually large inputs (~1.6GB), with no practical remote RCE demonstrated.
High CVSS ≠ high real-world exploitability.
https://t.co/SKm3DuVCfl
Wealth without the presence of another is merely cold, silent gold.
True worth lies not in accumulation, but in the shared gaze that gives life its meaning.
#grok#4u#explore
🚨 Java4Shell PoC released for critical OpenJDK vulnerability that could allow remote code execution; CVE-2026-114938
PoC: https://t.co/O1ti19WmDd
A public proof-of-concept has been released for Java4Shell, a critical memory corruption vulnerability in OpenJDK's Base64 decoder that could allow unauthenticated attackers to execute malicious code on affected Java servers.
Researchers have demonstrated remote code execution against Keycloak, Jira, Confluence, Jenkins, Artifactory, and PingFederate. Exploitation requires compatible x86-64 processors supporting AVX-512 VBMI.
CVSS: 9.2 Critical (v4.0)
Affected: OpenJDK 17, 21, 25, and 27 on supported hardware
Fixed: 17.0.21.1, 21.0.13.1, 25.0.5.1, and 27.0.1.1
The PoC includes a heap corruption reproducer, vulnerability scanners, detection rules, and a Docker testing environment. It does not include a complete remote code execution exploit.
‼️ BREAKING: Oracle is set to patch 11 Java vulnerabilities today — all potentially exploitable remotely without authentication.
Meanwhile, reports of a critical OpenJDK RCE flaw (CVE-2026-114938, CVSS 9.2) are raising alarms. Details remain unconfirmed.
What Java users need to know ↓ https://t.co/qb0pUMqTLe
URL validation holding you back?
Don't stress, we've got your back!
Our URL Validation Bypass Cheat Sheet has 200+ Payloads for all occasions!
Check it out: https://t.co/EvRuZGwFaN
#burpsuite#hacking#bugbounty#pentesting#cybersecurity
I built HexBrain: every publicly disclosed HackerOne report on one interactive map.
15,000+ reports by vulnerability class, weakness and program
Full write-ups: how each bug was actually found
405,000+ CVEs, exploited ones in red
Bypass and payload libraries
It's free and still early, so tell me what breaks or what's missing.
https://t.co/skpt737w3o
#bugbounty #infosec #bugbountytips
@elonmusk Sorry to say : Grok is extremely expensive. 🚩
And it's not doing security research. If you are not solving this issues your customer move to other platforms.
We've now paid out more than $1M in @muse bug bounties. That includes $300,000 to a security researcher who found the most critical bug we've seen in Muse. https://t.co/1PATDTtA6o
🧅 Tor2Tor: a simple tool for crawling an onion service and automatically capturing screenshots of the links it discovers
GitHub: https://t.co/ZKbu5Jl2nc
Give Tor2Tor an .onion URL and it will scrape the page, extract the available links, and capture screenshots of the discovered onion content over Tor.
Features include:
• Automated onion link discovery
• Screenshot capture
• Tor routing
• Linux and Windows support
• Docker deployment
• Firefox + Geckodriver automation
The project is useful for research, archiving, and quickly documenting onion-service content without manually opening every discovered page.
@galnagli I never used gemini carbon for bug hunting but I think it's good because Google have access to miljon of websites and articles. Most of the websites use Google tag and Google bot know exactly what source they need to train thire Ai. And also they have pro employees 😊
We are launching a PHP Capture the Flag challenge integrated with our Bug Bounty program to test our WAF protections. Security researchers are invited to bypass our defenses and capture the flag to help make the Internet safer. https://t.co/YzSYe7kbES