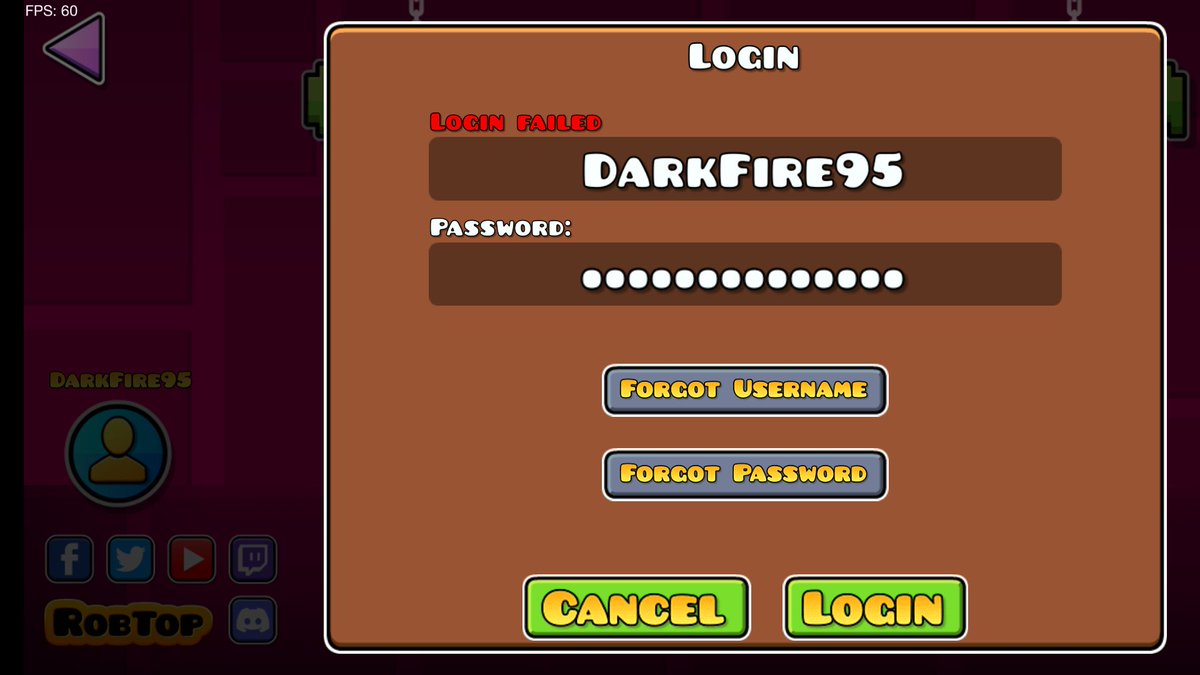
#GeometryDash The recently announced 9.2 PHP CVE is actually viable on GD. My personal advice would be to avoid logging in on the server for a while as @RobTopGames hopefully updates PHP ASAP.
The vulnerability is to an extend blocked by Cloudflare but it's not foolproof. For this reason I would not trust endpoints like login for a while which may leak your credentials if the exploit is used on the backend of Geometry Dash.