@ray_ban Today, a new, sealed RayBan Meta Wayfarer Gen 2 was found to contain an unknown photo dated 10 Oct 2025. Original JPEG EXIF shows: RayBan Meta Smart Glasses 2 Serial: 4****27 The box serial matching the EXIF. Was the device previously used? #RayBan#meta#privacy@Meta
The pattern: private data + untrusted content + external comms = the lethal trifecta, now exploited in the wild.
If you run LLM workflows and haven’t threat-modeled a single agent, you’re already exposed.
#CyberSecurity#AISecurity#PromptInjection#InfoSec#ThreatIntel
AI agents are now the attack surface and June 2026 made it undeniable.
In the last two weeks, attackers stopped targeting AI and started weaponizing the agents themselves.
Three incidents every security team should know 🧵👇
1.AutoJack a single malicious web page hijacks Microsoft’s AutoGen browsing agent and runs arbitrary code.
2.Gaslight (macOS) malware that hides prompt-injection strings to fool AI-assisted analysis tools.
3.Fake OpenAI tenants phishing employees into leaking data via chats.
@blrcitytraffic@hgatetrafficps The truck driver was rude to ladies and cannot rule out if he has intentionally hit the car driven by ladies. I request you to retrieve public CCTV. If intend is clear then please press criminal charges. Roads needs to be safe for #women drivers in #Bengaluru@DKShivakumar
@airtelindia@Airtel_Presence#Airtel has taken measures against spam calls on Mobile Numbers. How is Airtel India going to stop scam calls on Airtel Broadband landline? Lot of Airtel Customers started getting scam calls on airtel landline.
@Airtel_Presence New broadband scam has surfaced. Subscribers r getting scam call on airtel broadband connected landline and they are posing as customer service of airtel and asking to install remote access software to hack. Hw are these ppl getting customer data? #Airtel#india
PEEPER is a great tool for digital forensics investigators to work with large volumes of screenshots or document images. It reads text from images in the source directory and searches for terms specified by the user.
https://t.co/lcXvFs7zRg
#CyberSecurity#digitalforensics
- How to verify phishing websites when cybercriminals prefer to use SSL certificates to disguise phishing scams as legitimate sites?
https://t.co/uaSs6ztj10
- Active Directory Ntds.dit Forensics.
https://t.co/1PXp2WtFRv
- Forensic printer tracking codes.
https://t.co/TMS8Ju1crJ
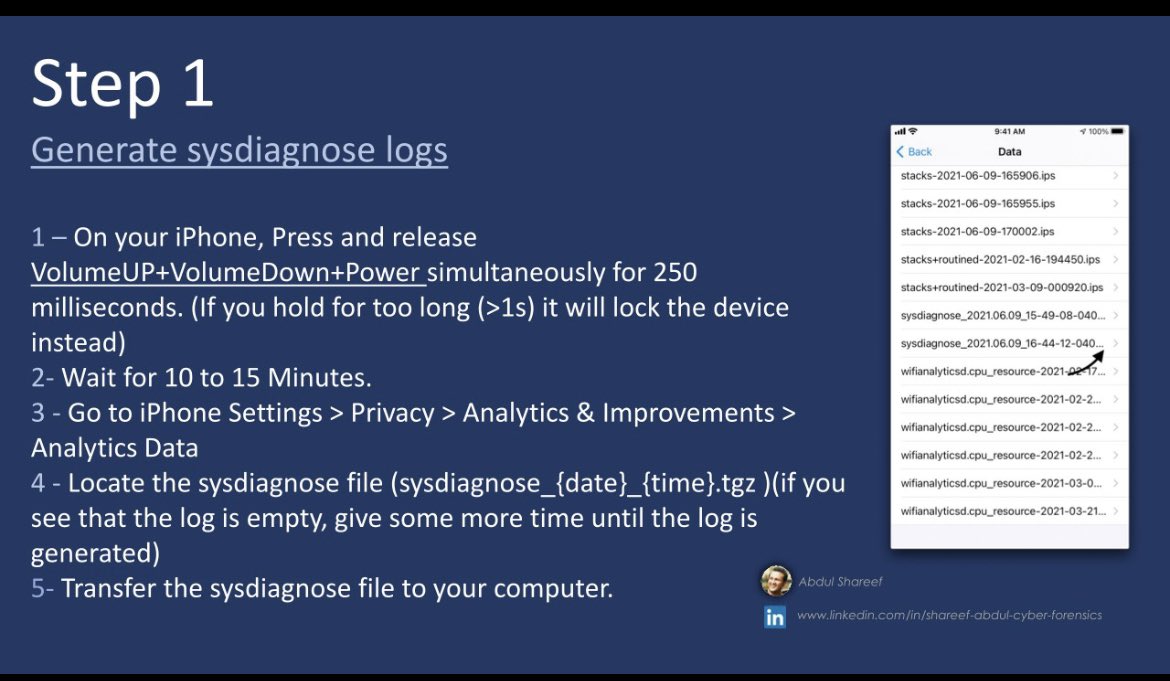
- SANS iOS cheatsheet
https://t.co/2aRxVqkqDr
- mvt-project
https://t.co/0W3i7hkikP
- Google Reverse Location Data - Best Practices.
https://t.co/JNezQENQBr
- GHunt - Investigate Google Accounts with emails.
https://t.co/llAP2ljjbD
…
#infosec#CyberSecurity
- NTFS timestamp changes chart during different operations in Windows OS ($MFT).
https://t.co/frWtTNCQyX
- Digital Evidence Collection Cheatsheet
https://t.co/Di1Tcxa0YF
- PhotoDNA using machine learning.
https://t.co/xrTK8hTetU
(R-I-T-A) Real Intelligence Threat Analytics.
An open-source framework for detecting command and control communication through network traffic analysis.
Source : https://t.co/P0rkv73se4
#CyberSec#ThreatHunting#threatintelligence
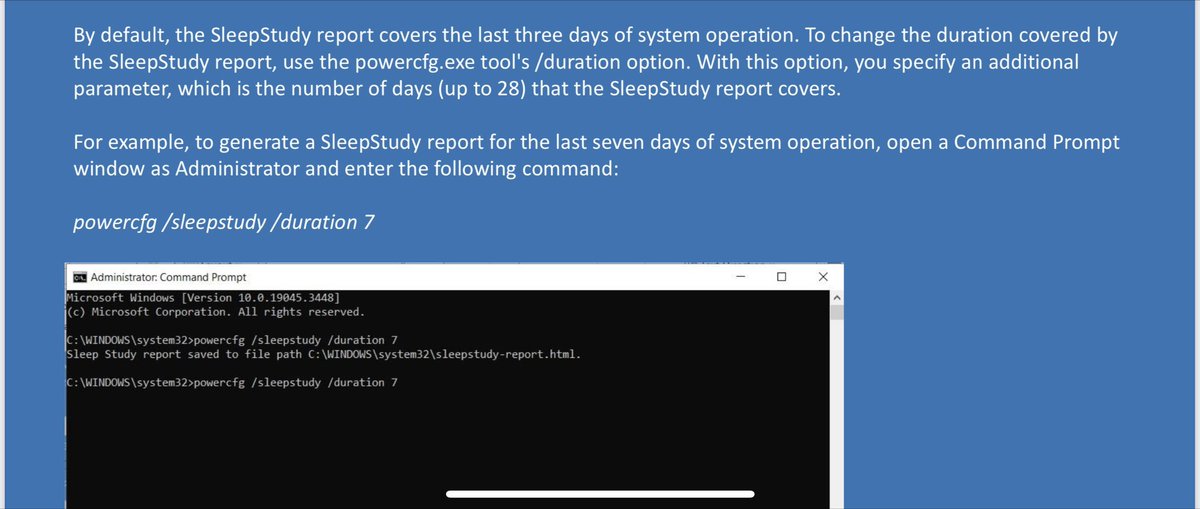
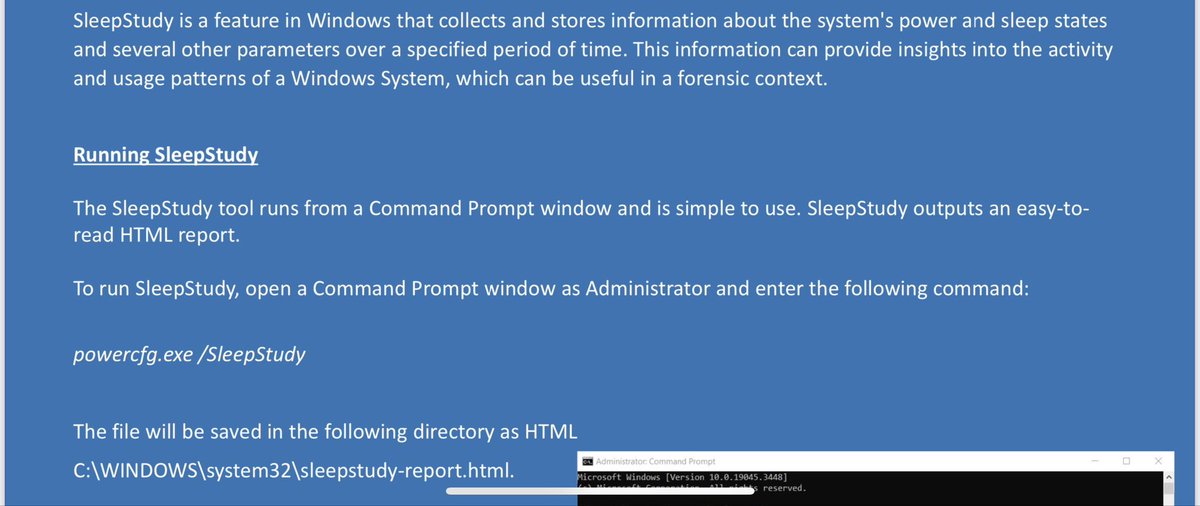
Windows SleepStudy Report for Forensics Analysis.
A great place to look for forensic timeline reconstruction and collect information such as User Activity, Battery and Power Information, Device Usage Patterns, Investigating Anomalies etc.,
#cyber#cybersecurity#Windows
@nabilajamal_@nabilajamal_ USB ports and phone charging cables are the most common devices used in juice jacking attacks… means you can say “dont use USB cable to connect to unknown USB port”. So there are mistakes in your tick mark points.
@hansmeths@etihad Can’t completely blame the employee for data leak. Even with baggage tag or boarding pass anyone can access the airline retrieve booking page with PNR and get personal details such as email ID and mobile. Airline should close this gap. I have posted several article on this.