Your coding agent keeps retrying the same broken fix.
Sondr records what you and the agent both ran, briefs it next session, and warns when you're looping.
Linux. Local. It never runs a command itself.
https://t.co/Bii2NxyLtp
#linux#bash#debian
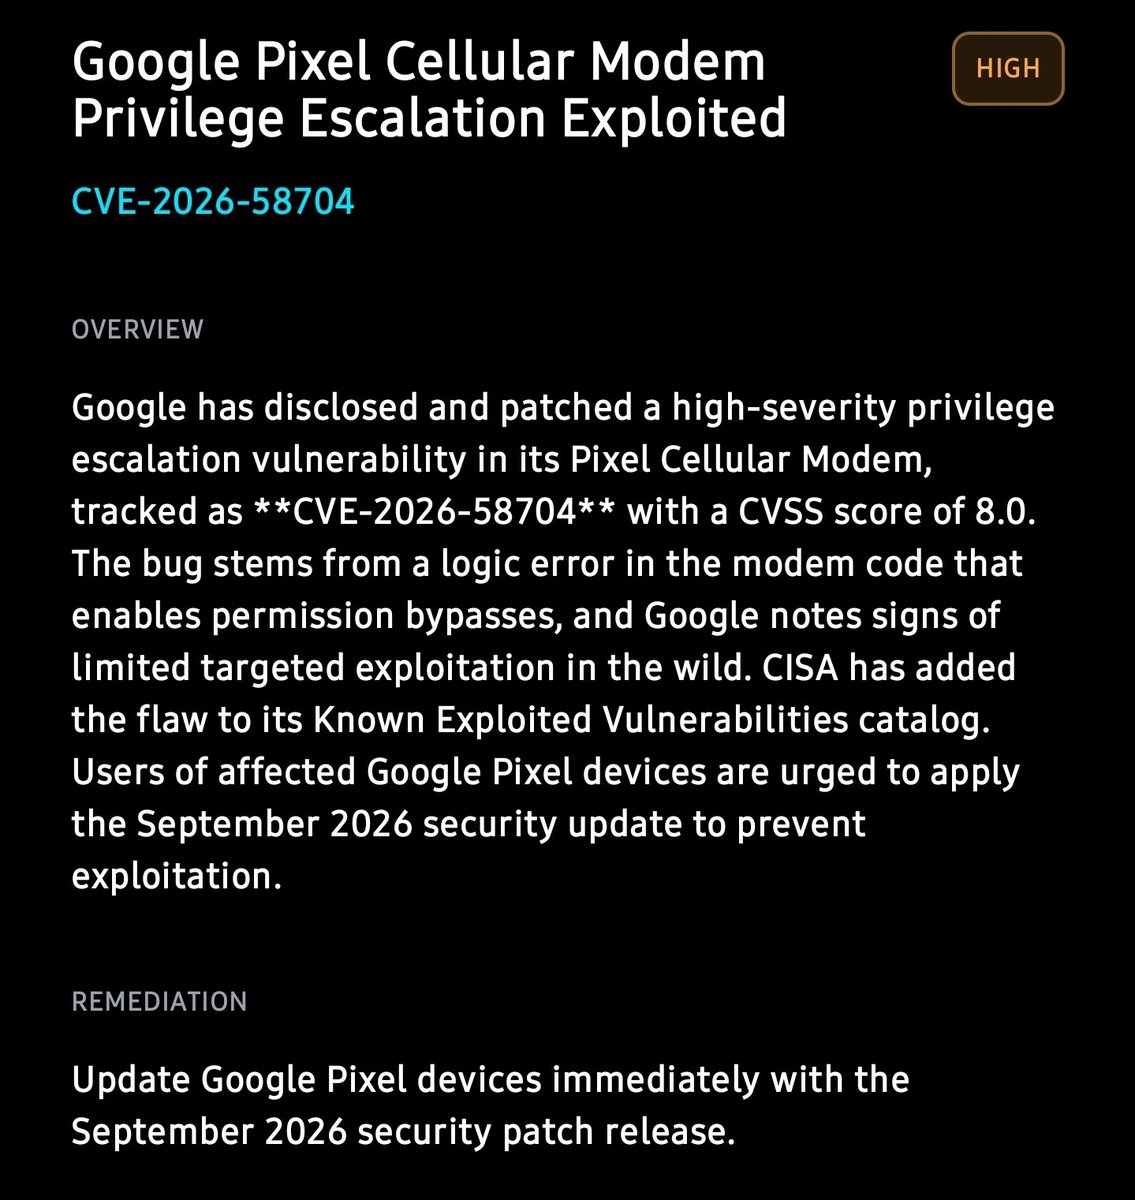
Limited targeted exploitation is the phrase that should make Pixel owners check their update status today. This isn't mass exploitation yet, but CISA doesn't add things to KEV for fun.
CVE-2026-58704 (CVSS 8.0): Google patched a privilege escalation flaw in the Pixel Cellular Modem with signs of limited targeted exploitation. CISA added it to KEV. If you're on a Pixel, install the September 2026 security update now. #MobileSecurity#Android
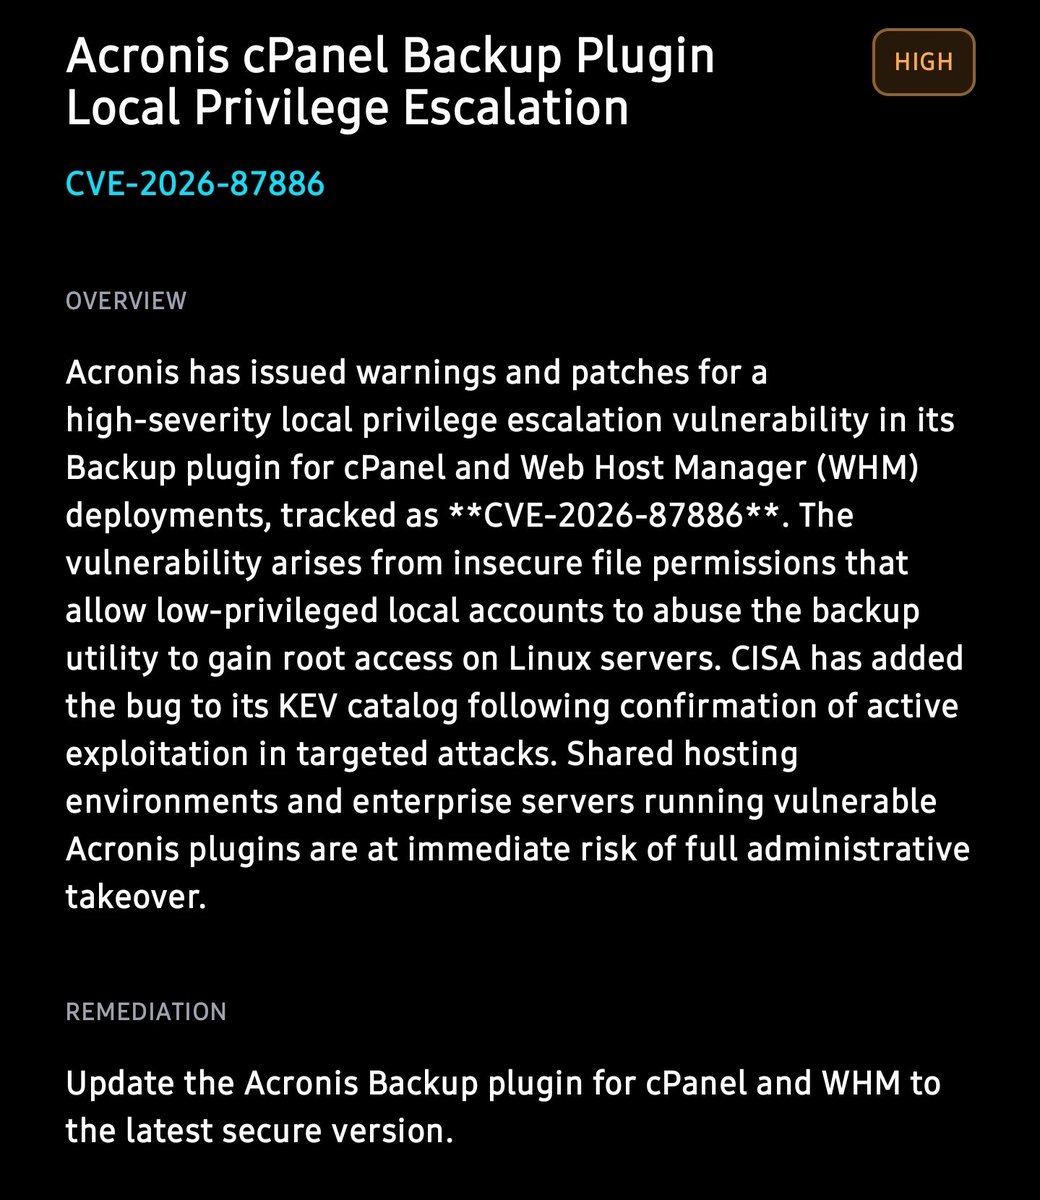
A backup tool becoming the path to root because of file permissions nobody double-checked. If you're on shared hosting running Acronis for cPanel/WHM, this is worth confirming today, not next maintenance window.
CVE-2026-87886: local privilege escalation in the Acronis Backup plugin for cPanel/WHM lets low-priv accounts abuse insecure file permissions to get root on Linux servers. CISA confirmed active targeted exploitation. Shared hosting environments, patch now. #InfraSecurity#LPE
This Cisco email gateway bug just got reclassified as worse than first reported, now SQL injection plus command execution, max CVSS. If you were waiting on this patch, that window just got a lot smaller.
Update: CVE-2026-76461 in Cisco Secure Email Gateway now confirmed at max CVSS 9.8, enabling SQL injection AND arbitrary system commands, not just RCE. CISA's BOD 26-04 deadline stands. If you haven't patched yet, this just got worse. #EmailSecurity#CISA
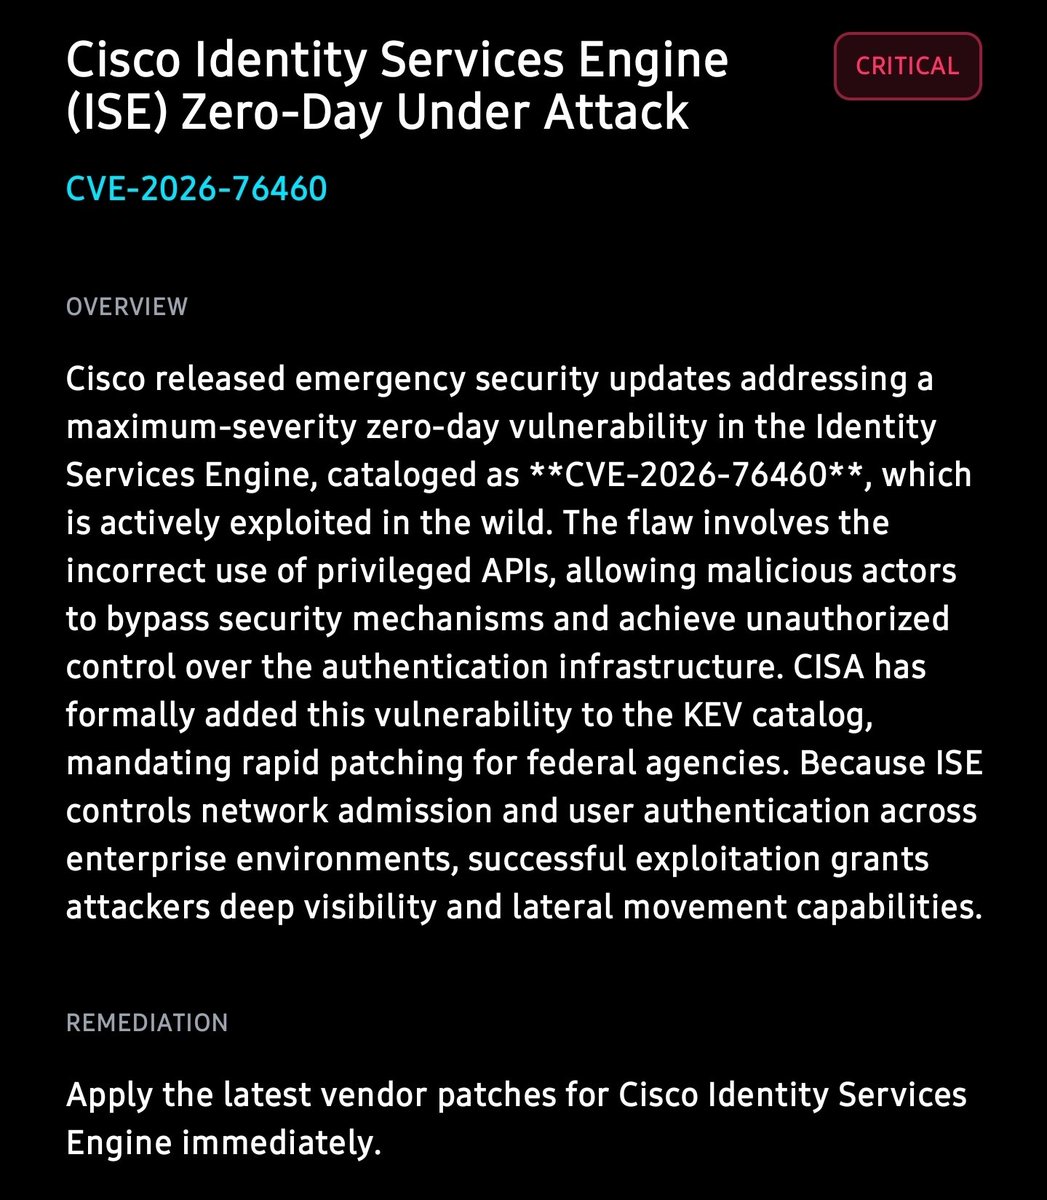
ISE decides who gets on your network and who doesn't. An active zero-day that hands attackers control of that decision layer is about as bad as network security incidents get.
CVE-2026-76460: Cisco ISE zero-day under active exploitation via privileged API misuse, bypassing security controls for full auth infrastructure takeover. CISA mandated rapid federal patching. ISE controls network admission org-wide, patch immediately. #NetworkSecurity#Cisco
6,000+ stores running a plugin that now lets anyone drop a PHP backdoor without logging in. If WooCommerce Wholesale Lead Capture is installed anywhere in your stack, go check your web root today, not eventually.
A critical flaw in WooCommerce Wholesale Lead Capture (6,000+ installs) is being exploited for unauthenticated file upload and RCE via PHP backdoors. Wordfence is tracking live exploitation. Update the plugin and scan web roots for rogue PHP files now. #WordPress#Ecommerce
Root access via how your email gateway parses messages, no login needed. CISA didn't just flag this, they issued a binding directive over it. If Cisco Secure Email Gateway is in your stack, don't wait on this one.
CVE-2026-76461: Cisco Secure Email Gateway zero-day under active exploitation. Unauthenticated attackers get root-level commands via malformed email parsing. CISA added it to KEV under BOD 26-04. Patch and inspect for prior compromise now. #EmailSecurity#CISA
Forging your own admin token because signature verification wasn't actually checking signatures properly, that's the kind of bug that makes JWT feel less trustworthy than people assume. Patch WSO2 now if this is in your stack.
CVE-2026-5430: WSO2 API Manager JWT signature verification flaw is under active exploitation. Attackers forge admin tokens for full account takeover of API management platforms. Treat any unpatched instance as an active breach. Patch and audit access logs now. #APISecurity#JWT