🚀 Want access to Immunefi Studio?
I’ve got 4 invitations available for security researchers who are serious about getting started.
Here’s what you should know before requesting one:
🎁 3 months of Immunefi Studio included with your invitation.
💳 $300 in credits required to activate your account. The subscription is already covered.
⏰ 20 hours to activate once you receive your personal invitation link.
🔄 Any invitation that isn’t activated within that window will be reassigned to someone else.
🤝 Full transparency: I receive 300 credits for each successful referral.
A small request: Please only reach out if you’re genuinely interested and ready to complete the $300 purchase. I’d rather see these invitations go to people who will actually use them.
💬 Want one? Drop a comment below or send me a DM.
First come, first considered. Only 4 spots available!
#Immunefi #BugBounty #Web3Security #SecurityResearch
Immunefi Studio opens November 18, the same day the @base audit competition begins.
Here's what you get:
✦ Signals: see how programs respond, pay, and how crowded they are
✦ Instascope and Blueprint: see the scope as code and a map of the protocol
✦ Alerts: get notified when scope or code changes
✦ Workspace: manage your cases and tasks in one place
✦ Studio Review: get feedback on your report in about 3 minutes. Get a green verdict and submit directly to the program with no fee and no accuracy penalty if the report is closed
✦ Audit competitions: everything set up for you from day one, starting with @base
✦ Studio MCP: give your AI agents access to all of it
And we've already seen what Studio can do.
During the beta, researchers who checked most of their reports with Studio Review had:
✦ 2.5x higher valid report rates
✦ 63% fewer reports closed as duplicates
But Studio isn't just about writing better reports. It's also about knowing where to hunt.
"It really help me a looooot to choose the next target very wisely, its really useful and help me really good to know where to put my focus and time on." — @ZeroK_____
So, how do you get access?
Studio is invite-only. Access will grow through researchers inviting researchers they trust, starting with our Ambassadors.
Already on the waitlist?
Some of you got early access and helped us build Studio. But demand was much higher than we could handle during beta.
Now we're opening the doors to more researchers.
Want access?
Comment "." below.
Our Ambassadors will look at the comments first when invites open on November 18.
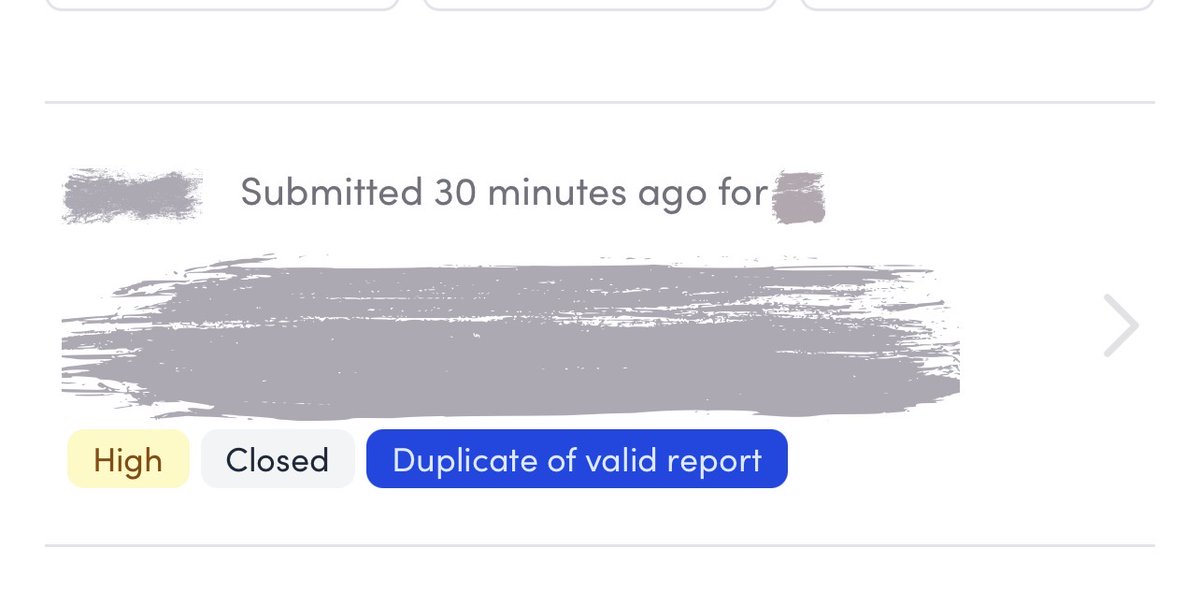
Imagine paying $50 to report a real security vulnerability, only to hear:
“Valid bug, but someone got here first.”
Thanks for the research. We’ll keep the $50. 😂
Should valid duplicates qualify for a refund?@immunefi
Offline keys aren’t enough if display and signing disagree. I found a high-impact flaw in a Bitcoin signer: a crafted PSBT could show the expected transaction while signing another. No physical access or seed extraction. Patched upstream; full write-up after disclosure.
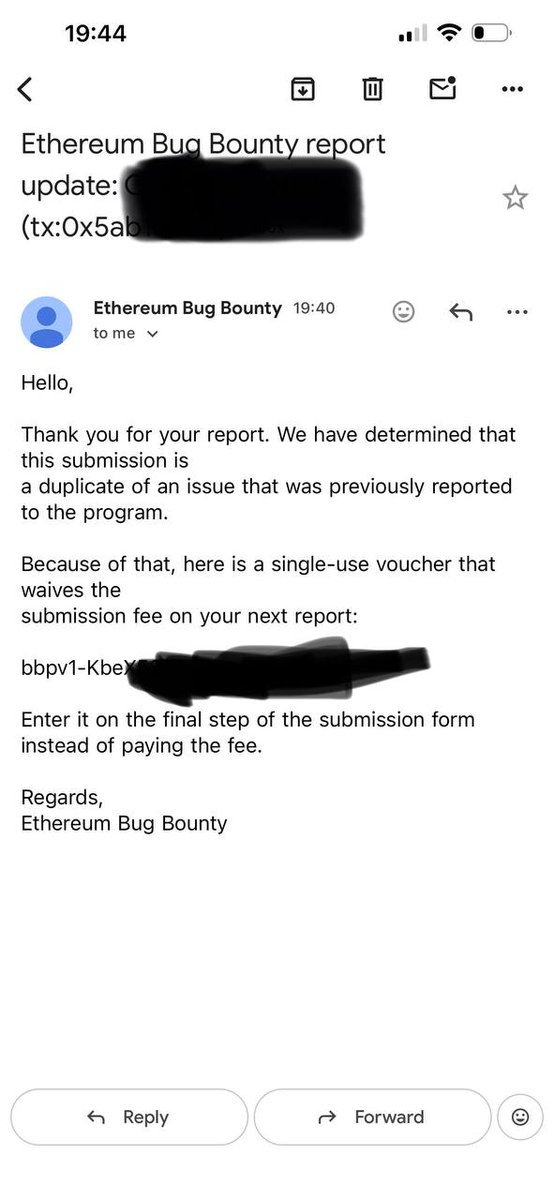
Slightly painful, but also reassuring: my Ethereum Bug Bounty submission was closed as a duplicate of a previously reported issue.
No bounty this time, but “duplicate” is still useful signal — the bug class and attack path I independently reached were real enough to already exist in the program.
Back to hunting.
My $VENTRA allocation: 10,620 $VENTRA
Every Arbitrum One transaction I already made counts toward it. Check what you are owed:
https://t.co/MzdrdYhIZk
@ventranxyz
@Blockstream Yeah 15% is a lot, but I’m only person in this room who believes theirs proposal was 1500$ reward, low severity, because they don’t think this bug is critical
First of all, poor hygiene of code in your protocol is the main reason you got hacked. There are so many more concerning issues in your elements codebase but instead of learning your lesson and going back to work, you’re complaining about it. As a matter of fact, I disclosed an encrypted vulnerability report days ago to your team and I still haven’t heard back, maybe instead of tweeting nonsense like this, go look in your inbox.
Second of all, open sourcing in blockchain field is so common that using it as an excuse is laughable (we got hacked because our codebase was open sourced). What a joke.
Unfortunately users had to pay for your negligence and carelessness for security, but instead of taking accountability, you come and post something like this acting as a victim like nobody else was going to exploit it soon or later anyways. Those hackers should be thanked for their work, if North Korean hackers got to your protocol you wouldn’t have even seen a cent of the 85% that you have today.
Protocols don’t get hacked by accident, most times it’s always projects with this exact tone and victim mentality that this happens to.
I’ve seen many that actually cared about their security, they paid big bounties and actually had a bounty page and they still got hacked. Those are the only protocols that I would feel bad for because they did all they could do, so they would deserve a break and some credit, and they still come and take accountability and apologize to their users.
The norm in blockchain cybersecurity has always been 10% of the damages, in this case they already returned 85%, if you’re gonna call them criminals, what was the point of them returning the 85%? Could’ve been criminals with all of the money.
I'm sharing the process, not the exploit — the fix is out and I won't put users at risk.
If you're a researcher weighing disclosure to @rainbowdotme, know how this went. Happy to be corrected publicly if they make it right. Receipts available.
In April I responsibly disclosed a security vulnerability in RainbowKit — @rainbowdotme's open-source wallet-connection library used across thousands of dApps.
They confirmed it. Their CTO approved a bounty. Then they went silent and never paid.
Timeline 🧵
Since then: nothing.
Two deadlines I set came and went. Every follow-up now gets an automated "check our Knowledge Base" reply. The amount was never even communicated.
It's not about the payout size — it's that they approved it and ghosted.