The cybersecurity industry has no shortage of challenges. But what does working on the frontlines actually teach you?
Our Founder, @0ctac0der joins @AccessGrantedHQ Access Granted to share his journey, experiences, and takeaways from the field.
Tune in to the full episode: https://t.co/p0ARaVcSEz
#CyberSecurity #ApplicationSecurity #AIinsecurity #ethicalhacking
🎙️ Episode 8 of Access Granted is LIVE!
@0ctac0der explores what separates a skilled pentester from a tool operator in the age of AI — with AI-assisted pentesting, real-world methodology & skills AI can’t replace
@EnciphersLabs@vantag3point
🎥 Watch → https://t.co/iIJAjFilqk
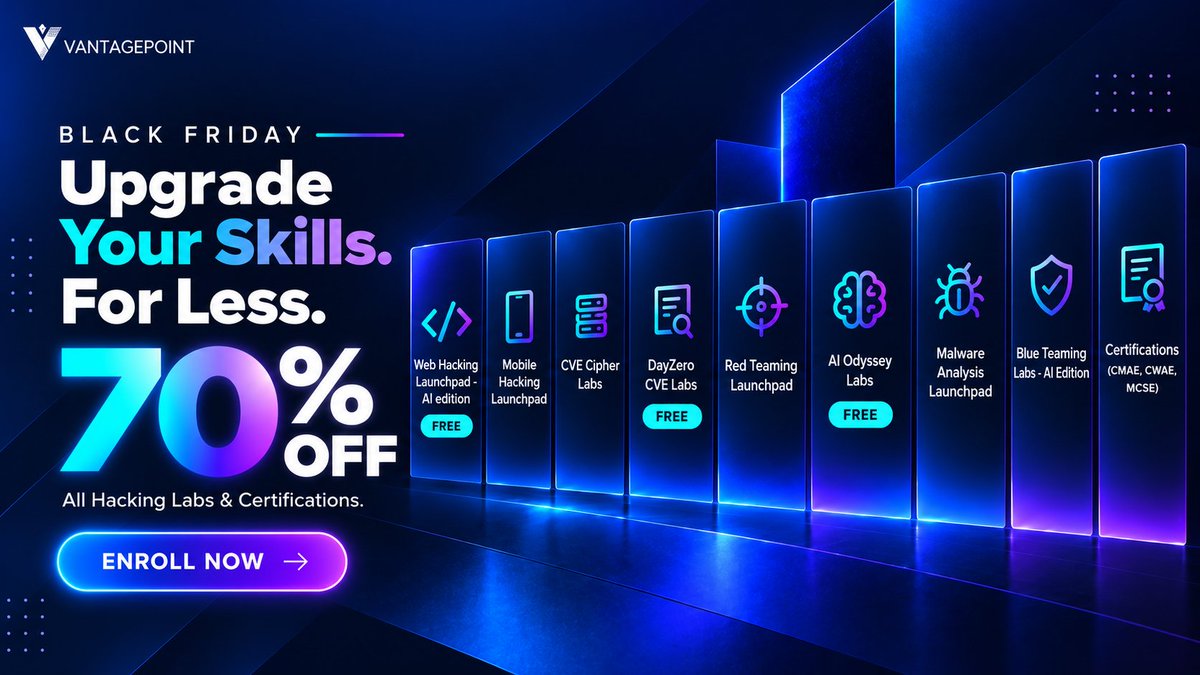
Get 70% OFF all hacking labs and cybersecurity certifications this #BlackFriday.
Build practical skills. Earn industry-recognised certifications. Practise in real-world environments.
👉 Explore: https://t.co/PxR6qutpg7
#Cybersecurity#EthicalHacking#OffensiveSecurity
One sale. Every attack surface. More ways to sharpen your skills.
This Black Friday, get 70% OFF all VantagePoint hacking labs and cybersecurity certifications.
Explore the Sale: https://t.co/PxR6qutpg7
#BlackFriday#Cybersecurity#EthicalHacking#OffensiveSecurity
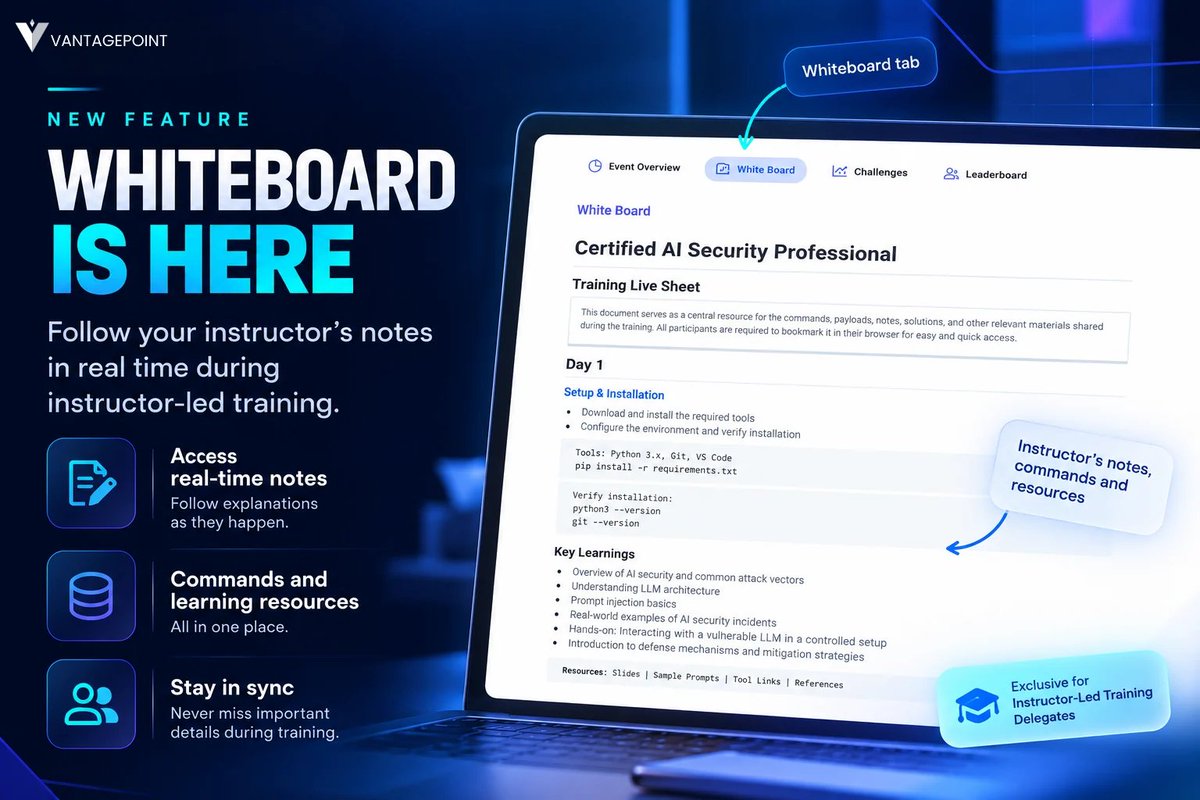
Introducing the Whiteboard Feature!
Delegates can now access instructor notes, commands, payloads, and shared resources in real time during instructor-led training.
Your training resources, all in one place. https://t.co/PxR6qutpg7
#CyberSecurity#NewUpdate
🚨 Episode 8 of Access Granted with @0ctac0der drops soon!
If AI can recon, test & suggest attacks, what still separates a real pentester from a tool operator?
We explore AI-assisted pentesting, methodology & the skills AI still can’t replace.
@EnciphersLabs@vantag3point
Your next #cybersecurity upskilling comes with 70% OFF.
From hands-on hacking labs to industry-recognised certifications, #BlackFriday is the perfect opportunity to invest in your skills.
Make your next move count.
https://t.co/PxR6qutpg7
#EthicalHacking#OffensiveSecurity
70% OFF Black Friday Sale is officially live, enjoy the BIGGEST discount of the year across hands-on hacking labs and cybersecurity certifications- https://t.co/PxR6qusRqz
Ready to take your cybersecurity skills further?
#BlackFriday#EthicalHacking
VantagePoint now supports Multi-Factor Authentication!
Add an extra layer of security to your account using Google Authenticator.
A smarter way to keep your account secure🔒
Enable MFA today: https://t.co/PxR6qutpg7
#VantagePoint#CyberSecurity#MFA
What’s inside?
- Log and network traffic analysis
- Attack detection with Snort
- Phishing and malware investigation
- Threat hunting with Splunk and MISP
- SOC automation and AI-driven security
Complete the lab and earn your Blue Teaming Practitioner badge!
#BlueTeaming
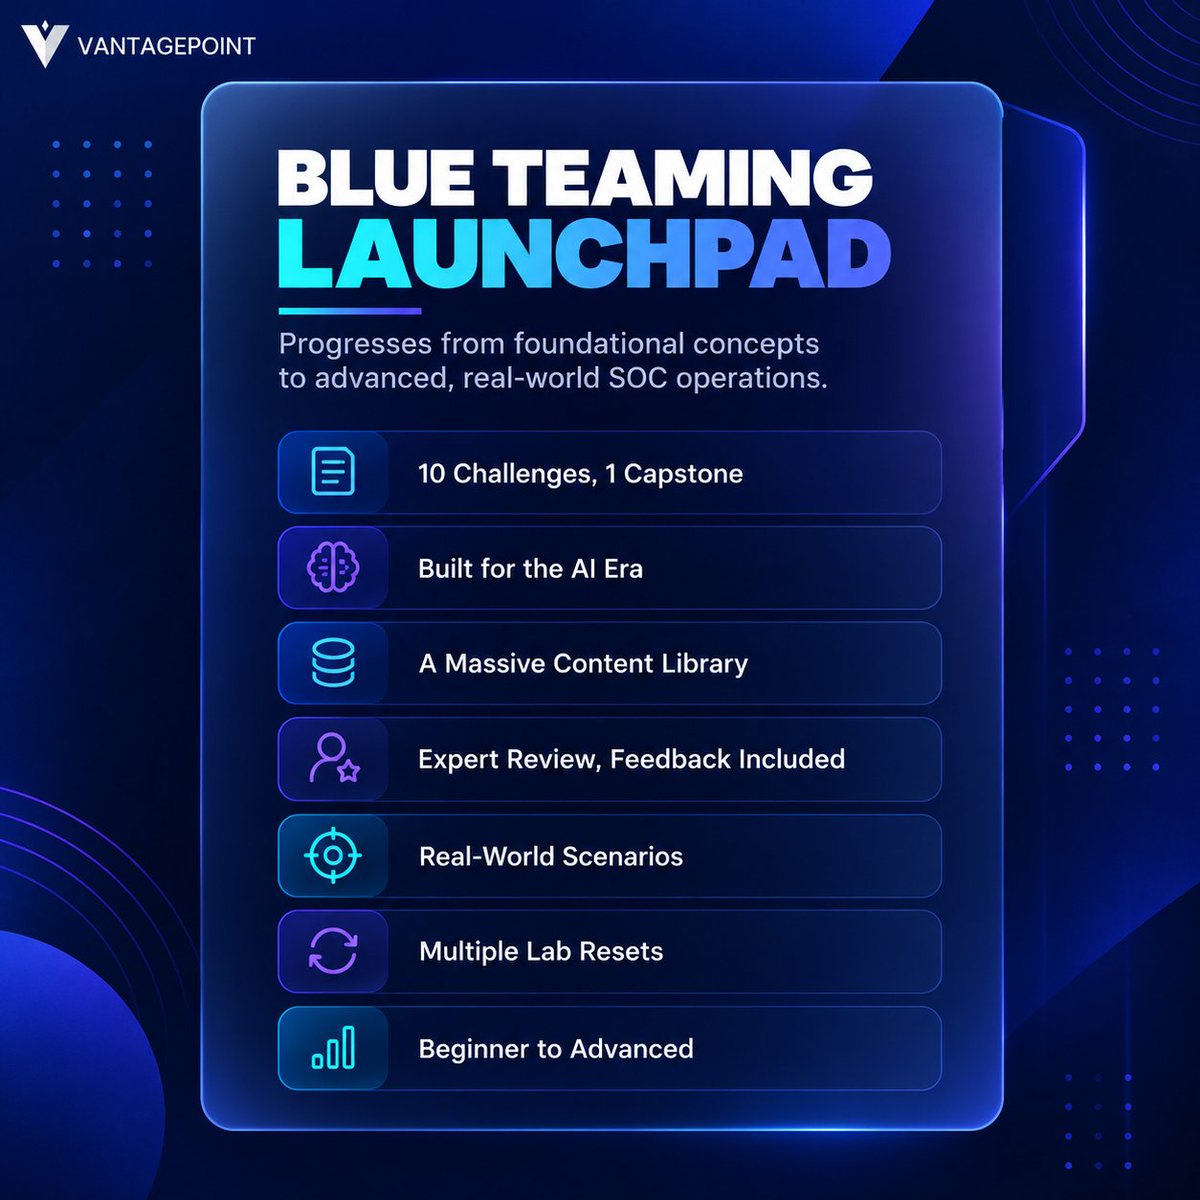
We're excited to announce the addition of Blue Teaming Launchpad to our portfolio!
Designed to take learners from foundational concepts to advanced, real-world SOC operations, BTL offers a hands-on approach to building practical defensive security skills.
https://t.co/PxR6qutpg7
24-hour exams. Zero feedback. Renewal fees for skills you already proved.
We got tired of it, so we built cybersecurity certifications that work differently. Here’s how 👇 https://t.co/HEPnma42k6
Explore the Web Hacking Launchpad or any VantagePoint lab & certification, uncover a creative attack, and submit your technical write-up.
Win a 3-month Burp Suite Professional license, sponsored by @PortSwigger
https://t.co/PxR6qutpg7
#WebHacking#bugbounty
The best discoveries often start with a simple question: What if I try something different?
Pick any lab or certification,submit your technical write-up, and stand a chance to win a 3-month Burp Suite Professional license, sponsored by @PortSwigger .
👉 https://t.co/PxR6qutpg7
You found the solution. But what if that’s just the beginning?
Go beyond the intended solution in any lab or certification, document it and stand a chance to win a 3-month Burp Suite Professional license, sponsored by @PortSwigger
👉 https://t.co/PxR6qutpg7
#Bugbounty
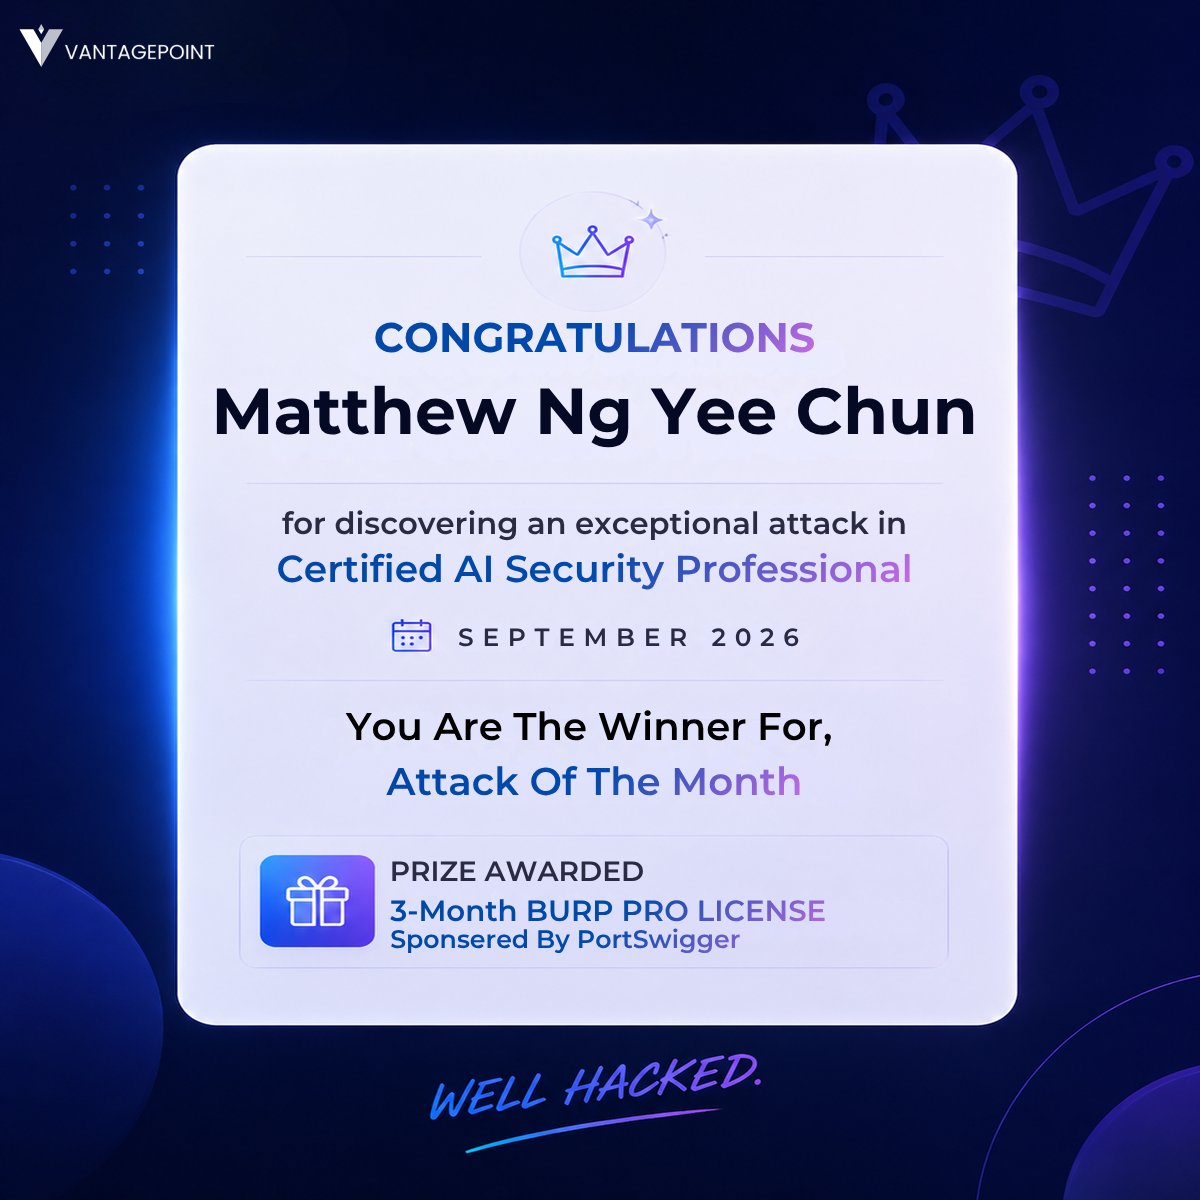
Massive props to Matthew for going all the way in CAISP Challenge 2: The Listening Post and winning “Attack Of The Month”
The best part?
He didn’t stop at finding the CVE.He kept digging, validated the vulnerability, took it all the way through exploitation to achieve RCE.