I made a fun little game: ZeroDay Tycoon 🐛
Start as a broke bug bounty hunter, survive triage and your worst enemy (Duplicate), and build a cybersec empire.
100% free, plays in your browser.
👉 https://t.co/ShNSNPBk3Z
💬 discord : https://t.co/Zo9XzpB9Z1
Our research team discovered two vulnerabilities in Discourse: a pre-authentication cache poisoning to sitewide XSS (CVE-2026-55674), and an arbitrary file read (RCE) chaining a JPEG race condition with ImageMagick and Ghostscript (CVE-2026-55420). You can read more here:
Recently, I've been looking at DOMPurify again, trying to find ways to bypass 3.x.x after browsers started encoding attrs during serialization.
I ended up with a nice ≤3.2.6 Safari default-configuration bypass using only SMIL tags/attrs :D
Details 👇
https://t.co/EMfsjlXUem
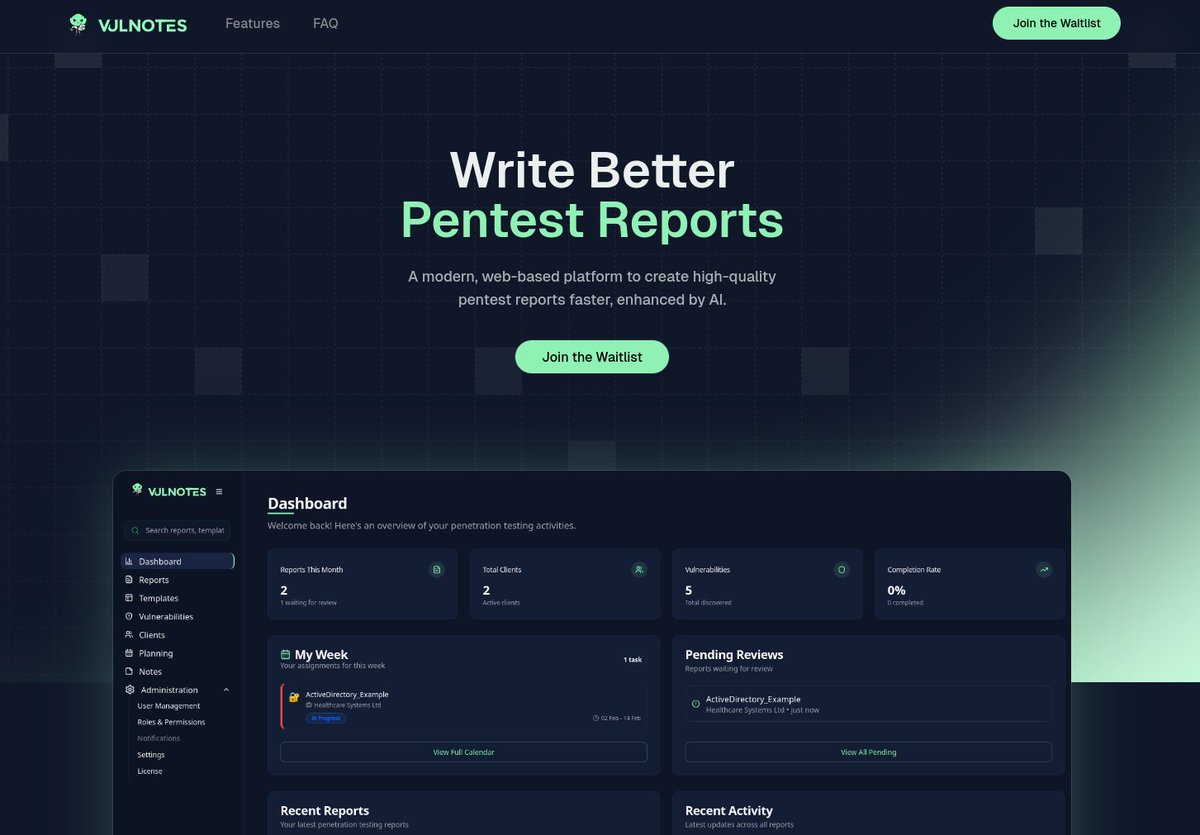
I left my pentest job to fix what every pentester complains about: reporting and team management.
18 months building, 6 months tested on real engagements.
Today it goes live.
Vulnotes is officially available 🚀
🚨🚨 TOOL 🚨🚨
NMAP is an ADVANCED port scanning tool used by AI HACKING FRAMEWORKS and PENTESTERS alike 🤓
Can scan ALL of YOUR ports 🤖🤖
Generates XML AND greppable REPORTS! 🔥🔥🔥
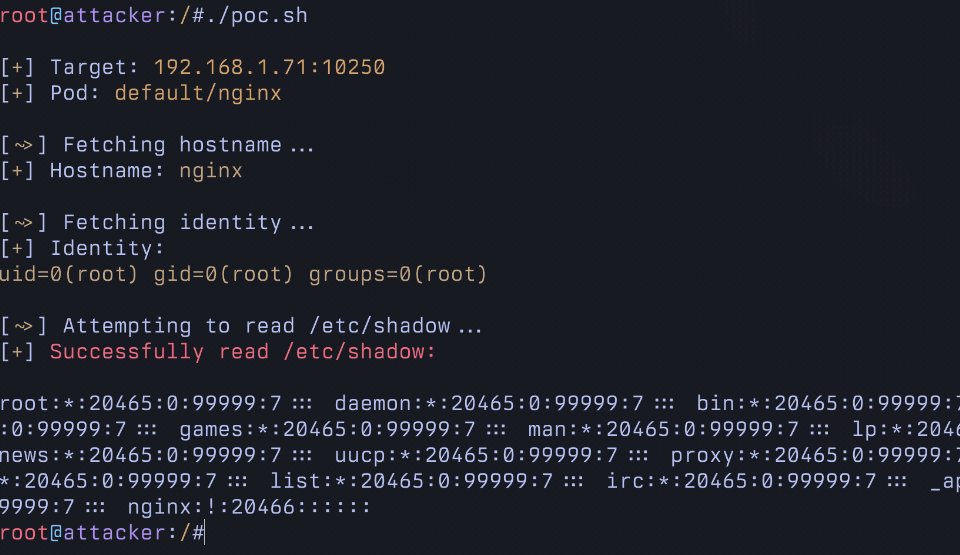
Excited to disclose my research allowing RCE in Kubernetes
It allows running arbitrary commands in EVERY pod in a cluster using a commonly granted "read only" RBAC permission. This is not logged and and allows for trivial Pod breakout.
Unfortunately, this will NOT be patched.
Thrilled to finally share what I’ve been building for over a year: Vulnotes👾,a reporting tool for pentesters who are tired of clunky, incomplete solutions.
Vulnotes was born from countless hours writing reports and hearing the same frustrations from friends and colleagues.
DOMLogger++ v1.0.9 is now out and available! 🎉
This update fixes a lot of issues, including the historical DevTools bug on Chromium 🔥
It also brings full Caido session handling, which is going to be useful in the near future! 👀
👉 https://t.co/wQHbXqzvkq
1/2
I'm happy to release a script gadgets wiki inspired by the work of @slekies, @kkotowicz, and @sirdarckcat in their Black Hat USA 2017 talk! 🔥
The goal is to provide quick access to gadgets that help bypass HTML sanitizers and CSPs 👇
https://t.co/SgsSyxoEMR
1/4
the research paper is out:
Next.js and the corrupt middleware: the authorizing artifact
result of a collaboration with @inzo____ that led to CVE-2025-29927 (9.1-critical)
https://t.co/GZkbnr6o9H
enjoy the read!
🔍 Just released a major update for Hippie OSINT Toolkit!
✅ Rebuilt backend architecture
✅ New Discord module
✅ TikTok user search capability
✅ Enhanced UI/UX
✅ TikTok & Mastodon techniques articles
✅ Significantly faster execution
✅ Improved socket handling
DOMLogger++ v1.0.8 is now out and available! 🎉
This update includes several UX improvements, such as syntax highlighting and new shortcuts. Major changes have been made to custom types and several annoying bugs have been fixed 🚀
👉 https://t.co/sPjJmtdDeZ
I'm very happy to finally share the second part of my DOMPurify security research 🔥
This article mostly focuses on DOMPurify misconfigurations, especially hooks, that downgrade the sanitizer's protection (even in the latest version)!
Link 👇
https://t.co/Hg1MkqVuGw
1/2