"Visibility is survival." 🚨
Perimeter defense is obsolete. Stop trusting certifications and start continuously validating vendor behavior. You must see the entire risk map.
Watch our founders on the shift to supply chain control.
#FrontierZero#SaaSDefense#SupplyChain
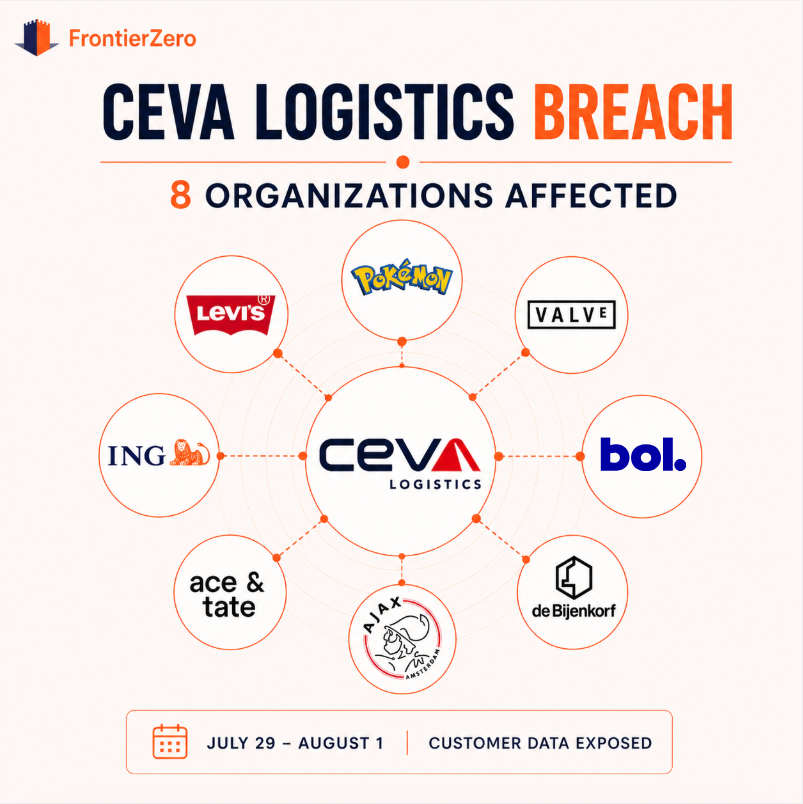
CEVA Logistics breach hit 9 companies at once: Pokémon, Valve, bol, De Bijenkorf, Ajax, ING, Levi Strauss, all found out via legal notice, not security alerts.
Hackers don't attack companies anymore. They attack the connections between them.
Are you monitoring yours?
Hackers don't hack anymore. They log in using valid credentials. Your firewall sees legitimate traffic. Your SIEM sees a legitimate login.
Everything looks normal until your data is gone.
Pattern of life security is the only defense.
https://t.co/AVfkJOx2lO
Bol & De Bijenkorf: systems untouched, 400k+ records stolen. How? CEVA Logistics vendor breached.
Amgen. EY. Rockstar. Same pattern: hackers don't hack your company, they log in your vendors.
Your firewall can't defend what you can't see. Do you know who is connected right now?
You think Microsoft Defender has you covered. It doesn't.
Defender = Microsoft apps only. Your business runs on 300+ others (Canva, Figma, HubSpot + 30 more you forgot about).
60% of breaches hit via third parties Defender can't see.
Read more: https://t.co/Sop6QL662W
Your vendor scored well. Passed every check.
Then breached you through a trusted OAuth connection nobody was watching.
48% of breaches work this way now.
We compared the top 5 TPRM tools for GCC teams, and the gap is bigger than most realise 👇
https://t.co/FkA1TO7X1u
Third-party breaches hit 48% of incidents. Polymarket. LastPass. Oxford.
We're tracking every major 2026 breach in one place. Bookmark it. Share it with your board.
https://t.co/TjY9LuglzK
#Cybersecurity#SSPM#FrontierZero
LastPass wasn't hacked. Their vendor was.
A forgotten 2022 credential → stolen OAuth tokens → straight into Salesforce.
48% of breaches start this way according to Verizon DBIR.
Know what's connected to your environment:
https://t.co/NuTKUMFl7z
48% of breaches involve a third party. Up 60% in one year. (2026 Verizon DBIR)
HackerOne. Oxford. Rockstar via Anodot.
Same root cause every time: a vendor nobody was watching.
Find yours → https://t.co/MWNJFDTpe7
Your vendor just got an A on SecurityScorecard.
Their OAuth token from 8 months ago is still active. Nobody flagged it.
Because SecurityScorecard goes silent the moment a vendor connects to your environment.
We mapped where that visibility ends 👇 https://t.co/a35SxhXDqs
Do you actually know which AI tools your employees are using?
One customer banned DeepSeek. 5 employees were still using it. No alert fired.
You can't enforce what you can't see.
#ShadowAI#CyberSecurity
GitHub is investigating an internal breach by TeamPCP. Their playbook? Compromise one app, use it as a skeleton key, and move through everything connected. Trivy. Checkmarx. LiteLLM. Now GitHub.
Do you know what GitHub is doing inside your environment right now?
#SaaSSecurity
ShinyHunters didn’t hack Zara—they found an open door.
A forgotten #vendor token gave silent access to multiple companies. No alerts triggered.
A textbook 3rd‑party risk scenario—broken down by @FrontierZeroIO
👉 https://t.co/KwsqshPr8x
Most SSPM vendors were built for the US market.
SOC 2. GDPR. Fortune 500 case studies.
UAE PDPL, NCA ECC, DIFC, afterthought at best.
We mapped the 5 most evaluated SSPM platforms against what GCC organisations actually need.
👉 https://t.co/5m6Cam50ni
#SSPM#CyberSecurity#GCC
Zara. 197,000 records. A vendor connection nobody closed.
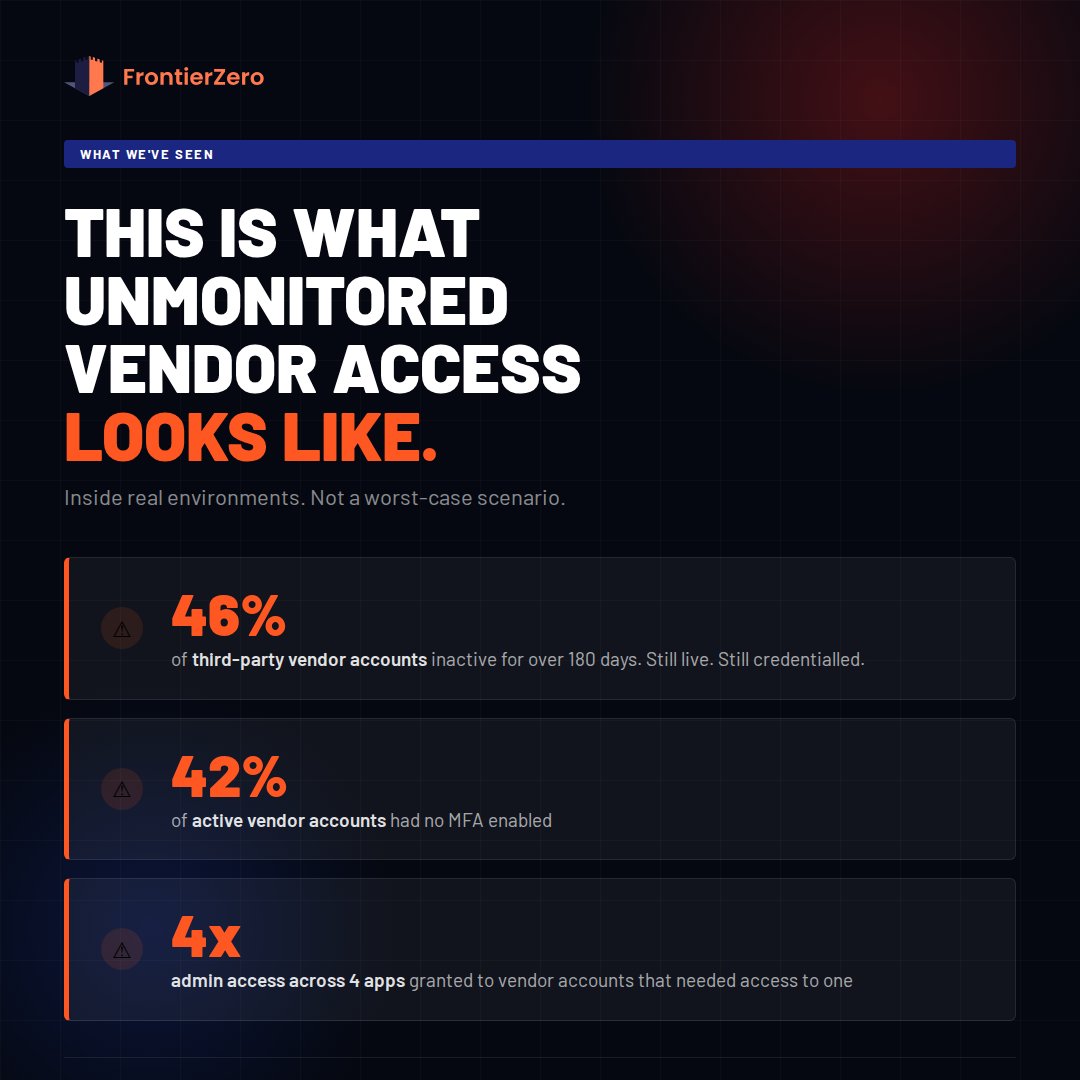
In environments we've analysed: → 46% of vendor accounts inactive 180+ days. Still live. → 42% had no MFA → Admin access across 4 apps when 1 was needed
You can't offboard a vendor you've forgotten about.
#FrontierZero
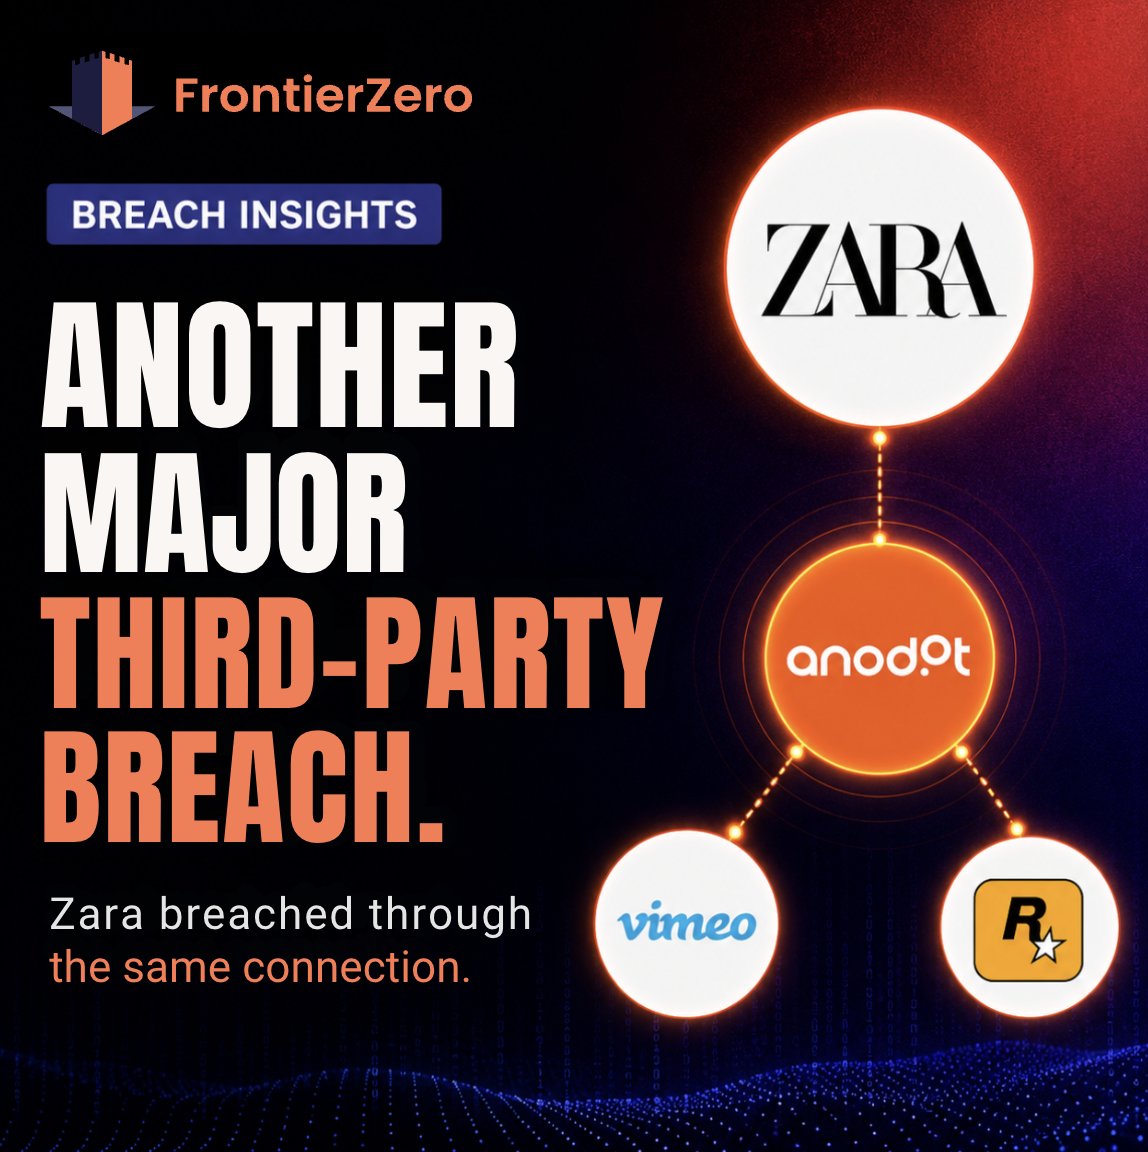
Zara. Vimeo. Rockstar. All breached in April through the same vendor.
One analytics tool. Three household names. Millions of records gone.
Nobody's systems were touched. Just their third-party connections.
#ThirdPartyRisk#SSPM
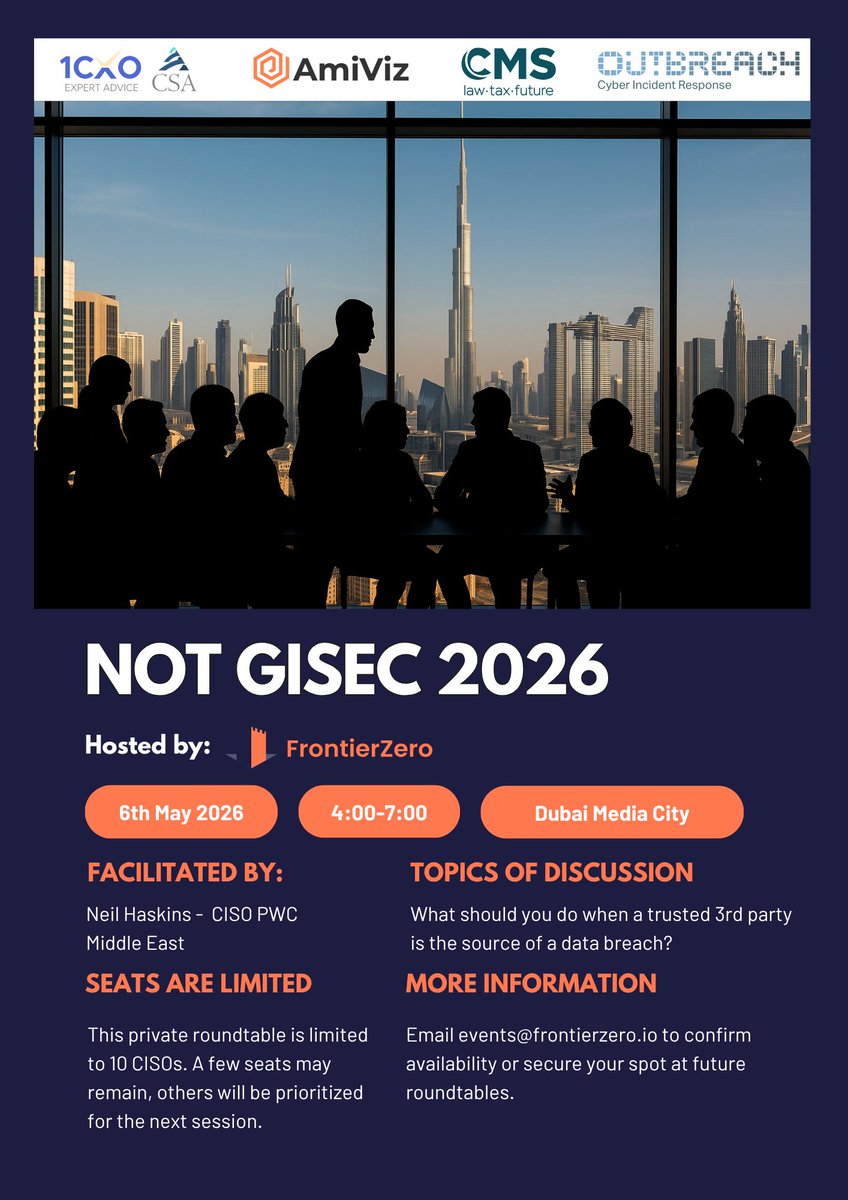
Yesterday's roundtable. Dubai Media City. The kind of conversation you don't get at a conference.
Takeaways coming soon.
If you want to be there next time, email [email protected]#Cybersecurity#ThirdPartyRisk#Dubai
Vimeo breached through a third-party tool. Not hacked directly. Same for Rockstar Games, Crunchyroll, Vercel, HackerOne, JLR, Qantas.
The list keeps growing. Attackers aren't breaking in. They're logging in through vendors you already trust.
#ThirdPartyRisk#CyberSecurity#SSPM
Jaguar Land Rover. Qantas. M&S.
All breached through a third party.
Most tools watch your employees. Nobody watches the supplier who is still connected to your data.
FrontierZero does, and that's just the start.
With @ami_viz 👇
#SaaSSecurity#ThirdPartyRisk
Most SaaS tools focus on applications.
FrontierZero focuses on identities.
When someone leaves email gets cut. SaaS access? Still open.
That's the blind spot we built to fix.
Filmed with @ami_viz#SaaSSecurity#SSPM