Vous êtes en train de nous rejouer le coup d'Internet qui serait pour les méchants pédophiles et néonazis.
Regardez les archives @Inafr_officiel des JT des années 90.
30 ans plus tard, ces images sont ridicules. Ne tombez pas dans la même facilité...
https://t.co/mT3ZHPecnZ
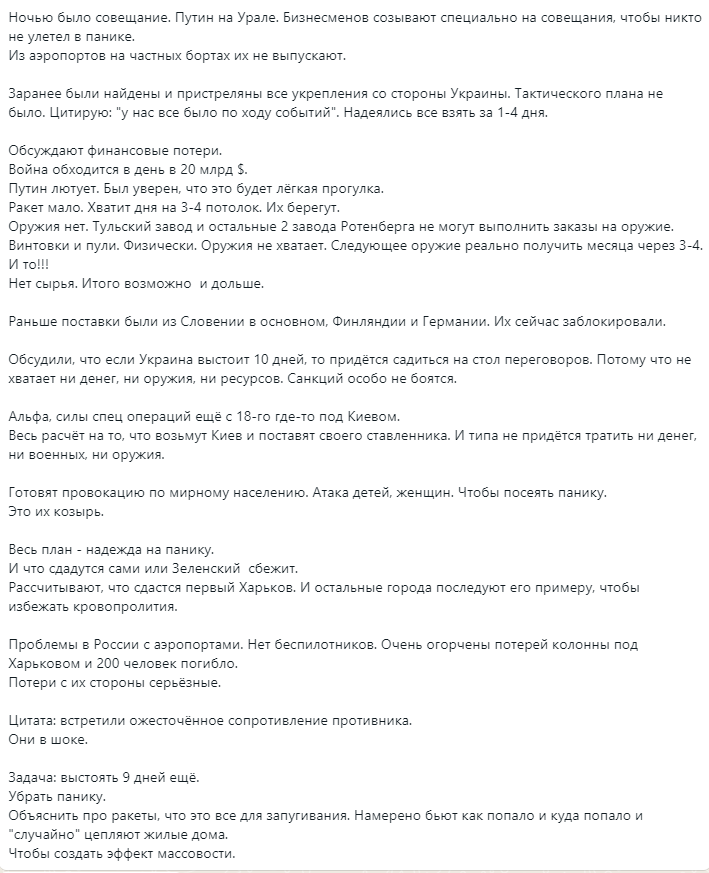
THREAD 1/7 Intel from a Ukrainian officer about a meeting in Putin’s lair in Urals. Oligarchs convened there so no one would flee. Putin is furious, he thought that the whole war would be easy and everything would be done in 1-4 days. @EPPGroup@general_ben@edwardlucas@politico
This article has the worst securty suggestions I've ever read:
- If someone has admin privs on anything, they should have it everywhere
- Fire your security folks if you have a breach
- Never hire anyone who ever worked at an org that experienced a breach
https://t.co/bDj02SZmdB
@matthieugarin Si avéré, effectivement c'est une bonne nouvelle 👍
Pour autant il ne faut pas crier victoire et continuer de monter en maturité car ils ne vont pas lâcher comme ça: "Ransomware Gangs Get More Aggressive Against Law Enforcement" https://t.co/uxuZIcIc2L
@matthieugarin Les gars derrière ce projet sont 2 jeunes italiens de 19 et 16ans qui sont inconnus au bataillon, et du coup, perso je réfléchirais à 2 fois avant de donner mon numéro. Rien à voir avec le « track record » de Troy Hunt et son site https://t.co/JGbe8Ol6er donc attention!!!
🤔 Windows credential theft without Mimikatz, admin nor touching LSASS?
💡 Discover #Kekeo by @gentilkiwi to abuse CredSSP / TSPKG (RDP SSO)!
➡️ Read the article to learn how to exploit it & how to discover such dangerous configuration in your environment
https://t.co/LDGiOa4vgF
💣 "Risks of Microsoft Teams and Microsoft 365 Groups"
What happens when users create public Teams? What is an M365 Group? How to find chats, files, emails.. shared publicly within an organization?
📝 https://t.co/SqRUFIy4BG
🛠️ https://t.co/hMMabNQBHU
🏷️ #pentest#AzureAD#M365
I've been compiling a Windows #cheatsheet of common commands and areas of interest for #DFIR including common tool-sets (more information to come). This can be found below, any comments or feedback is always welcome.
https://t.co/iHcwHP1d4j
How do you integrate @ProjectJupyter#notebooks with the #sigma project? How do you convert 300+ rules to @elastic ES query strings & pack them as part of notebooks to query ES? All from code 😱. I wrote about it here! Weekend readings! 🍻 #threathunting https://t.co/6jeuvDEt0y
I finally have an answer to the question, "How do we find API tokens scattered in a string?"
Current solutions use shannon entropy and regular expressions to tackle this problem with horrible false positive/negative rate.
I am publishing my algorithm tomorrow, here's a demo
https://t.co/dShHefHhBI 2019 is out!
better, cleaner code and performance boost.
Improved Microsoft #AzureSentinel Query support
345% Faster load time
223% Smaller page size
74% Less requests
332 #sigma rules included
latest sigmac supported
#uncoder#SIEM#threathunting
I always wondered how I could share #ThreatHunting detections via @ProjectJupyter notebooks in a more practical and interactive way so that anyone in 🌎 can reproduce the research! Thx to @mybinderteam 💜 @HunterPlaybook @Mordor_Project it is now possible https://t.co/Jxawj7P2f5
Attackers sharpen the saw too. See this post on how phishers 🎣are returning tailored AAD login pages for victims🎭, tricking defenders with custom 404 pages👀, and abusing Google's "I'm feeling lucky" feature with SEO techniques 💉
https://t.co/w5UilYgZcU
We hear about attacks at the same time, but learn to defend alone.
How can we change this so every defender can be as good as the best defender?
In this post, I talk about an open, vendor neutral, community based approach to accelerate infosec learning.
https://t.co/5QPIEpxoYr
Check outgoing web requests.
They are the low hanging fruit if you already have a web proxy in place and integrated into your SIEM.
Sigma has a set of rules to detect malicious requests.
https://t.co/yPkFoXO4R9
For those looking at different #Security#Certifications, this is a nice way of presenting a lot of information by SinecureLife. Just don't forget the benefit of a home lab and hands on experience...
User:
(https://t.co/IVpZx95fWV)
Reddit:
https://t.co/JxJWwcy1br
I'm doing research for my next book and I'd love to talk to you if:
- You've used honeypots/tokens to successfully catch bad guys
- You've been caught by honeypots/tokens as a pen tester
- You've used a non-typical type of deception tech to do cool things
RTs appreciated