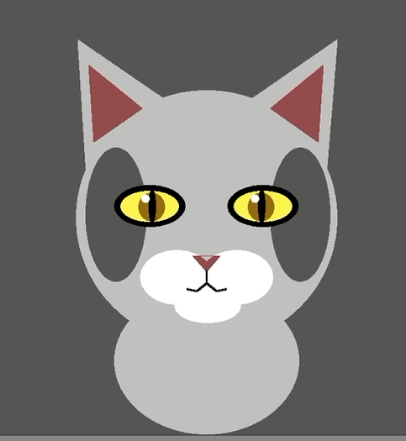
@makc3d I usually have problem with visualisation with all this models - they cannot understand orientation in space, and frequently miss with rotation or orientation of one object relative to another
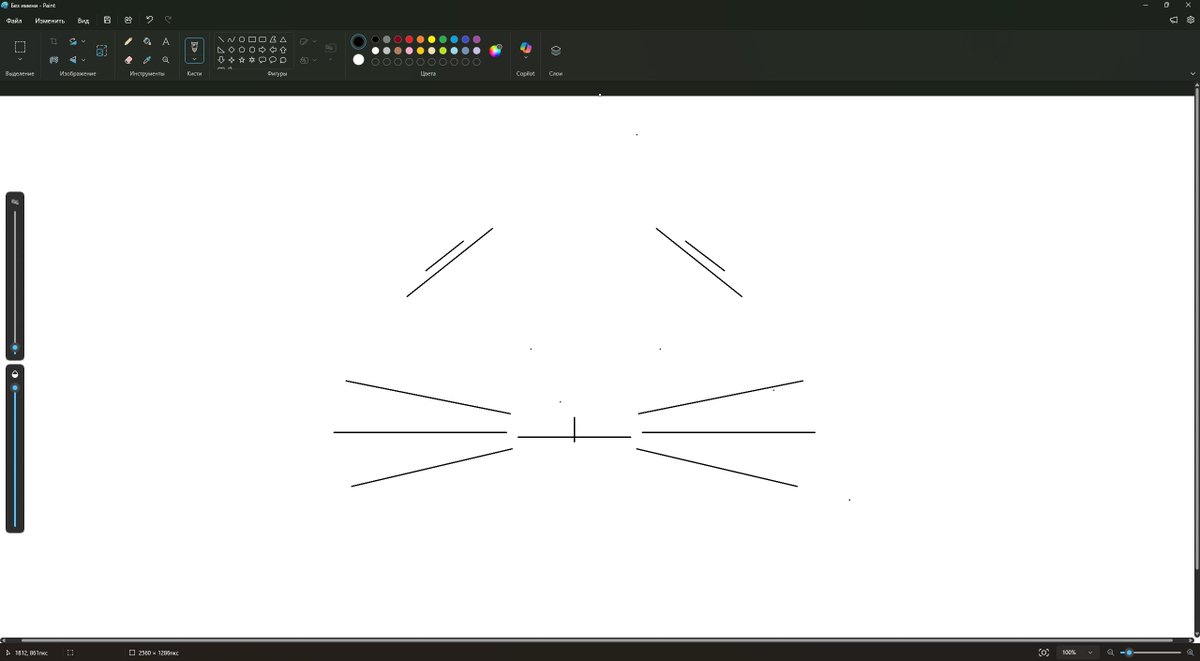
@makc3d tried dots today, he draw me a cat in paint on my PC, but then he do the same on his virutal PC
For open weight models, i try deepseek v 4.1 flash aswell, i think i prefer GLM 5.3 flash over deepseek.
@thsottiaux It was GIGA task.
I get all my old documentation for about 10-15 years.
All my old code base unfinished game engines, games.
Create huge migration and consolidation plan step by step with soruce links, etc...
Start this task in cloud agent. And actually get good results
@thsottiaux It seems it should NOT: the subscription is not converted into a general or multi-user API and no usage is re-served/shared. Are local observability, routing, or compression wrappers treated like Pi/OpenCode, or can the proxy hop itself trigger a fraud flag?
@thsottiaux@thsottiaux Could you clarify the boundary? Does a local single-user wrapper/proxy like Caveman count as sub2api if it uses only the owner’s Sign in with ChatGPT session, exposes nothing to others, and never pools, resells, or shares quota?
@agrimgupta@thsottiaux@ajambrosino problem is you cannot do is you cannot do it from UI, and UI have old outdated configuration style.
And for configure it by yourself ask codex, or read documentation.
BUT it still complicated actually
@agrimgupta@thsottiaux@ajambrosino folder e.g
'C:\Program Files\PowerShell\7' = "read"
'C:\Program Files\PowerShell\7' = "write"
etc...
then in your specific project you can extend this profile
default_permissions = "my-project"
[permissions.my-project]
extends = "trusted-project"
@agrimgupta@thsottiaux@ajambrosino and you have it, you have settings on user.../.codex/config.toml level and in project/.codex/config.toml
you can create permission profile in root like
[permissions.trusted-project]
and in [permissions.trusted-project.filesystem]
you can give access or restict for specific
@clarity99@thsottiaux and you actually can share ssh, etc to give sandbox user access to git in elevated, but it still it cannot pull. mb you can provide separate auth for sandbox user idk
But yes - simply turn on sandbox mode = your workflow is broken
And it probably after 11 or 13 august uodate
@clarity99@thsottiaux you need to manualy add access to all tools, folders, etc.. and still you haave two sandbox levels
elevated - youcannot access outside workspace e.g cannot commit/push/pull
unelevated - process cannot spawn subprocess so e.g vitest isnt work
@getjjed@thsottiaux you can completely turn it off in config by
approval_policy = "never"
approvals_reviewer = "user"
and you also can configure autoaprove policy and model manualy, and aprove promt if you want
@getjjed@thsottiaux you can configure it in "approval policy" and in app UI you did not have all options, conigure it manualy in config.toml, if you set-up approval policy as "never" codex never ask you for approve, and never send it to model for auto aprove, on request will evaluete it by model