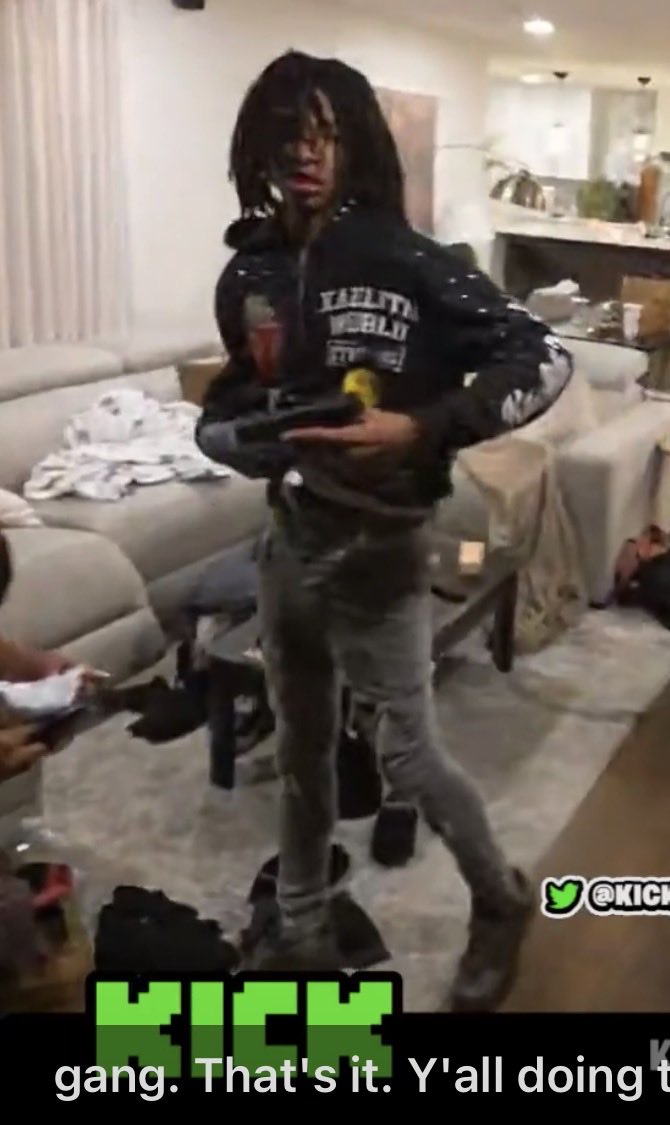
@clapyogal I just watched the video of the deputy single-handedly arresting all of these kids. Not one N word when they were in cuffs. Red head was counting to 3 out loud repeatedly while crying having a panic attack. Pussies.
On 7 April 2026 NIST issued a concept note for an AI risk profile aimed at critical infrastructure. The base framework stays voluntary. Operators still need practices for the system they actually run, not a demo.
https://t.co/iY9EzBQJxv
Privacy programs love counting controls. People experience outcomes. If a compliant system can still expose, exclude, or manipulate someone, the risk model is measuring the wrong thing.
https://t.co/hIj7WlBAKs
The EU terms-and-conditions database holds over 790 document sets from more than 400 services and reviews them several times a day. Policy text that changes in the dark is not a contract the user can follow.
https://t.co/cO0kUTFfVN
If AI could do most coding, 75 percent of developers would still ask a person when they do not trust the answer. The survey puts humans in the role of final check. A workflow that removes that check has left the evidence behind.
https://t.co/ZY420G4rY3
The worst AI code is not obviously broken. It is almost right, passes the happy path, and leaves the expensive debugging to a human.
Should AI-generated changes face stricter review than human changes?
https://t.co/ZY420G3U8v
52 percent of developers either skip AI agents or stay with simpler tools, and 38 percent have no plan to adopt agents. The majority is not waiting for a better prompt. They are refusing unattended change.
https://t.co/ZY420G4rY3
General-purpose AI providers must document capabilities, limits, and training-content summaries in the EU. That is not anti-innovation. It is the minimum evidence required to sell power responsibly.
https://t.co/SnjkjpOQhk
The Commission says a minor change to a general-purpose model does not make you its provider. A significant modification does. The guideline is not a statute, but it is what enforcement will follow.
Who draws that line in your release process?
https://t.co/SnjkjpPo6S
MFA, logging, and SSO should not be premium security features. CISA says secure products should include them without extra cost. Charging for basic defense turns risk into an upsell.
https://t.co/wAHEhVgLep
Shipping critical-infrastructure software that already contains a known exploited vulnerability is a bad practice. CISA says patch those components before release. A launch that includes an active flaw is an incident with a marketing date.
https://t.co/l8hgY0Y5YZ
Experienced developers trust AI less, not more. That may be wisdom, or it may be a profession defending its status. What evidence would actually change your mind about agent-written production code?
https://t.co/ZY420G3U8v
Hardcoded credentials in source are a product defect, not a developer habit. CISA tells manufacturers to pull secrets from a manager in the pipeline and to scan for them before release. If the key is in the repo, the customer cannot rotate it.
https://t.co/l8hgY0Y5YZ
On 26 July 2024 NIST published a generative AI profile of its risk framework, NIST-AI-600-1. It is voluntary. A profile that names unique generative risks still leaves the vendor free to ignore it. Voluntary is not a control.
https://t.co/iY9EzBRhn3
CISA says logs of configuration changes, sign-ins, and data access belong in the baseline product. Cloud vendors should keep them at least six months without an extra fee. I will not pay to see the evidence. https://t.co/l8hgY0YDOx
Open source maintainers are expected to secure critical infrastructure with volunteer economics. If a company depends on a project for revenue, contribution should be a cost of doing business.
Fair or impossible?
https://t.co/qebCFhy04P
Vetted researchers can receive internal data from very large platforms when the work studies systemic risk. The status requires a research affiliation and a promise to publish the results free of charge. Access without publication is not scrutiny.
https://t.co/cO0kUTFNLl
Very large platforms must assess systemic risk every year and take an independent audit on that cadence. Within three months they publish the assessment, the audit, and what they changed. https://t.co/cO0kUTFfVN