#CommunityAlert 🚨
The @AudiusProject has been exploited for a total of ~$6M worth of AUDIO tokens, the tokens were sold for 705 ETH.
The attacker modified the Audius governance contract's configurations, then proposed and executed a malicious proposal draining 18.5M AUDIO.
1/ The Harmony team has identified a theft occurring this morning on the Horizon bridge amounting to approx. $100MM. We have begun working with national authorities and forensic specialists to identify the culprit and retrieve the stolen funds.
More 🧵
A critical bug has been found on $OSMO / @osmosis which could have potentially drained all liquidity pools.
It has been discovered after a post on the subreddits /r/CosmosNetwork and /r/OsmosisLab.
The chain was halted under immediate emergency to avoid further damage.
🧵
🚨 CRITICAL ALERT
A severe 0-day vulnerability called #Follina has been exposed (since May 27th) in MS Word Documents.
It could allow hackers to take full control of your computer, in some cases WITHOUT even opening the file. 🧵
Anchor Protocol was exploited.
#LUNC oracle price after the launch of #luna2 went to $5 and someone deposited around 20mln #BLuna, which was considered as $100mln by @anchor_protocol and took a loan of $40mln #UST. #LUNA
$800k for someone lucky enough.
@stablekwon@FatManTerra
Chainlink pausing the LUNA oracle allowed several attackers to deposit millions of LUNA which is still worth $0.10 according to the Chainlink oracle to borrow all the collateral.
The protocol has been drained before we could pause due to our timelock.
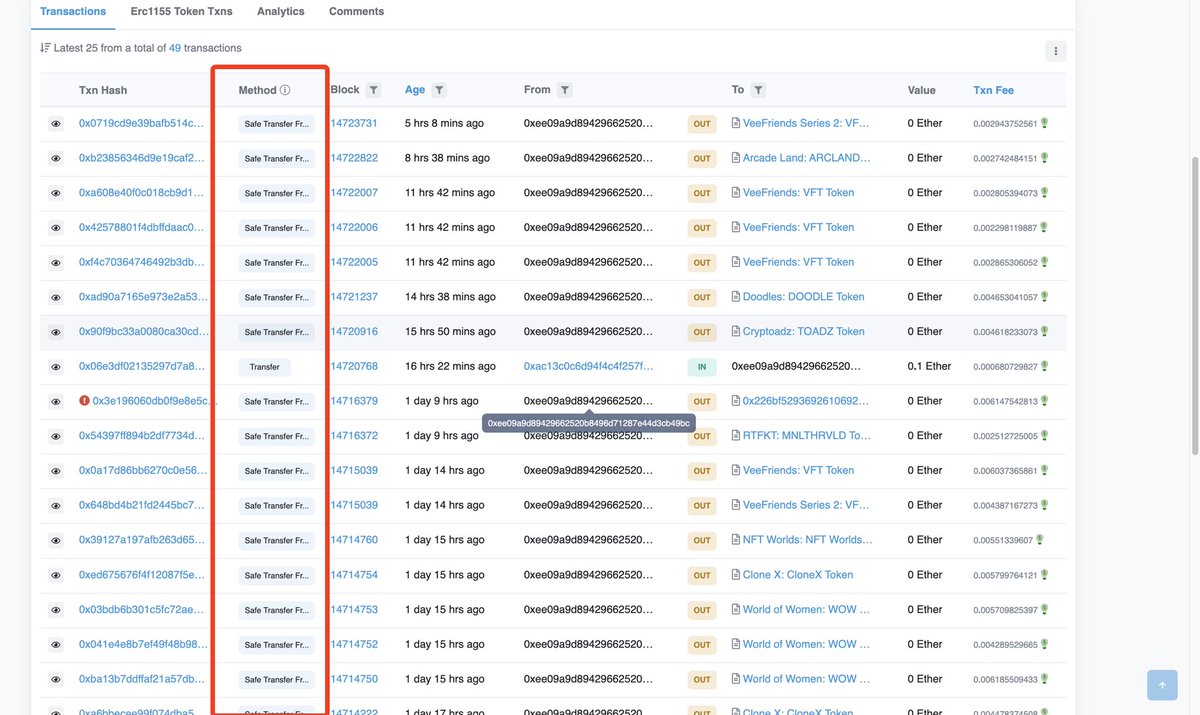
The #NFTCommunity needs to be prepared for a new storm of #NFT hacks, the hack is done with the following steps:
1.Hacker identifies targeted wallets (often big holders of blue chips and whales) and airdrops suspicious but attractive #NFTs to these wallets
1/8
On April 7th, we reported an oracle misconfiguration issue on @AaveAave that had gone unnoticed for a month. If the right condition was met, would allow draining all borrowable funds across deployed L2 chains (~$3B). Aave V3 was audited by 5 security firms.
Rari is aware of an exploit on various Fuse pools. Borrowing has been paused globally and no further funds are at risk.
The Rari team, and the rest of the Tribe, are working mitigate the loss and recover exploited funds, and will provide updates as soon as they are available.
We found an oracle manipulation vulnerability on @RariCapital via @immunefi which could allow draining $4M from a verified Fuse pool with as little as 1 ETH as the cost. The team downplayed it because it's users' responsibility.
👇Check out the write-up
https://t.co/4w26qD2fDN
We found a bug on @AaveAave V3 that could allow anyone to set any prices on their fallback oracle. Aave fixed it within one day after responsible disclosure.
Special thanks to @samczsun for helping out!
👇Check out the write-up
https://t.co/vSKK2nwK9O
Rugpull vulnerability patched in @ConvexFinance’s live contracts. $15 billion in TVL secured.
Summary in thread below. See blog for technical details.👇
https://t.co/dAkUom9qX1
1/5
We’re back to interesting exploits, and @InverseFinance users lost money today.
As a result, $15.6M was stolen in the form of:
- 1588 ETH
- 94 WBTC
- 4M DOLA
- 39.3 YFI
1/ It has come to our attention that the BMIZapper has a vulnerability in it. Please revoke all approvals for https://t.co/9vWRjELjCr
How to revoke in next tweet
Agave and Hundred Finance were exploited today on Gnosis chain (formerly xDAI).
The underlying reason for the hack is that the official bridged tokens on Gnosis are non-standard and have a hook that calls the token receiver on every transfer. This enables reentrancy attacks.